[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentGeneral cybersecurity news and analysis
The real risk of Shadow AI isn't about employees sharing sensitive info, but about unauthorized AI agents operating within your organization, connected to critical systems, and taking actions that can lead to data breaches and access-control failures. A staggering 65.4% of unused chatbots still have active credentials, leaving a gaping hole in your security.
Discover and remediate code vulnerabilities with ease using AWS Continuum, a game-changing platform that streamlines vulnerability management with AI-powered recommendations and automated remediation. With Continuum, you can gain confidence in your security posture and automate fixes based on your own risk profiles and priorities.
As cybercriminals shift their focus from email to other trusted channels, a glaring gap in non-email threat detection has emerged, leaving organizations vulnerable to attacks on messaging and social platforms. A recent survey of cybersecurity pros reveals that while 60% of attacks now target non-email channels, half of respondents admit their organizations lack confidence in detecting these threats.
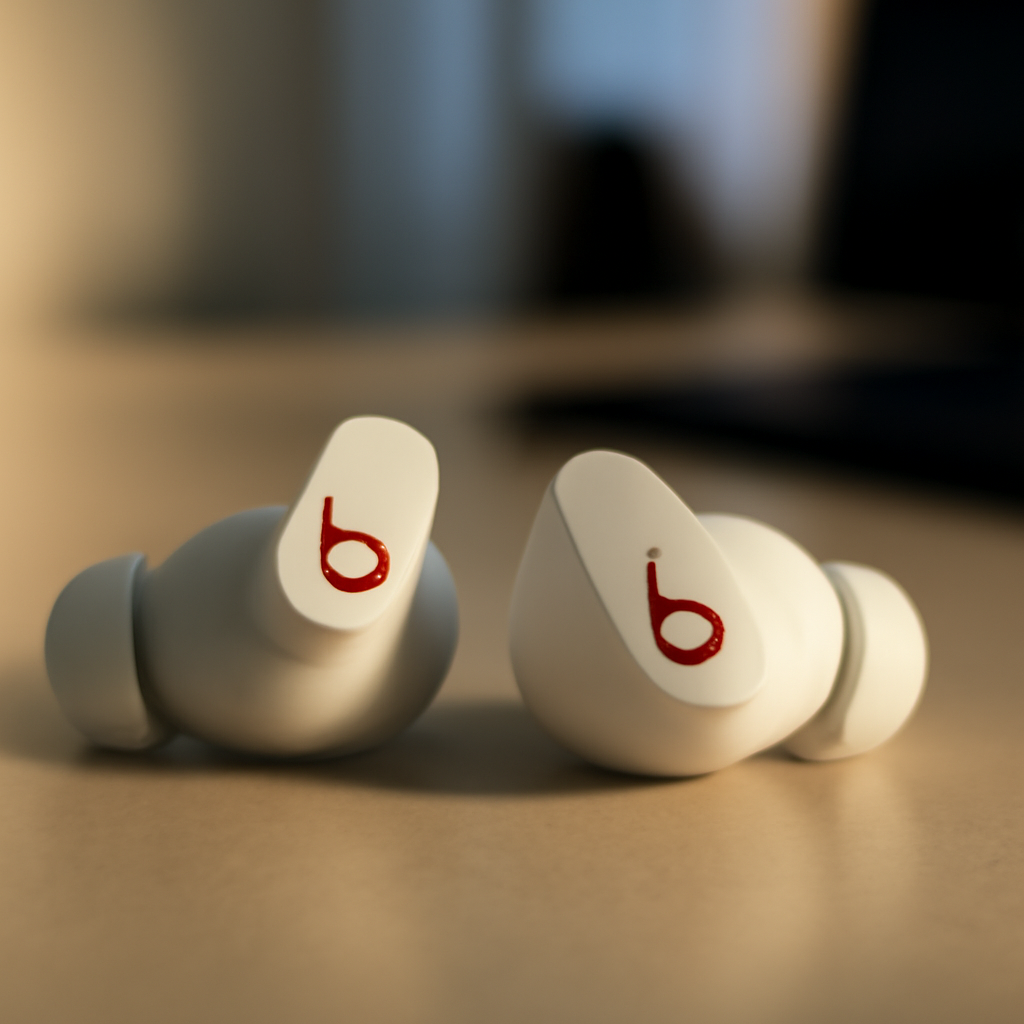
Apple just released a crucial update, Firmware 1B211, to fix a major flaw in Beats Studio Buds that let hackers eavesdrop on you through the earbuds' microphone - even if they're not paired with your device. This security patch protects you from unwanted listeners lurking within Bluetooth range.
F5 has issued urgent security updates for NGINX products after discovering two critical flaws, CVE-2026-42530 and CVE-2026-42055, that could allow remote code execution. These vulnerabilities, rated 9.2 on the CVSS v4 scale, pose a significant threat and require immediate attention to prevent exploitation.
As Robert M. Lee aptly puts it, our critical infrastructure, from energy and water systems to manufacturing plants, is crying out for robust cybersecurity that can stay one step ahead of evolving threats - and failing to deliver it could have disastrous societal consequences. Accenture is answering the call with a whopping $4.18 billion investment to bolster industrial cybersecurity.
Google's security team initially praised researcher Justin O'Leary for uncovering a high-severity flaw, dubbed ConfigConfusion, in the Config Connector add-on for Kubernetes - only to later claim it wasn't a vulnerability at all and deny a bug bounty. The issue still lingers, leaving users of the open-source tool potentially exposed.
Microsoft 365 is a powerhouse for productivity, but it leaves data protection gaps that put businesses at risk. The harsh reality is that while Microsoft safeguards its infrastructure, the responsibility of protecting your business data - including backups and recovery - falls squarely on your shoulders.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Can your security team instantly identify who authorized an autonomous AI agent to access your company's core intellectual property? The uncomfortable truth is that most enterprises have no clear answer, leaving them vulnerable to hidden AI access risks.
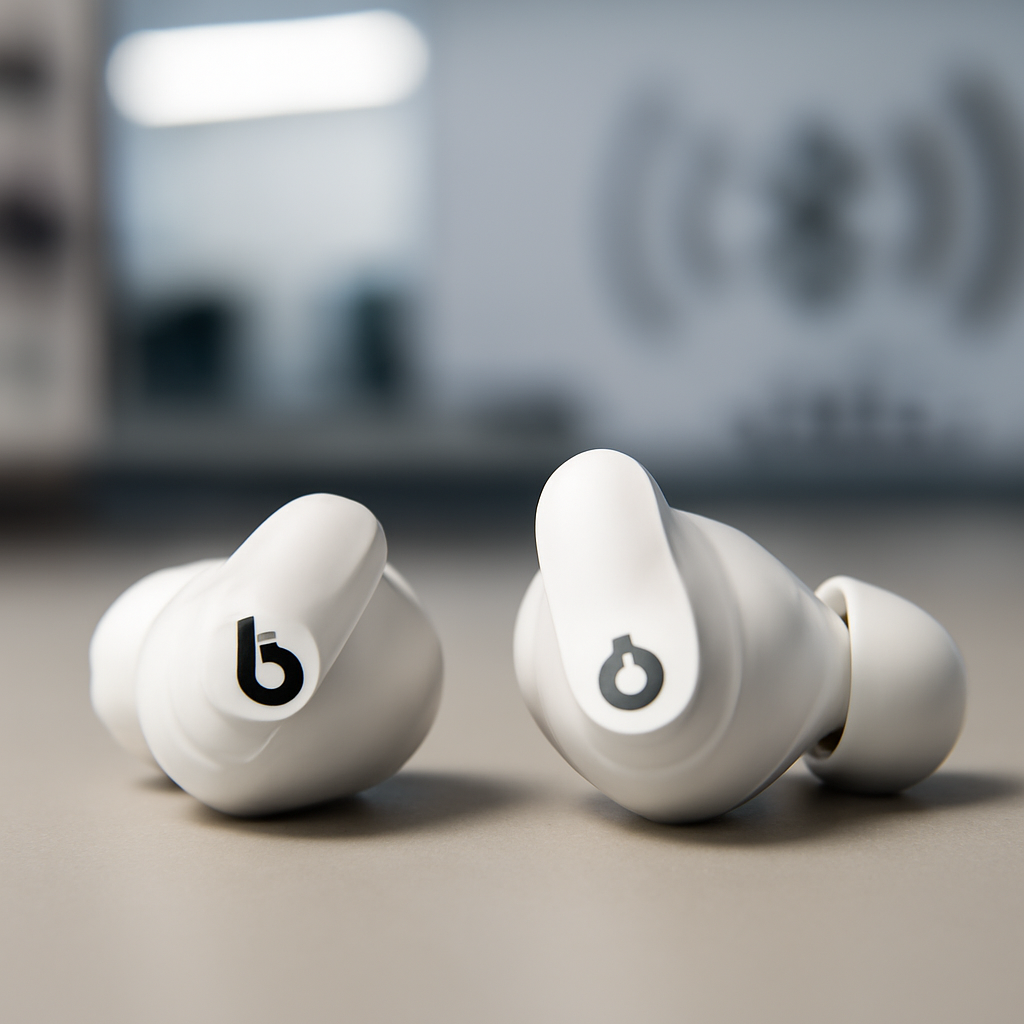
Apple just patched a major flaw in its Beats Studio Buds that allowed hackers within Bluetooth range to eavesdrop on conversations through the earbuds' microphone, even if they weren't paired with the device. The company has released a security update, Beats Firmware Update 1B211, to fix the issue.
Cybercriminals are getting anxious about the impact of AI tools on their illicit trade, and experts warn that now is the time for organizations to step up their cyber hygiene game with measures like timely patching, multifactor authentication, and passkey use. By prioritizing these defenses, businesses can stay ahead of emerging threats, including AI-assisted attacks.
F5 has urgently released patches to fix two critical vulnerabilities in NGINX modules that can be exploited by remote attackers to cause denial-of-service or even execute remote code. Admins are advised to install the updates ASAP to protect NGINX Plus, Open Source, Gateway Fabric, and Instance Manager from potential attacks.
Microsoft has fixed a frustrating issue that caused June's security update to fail installation on some Windows Server 2016 devices, resolving the error code 0x80070002 (ERROR_FILE_NOT_FOUND) problem that had administrators scratching their heads. The update should now install smoothly on affected servers.
Get ready for a change in ad personalization: on August 3, 2026, Google will start using IP addresses to tailor ads to individual devices across the UK, EU, and Switzerland. This update, framed around privacy-enhancing technologies, will allow for more targeted advertising using data that's already being collected.
Cisco has urgently warned organizations using its Catalyst SD-WAN products to investigate their exposure to network compromise and hunt for malicious activity following a maximum-severity bug. This critical alert was issued after Cisco expanded its advisory to include the Cisco Catalyst SD-WAN Validator, which is vulnerable to a 10.0 improper-authentication exploit.
As attackers increasingly target identities rather than infrastructure, account takeovers are on the rise - and with 22% of breaches involving credential abuse, it's clear that traditional username-and-password security just isn't cutting it. The explosion of identities across cloud services, SaaS apps, and remote environments has created a perfect storm of vulnerability.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
Homebrew just got a major security boost with its 6.0 release, introducing a new security mechanism and Linux sandbox to keep things safe and secure. This latest update, which landed on June 17, 2026, promises even more under the hood.
In just one year, enterprise data uploads to AI models have skyrocketed 93%, with a staggering 18,033 terabytes of data - equivalent to 3.6 billion digital photos - being transferred to AI and machine learning applications. This massive surge raises serious concerns about data breaches and cyber espionage.
Despite pouring resources into security tools for better visibility, many teams still struggle to turn insights into action, leaving them overwhelmed by endless findings with unclear priorities. It's time to bridge the gap between detection and response to truly fortify digital defenses.
Microsoft is investigating a frustrating issue that prevents some third-party apps from launching Office applications or opening documents after installing recent Windows updates. This problem, affecting Word, Excel, PowerPoint, and more, leaves users unable to access their files or work smoothly.
Did you know that 60% of organizations have at least one HTTP panel exposed to the internet, leaving them vulnerable to rapid exploitation by cyber attackers? In today's threat landscape, this kind of exposure can turn into a security breach in just 24 hours.
The EU has stepped up to bolster Ukraine's cyber defenses, approving the country's inclusion in the EU Cybersecurity Reserve and making 47 trusted private providers available to offer emergency support against cyber threats. This move enables Ukraine to tap into critical EU cyber support, even as it pursues EU membership.
Don't wait until it's too late - CISA is requiring Federal agencies to patch a critical Joomla plugin flaw by Friday, as hackers can exploit it to upload and execute malicious PHP code. The vulnerability, found in the Widget Factory Joomla Content Editor, allows unauthenticated users to create new editor profiles and poses significant risks to your online security.
The 2026 SANS SOC Survey reveals a disconnect: while 79% of respondents use AI or machine learning tools, only 36% have integrated them into a defined workflow, highlighting a key challenge in Security Operations Centers. Practitioners cite staffing shortages as their top operational challenge, but leaders seem less concerned.