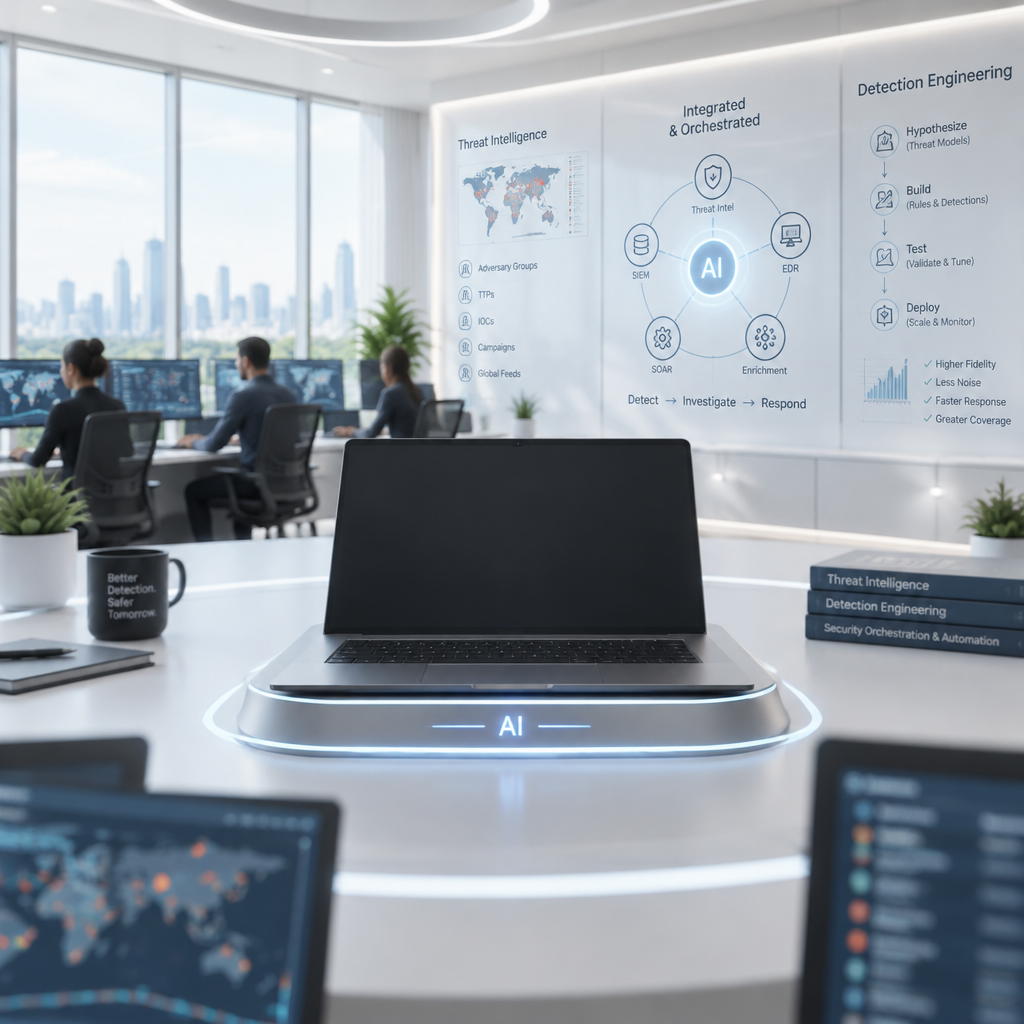
"AI is beginning to take over much of the work that has traditionally defined the security analyst's job," The Hacker News observed, setting the stage for a redefinition of security operations and careers as agentic systems move from assistance to orchestration.
From Individual Tasks to Overall Defense
The article describes how AI is starting to integrate functions that were historically separate inside security operations centers (SOCs): threat intelligence, hunting, detection engineering, investigation, and incident response. Rather than a sequence of handoffs across distinct teams and tools, AI agents can now carry context from one stage to the next — turning intelligence about a new threat into a hunting hypothesis, surfacing detection gaps, triggering investigations, and recommending containment or remediation steps.
That connectivity shifts where human value sits. Instead of focusing on individual alerts and repetitive triage, humans will be expected to set defensive priorities across the lifecycle and to judge whether AI-driven operations are actually improving security.
The Threat Operator and human-on-the-loop oversight
The source coins a role for this new operating model: the Threat Operator — an "AI-native security professional" who translates business risk into defensive priorities, directs AI-driven operations, and exercises judgment over automated decisions. As AI assumes more operational workload, the model moves from human-in-the-loop to human-on-the-loop: humans supervise and govern AI-driven workflows, defining autonomy boundaries and remaining accountable for consequential actions.
The article stresses that the level of autonomy will depend on technology maturity, the consequences of particular actions, and organizational risk tolerance — but a human is still responsible throughout. That requirement for oversight is noted as being consistent with the NIST AI Risk Management Framework.

Audit-ready is a season. It shouldn't be.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scrambleRethinking entry-level experience and mentorship
Junior analysts are singled out as likely to feel the earliest effects. SOC work traditionally provided an apprenticeship through alert triage, evidence collection, investigations, documentation, and escalation. As AI takes on more of those repetitive and increasingly sophisticated tasks, the conventional "handle simple alerts, then complex investigations" progression may become less relevant.
The Hacker News argues that AI can also enable broader, supervised exposure: junior Threat Operators can review AI-generated findings, examine how intelligence informs hunting, and learn from decisions made by senior colleagues — but only if organizations invest in technical fundamentals and structured mentorship. Analysts must still learn networks, operating systems, attacker techniques, and the security technologies that underlie AI workflows; experienced practitioners must teach how to evaluate conclusions and exercise judgment when evidence is incomplete.
Four areas of expertise Threat Operators must master
The piece lays out four combined expertise domains that will define the role:
- Business security risk — understanding priorities, critical assets, and consequences of defensive decisions;
- Threat and adversary understanding — interpreting intelligence and anticipating attacker behavior;
- Defensive operations — detection, hunting, investigation, and response across the lifecycle;
- AI orchestration and judgment — directing agent workflows, evaluating conclusions, and governing automated actions.
Practically, Threat Operators will translate risk into actionable objectives for AI, validate hypotheses and evidence, set escalation criteria, and decide whether an automated action achieved its intended outcome — for example, whether an AI-recommended isolation of a server is acceptable given the server's operational dependencies.
What this means for junior analysts, security leaders, and financial institutions
- Junior analysts: Expect a different apprenticeship. Rather than primarily doing repetitive triage, they will review AI reasoning chains, validate evidence, and learn through mentorship focused on judgment and context.
- Security leaders: The article urges building training, governance, and progression frameworks now — including rules for which decisions require human approval, how autonomy expands with demonstrated reliability, and how to evaluate operator performance using outcome-focused measures.
- Financial institutions (and similar enterprises): The piece uses a financial institution facing a threat to identity infrastructure as an example, noting that AI agents could assess exposure, hunt for relevant activity, identify detection gaps, and recommend actions — while the Threat Operator supplies institutional context about critical systems and acceptable risk.
Conifers.ai’s CognitiveSOC and operational evidence trails
The article mentions Conifers.ai’s CognitiveSOC platform as an example of agentic AI connecting intelligence, hunting, detection engineering, investigation, and response. According to the source, every agent action in that platform comes with a reasoning chain and evidence trail that analysts can review — an architectural detail the article highlights as central to enabling human review and governance of automated activity.
The Hacker News concludes that security professionals will have more say in how their organizations defend themselves and that the "AI-native SOC has to train them to operate the defense." Security leaders are advised to start building the governance, training, and progression frameworks that will make threat operation practicable — defining approval points, validation practices, autonomy boundaries, and outcome metrics such as the quality of defensive decisions, closure of detection gaps, and improvements in threat coverage.