Latest Analysis

Cybersecurity intelligence, threat analysis, and national security reporting.

Technicians work in a semiconductor fabrication facility cleanroom with rows of equipment and workstations.

US AI Lead at Risk as Chip Controls Weaken

The US risks losing its lead in artificial intelligence to China by 2028 unless export controls on advanced computer chips are tightened, according to a report by Anthropic. Without stricter controls, the US advantage in frontier AI development will quickly narrow.

Analyst 207
Dimly lit underground space with rows of beds and people milling about near a distant entrance with soft daylight.

Forum Vigilantes Enforce Order in Online Discussion

Discover the ultimate underground getaway in London, where 4,000 cozy beds await Festival of Britain visitors at an unbeatable rate of just three shillings a night. Located a mile long and 45 feet beneath the underground railway, the Clapham deep shelter offers a unique and affordable place to stay.

Analyst 207
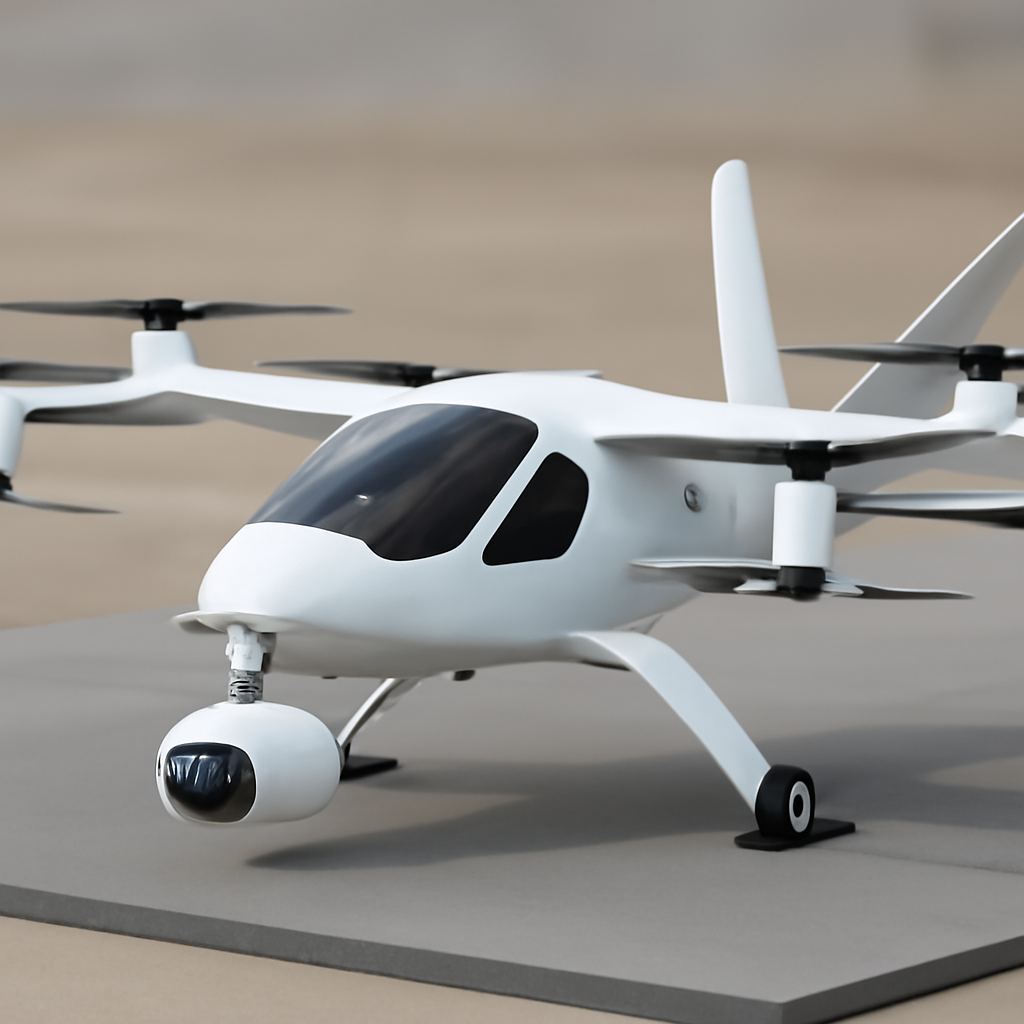
Sleek hybrid-electric VTOL aircraft on exhibition stand with blurred background.

AIRO Unveils Hybrid-Electric VTOL Drone for Resupply Missions

Meet AIRO's game-changing hybrid-electric VTOL drone, designed for resupply missions in remote areas where traditional charging infrastructure is scarce. With its versatile JC250 cargo and JX250 ISR variants, this cutting-edge platform is poised to revolutionize defense, government, and commercial operations.

Analyst 207
Gas station attendant checks fuel level on tank gauge screen in dimly lit storage room.

Iran Targets US Gas Stations with Tank Reader Hacks

US gas stations have been targeted by Iranian hackers, who manipulated fuel level readings at vulnerable sites, sparking concerns of a potentially catastrophic cyber attack. The breach highlights the alarming threat of kinetic cyber attacks, with experts warning of the devastating consequences.

Analyst 207
Cloud storage workstation with blank laptop screen and keyboard, symbolizing a data breach.

ShinyHunters Fuel Surge in Data Leaks

Meet the ShinyHunters, a notorious group behind a surge in public data leaks, who team up with The Com to scam victims out of cloud system access and then hold their data for ransom. This duo's alarming tactic has resulted in a steady stream of sensitive information being dumped into the public domain.

Analyst 207
Researchers collaborate in a modern lab with AI equipment and large display screens showing code visualizations.

Microsoft Unveils 100-Agent AI System for Advanced Bug Hunting

Microsoft has just unveiled MDASH, a game-changing AI system that leverages 100 specialized agents to supercharge bug hunting and vulnerability discovery. This cutting-edge technology combines multiple AI models to outperform traditional single-model approaches, giving enterprises a powerful new defense against cyber threats.

Analyst 207
Retail checkout counter with payment terminal and WooCommerce logo, laptop screen blurred with loading animation, hinting…

Funnel Builder Plugin Exploited to Inject Credit Card Skimmers

A vulnerability in the popular Funnel Builder plugin, used on over 40,000 websites, has been exploited to inject credit card skimmers into WooCommerce checkout pages, putting sensitive payment data at risk. This flaw allows attackers to sneak malicious code into checkout pages, harvesting valuable information from unsuspecting customers.

Analyst 207
Locked cabinet with combination dial in a dimly lit, institutional office setting.

Ransomware Gangs Test Trust with Data Deletion Promises

Can you ever trust a ransomware gang's promise to delete stolen data? The recent Instructure breach has brought this question to the forefront, leaving victims wondering if paying up is worth the risk of broken promises.

Analyst 207
Brightly-lit conference room with rows of seating and a prominent stage.

Hackers Disrupt Microsoft Exchange, Windows 11 at Pwn2Own Contest

Security researchers just scored big at Pwn2Own Berlin 2026, raking in $385,750 for exploiting 15 zero-day vulnerabilities in top tech targets like Microsoft Exchange and Windows 11. The contest, running from May 14-16, offers up to $1 million in prizes for hacking the latest enterprise technologies.

Analyst 207
Rows of rack-mounted computer equipment and cables in a neutral-colored server room.

Turla Upgrades Kazuar Backdoor to Modular P2P Botnet

Microsoft's Threat Intelligence team has uncovered a significant upgrade to the Kazuar backdoor by the notorious Russian state-sponsored group Turla, now a modular P2P botnet designed for long-term intelligence collection. This move enables Turla to maintain a persistent grip on compromised systems.

Analyst 207
Developer installing software on laptop at cluttered desk with subtle signs of malware in the background.

Node-ipc Package Infected with Credential-Stealing Malware

A malicious update to the widely-used node-ipc library has infected thousands of projects with credential-stealing malware, posing a significant supply-chain risk for developer environments and CI systems. With over 690,000 weekly downloads, this single compromised library could be exfiltrating sensitive data from countless unsuspecting users.

Analyst 207
Laptop on a clean surface with a blurred screen, surrounded by ordinary indoor lighting.

OpenClaw Flaws Expose Data, Enable Privilege Escalation

A chain of four vulnerabilities, dubbed Claw Chain, in OpenClaw can be exploited to turn an agent into a powerful tool for attackers, allowing them to extract sensitive data, escalate privileges, and plant backdoors for long-term access. This flaw chain enables adversaries to gain a foothold, move undetected, and wreak havoc on an OpenClaw-managed environment.

Analyst 207
Web development workspace with laptop and coding materials on desk.

Avada Builder Flaws Expose WordPress Sites to Credential Theft

A critical vulnerability in the Avada Builder WordPress plugin, used by an estimated one million active installations, leaves sites exposed to credential theft and data breaches. Two flaws, CVE-2026-4782 and CVE-2026-4798, allow attackers to read sensitive files and extract database information, putting your site at risk.

Analyst 207
Laptop screen on a desk shows a blurred password manager page with a hand hovering over the keyboard.

Microsoft Alters Edge to Mitigate Password Exposure Risk

Microsoft is taking a major step to boost password security in its Edge browser, rolling out a defense-in-depth change to mitigate the risk of password exposure. This update will be applied across all supported Edge versions, prioritizing a swift rollout to protect users.

Analyst 207
Dimly lit, cluttered room with computer and stacks of dusty papers.

REMUS Infostealer Targets Session Theft, Password Managers

Meet REMUS Infostealer, a rapidly evolving threat that's been making waves in the underground scene since February 2026, with its operators boasting a staggering 90% callback rate thanks to top-notch crypting and a dedicated server. This infostealer has quickly become a commercialized and professionalized menace, with a flurry of updates, features, and customer communications flooding the dark web.

Analyst 207
City transit platform with people in background and laptop on blurred table in foreground.

Gremlin Stealer Evolves with Advanced Evasion Tactics

In just 12 months, the Gremlin stealer malware has transformed from a basic credential harvester to a sophisticated modular toolkit that can stealthily siphon sensitive information from compromised systems. Its latest variant now specifically targets Chromium-based browsers, making it an even more formidable threat.

Analyst 207
Dimly lit server room with humming racks and tangled cables, showing signs of system distress and potential failure.

Autonomous AI Exposes Gaps in Enterprise Resilience Plans

As organizations deploy autonomous AI, they're exposing gaps in their resilience plans, putting business continuity at risk and creating new operational and infrastructure challenges for IT teams to navigate. Traditional security and recovery models are ill-equipped to handle the machine-speed, dynamic environments that autonomous AI creates.

Analyst 207
Brightly-lit network operations center with a large wall-mounted screen displaying security data.

Securing Autonomous AI Requires New Risk Strategies

Autonomous AI agents are revolutionizing enterprise environments with lightning-fast speed, unprecedented autonomy, and access to sensitive systems and data - but many security teams lack the visibility and control to manage the resulting risks. This game-changing technology is rapidly expanding the enterprise attack surface, demanding new risk strategies to stay ahead.

Analyst 207
Worker looks concerned at laptop screen in office setting.

AI-Powered Phishing Scams Evade Detection in Workplace

Phishing scams are getting sneakier, with 72% of people saying AI-powered attempts are more convincing than ever - and 57% believe AI makes them harder to spot because they seem more professional. As a result, employees are struggling to tell the difference between genuine workplace messages and fraudulent ones.

Analyst 207
Modern corporate office interior with a large blank screen in a sleek conference room.

Autonomous AI Exposes Governance Gaps in Enterprise Security

As autonomous AI revolutionizes enterprise security, it's also revealing alarming governance gaps that can leave organizations in highly regulated environments exposed to unprecedented risks. The rapid adoption of autonomous AI is creating a trust gap, where innovation outpaces control, and novel risks to visibility, control, and regulatory compliance are emerging.

Analyst 207
A laptop on a simple desk in a corporate office with a blurred background of cubicles and a hint of a coding workspace on…

TanStack Supply Chain Attack Targets OpenAI, Forces macOS Updates

OpenAI sprang into action after detecting a sneaky supply chain attack targeting TanStack, quickly investigating and containing the threat to protect its systems. The attack impacted just two employee devices, with limited internal code repositories and credential material compromised.

Analyst 207
Executives in a meeting room discuss technology with laptops and notes nearby.

Enterprises Lag in AI-Agent Risk Mitigation Despite Funding

Most enterprise leaders are bracing for a major security breach or fraud incident driven by AI agents within the next year, yet their organizations are woefully unprepared to mitigate the risks. A recent survey of 300 security leaders reveals a stark gap between threat awareness and adequate safeguards.

Analyst 207
Large, open office space with workstations and people, featuring a blank whiteboard on the wall.

Autonomous AI Exposes New Risks in Enterprise Environments

As autonomous AI weaves itself into the fabric of enterprise operations, it brings a new wave of complexity and unpredictability, testing the limits of infrastructure and IT teams like never before. The result? A whole new landscape of operational and infrastructure risks that threaten to upend traditional security and recovery models.

Analyst 207
Busy office scene with wireless devices and equipment on a table, surrounded by people working.

Wireless Vulnerabilities Skyrocket, Outpacing Traditional Threats

The number of wireless vulnerabilities has skyrocketed, with a staggering 937 new threats discovered in 2025 alone - that's 2.5 new vulnerabilities every day. This represents a 60% increase since the start of 2024, and a growth rate that's 20 times faster than traditional threats over the last 15 years.

Analyst 207