[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it alongCybersecurity intelligence, threat analysis, and national security reporting.

The financial sector saw a staggering 2.41 billion network- and transport-layer denial-of-service attacks in 2025, with banking bearing the brunt, accounting for 60% of total web attacks and over 80% of API-related incidents. TurboMirai, a powerful AI botnet, was a key driver of this alarming surge, fueling attacks that lasted a whopping 738% longer than usual.
GitHub's internal repositories were breached after a malicious Visual Studio Code extension was used to launch the attack, but thankfully, customer data appears to be safe. The incident has left users wondering what else may have been compromised.

A critical Linux flaw, dubbed PinTheft, has been exploited, allowing local attackers to gain root privileges on affected systems through a complex vulnerability in the Reliable Datagram Sockets (RDS) code. This security gap can be triggered by a specific interaction between RDS zerocopy and io_uring fixed buffers.

Typosquatting has morphed into a sinister supply chain threat, with attackers now embedding malicious lookalike domains within legitimate third-party scripts to intercept sensitive data. This alarming evolution has led to devastating attacks, such as the Trust Wallet compromise, where 2,500 wallets were drained in just 48 hours.

GitHub's security team swiftly contained a breach that exposed 3,800 internal repositories to a malicious VS Code extension, and immediately took action to prevent further damage. The company has completed critical secret rotations and is now meticulously analyzing logs to ensure the incident is fully resolved.
The Metropolitan Police made a staggering 700,000+ requests to tech companies in 2025 to access private communications data, helping officers solve crimes, find missing people, and gather crucial intelligence. This massive surge in data requests highlights the force's growing reliance on digital information to keep London safe.

Microsoft has stepped in to squash a newly revealed BitLocker bypass exploit, dubbed YellowKey, by releasing crucial guidance to protect users from potential attacks. This security move comes after a researcher demonstrated how the exploit could spawn a shell with unrestricted access to sensitive data.
Millions of users are under attack by the CypherLoc scareware, with Barracuda researchers tracking around 2.8 million attacks since January 2026 alone. This staggering number reveals a coordinated and widespread campaign that's putting tens of millions of people at risk.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
For the first time in nearly two decades, exploiting vulnerabilities has surpassed compromised credentials as the top breach entry point, accounting for 31% of data breaches over the past year. This significant shift suggests that threat actors are adapting their tactics, and defenders must follow suit.
GitHub recently uncovered a sneaky attack involving a tainted VS Code extension that compromised an employee's device, putting 3,800 repositories at risk. The breach was quickly contained, but not before some internal repositories were exfiltrated.
Microsoft has issued urgent guidance to mitigate a newly publicized Windows zero-day vulnerability, dubbed YellowKey, which could allow attackers to bypass security features. The tech giant is working on a fix, but in the meantime, it's urging users to follow its interim guidance to stay protected.

Grafana Labs recently reported a security breach that exposed source code and internal data, but fortunately, there's no evidence that customer production systems were compromised. The breach, detected on May 11, was confined to the company's GitHub environment and involved both public and private source code and internal repositories.

GitHub is investigating a possible internal breach after a hacking group claimed unauthorized access to its repositories. The company says it has no evidence that customer data has been compromised so far.

GitHub is investigating a security breach claim by hackers TeamPCP, who allegedly stole around 4,000 of the platform's internal repositories and put the source code up for sale for a hefty $50,000. The company has already sprung into action, detecting and containing the breach and taking steps to mitigate the risk.

As US and Israeli strikes on Iran intensified, Spain's Prime Minister Pedro Sánchez boldly declared, We are a sovereign country that does not wish to take part in illegal wars, effectively shutting the door on US forces at Naval Station Rota and the Morón Air Base. This move sparked a stern warning from President Donald Trump, threatening a full trade embargo on Spain.
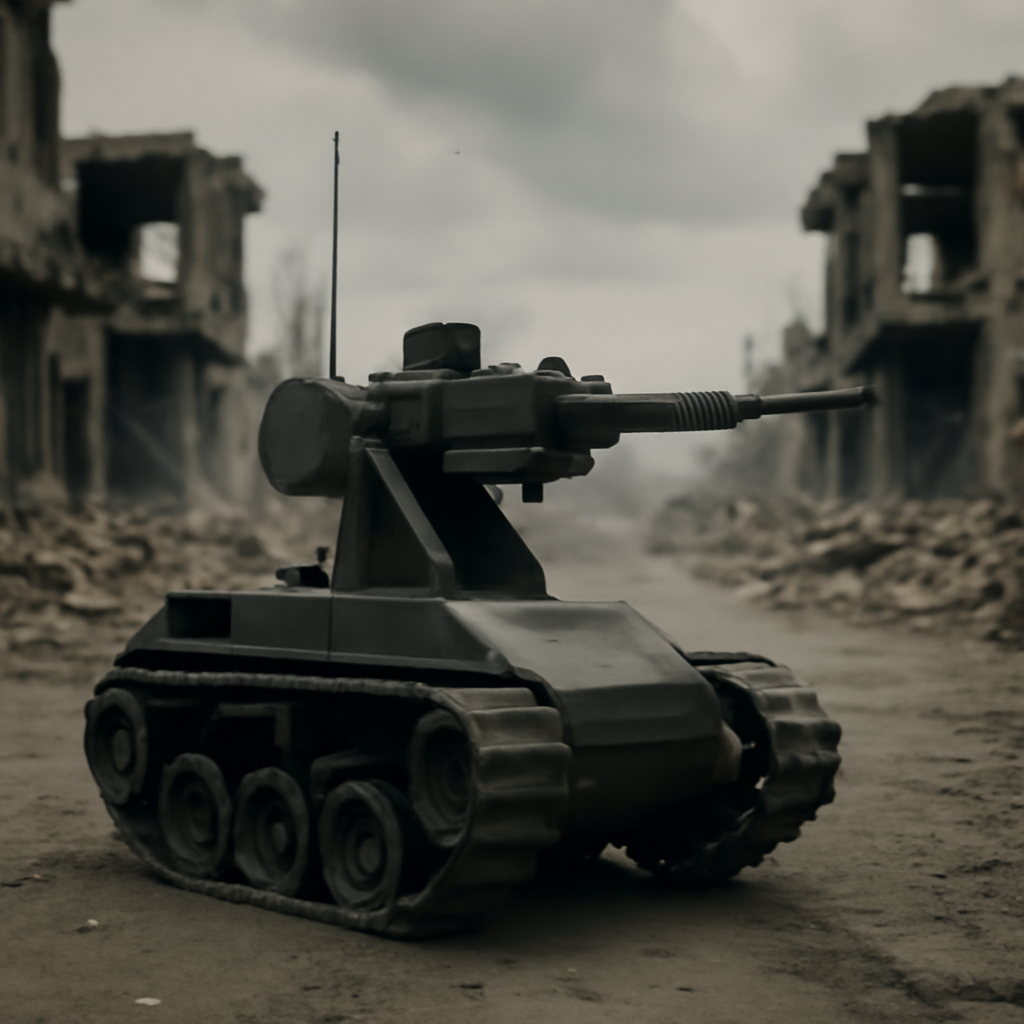
Meet the game-changing Droid TW 12.7, a remote-controlled ground robot that single-handedly defended a crucial intersection for 45 days, repelling enemy attacks and safeguarding Ukrainian lives. With its operator safely positioned 10 kilometers away, this robotic hero successfully disrupted every attempted breakthrough, proving to be a powerful force on the front lines.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
Meet BlitzBox, a game-changing containerized drone launch system that pairs a small, modular fixed-wing drone with a stealthy shipping-container launcher, offering unparalleled flexibility in electronic warfare and deception operations. This innovative system cruises at 40-75 knots, packing a powerful punch with its adaptable payload and endurance capabilities.
Defense Secretary Pete Hegseth is hitting the pause button on the Army Transformation Initiative, admitting that while some aspects are promising, others require a closer look. The move has sparked questions from lawmakers and military leaders about the future of the Army's overhaul.

Sweden is set to supercharge its air defense capabilities, with Prime Minister Ulf Kristersson announcing that the country's new Luleå class frigates will triple its ground- and surface-based air defenses. The decision to base the Luleå class on the French FDI frigate design marks a significant upgrade to Sweden's surface combatant fleet.

The Navy has just cleared a major hurdle with its MQ-25A Stingray drone refueler, reaching Milestone C and greenlighting low-rate initial production - a game-changing capability that enables unmanned inflight refueling and extends the lethality of Carrier Strike Groups. This advancement empowers the Navy to take its operations to new heights.

Russia just took a major leap in military aviation with the successful first flight of its two-seat Su-57 fighter, a game-changing aircraft that combines cutting-edge combat capabilities with advanced training and command functions. Developed independently by Russian manufacturers, this fifth-generation fighter is set to revolutionize the skies.
CENTCOM Chief Adm. Brad Cooper is calling for game-changing tech to tackle buried targets, emphasizing the urgent need for advancements in electronic warfare, counter-UAS systems, and munitions to strike hard-to-reach enemy hideouts. As the threat landscape evolves, Cooper stresses that investing in these areas is crucial to staying ahead.

US Special Operations Command is set to supercharge the AC-130J Ghostrider gunship with advanced cruise missiles and radar, boosting its firepower to strike targets over 400 miles away. The upgrade, part of the Precision Strike Package, promises to dramatically expand the aircraft's combat reach.
With attackers exploiting vulnerabilities at an alarming rate, it's clear that organizations are struggling to keep up with the pace of security defects - and it's leaving them exposed. Exploits have now become the top breach entry point, accounting for 31% of all known initial access vectors.