[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
Imagine owning a piece of history - a fully-equipped nuclear bunker that could shelter up to 235 people, complete with kitchen facilities, dormitories, and decontamination chambers, now on the market for £575,000. This underground shelter, built in 1990, is a unique opportunity to own a self-sufficient hideaway.
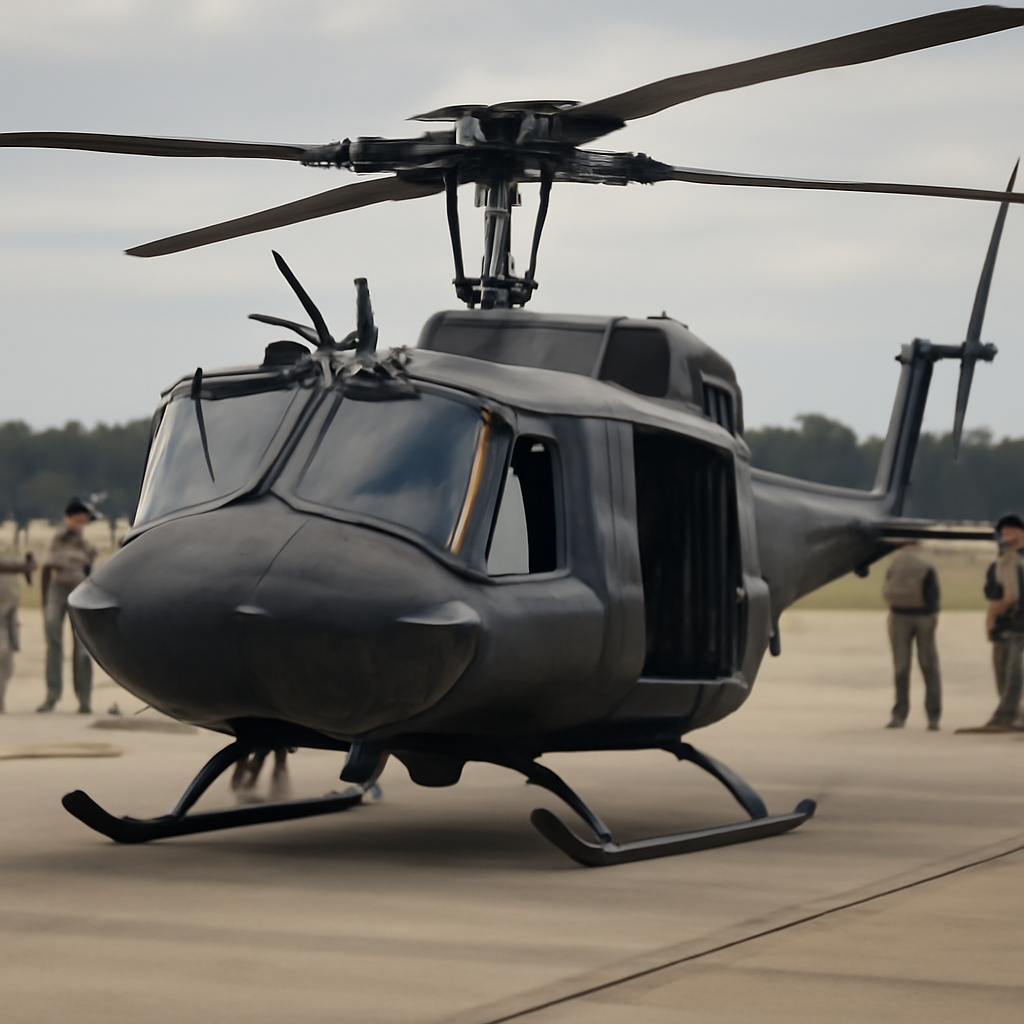
The Army has taken a giant leap forward in modernizing its aviation training with a $10 billion contract awarded to M1 Support Services, revolutionizing the way pilots learn to fly. This game-changing deal paves the way for a cutting-edge training model that lets pilots focus on mastering the essentials of aviation.
As the AI giants OpenAI and Anthropic face growing headwinds, including public backlash and market turbulence, some experts believe the US government should consider nationalizing these companies before they stumble. With their valuations already taking a hit, now may be the perfect time for the government to step in and catch them before they fall.
Anthropic is taking a proactive approach to transparency with AI-generated text by embedding watermarks globally, ensuring accountability and compliance with regulations like the EU AI Act. This innovative technique, inspired by Google DeepMind's research, helps distinguish AI-created content from human-written text.
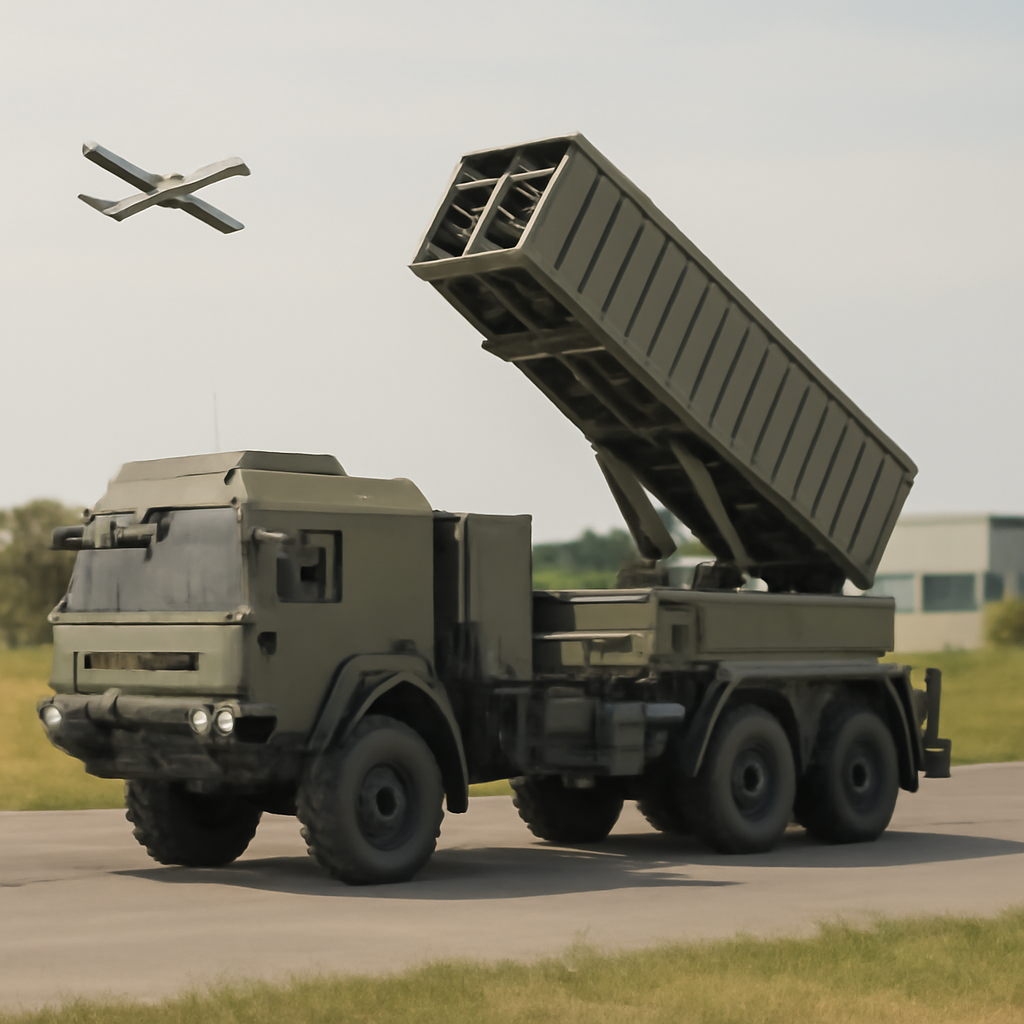
Imagine a game-changing weapon that can scout out its target, track it, and then strike with precision - all from a mobile launch platform. Rheinmetall's FV-014 loitering munition system makes it all possible, boasting a 100km range and 70-minute flight time.
The US Navy is exploring a game-changing strategy: building combat ships abroad, but experts warn that this approach is fraught with technical, logistical, and political hurdles. A senior policy researcher notes that the main challenge lies in the unknown territory of foreign shipbuilding for combat-type vessels.
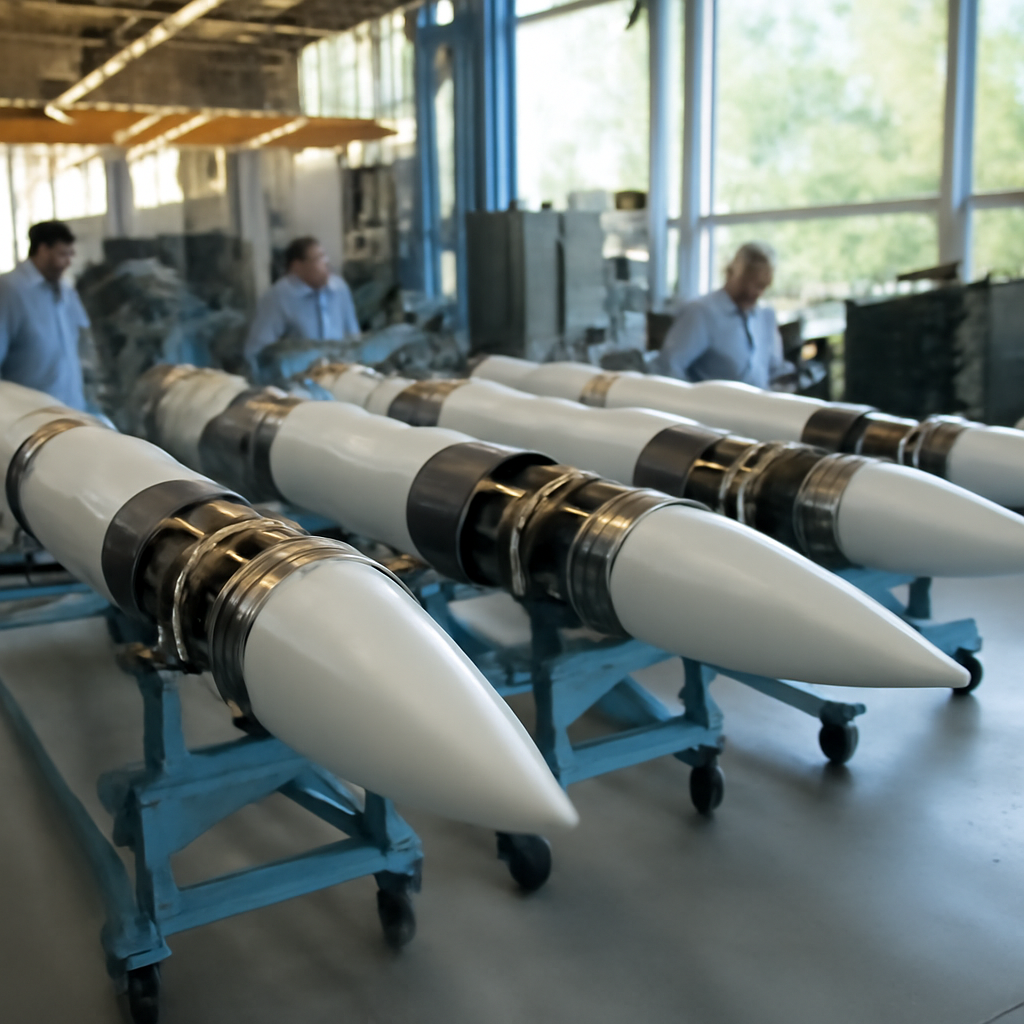
The Pentagon is bolstering its defenses with framework deals with Boeing and RTX to ramp up production of the SM-3 missile, a crucial component of the US and its allies' air and missile defense systems. This move strengthens the backbone of US sea-based missile defense, both at home and abroad.
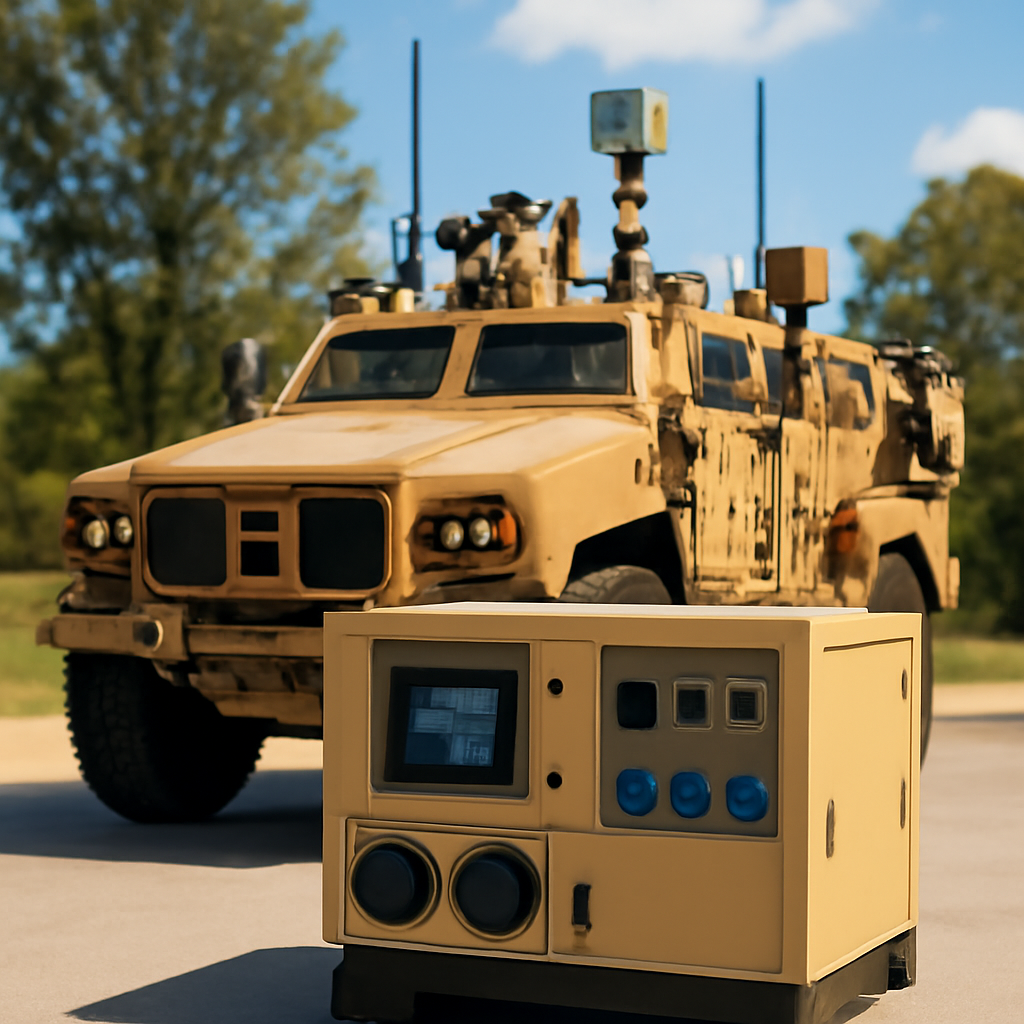
The Army is facing a pressing power problem: its vehicles lack the exportable power needed to fuel modern sensors, drones, and command centers, severely limiting operations. Brigade commanders are being forced to ration critical assets like unmanned aerial systems due to insufficient power, not mission requirements.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
The US Army is on a mission to develop a game-changing, lower-cost strike missile that can travel up to 1,000 kilometers, and their Affordable High Speed Strike (AHSS) program is already exploring two innovative design concepts. This new missile promises to be a total game-changer, offering unprecedented speed and range at a fraction of the cost.
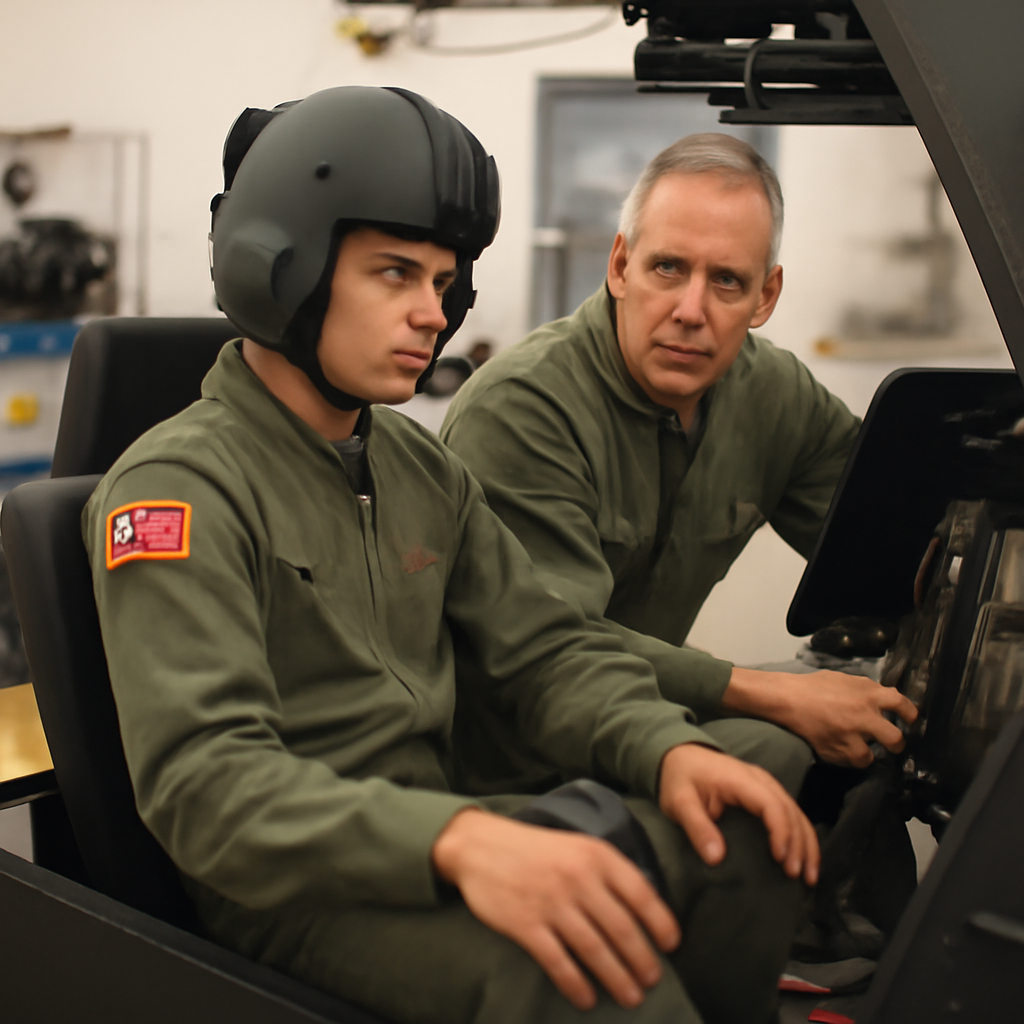
The Army is revolutionizing its helicopter pilot training program with Flight School Next, a cutting-edge initiative led by M1 Support Services, which promises to equip new pilots with top-notch skills. This game-changing program has secured a long-term contract worth up to $10 billion.
Meet the upgraded CoolClient Backdoor, now packing a kernel-level rootkit courtesy of the sneaky HoneyMyte APT Group - and it's hiding in plain sight with a legit digital signature. This clever malware uses a Windows service and a kernel-mode driver to evade detection.
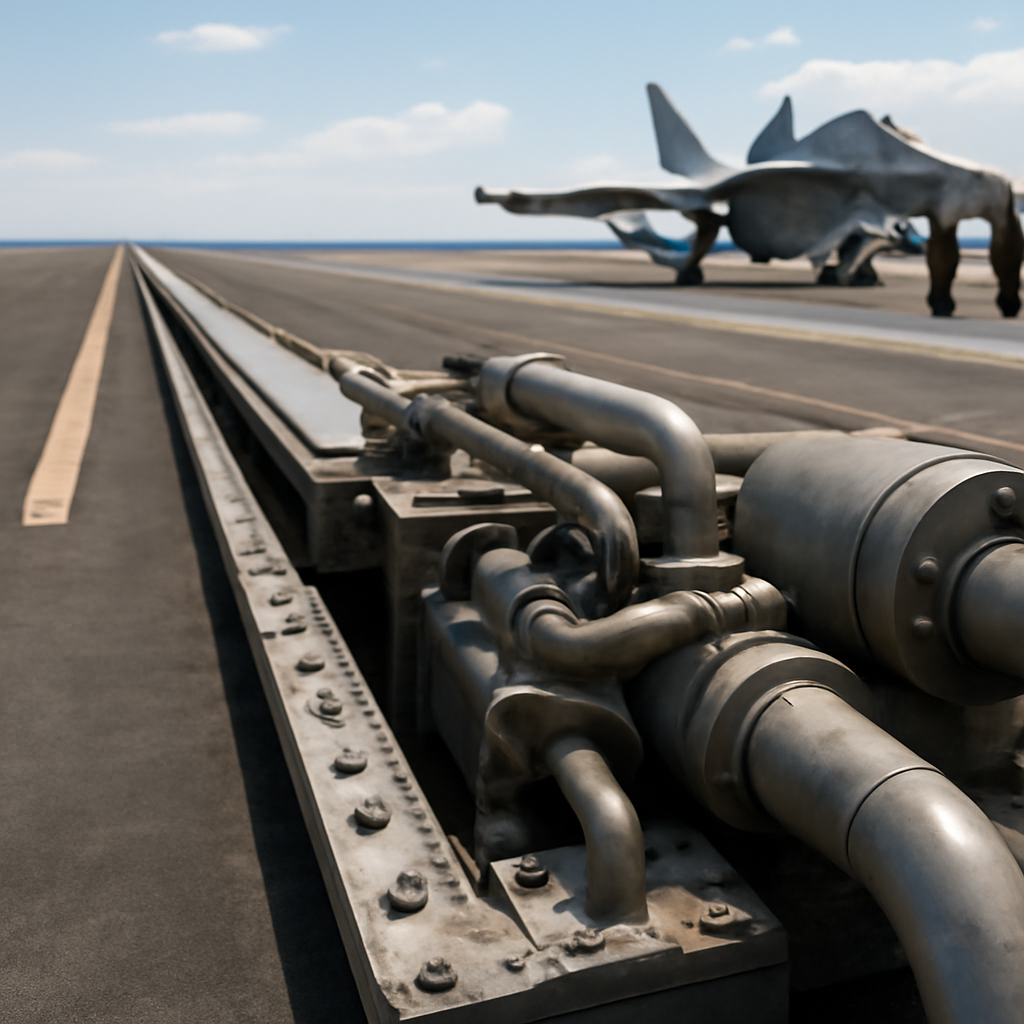
The White House is pushing the Pentagon to radically redesign the Ford-class carrier program, after President Trump issued a memo calling for a switch back to steam catapults, a technology that's been around for 50 years. This abrupt change has left the US Navy facing significant risks and a tight 60-day deadline to come up with a new plan.
In a move with far-reaching implications, Saudi Arabia, Pakistan, and Turkey have inked the Mecca Joint Deterrence Agreement, pledging to consider an attack on any one of them as an attack on all three. This bold pact, signed by the leaders of the three nations, cements their unity and shared commitment to strategic interests.
The US naval presence in the Taiwan Strait is dwindling at an alarming rate, with a projected 50-56% decline in transits under the current administration compared to the previous two, dropping from 28 and 32 to just 14 publicly reported transits. This significant decrease marks a sharp departure from the norm.
In a massive €30M heist, hackers exploited a vulnerability in a service provider's software, making unauthorized direct debits from Commerzbank customer accounts in 2023, but fortunately, no customers suffered financial losses. The incident highlights the risks of relying on third-party services and the importance of robust security measures.
A massive data breach at RingCentral has exposed the sensitive information of 1.6 million customers, including names, addresses, phone numbers, and email addresses, which have been posted online by the hacker group ShinyHunters. This breach was discovered on July 28, and although RingCentral took swift action to stop the unauthorized activity, the damage has already been done.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Data breaches are surging out of control, with 1,803 compromises reported in the first half of 2026 alone, putting the year on track to shatter the 2025 record of 3,321 breaches. If this pace continues, 2026 could see a staggering 3,600 data compromises.
The French Tax Authority has confirmed a data breach after a hacker claimed to have stolen sensitive information from over 2 million taxpayers, exploiting stolen credentials and a security loophole. The breach was detected in June, and an immediate audit helped sever the unauthorized access.
Hackers are exploiting a recently fixed macOS security flaw to secretly deploy Monero miners, and experts warn that public exploit code is now available, putting users at risk. This vulnerability, affecting macOS's built-in Screen Sharing feature, allows attackers to gain access without valid credentials.
Meet ExfilSquad, a notorious data-extortion group that's made off with a whopping 27 million records and 382.64 GB of sensitive data from 13 major organizations across government, education, finance, and manufacturing. The stolen treasure trove was dumped online for all to see, courtesy of a simple misconfiguration in Microsoft Power Pages.
The traditional attack chain is getting a makeover: instead of starting with a malicious email, attackers now use OAuth apps to breach Google Workspace, exploiting new vulnerabilities in an AI-driven threat landscape. It's time to shift from an inbox-centric to an OAuth-first security approach to stay ahead.
The threat of autonomous AI attacks on critical infrastructure is no longer a distant possibility, but a looming reality that could unleash devastating kinetic disasters, warns Tom Kellermann, VP of AI security and threat research at TrendAI. The perfect storm of rising geopolitical tension and increasingly powerful off-the-shelf AI agents makes a crippling attack on our infrastructure not just plausible, but imminent.
Hackers are actively exploiting a critical vulnerability in SAP Commerce Cloud, allowing them to remotely execute code without any login credentials. This severe flaw, tracked as CVE-2026-58231, was patched by SAP just three days before attacks began.
Meet Evooo1Bot, a newly identified Mirai-derived Linux botnet that's turning devices into proxies by exploiting vulnerabilities, and has been actively targeting internet-facing devices since July 2026. Its operators have been using a single loader URL to launch attacks, allowing researchers to track and identify the malware.