Tag: supply chain
1740 articles
BdThemes plugins compromised in supply-chain attack
A stealthy supply-chain attack on BdThemes plugins has turned into a high-stakes problem, putting over 350,000 active WordPress installations at risk. The breach affects popular plugins like Element Pack, Prime Slider, and others, prompting the WordPress Plugins team to swiftly pull them from download.
Defense Sector Bolsters Undersea Capabilities with $8.7 Billion Investments
The defense sector is making a splash with a whopping $8.7 billion investment to strengthen its undersea capabilities, with Lockheed Martin leading the charge by acquiring Ultra Maritime in a $3.5 billion deal. This massive move is set to bolster the sector's underwater defenses, amid growing concerns over China's expanding subsea sensor and unmanned systems efforts.
Royal Navy's Drone Boats Expose Cyber Vulnerabilities
The Ministry of Defense swiftly addressed a cyber vulnerability in the Royal Navy's Kraken K3 Scout unmanned surface vessels after a routine check exposed a weakness in the camera system, and promptly cut off internet connectivity to prevent any potential breaches. The MOD assured that its quick action and follow-up investigation found no evidence of data or system compromise.
NATO, AI Startup Gain Power to Track Software Vulnerabilities
The cybersecurity landscape just got a major boost: NATO's Cyber Security Centre and AI startup AISLE have joined forces with ENISA to supercharge vulnerability management, bringing the total number of CVE numbering authorities to 20. This powerful collaboration aims to revolutionize the way we track software vulnerabilities and stay one step ahead of cyber threats.
China-Linked Hackers Deploy StormEncryptor Ransomware via N-central Flaw
Meet StormEncryptor, a sneaky new ransomware strain linked to China that's leaving a trail of encrypted files and ransom notes in its wake. This malicious software, written in C++, is marked by its telltale .encrypted file extension and !!!README_FIRST!!!.txt ransom notes.
Ransomware gangs exploit SonicWall SMA1000 flaws
Ransomware gangs are actively exploiting two recently patched flaws in SonicWall's SMA1000 remote-access gateway, which can let attackers hijack vulnerable servers and send requests on their behalf. The vulnerabilities, tracked as CVE-2026-15409 and CVE-2026-15410, were patched in mid-July, but threat actors are now using them in real-world attacks.
WordPress Plugins Targeted by Rogue Feed Exploits
Hackers have found a sneaky way to exploit WordPress plugins, using a promotional banner feed to plant rogue administrator accounts and webshells on live sites - all without modifying a single plugin file. The attack, traced back to an unescaped field in a banner notice, has already hit seven plugins from a popular Elementor add-on vendor.
TrueConf Server Flaws Targeted to Deploy PhantomCore Backdoor
Security researchers at Kaspersky have uncovered a sneaky plot by threat actor Head Mare to exploit unpatched TrueConf servers and deploy the PhantomCore backdoor to unsuspecting users. The attack relies on a two-stage vulnerability chain that allows attackers to run malicious commands with high-level privileges.
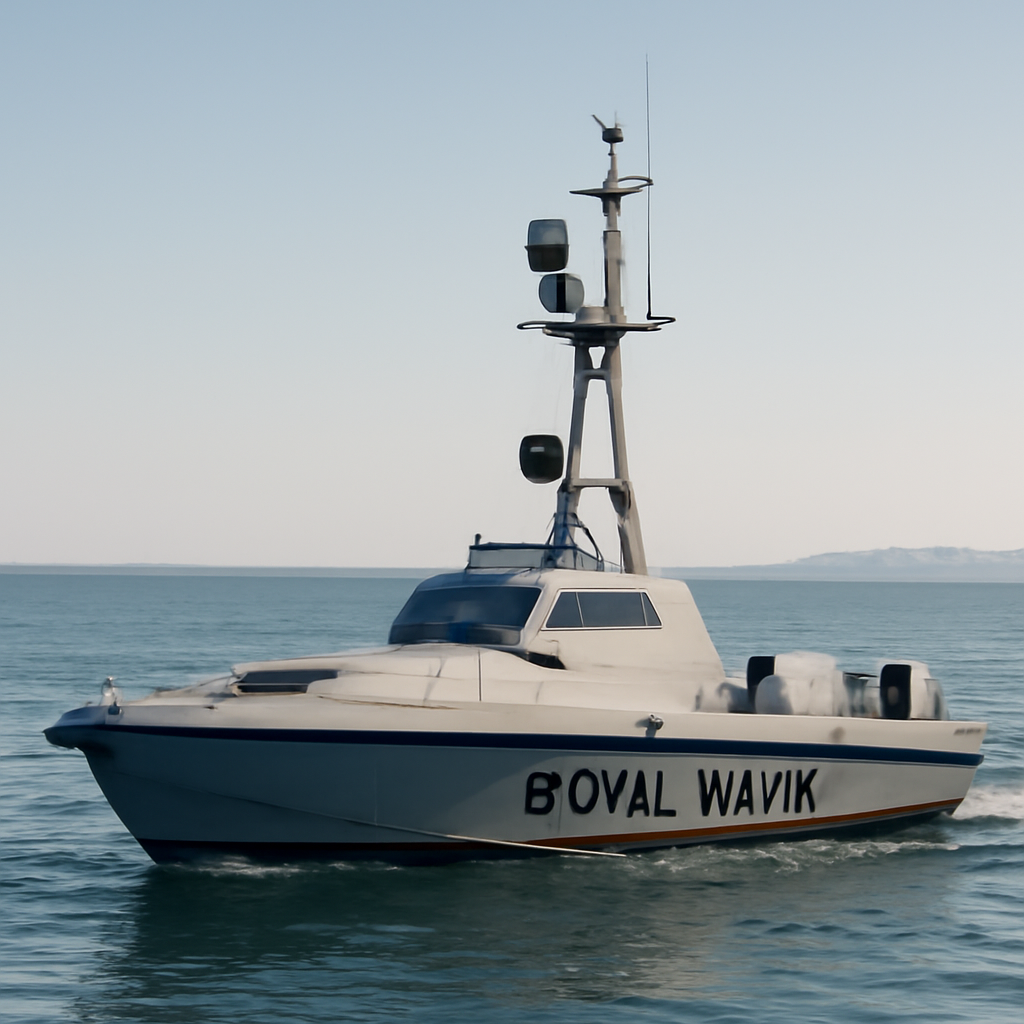
Royal Navy drones transmit data to China in cyber vulnerability test
Royal Navy drones recently raised eyebrows when their cameras started sending signals to a Chinese IP address during a routine cyber vulnerability test, sparking concerns over data security. The Ministry of Defence quickly stepped in to reassure that no sensitive data was compromised, and the transmission was just a harmless "heartbeat" signal.
Valve Exposes Steam Hardware Customer Data Breach
A recent cyberattack on CEVA Logistics, a shipping partner for Steam hardware in Europe, exposed sensitive customer data, including names, addresses, phone numbers, emails, and order details, between July 29 and August 1, 2026. Valve has notified affected customers about the breach, which may have compromised their personal information.
Metabase Zero-Day Exploited to Breach Framework Customer Data
A zero-day exploit in analytics provider Metabase has led to a data breach at laptop maker Framework, exposing personal customer information, and prompting a review of its data storage methods with external vendors. Metabase has since patched the bug, blocked attack endpoints, and deployed a fix across its cloud service to prevent further exploitation.
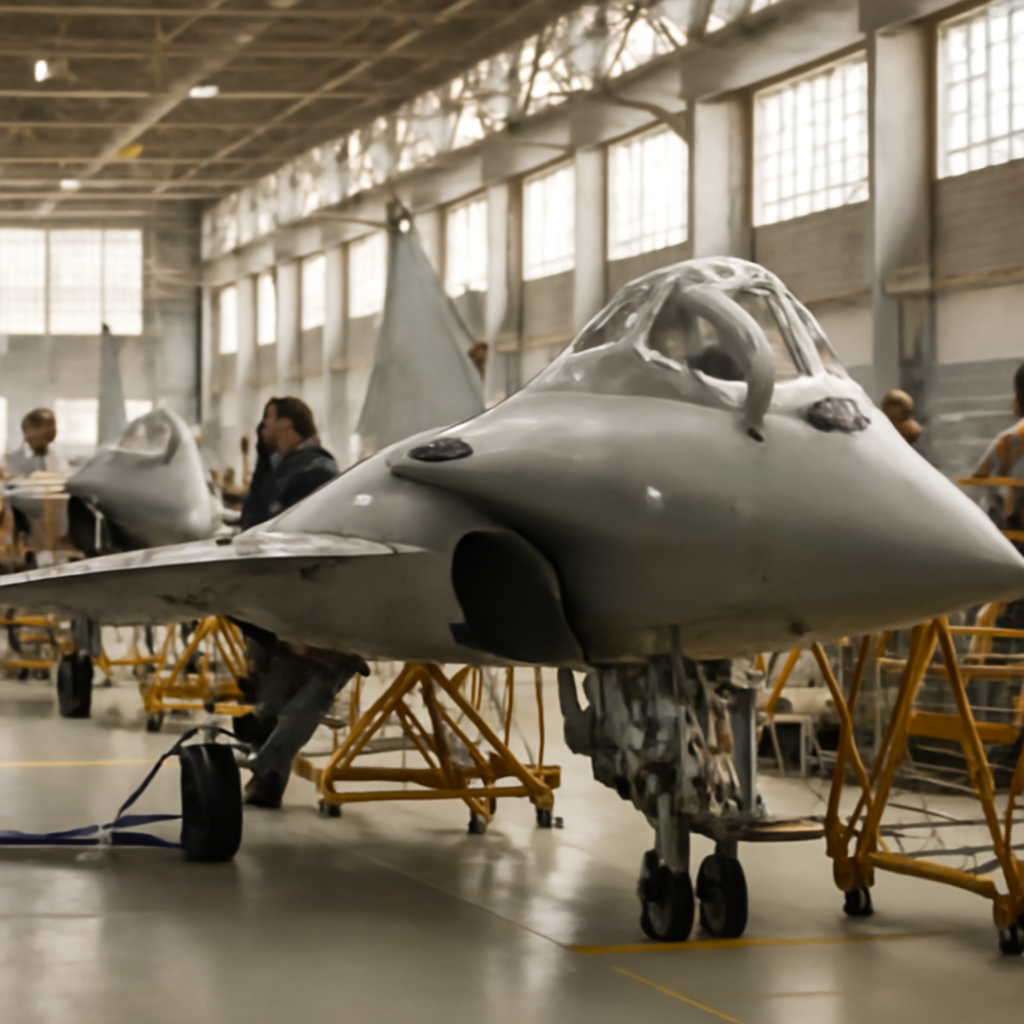
Dassault Targets India with 114-Rafale Bid
Dassault Aviation has thrown down the gauntlet with a bold bid to supply 114 Rafale fighter jets to the Indian Air Force, comprising 20 flyaway aircraft and 94 built in India. This ambitious proposal is now under evaluation by India's Ministry of Defence and the IAF.
Australia's North Requires Systems Overhaul for National Resilience
Imagine a 2,800 km lifeline stretching across Western Australia, the Northern Territory, and Queensland, transforming the north into a national strategic powerhouse that supercharges freight resilience, disaster response, and supply chains. The Outback Way is more than just a transport project - it's a game-changer for Australia's national resilience.
Ransomware Gangs Target Mid-Level Managers to Accelerate Payments
Ransomware gangs are now taking a sniper approach, targeting mid-level managers with precision to get payments faster. This new tactic is a far cry from the scattergun methods of the past, with one recent campaign hitting 351 victims across 334 organizations in just a month.
Hackers Breach TrueConf Servers to Deploy Backdoors via Trojanized Updates
Hackers have breached TrueConf servers by exploiting a gaping security hole - an open TCP port that lets them in without needing a password, then using trojanized updates to deploy backdoors and take control. This sneaky attack vector has been used by threat actors like Head Mare to spread malware and gain unauthorized access.
N-able Bolsters Defenses as Attackers Exploit RMM Flaw
N-able is stepping up its defenses with a second hotfix for its N-central Remote Monitoring and Management product, proactively expanding protections to stay ahead of evolving attack techniques that exploit a recently disclosed vulnerability. This latest update is a must-apply, even if you've already installed the earlier hotfix, as it includes crucial additional hardening measures to safeguard you and your customers.
Metabase Zero-Day Exploits Grant Admin Access
A critical zero-day vulnerability in Metabase allows hackers to gain admin access and wreak havoc on your data, with a perfect 10.0 CVSS score highlighting the severity of this threat. Attackers can inject malicious SQL, steal sensitive credentials, and export data, making immediate patching a top priority.
Malicious npm Packages Deliver Cross-Platform Malware
Nearly 800 malicious npm packages have been discovered delivering a potent cross-platform malware payload, including a remote access trojan and infostealer, via a sneaky trick that tricks developers into loading the malicious code. These packages use cleverly crafted names and README instructions to evade detection and deploy the WEL1DROPPER downloader.
US Coast Guard Monitors Cyberattack Disrupting North Carolina Ports
A cyberattack brought North Carolina's ports to a grinding halt, forcing delays and manual processing at the Port of Wilmington, the Port of Morehead City, and the Charlotte Inland Port. The U.S. Coast Guard is now monitoring the situation and coordinating a response with partner agencies to get operations back on track.
Ransomware Attacks Surge 20% as New Gangs Target Finance, Healthcare
Ransomware attacks are on the rise, surging 20% in July with a staggering 799 incidents reported, with finance, healthcare, and tech industries becoming prime targets for new gangs. The alarming increase marks the second-busiest month of the year so far, with the US leading the list of targeted countries.
N-able Flaw Exposes Customer Networks to Attackers
A critical vulnerability in N-able's N-central platform, known as CVE-2026-18577, has been exploited by attackers to gain unauthorized access to customer networks, allowing them to take control of managed endpoints. This flaw gave attackers an open door to wreak havoc, and it's essential for affected users to take immediate action to protect themselves.
Cyberattackers Hijack Legitimate Emails, Payments in Twin 2026 Campaigns
Cyberattackers are sneaking into legitimate emails and payments, exploiting our trust in everyday business communications to pull off scams that now account for almost 46% of all threat detections. They're using ordinary emails like shipment notices and invoice prompts, often sent from compromised corporate mailboxes, to carry out banking malware campaigns.
Cyberattack Disrupts North Carolina Ports Operations
A cyberattack has brought North Carolina's ports to a grinding halt, causing a systems-wide outage that has delayed operations and truckers at the Port of Wilmington, the Port of Morehead City, and the Charlotte Inland Port. Gates at all three locations are now back to a normal operating schedule, but the impact of the disruption is still being felt.
Open Source Software Faces Reckoning
Open source software had a carefree adolescence, running wild and free for two decades, but its idyllic era is now coming to an abrupt end, forcing it to confront a harsh new reality. It's time for open source to grow up and face the challenges of a rapidly changing world.