Tag: nation state
1338 articles
CubePilot Hit by DNS Hijacking to Intercept Traffic
On July 24, a DNS hijacking attack hit CubePilot, allowing hackers to intercept traffic and potentially capture sensitive credentials from visitors to their portal and forum. The attackers obtained TLS certificates for all cubepilot.org subdomains, making their scam nearly undetectable.
Mirage Kitten Unveils New Malware Arsenal for Middle East Espionage
Mirage Kitten hackers have unleashed a potent new malware arsenal targeting the Middle East, threatening aerospace, aviation, defense, and telecom organizations with stealthy backdoors and tunnelers that enable covert surveillance and data relay. Their latest Windows backdoor, NightLedger, masquerades as a legitimate system file to infiltrate and gather intel.
US, Australia Urge Critical Infrastructure to Isolate Vital Systems During Cyberattacks
Stay ahead of cyber threats: the US and Australia are urging critical infrastructure operators to isolate vital systems during cyberattacks to minimize damage and protect essential services. A new advisory provides practical guidance on how to plan for and execute a safe disconnection from vulnerable networks.
SSO Security Requires Proactive Defense Against Credential Attacks
A single compromised SSO account can become a master key, unlocking a vast array of sensitive services and putting millions of individuals at risk, as seen in the 2025 University of Pennsylvania breach where 1.2 million people's data was stolen. Proactive defense against credential attacks is crucial to protecting your organization's security.
Iranian Hackers Deploy NightLedger Backdoor in Global Espionage Campaign
Meet NightLedger, a sneaky new Windows backdoor that's part of a sophisticated espionage toolkit used by Iranian hackers to secretly infiltrate and gather intel from targets worldwide. This powerful tool enables hackers to execute commands, capture screenshots, and operate undetected, putting organizations in the Middle East, Africa, and South Asia on high alert.
NVIDIA Launches Open Secure AI Alliance Without Key Players
NVIDIA is shaking up the AI security landscape with the launch of the Open Secure AI Alliance, a groundbreaking coalition of nearly 40 tech giants, including Adobe, Cisco, and Microsoft, dedicated to developing open-source security tools to safeguard artificial intelligence. By joining forces, they're building a robust defense stack to protect AI agents from identity threats to secure coding workflows.
Legacy Technology Exposes Nations to Growing Cyber Risk
The clock is ticking: with legacy technology, organisations know the risks, but lack a mechanism to spark change, leaving nations vulnerable to growing cyber threats. As exploits and AI evolve at breakneck speed, the window for protection is shrinking fast.
Phishing Campaign Operation BlueDash Targets Teams Users with RMM Tools
Beware of Operation BlueDash, a sneaky phishing campaign that tricks Microsoft Teams users into downloading malicious RMM tools by masquerading as a genuine Microsoft Store update. Victims are cleverly directed to a fake store page that claims Teams needs to be updated to access a shared document.
TELESHIM Malware Exploits Telegram for C2 in Middle East Attacks
TELESHIM malware has launched a sophisticated attack in the Middle East, using a multi-stage chain to infect systems and cleverly leveraging Telegram's API to disguise its command-and-control communications as legitimate internet traffic. This sneaky tactic allows the malware to blend in seamlessly, making it a formidable threat.
Google Unveils Cybercrime Taxonomy, Shakes Up Threat Naming Norms
Google is shaking up the world of cybercrime threat naming with a fresh approach, introducing a simple and streamlined taxonomy that's easy to map across different systems. The tech giant has teamed up with Mandiant to launch the Google Threat Intelligence Group, using a catchy two-word naming schema to identify cybercrime crews.
Botnets Persist Despite Takedowns, Fueled by Residential Proxy Networks
Botnets just won't quit, and it's no surprise why - there's a thriving market for access to millions of IPs, making it easy for them to keep growing and snaring more victims. Residential proxy networks are fueling this expansion, with nearly 60 million victim IP addresses globally and a significant chunk of them right here in the US.
Hackers Target Hotel Wi-Fi to Steal Microsoft 365 Accounts
Hackers are targeting hotel Wi-Fi networks to steal Microsoft 365 accounts from unsuspecting travelers, with a widespread campaign affecting various industries across multiple countries. This sneaky tactic redirects visitors to attacker-controlled sites, putting business travelers at risk of having their sensitive information compromised.
BlueNoroff Phishing Kit Targets Crypto Wallets with Zoom Lures
BlueNoroff's phishing kit is a masterclass in deception, using Zoom lures and compromised industry contacts to trick victims into divulging their crypto wallet info. This sophisticated scam combines social engineering and malware to selectively target high-value victims.
Hackers Leverage AI Tool Hermes to Breach Thai Finance Ministry Network
A careless mistake left 585 files and 470 MB of sensitive data exposed, as hackers used an open-source AI agent called Hermes to breach Thailand's Ministry of Finance network. The breach was made possible when an operator enabled YOLO mode, which disabled the agent's normal approval requirement.
US Restricts Visas for Cyber Scammers and Sextortionists
The US is cracking down on cyber scammers and sextortionists by restricting visas for those behind these crimes, sending a strong message that it won't tolerate exploitation of its citizens. This move targets not only the culprits but also their immediate family members, aiming to dismantle these criminal networks.
Clop Ransomware Targets PTC Windchill in Data Theft Attacks
A critical vulnerability, CVE-2026-12569, with a near-perfect CVSS score of 9.3 is being exploited by Clop ransomware attackers to breach PTC Windchill and FlexPLM systems, putting sensitive data at risk. Security patches are available, but urgent action is needed to prevent data theft.
Pentagon Chiefs Under Fire as Iran War Rationale Shifts
Defense Secretary Pete Hegseth faced intense scrutiny from senators over his claims about the US war on Iran, struggling to provide clear answers about the strategy and impact of the conflict. Hegseth made assertions about the devastating effects of US strikes on Iran's military and infrastructure, but also made partial admissions about Tehran's ongoing capabilities.
Government Urged to Harden Private 5G Networks Against China-Backed Threats
Imagine having an invisible backdoor to your most sensitive information - that's what happened when China-backed hackers infiltrated private 5G networks, leaving no limits to what they could access or manipulate. Government agencies and cybersecurity experts warn that these threats, known as Salt Typhoon and Volt Typhoon, have been targeting US networks for years.
Russian Hackers Exploit Zimbra Webmail in Global Espionage Campaign
Russian hackers have launched a global espionage campaign, exploiting a vulnerability in Zimbra Webmail since July 2025, with a sneaky zero-click phishing attack that tricks victims into handing over sensitive info. The clever tactic uses fake news headlines and hidden code to inject malware into browsers, all without requiring a single click.
Russian Espionage Group Exploits Zimbra Flaw to Steal Western Data
A single, stealthy view is all it takes for hackers to exploit a Zimbra flaw, allowing them to siphon off 90 days' worth of emails, passwords, and sensitive data. This alarming vulnerability, tracked as CVE-2025-66376, has prompted a joint warning from US and international cybersecurity officials.
Iran Threatens UK Air Base After US Bombers Launch Strikes
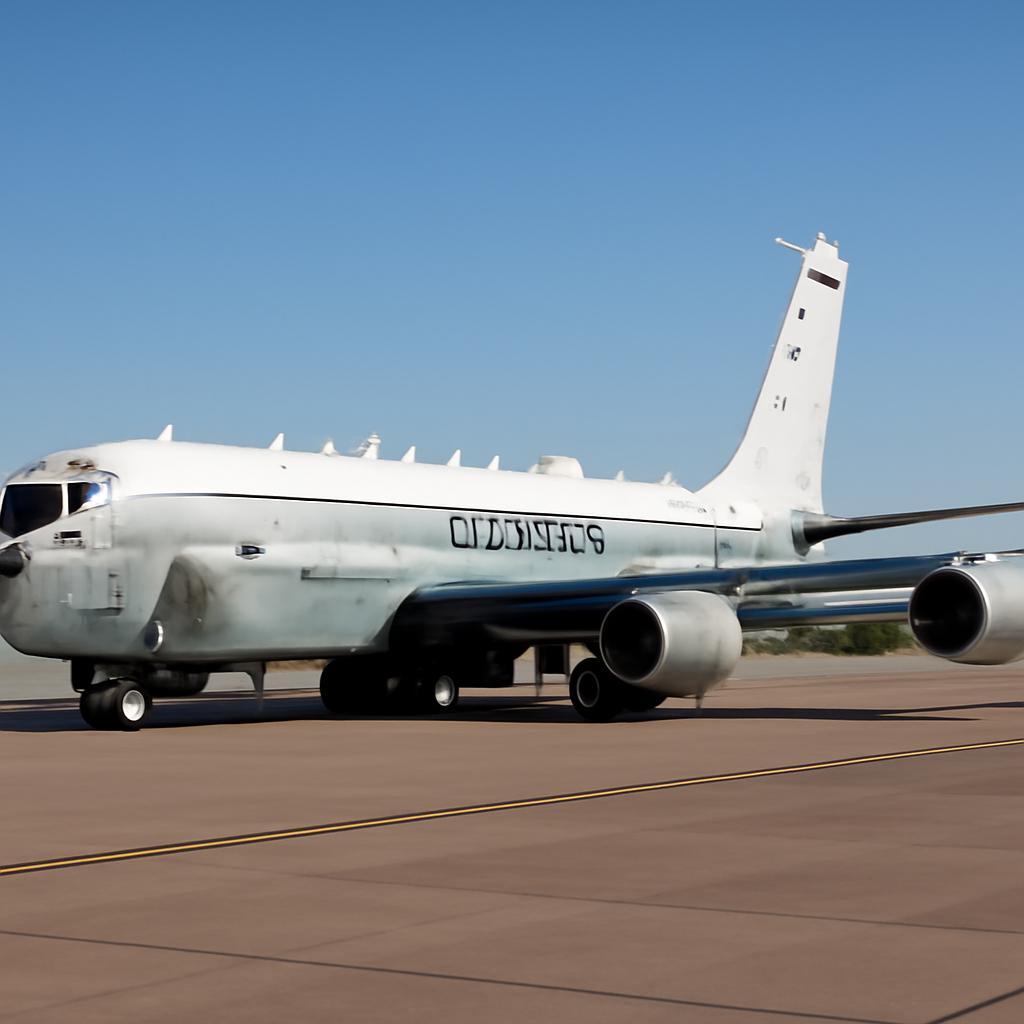
Iran has issued a stark warning to a UK air base, threatening it as a legitimate target if used to launch attacks on Iranian territory, after US bombers took off from the base to carry out strikes. The base, RAF Fairford in England, has also recently welcomed electronic warfare aircraft, heightening tensions.
Kremlin Hackers Exploit Zimbra Bug to Infiltrate Networks
Kremlin hackers, also known as Laundry Bear, have been exploiting a vulnerability in the Zimbra Collaboration Suite to secretly infiltrate government and commercial networks for over a year, aiming to gather sensitive information for the Russian Federation. They've been using malicious emails to inject JavaScript code, allowing them to covertly acquire email data.
Russian Hackers Exploit Zimbra Flaw for Widespread Email Theft
Russian hackers have exploited a Zimbra flaw, CVE-2025-66376, to steal emails from targeted organizations, allowing them to automatically collect a victim's last 90 days of email without requiring any interaction. This alarming vulnerability was weaponized by the Russian state-sponsored group Laundry Bear using a combination of phishing and specially crafted HTML emails.
Russian Hackers Exploit Zero-Click Attack on Western Organizations
Russian hackers have launched a stealthy zero-click attack, dubbed "beehive," targeting Western organizations by exploiting a vulnerability in the Zimbra Collaboration Suite, allowing them to siphon off sensitive emails and data with just a viewed email. This alarming threat highlights the need for organizations to bolster their defenses against such sophisticated cyber threats.