Tag: nation state
1338 articles
FBI Disrupts Chinese Espionage Proxy Network
Kudos to the FBI and DOJ for taking down a Chinese cyber espionage proxy network that's been targeting US critical infrastructure - a huge win for national security. This disruption, made possible by Lumen Technologies' Black Lotus Labs' year-long tracking, has crippled the infrastructure used by Chinese hackers to spy on and gather intel from American targets.
OpenAI Disrupts Russian Influence Operation Using ChatGPT
OpenAI recently took down a cluster of Russian ChatGPT accounts that were being used to spread influence through social media posts and comments, revealing a new and concerning threat. The accounts promoted the International Burke Institute, a self-described expert community based in Israel.
Russia Seizes Unprotected Infrastructure Amid Ukraine Drone Strikes
Russia's government is cracking down on lax security measures, with President Putin signing a decree that allows for the temporary seizure of critical infrastructure from private owners who fail to protect it from drone attacks or neglect repairs. This move comes after Kremlin spokesman Dmitry Peskov warned that many business owners aren't taking sufficient anti-drone safety precautions.
US Targets Iran-Linked Hackers in Sanctions Crackdown
The US is launching a fierce economic crackdown on Iran, targeting nearly 60 entities, individuals, and vessels linked to the country's nuclear, missile, oil, and cyber networks. Secretary of the Treasury Scott Bessent vows to cut off every financial lifeline sustaining the regime, leaving Tehran isolated.
Treasury Targets Iranian Hackers Tied to US Critical Infrastructure Breaches
The Treasury Department has taken a bold step, calling it an "economic D-Day," by imposing sanctions on five Iranian hackers linked to a string of brazen cyberattacks on US critical infrastructure, government offices, and digital assets. This move is part of a broader effort to isolate Iran and cut off its revenue streams.
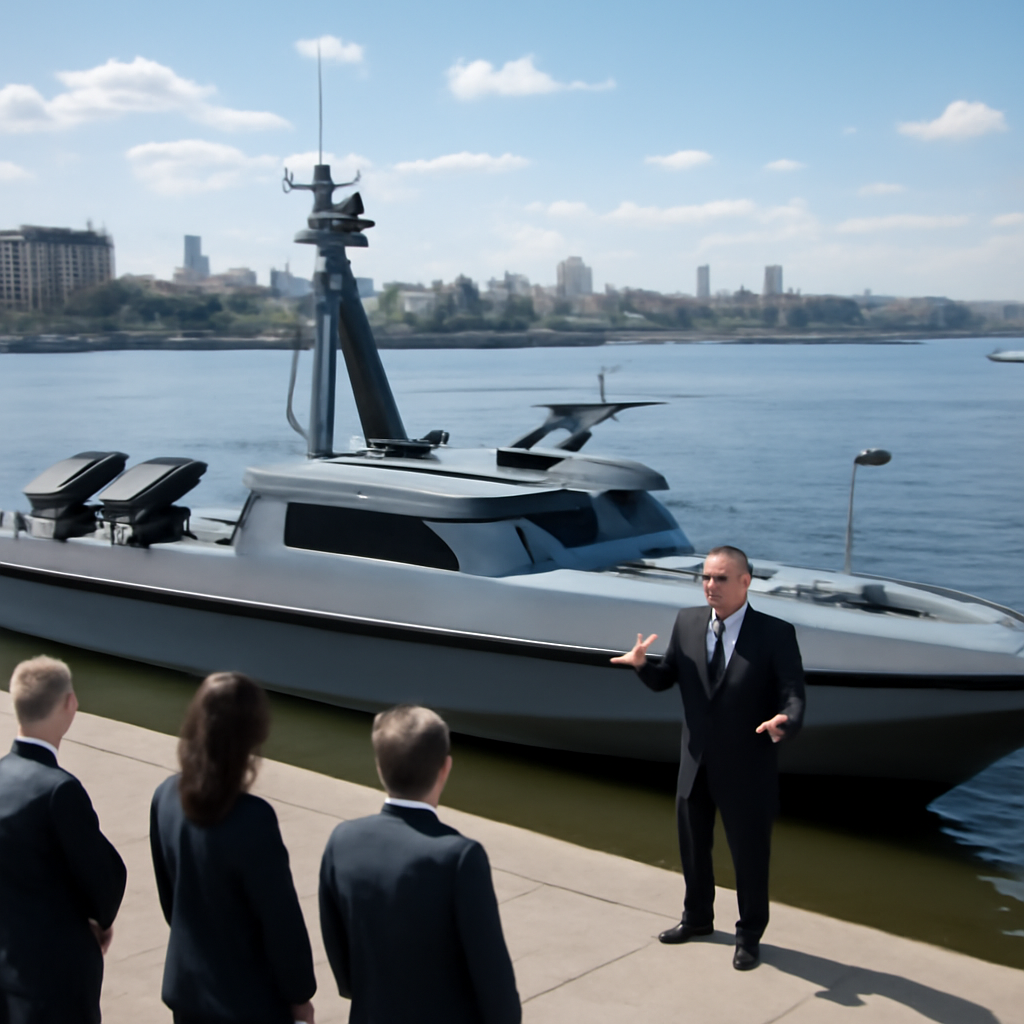
Ukraine Unveils MV11 Unmanned Vessel with Advanced Anti-Drone Capabilities
Meet the MV11, a game-changing unmanned vessel that's redefining naval capabilities with its advanced anti-drone tech and multi-domain prowess. This behemoth of the Magura family is set to revolutionize operations across land, sea, and air.
US Government Cyber Experts Warn of AI-Driven Security Challenges
The US Coast Guard faces a daunting task in keeping its vast network secure, with 1,500 global locations - including remote sites in Alaska and Maine that are only accessible by snowmobile - making routine maintenance and patching a logistical nightmare. This dispersed footprint poses significant cyber security challenges, especially when combined with environmental constraints.
Identity Verification Exploited in Onboarding, Recovery Processes
Cyber attackers are now exploiting weaknesses in identity verification processes, targeting the moments when identities are created or re-established, and using tactics like falsifying documents and stolen credentials to gain a foothold. This shift comes as defenders have made logins more secure, with stolen credentials involved in nearly 45% of breaches.
Recruiter Scams Target Corporate Credentials on Mobile Devices
Beware of recruiter scams targeting your corporate credentials on mobile devices! A recent discovery by Zimperium uncovered a sneaky phishing campaign impersonating top employers and recruiters, including Amazon, Apple, and Louis Vuitton, to steal sensitive info.
Australian Cyber Agency Warns of Widespread TeamCity Server Exploit
A critical TeamCity server flaw, tracked as CVE 2026-63077, is being actively exploited, allowing unauthenticated attackers to bypass security checks and execute malicious commands, posing significant risks to organizations. This vulnerability, with a near-perfect CVSS score of 9.8, is a high-priority threat that demands immediate attention.
US Targets Mabna Institute Hackers with Sanctions Over Iranian Cyber-Attacks
The US has imposed sanctions on 17 alleged Mabna Institute hackers responsible for a massive cyber-attack spree targeting over 300 universities, 50 private companies, and several government agencies since 2013. This crackdown, dubbed Operation Economic Outcast, aims to cut off the financial lifelines sustaining Iran's cybercrime operations.
CISA Warns of Actively Exploited Oracle WebLogic Flaw
A critical Oracle WebLogic flaw, CVE-2026-21962, is being actively exploited, allowing hackers to wreak havoc on your system by creating, deleting, or modifying sensitive data. This severe vulnerability has a CVSS score of 10.0, making it a high-priority threat that demands immediate attention.
US Army Cyber Command Forges Integrated Cyber Warfare Capability
The US Army Cyber Command's Joint Integrated Fire Cell proved to be a game-changer, seamlessly integrating Joint Force Headquarters with Army Cyber to tackle complex cyber challenges with unprecedented speed and agility. By synchronizing cyber effects in real-time, the team achieved a major milestone in coordinated cyber warfare.
Senate Bill Targets Energy Sector's Quantum Cybersecurity Gaps
The clock is ticking: as quantum technology advances, our critical energy systems are vulnerable to devastating cyberattacks - that's why Sen. Chris Coons is pushing for the Quantum-GUARD Act to safeguard our nation's infrastructure. This crucial bill would empower the Federal Regulatory Energy Commission to proactively defend against quantum-enabled threats.
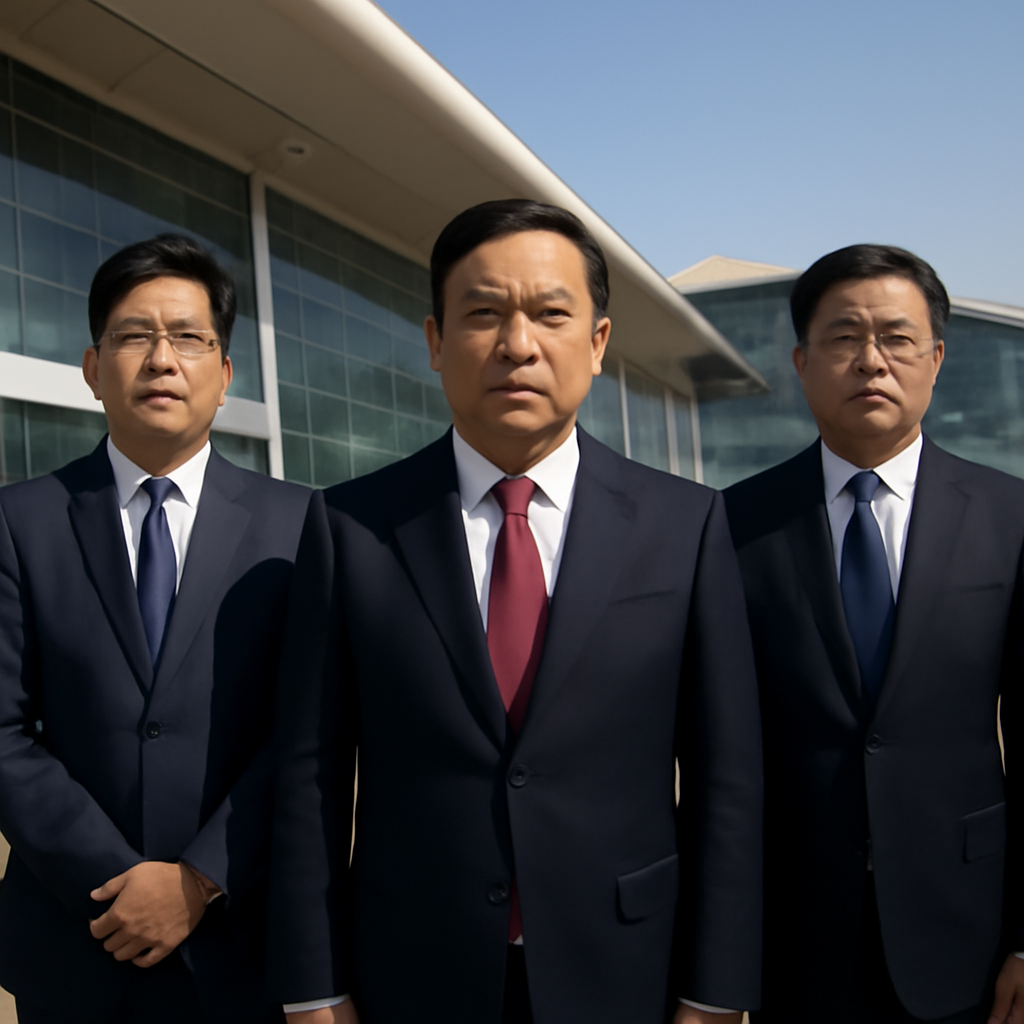
China's New Ambassador in Australia Signals Assertive Stance with United Front Ties
China's new ambassador to Australia, Liu Jinsong, made a bold statement on his first day in Sydney by posing for a photo with two high-profile figures tied to the United Front, a move that signals a more assertive approach to his role. This striking image, published on the Chinese embassy's website, immediately linked Liu to organised groups promoting the Chinese Communist Party's interests.
US Treasury Targets Iranian Hackers in Cyber Sanctions Push
The US Treasury Department has launched a bold crackdown on Iranian hackers, designating four individuals for sanctions for their alleged roles in targeting critical US infrastructure and stealing sensitive information. This economic onslaught aims to disrupt Iran's global financial connections and hold its malicious cyber actors accountable.
Malware Spreads via Fake Minecraft Clients Using SEO Poisoning
Malware is sneaking its way into gamers' computers through fake Minecraft clients, using clever tricks like search engine manipulation and spreading malicious links on popular platforms like Discord and YouTube. Over 6,300 attempts to access these malicious sites have already been blocked by McAfee Labs.
Iran Targets UK Power Grid with Cyberattack
A small UK power plant was taken offline for four days in July after a cyberattack, potentially linked to Iran, but officials quickly reassured that the broader energy system was never at risk. The incident has still been flagged as a major escalation in cyber threats, highlighting the need for continued vigilance.
Iran-linked hackers disrupt UK power plant operations
A recent cyberattack linked to Iran caused a small UK power plant to shut down, but fortunately, the incident was contained and posed no risk to the broader energy system. The UK government assured that the country's energy infrastructure is highly resilient and that they're working closely with the sector to protect it.
Medusa Ransomware Gang Targets Over 500 Organizations, Experts Warn
The Medusa Ransomware gang has hit over 500 organizations since June 2021, and experts are sounding the alarm. This active and rapidly expanding Ransomware-as-a-Service campaign has prompted urgent warnings from top US security agencies.
US Warns of AI-Powered Attacks on Siemens PLCs
The US government has issued a stark warning: hackers are harnessing the power of artificial intelligence to launch targeted attacks on vulnerable Siemens PLCs, critical infrastructure devices used in water, energy, and manufacturing sectors. This is no hypothetical threat - it's a very real and active danger.
China-nexus Operation QUICSILVER Targets Myanmar with QUICAgent Backdoor
Meet Operation QUICSILVER, a sneaky cyber espionage campaign targeting Myanmar's government and tech sectors with a multi-stage backdoor delivery chain, likely orchestrated by a China-nexus threat actor. The attack begins with clever social-engineering lures disguised as official materials, like graduation invites and fake holiday messages.
Iranian Hackers Expose UK Power Plant Vulnerability
Can a UK power plant vulnerability leave millions in the dark? Iranian hackers recently caused a four-day blackout at an unnamed UK facility, raising concerns about the potential for a larger, more critical attack.
China's Lunar Ambitions Hit Snag with Chang'e-7 Delay
China's ambitious lunar plans have hit a roadblock with the sudden delay of its Chang'e-7 launch, a crucial mission to scout out a future research base on the Moon's south pole. The postponement throws a wrench into the country's quest to establish a foothold on the lunar surface and set the rules for future exploration.