Tag: mfa bypass
245 articles
Instructure Negotiates Data Return After Ransomware Breach
In a major win for data security, Instructure has successfully negotiated the return of stolen data and confirmed its destruction after a ransomware breach affected nearly 9,000 educational institutions using its Canvas Learning Management System. The company has ensured that its affected customers are protected and won't be individually targeted for extortion.

Organizations Fortify Defenses Against Evolving Scattered Spider Threats
As Scattered Spider threats evolve, organizations across finance, healthcare, and telecom are bolstering their defenses against sophisticated identity-driven attacks. They're facing an adaptable adversary that's changing tactics, putting pressure on institutions to respond.
Attackers Exploit AD CS for Stealthy Privilege Escalation
Malicious actors are exploiting weaknesses in Active Directory Certificate Services (AD CS) to secretly escalate privileges, often disguising their attacks as routine administrative actions. This stealthy tactic allows them to blend in with normal operations, making it a high-impact threat that's often under-monitored.

Threat Actors Leverage AI for Vulnerability Exploitation and Cyber Operations
Google Threat Intelligence Group has spotted a threat actor using a zero-day exploit likely developed with AI, marking a chilling new trend in cybercrime. This game-changing tactic turbocharges exploit development, malware autonomy, and access to premium AI services.
Google Exposes AI-Driven Zero-Day 2FA Bypass Exploit
Google's Threat Intelligence Group just uncovered a zero-day exploit that was likely crafted by AI, highlighting the rapidly evolving threat landscape. This AI-driven attack uses a Python script with telltale signs of large language model-generated code.
Google Exposes AI-Generated Zero-Day Exploit Used by Hackers
Google's Threat Intelligence Group has made a groundbreaking discovery - a zero-day exploit, potentially crafted with AI, was used by hackers to bypass two-factor authentication in a widely-used open-source tool. This alarming finding highlights the emerging threat of AI-generated cyber attacks.
Hackers Exploit Google Ads, AI Chats to Spread Mac Malware
Malicious hackers are exploiting Google ads and AI chat platforms to trick Mac users into downloading malware, using a sneaky tactic that involves fake installation guides and Terminal commands. Clicking on what seems to be a legitimate ad can lead to a malware-ridden surprise, thanks to a vulnerability in Claude's shared-chat feature.

ShinyHunters Breach Exposes 330 Colleges in Canvas Hack
The notorious ShinyHunters gang has breached Instructure's Canvas, exposing a staggering 330 colleges to a devastating hack, and issued a chilling ultimatum with a May 2026 deadline to negotiate. The attackers replaced login pages with an extortion message, demanding schools seek cyber advisory help and secretly reach out to settle.

Crypto Heist Ringleader Gets 6.5 Years for $230 Million Loot
Marlon Ferro, the mastermind behind a brazen crypto heist, has been sentenced to 6.5 years for stealing $230 million in cryptocurrency using a cunning mix of online scams and targeted home invasions. He served as the group's instrument of last resort, carrying out daring residential burglaries to get his hands on valuable digital assets.
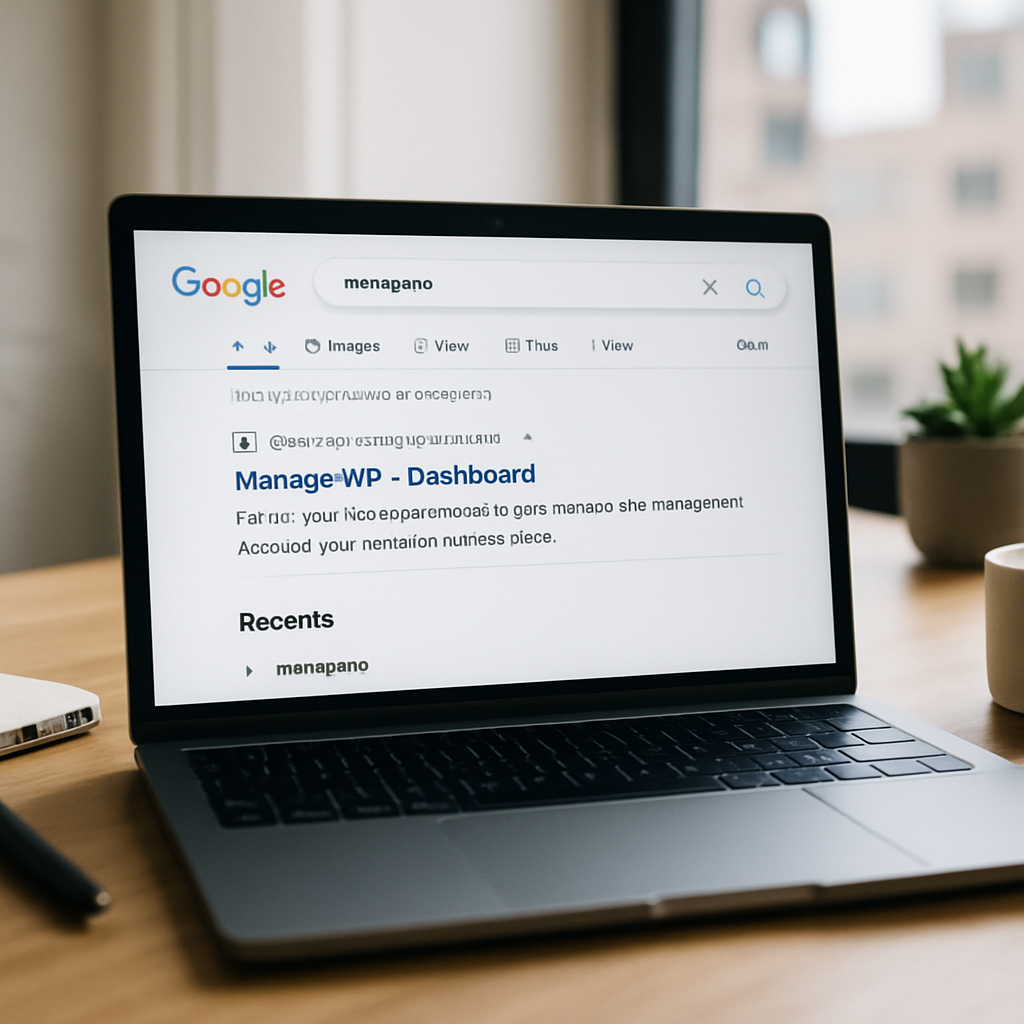
Hackers exploit Google ads for ManageWP phishing scam
Beware of a sneaky phishing scam targeting ManageWP users, where hackers use Google ads to trick victims into divulging their login credentials on a fake website that looks identical to the real one. This clever attack can put hundreds of sites at risk, since each ManageWP account typically hosts multiple sites.
MuddyWater Exploits Microsoft Teams in False Flag Ransomware Attacks
MuddyWater hackers are impersonating Chaos ransomware affiliates, using clever social engineering tactics via Microsoft Teams to steal credentials and gain access to sensitive systems. Their sophisticated campaign involves interactive screen-sharing and manipulation of multi-factor authentication.

Iran-Linked APT Exploits Ransomware Disguise for Espionage
MuddyWater, an Iran-linked APT group, has been caught exploiting a ransomware disguise to secretly infiltrate systems, using interactive tactics to harvest credentials and gain internal access. By masquerading as a Chaos ransomware affiliate, the group aimed to throw off detectives and cover its espionage tracks.
Microsoft Uncovers Large-Scale Phishing Campaign Using Fake Compliance Emails
In just 48 hours, a massive phishing campaign targeted over 35,000 users across 13,000 organizations in 26 countries, using convincing fake compliance emails to steal login credentials. The sophisticated attack, detected by Microsoft's Defender Research team, hit US firms hard, but its global reach was widespread.
Microsoft Exposes Large-Scale Phishing Campaign Targeting 35,000 Users Worldwide
A massive phishing campaign targeting over 35,000 users worldwide has been uncovered, using sophisticated email templates that convincingly masquerade as legitimate internal communications. The highly convincing lures successfully hit organizations across 26 countries, with a staggering 92% of targets based in the US.
Ransomware Breach Exposes Sensitive Data at Sandhills Medical Foundation
Sandhills Medical Foundation suffered a devastating ransomware attack on May 8, 2025, putting sensitive data at risk. It took nearly 11 months for affected individuals to be notified in April 2026, sparking an investigation into the breach.
Vietnamese Hackers Exploit Google AppSheet in 30,000-Account Facebook Phishing Spree
A massive phishing operation, dubbed AccountDumpling, has compromised around 30,000 Facebook accounts using a clever tactic: sending malicious emails from a legitimate Google AppSheet address to bypass spam filters. This sophisticated scam was more than just a simple phishing kit - it was a constantly evolving operation with real-time control panels and a lucrative criminal enterprise.
Cybercrime Groups Exploit Vishing, SSO Abuse in SaaS Extortion Spree
Cybercrime groups are launching lightning-fast extortion attacks within trusted SaaS environments, exploiting vishing and SSO abuse to evade detection and strike with precision. By hiding in plain sight, they're creating significant challenges for defenders trying to keep up.
Microsoft Fixes Remote Desktop Security Warning Display Flaw
Microsoft just dropped an optional update, KB5083631, to squash a bug that's been causing Remote Desktop security warnings to display incorrectly - a fix that's especially crucial for those using multiple monitors with different scaling settings. This targeted update is part of a larger release that includes 34 other changes to improve your Windows 11 experience.

Brazilian DDoS Firm Exposes Own Security Breach
A Brazilian firm's bold admission about notifying major internet providers of massive DDoS attacks against small ISPs took an unexpected turn when evidence revealed a shocking security breach of its own. The company's CEO, Erick Nascimento, revealed that an intrusion in January 2026 compromised key servers and his personal security codes.
Phishing Exploits Persist, Breaching Half of UK Businesses
Phishing attacks remain a major threat, with nearly half of UK businesses falling victim to these scams in the past year, and a staggering 85% of breaches involving phishing as the primary entry point. These attacks often rely on human error, using tactics like impersonation emails and fake logins to trick staff into handing over sensitive information.

OAuth Breach Risks Expose AI-Driven Enterprise Vulnerability
A single misstep with a trial AI tool led to a major breach: a Vercel employee's casual OAuth grant to Context.ai created a lasting vulnerability that attackers exploited when Context.ai was compromised. This incident highlights the alarming ease with which AI-driven tools can become enterprise security weak spots.
GoDaddy Domain Transfer Exposes Non-Profit to Security Risks
A shocking security breach occurred when a 27-year-old domain was transferred from a GoDaddy account to another customer without any authentication checks, putting a non-profit at risk. The alarming transfer was completed in just four minutes, raising serious concerns about GoDaddy's domain transfer process.
Healthcare Sector Grapples with Rising Medical Device Cyberattacks
A staggering one in four healthcare organizations have fallen victim to cyberattacks that compromised their medical devices in the past year, posing a significant threat to patient care. This alarming trend highlights a pressing need for robust medical device cybersecurity measures to prevent delayed treatments and critical care interruptions.

Scattered Spider Targets Global Firms with Identity-Driven Attacks
Scattered Spider is on the prowl, launching identity-driven attacks on major global firms across various industries, from retail and hospitality to telecom, insurance, and airlines. Get insider expert advice from Dr. Torsten George on how to outsmart this sophisticated cybercrime collective.