Tag: hong kong
8 articles
AI-Powered Pentesting Tool Exploited in South Korean Financial Data Heists
Meet ARTEX, an AI-powered pentesting tool that was originally designed for learning and research, but was repurposed by hackers to steal sensitive data from South Korean financial organizations. In a shocking campaign, attackers used ARTEX to breach security and get away with valuable information.
China Obtains F-35 Parts in Hong Kong Shipment Breach
A shipment of F-35 parts bound for the US took a mysterious detour from Australia to South Korea to Hong Kong, where Chinese authorities seized the components, including a cockpit canopy and a weapons-bay door, and have yet to return them. The incident has raised serious questions about security breaches in the international logistics system.
Chinese Hackers Exploit Chrome-Windows Zero-Days to Deploy CLEANGULP Malware
Chinese hackers masqueraded as reputable media organizations and NGOs, using convincing phishing messages and fake sites to deploy the CLEANGULP malware, with one recent campaign targeting Asian government entities over support for a Hong Kong activist. They sent spoofed emails that appeared to be from the Center for American Progress, complete with links to suspicious domains.
F-35 Parts Diverted to Hong Kong, Sparking Security Concerns
Australia's defense minister Richard Marles is downplaying security concerns after F-35 parts shipped from the country were diverted to Hong Kong, saying the components aren't sensitive. The incident has sparked an investigation, with Canberra reviewing its procedures to prevent similar incidents in the future.
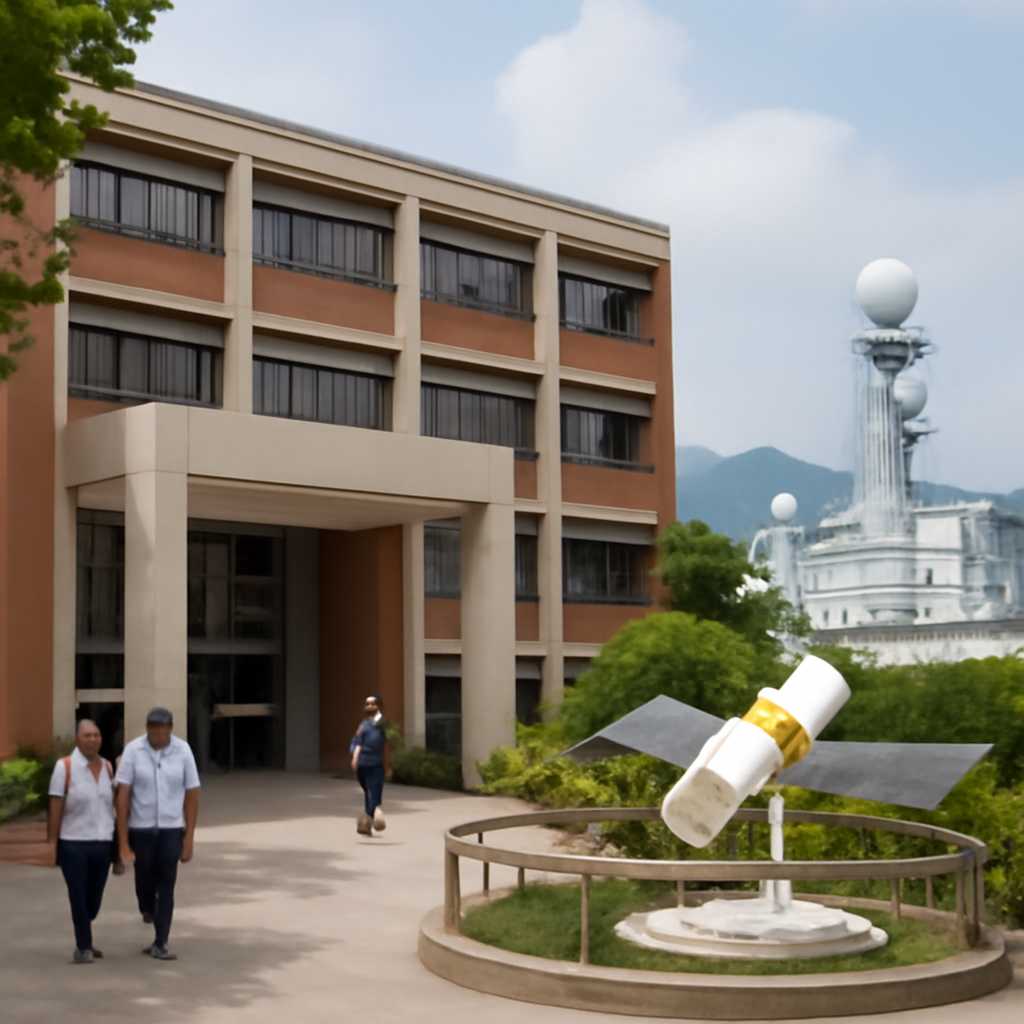
Hong Kong, Macau Universities Deepen Ties with China's Defence Research
The lines between Hong Kong, Macau, and mainland China's research institutions are blurring, with universities in the special administrative regions forging deep ties with defence and space organisations. A new update to the China Defence Universities Tracker reveals a web of research links, from satellite launches to joint labs and personnel exchanges.
Chinese Threat Actor Exploits Leaked DarkSword Kit to Deploy GHOSTBLADE on iOS Devices
A Chinese threat actor has cleverly exploited a leaked DarkSword kit to deploy GHOSTBLADE on iOS devices, with hosting concentrated in Hong Kong but reaching as far as Japan, the US, and Europe. This surprising attack follows the kit's public leak, which has been rapidly reused to target Apple devices running iOS versions 18.4 through 18.7.
Streaming Devices Expose Users to Ad Fraud, Proxy Schemes
A threat researcher stumbled upon a massive ad-fraud operation linked to cheap TV streaming sticks, uncovering a scheme that used these devices to impersonate mobile phones and click ads on fake websites. This cleverly concealed operation was relaying residential proxy traffic and raking in cash through complex networks.
SoFi Hong Kong Breach Exposes Customer Data at Third-Party Vendor
SoFi Hong Kong recently discovered a data breach at a third-party vendor that exposed customer information, with unauthorized access detected on April 30, 2026. The company's investigation is ongoing, but it confirmed the breach originated from a vendor, not its internal systems.