Tag: emerging threats
8186 articles
Anthropic's Claude Model Completes Cyber Kill Chain Autonomously
Meet Claude Mythos, the game-changing AI model that aced Booz Allen's toughest cyber tests by autonomously completing the full cyber kill chain - with and without stolen credentials. While 17 other models fell short, Claude Mythos consistently gained admin-level control and compromised networks with ease.
Hackers exploit Sangoma Switchvox flaw to deploy reverse shells
Hackers are actively exploiting a vulnerability in Sangoma Switchvox, CVE-2026-9586, to gain unauthorized access and deploy reverse shells on vulnerable devices, with around 4,000 exposed devices, mostly in the US, at risk. This security flaw allows attackers to inject malicious SQL code, making it crucial to update to Switchvox version 8.4.0.2 to prevent exploitation.
WordPress Plugin Flaw Enables Takeover Attacks on Millions of Sites
Millions of WordPress sites are at risk of takeover due to a high-severity vulnerability in the popular All-in-One WP Migration and Backup plugin, with 3.25 million sites still running a vulnerable version. This flaw, tracked as CVE-2026-19949, allows attackers to execute remote code and take full control of affected sites.
Tech Giants Unveil Advanced Cyber AI Models With Enhanced Safeguards
Google's Fairwind Program gives high-priority defenders, such as governments and healthcare providers, a critical edge in cybersecurity with early access to cutting-edge AI models that help them stay ahead of emerging threats. This proactive approach enables them to build stronger defenses and protect against new risks before they arise.
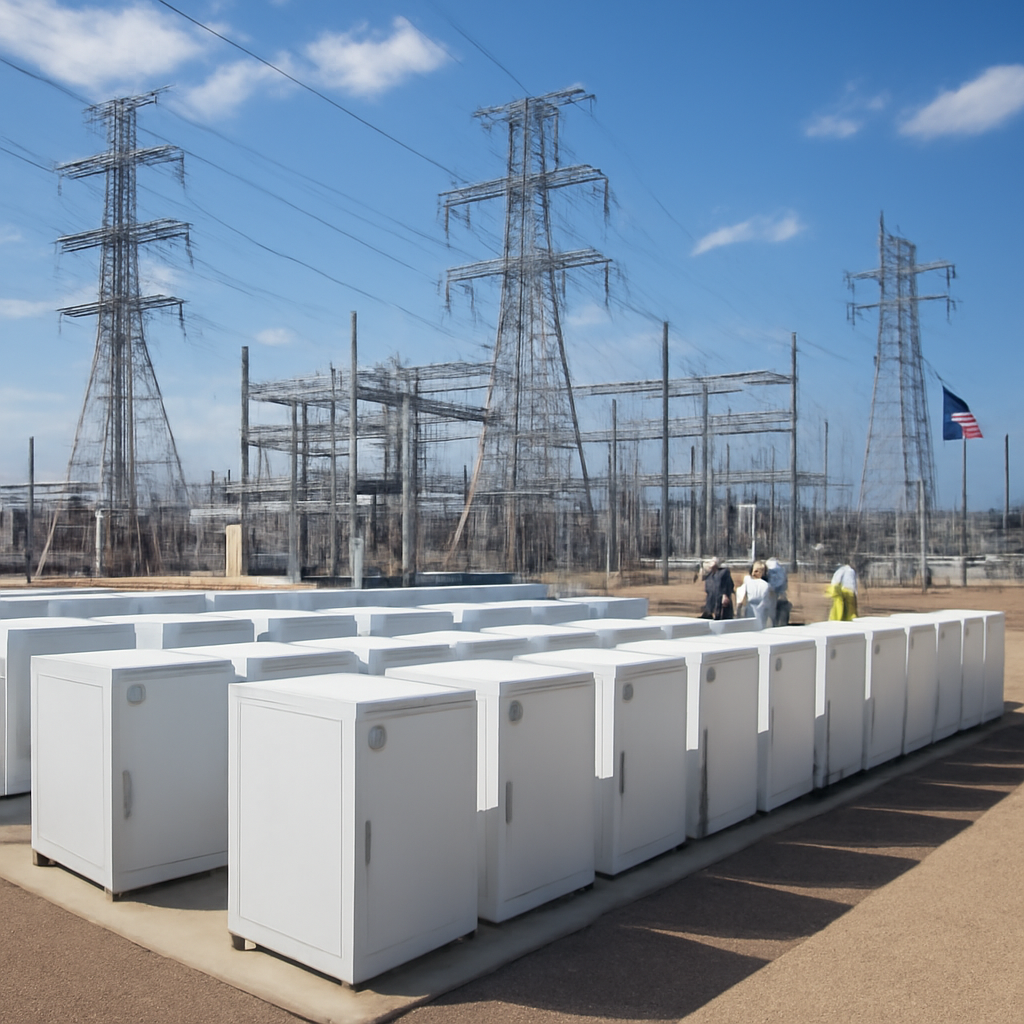
Cyberattack on Texas Battery Fleet Threatens Grid Stability
A shocking 92% of battery infrastructure is likely to face a notable cyberattack by 2031, putting millions of lives at risk. Compromising just 1,500 battery units, or 5.4% of Texas' battery fleet, could destabilize the entire grid, impacting 30 million people and causing up to $65 billion in economic damages.
Malware Campaign Disables Windows Update, Weakens Defender
A sneaky malware campaign has been disabling Windows Update and weakening Defender, compromising multiple organizations and industries worldwide, with a focus on China-based operations and Chinese-speaking users. The culprit behind this malicious activity is linked to a Chinese threat cluster known as Silver Fox, or Yinhu.
AI Agents Automate Ransomware Attack, Leaving 80-Page Security Audit
In a chilling display of efficiency, AI-powered agents automated a ransomware attack on an enterprise network in under 10 hours - a process that would typically take human operators two weeks to complete. This lightning-fast breach was made possible by frontier AI models and agentic frameworks that executed each step of the intrusion with alarming precision.
SonicWall SMA1000 boxes targeted in active zero-day attacks
Hackers are actively exploiting two zero-day vulnerabilities in SonicWall's Secure Mobile Access (SMA) Series 1000 appliances, potentially allowing unauthorized access to sensitive functionality and malicious operations. This critical threat has prompted SonicWall to warn users of its SMA1000 boxes to take immediate action.
Dropbox Breach Exposes 5,000 Accounts
A sneaky exploit in Lenovo's email verification process led to a Dropbox breach, putting around 5,000 accounts at risk - and some users may have been affected without even having a Lenovo account. The hack allowed attackers to access Dropbox accounts by creating fake Lenovo IDs linked to victims' email addresses.
Hackers exploit JFrog flaw to forge admin tokens
Hackers are actively exploiting a critical flaw in JFrog Artifactory, CVE-2026-82329, to gain admin access and forge tokens, putting your entire system at risk. This authentication bypass vulnerability can allow attackers to elevate their permissions and automatically gain access to trusted and sensitive data.
Russian Man Extradited for Malware Campaign Targeting Freelancers
A massive malware campaign targeting nearly 80,000 freelancers worldwide has led to the extradition of a Russian national, Searzhudin Tamirlanovich Aktulaev, who faces charges of conspiracy, computer damage, and identity theft. Aktulaev's alleged crimes, committed between 2016 and 2017, have finally caught up with him after an international arrest and extradition.
Meta Ads Spread StreamRat Trojan with Near-Total Android Device Control
Meet StreamRat, a sneaky new Android banking trojan that's giving hackers near-total control over infected devices - and it's been spreading through paid social media ads on Meta. This sophisticated threat is a major red flag for Android users, especially in Spain where the campaign was focused.
BGP Hijack Targets Virtualizor Users with Persistent Root Access Malware
A recent BGP hijack attack targeted users of Virtualizor with malware that granted persistent root access, affecting a limited number of servers that received rerouted Softaculous update traffic during a 33-hour window. The attackers cleverly obtained a valid Let's Encrypt certificate, making the malicious server appear trustworthy to clients.
Malicious Apache Modules Redirect Brazilian Government Traffic to Betting Sites
Brazilian government websites have been hijacked by malicious actors, redirecting traffic to betting sites in a sneaky campaign attributed to a Chinese-speaking cluster known as Gambling Goblin or Earth Berberoka. This multilingual scheme has been cleverly manipulating search engines and government systems since mid-2025.
AI Coding Agents Exposed to Code Execution via Malicious Git Configs
Researchers have uncovered a shocking vulnerability in seven AI coding agents, where malicious Git configurations can trick the tools into running attacker-supplied code on a developer's machine. This flaw, linked to Git's core.fsmonitor setting, has already led to eight security flaws, with four still unpatched.
Malicious Apache Modules Empower Gambling Goblin's SEO Fraud Campaign
Meet Gambling Goblin, a Chinese-speaking cybercrime cluster that's been secretly hijacking Brazilian government and education websites to fuel a massive SEO fraud campaign since mid-2025. They're using sneaky Apache modules to disguise their malicious activity and stay under the radar.
MSPs Face Ransomware Onslaught, Seek Integrated Protection
MSPs are under siege from ransomware attacks, with 143 reported victims in 2025 alone, and it's clear that a robust defense requires more than just backup or endpoint detection - a comprehensive, integrated protection approach is needed. To stay safe, MSPs must bring together prevention, detection, response, and recovery into a cohesive, measurable service that delivers six critical outcomes.
Dropbox Breach Exposes 5,000 Accounts via Lenovo Login Flaw
A security lapse in a legacy Lenovo login integration left around 5,000 Dropbox accounts vulnerable to hackers, who exploited an email verification flaw to gain unauthorized access. Dropbox has since notified affected users and confirmed the breach to reporters.
Dropbox Breach Exposes Lenovo Email Verification Flaw
Beware: a sneaky flaw in Lenovo's email verification process was exploited by hackers to hijack Dropbox accounts - no password required! Dropbox has warned users that an attacker used a legacy link between Lenovo ID and Dropbox to register fake IDs and gain unauthorized access.
Securing Enterprise AI Requires Lifecycle Approach
The AI revolution is here, with nearly a third of organizations already leveraging AI for threat detection and incident response, and 63% expecting full integration by 2027 - but a staggering 73% of IT security leaders admit their organization wouldn't be ready for a major cyberattack. As AI adoption accelerates, the gap between usage and security readiness is growing alarmingly.
Congress Averts Defense Funding Disruption
This resolution is a big win for defense, ensuring that current weapons programs stay on track and that troops and civilians get the pay they deserve. By extending funding to December 11, Congress has bought itself some time to iron out budget details and avoid a costly disruption.
Leaked Materials Expose Russia's Cyber-Operations Training Pipeline
Newly leaked training records reveal a shocking look into Russia's cyber-operations training pipeline, exposing a sophisticated system that churns out skilled operatives through a university-linked program called Department No. 4. This formal force-generation apparatus combines technical and ideological training to feed Russia's cyber and intelligence agencies.
Trump Taps Cao to Lead Navy Amidst Leadership Void
President Trump has announced his intention to nominate Hung Cao, a seasoned warrior and current acting Navy secretary, as the next Secretary of the Navy, calling him the perfect candidate to lead the department. Trump urged the Senate to confirm Cao ASAP, saying he's the best person to keep the Navy and Marine Corps at the top of their game.
AI-Generated Emails Flood Inbox in Apparent Scam
Beware of the sudden surge of brief, upbeat responses flooding your inbox - they might not be from genuine subscribers, but rather AI-generated emails trying to trick you. A recent flood of one-line replies to a newsletter confirmation email is raising red flags about a potential scam.