Tag: emerging threats
8186 articles
Australia's Data Centre Siting Conundrum Precedes Power Puzzle
Australia's national cabinet recently discussed the country's data centre power puzzle, but surprisingly overlooked a crucial issue - where these facilities should be built. The meeting's focus on energy, water, and land-use standards missed the harder question of ideal locations for these critical infrastructure projects.
Europe's Militaries Grapple with Airpower Modernization
As Europe's air fleets age and threats escalate, defense leaders are facing a daunting dilemma: how to modernize their airpower for a rapidly changing world. With aging aircraft and rising defense budgets, the question on everyone's mind is: what's the future of airpower - manned or unmanned?
Chinese Cargo Ships Gather Signals Intelligence Covertly
China's state-run shipping company COSCO has been secretly gathering signals intelligence for decades, using its commercial vessels to collect communication signals from ships and aircraft across Europe, North America, and Asia. This covert operation allows China to tap into a vast amount of sensitive information, giving it a significant edge in the global arena.
AI-Assisted Cyber Attacks Accelerate with Autonomous Agent Loops
In a recent ransomware attack, a human attacker used AI to breach an enterprise network in under 10 hours - compressing weeks of meticulous planning into a lightning-fast operation. This was achieved by leveraging autonomous agents that worked in parallel, methodically bypassing security layers to achieve a shared goal.
SonicWall Zero-Days Exploited in Chained Attacks
SonicWall has confirmed that two newly discovered zero-day flaws in its Secure Mobile Access (SMA) 1000 appliances are being actively exploited in chained attacks, posing significant security risks. The vendor has swiftly released fixes for the vulnerabilities, which were identified internally by its researchers.
FBI Probes Massive ID Theft Service Selling 153M+ Drivers Licenses
Imagine a black market service that boasts access to over 153 million drivers' licenses, 10 million ID cards, and 3 million travel documents - and has been secretly collecting data for over a year. The notorious Nexus service on Exploit is making these staggering claims, sending shockwaves through the cybersecurity world.
China Retreats from Pacific Threats After Unified Resistance
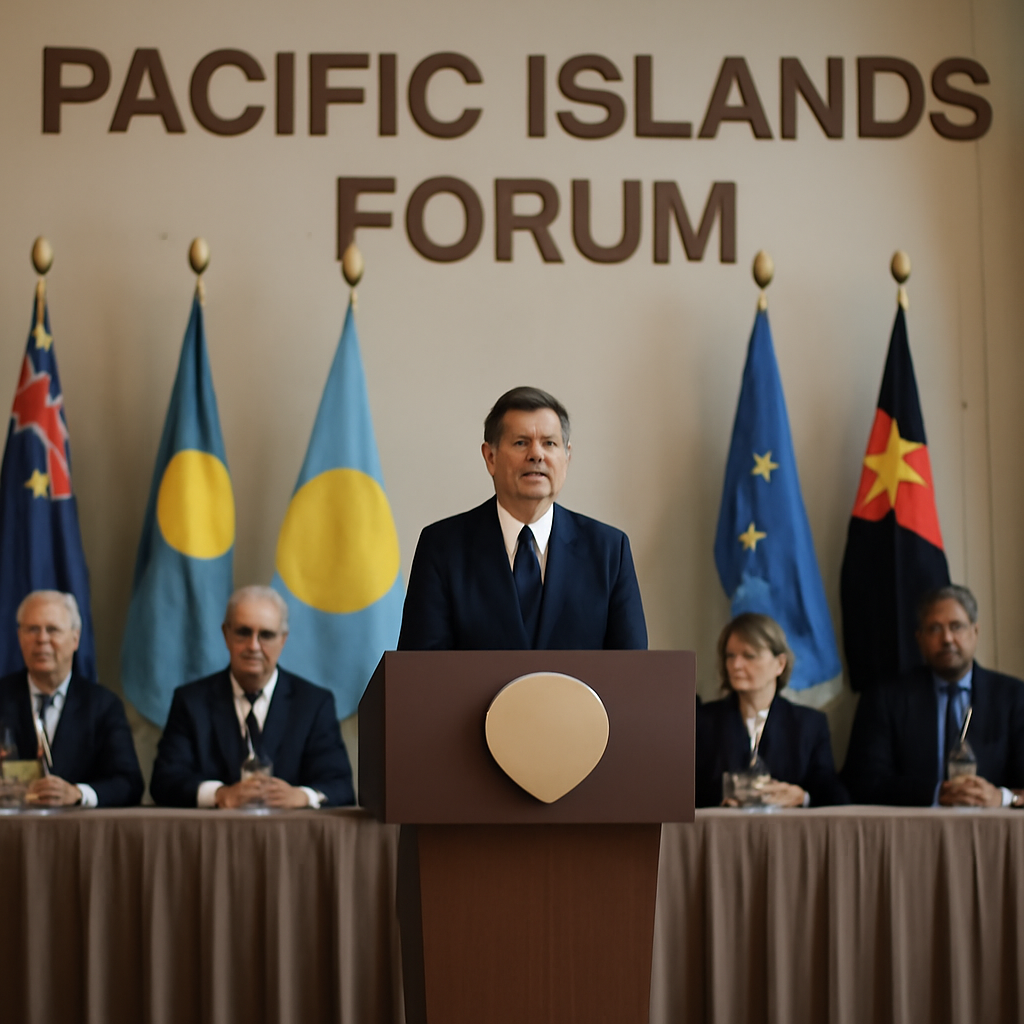
China's tough talk was noticeably absent at the Pacific Islands Forum, where its envoy Qian Bo had initially warned of consequences, but instead delivered a muted message of unity. The scaled-back statement came after a show of unified resistance from Pacific leaders.
Nutex Health Breach Exposes Patient Data to Ransomware Gang
Nutex Health revealed a devastating data breach on August 31, confirming that a ransomware gang had infiltrated its servers, compromising sensitive patient, employee, and business information. The attackers have even threatened to publicly expose the stolen data.
Congress Extends Cyber Info-Sharing Law Through December
The House has passed a short-term funding package that extends the Cybersecurity Information Sharing Act of 2015 through December 11, giving lawmakers more time to work on a longer-term reauthorization. This temporary reprieve preserves key cyber authorities that would have expired at the end of the federal fiscal year.
Comcast's WiFi Routers Expose Home Motion Data
Did you know that Comcast's WiFi routers can detect motion in your home and potentially share that data with third parties, even law enforcement, without further notice? This feature, called WiFi Motion, can track movement near your connected devices and send you alerts - but at what cost to your private life?
Microsoft Defender mistakenly targets Google search links
Microsoft Defender for Office 365's Safe Links feature has mistakenly flagged Google search links as malicious, blocking users from accessing legitimate search results. This faulty security classification is currently preventing users from opening harmless links.
Russian Hacker Charged Over Excel Malware Campaign Targeting Freelancers
A massive malware campaign, involving around 255 fake accounts and 80,000 targeted users, has led to charges against a Russian national, Searzhudin Tamirlanovich Aktulaev, who has been extradited and charged by the U.S. Department of Justice. The campaign, which spread malware through infected Excel attachments, allegedly ran from June 2016 to November 2017, targeting freelancers and others.
UK Tightens Cyber Bill Focus on Users, Not AI Vendors
The UK's Cyber Security Bill is shifting its focus towards users and operational controls, rather than targeting AI vendors, to effectively tackle potential harms and misuse by hostile actors. By doing so, the government aims to take firm action through other channels, such as supporting the AI Security Institute.
GeoNetwork Flaw Exposes Government Geoportal Backends to Unauthenticated Code Execution
A shocking security flaw in GeoNetwork has been discovered, leaving government and agency geoportals vulnerable to unauthenticated code execution - and it's already been exploited in 121 internet-exposed deployments across 39 countries. The vulnerability allows attackers to upload malicious files, giving them free rein to wreak havoc on sensitive systems.
US Indicts Russian for Infecting 80,000 Freelancers with Malware
A massive phishing campaign infected 80,000 freelancers with malware, using 255 fake accounts to spread malicious Excel attachments with hidden macros that downloaded additional software onto victims' systems. The cleverly designed scam exploited a popular freelance employment platform's online messaging feature to spread its digital damage.
SonicWall Zero-Days Exploited in Wild, Firm Urges Immediate Patching
SonicWall is urging immediate patching for two zero-day vulnerabilities in its SMA1000 appliances, which are being actively exploited in the wild by hackers. The more critical flaw, CVE-2026-83548, has a severity rating of 10.0 and can be triggered without authentication, putting sensitive data at risk.
Authorities Disrupt Sality's P2P Network, Neutralize Malware Payloads
In a major win for national security, authorities have successfully dismantled the Sality malware's peer-to-peer network, crippling its ability to spread and cause harm. By cleverly turning the malware's own protocols against it, law enforcement and private partners isolated infected hosts and rendered the threat actor powerless.
Attackers Exploit Switchvox Flaw to Deploy Reverse Shells
A critical flaw in Sangoma Switchvox SMB Edition 8.3 can let attackers execute malicious code without credentials, giving them alarming control over your system. This unauthenticated SQL injection vulnerability, tracked as CVE-2026-9586, is a serious threat that demands immediate attention.
AI-Powered Exploit Porting Threatens Industrial Control Systems
A recent exploit development stage for targeting Industrial Control Systems racked up a hefty $535.74 API usage bill over just 8 hours and 32 minutes, highlighting the costly and disturbing potential of AI-powered threat tactics. This unsettling advancement centers around CVE-2021-31886, a severe vulnerability in Nucleus FTP servers.
Global Authorities Disrupt Sality Botnet Infrastructure
In a major win for cybersecurity, global authorities have joined forces to dismantle the notorious Sality botnet infrastructure, seizing key domains in the US and Europe. This coordinated crackdown, involving the US Department of Justice and international partners, has disrupted the malware's grip on thousands of infected computers.
FulcrumSec Leaks 550GB of Manchester Airport Group Customer Data
A massive 550GB data leak at Manchester Airport Group has exposed the sensitive personal info of nearly 8.7 million customers, with hackers claiming to have posted almost all of the stolen data online. The breach is believed to contain a wide range of personal data, putting customers at risk of identity theft and other cyber threats.
CrowdStrike and Law Enforcement Disrupt 23-Year-Old Sality Botnet
In a major win for cybersecurity, CrowdStrike and international law enforcement agencies joined forces to dismantle the notorious Sality botnet, crippling its ability to communicate and operate by corrupting its core network. By targeting the botnet's peer list, they effectively isolated infected machines and brought the 23-year-old threat to a grinding halt.
US Intel Community Integrates AI into Cyber Operations
Imagine a future where networks of autonomous AI agents work together seamlessly across intelligence and operations - and the US Intelligence Community is already making this vision a reality. Senior officials are shifting their focus from single AI models to integrated systems that enable greater coordination and trust.
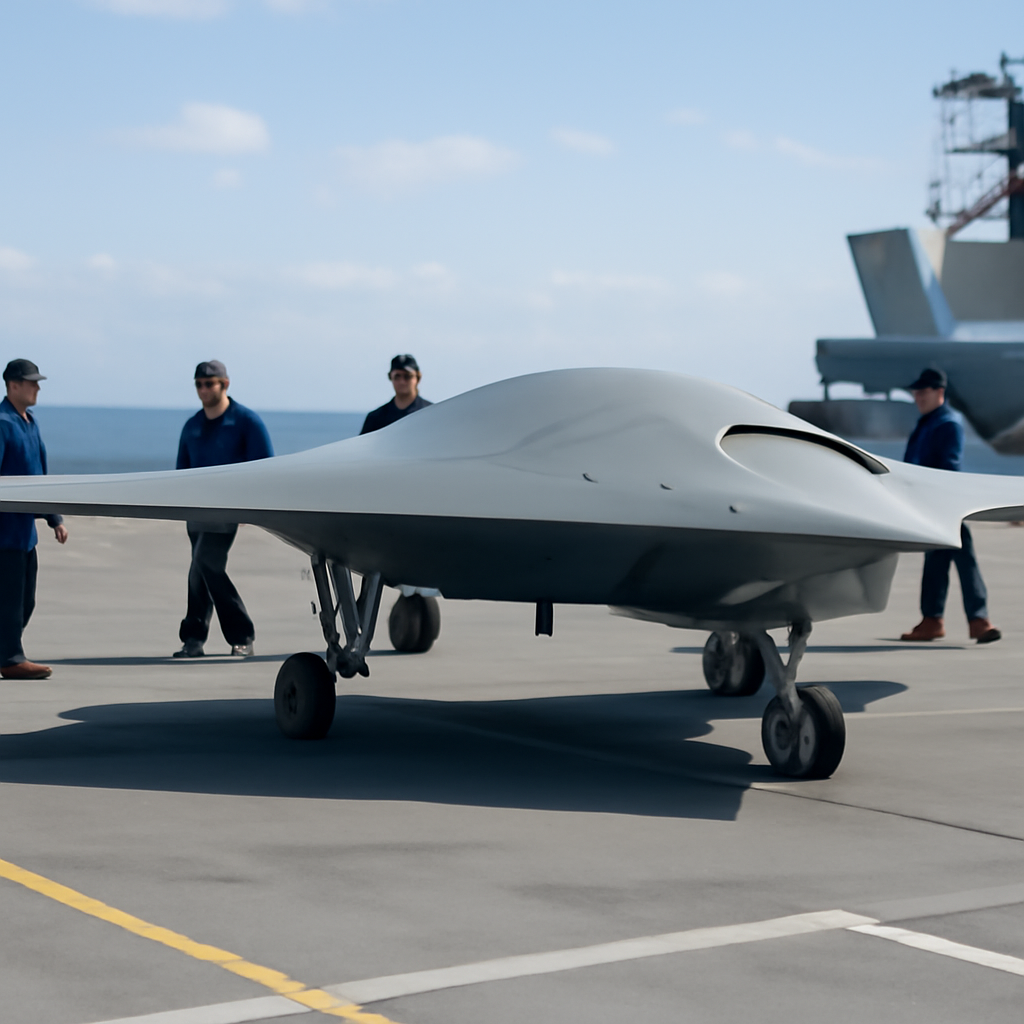
US Navy Revives Advanced Combat Drone Concept
The US Navy is pushing the boundaries of combat drone technology with a new Request for Information, seeking an aircraft that can carry massive external payloads of up to 2,500 pounds per weapon. This ambitious project, dubbed Collaborative Combat Aircraft (CCA) Increment 1, aims to deliver a prototype with unprecedented capabilities within a remarkably short timeframe.