Tag: emerging threats
8609 articles
US Enforces Total Maritime Blockade on Iran
The US has reportedly imposed a total maritime blockade on Iran, stretching along the entire coastline - not just the critical Strait of Hormuz. This massive escalation raises urgent questions about the scope and impact of US action.
Pentagon's Space Ambitions Hinge on Fiscal Maneuvers
The Pentagon's ambitious space plans are hitting a fiscal roadblock, as trillion-dollar defense budgets become the new norm, but the usual budgeting tools that make them possible are no longer reliable. Can planners find a way to reconcile ambitious new programs with an uncertain budgeting process?
Estonia Reassesses Defense Spending, Shifts Focus from Heavy Armor to Drones
Estonia is shaking up its defense strategy, ditching a $587 million plan to buy infantry fighting vehicles in favor of a more modern approach: prioritizing drones and air defense. The move reflects a hard-nosed assessment that heavy armor may no longer be the best bet on future battlefields.
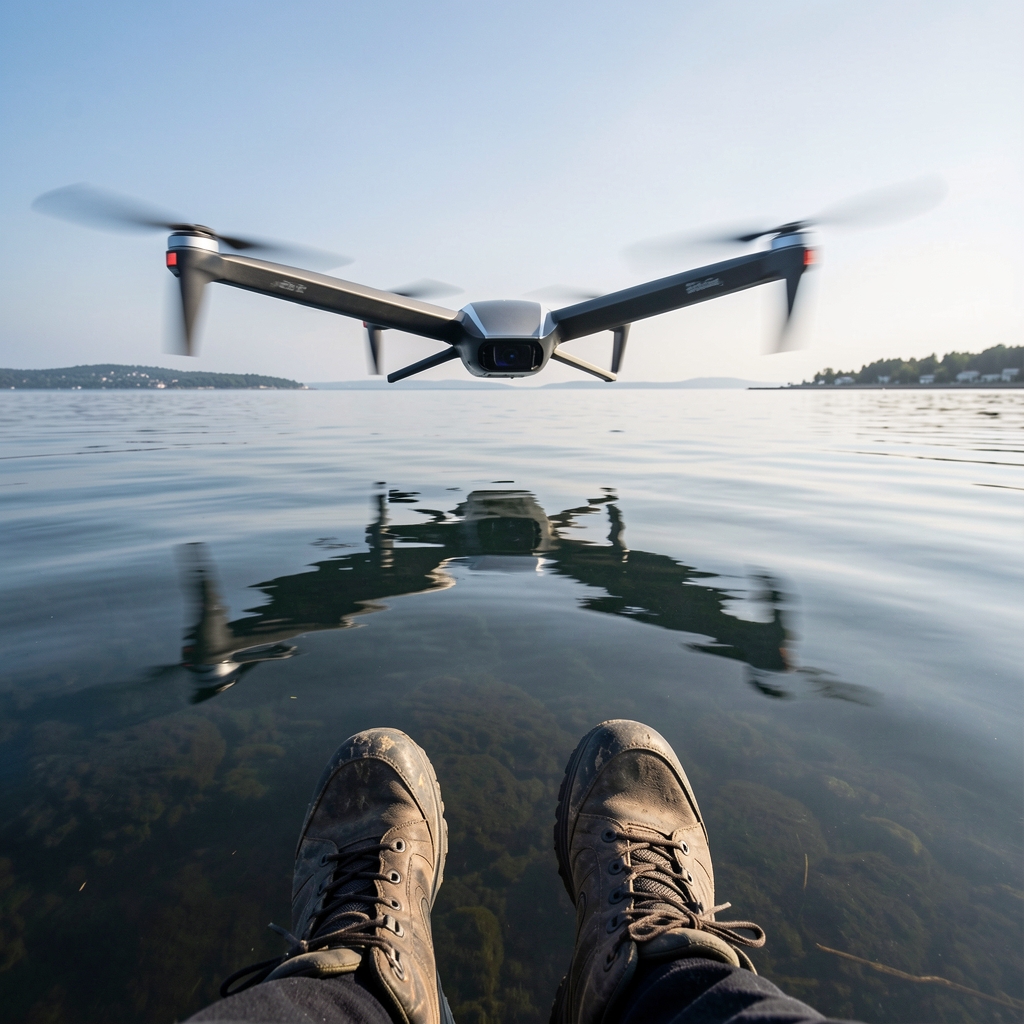
Marines Test Wing-In-Ground Effect Drone with Multirole Ambitions
The US Marines are eyeing a game-changing drone that's taken to the skies for the first time - the Regent Squire Wing-In-Ground Effect drone, a multirole marvel that could revolutionize military operations. With its maiden flight a success, this cutting-edge tech is generating serious buzz.

PNG, Australia Face Rising Drone Threat in Pacific Region
Imagine a swarm of affordable, commercial drones falling into the wrong hands - a very real threat that's no longer just a distant headline, but a looming reality for Papua New Guinea and the broader Pacific region. As non-state actors increasingly wield cheap, powerful drones, can PNG and Australia afford to wait and see what happens next?

Democracies Face Structural Test in Cognitive Domain Warfare
Can democracies keep up in the cognitive domain warfare game without sacrificing their core values? The real challenge lies not in technology or resources, but in restructuring democratic systems to effectively counter information threats while staying true to their principles.
Lawsuit Exposes AI Recording of Doctor-Patient Talks Without Consent
Imagine your most private conversations with your doctor being secretly recorded and analyzed by artificial intelligence without your knowledge or consent - it's a shocking reality that's now at the center of a proposed federal class action lawsuit. Two California healthcare organizations are accused of using an AI tool to record, transcribe, and process sensitive doctor-patient conversations without permission.
OpenAI Rushes Updates for Mac Apps After Axios Hack Compromise
OpenAI recently issued urgent updates for its Mac apps after a developer tool inadvertently pulled in a malicious library, highlighting the risks of supply-chain vulnerabilities. Fortunately, the company assured that its systems and software integrity remained intact despite the incident.

US Navy Deploys Minesweepers to Middle East
The US Navy is gearing up for a major operation in the Middle East, with a cluster of minesweeping assets making a significant move west from the Pacific, hinting at preparations for a large-scale effort to clear sea lanes of mines. This coordinated shift in posture suggests that something big is on the horizon.
wolfSSL library vulnerability undermines ECDSA signature verification
A single misstep in a crucial cryptographic check can have far-reaching consequences, rendering digital certificates unreliable and putting security at risk. The recently discovered wolfSSL library vulnerability compromises ECDSA signature verification, allowing for potentially forged certificates and weakened security.
JanelaRAT Malware Strikes Latin American Banks with 14,739 Attacks
Latin American banks faced a staggering 14,739 attacks from the JanelaRAT malware in 2025, putting sensitive information at risk and raising the stakes for financial institutions and their customers. This surge in attacks highlights the growing threat of JanelaRAT, a modified malware family that continues to target banks in countries like Brazil and Mexico.

France Accelerates Exodus from US Tech with Open-Source Push
France is taking a bold step towards digital independence, with a push to ditch American commercial software for open-source alternatives, and all government ministries are now racing against the clock to reduce their reliance on US tech by the fall. This move signals a growing unease among European governments about Silicon Valley's influence.
Rockstar Games Data Breach Exposes Sensitive Analytics Information
Rockstar Games has suffered a data breach, with sensitive analytics information - including insights into the behavior of millions of players - leaked by the ShinyHunters extortion gang on a criminal site. The breach is linked to a recent security incident at Anodot, a company used by Rockstar Games.

FBI dismantles W3LL phishing service, arrests developer
In a groundbreaking cross-border operation, the FBI and Indonesian authorities joined forces to dismantle the notorious W3LL phishing service, seizing key infrastructure and arresting an alleged developer. This historic collaboration marks a significant win in the fight against cybercrime, and raises hopes for a safer online landscape.
Impersonator Exploits Slack to Target Linux Developers
A clever impersonator tricked Linux developers on Slack by posing as a trusted official, leading them to click a link that seemed harmless but actually handed over their credentials and development environment. This sneaky attack used Google-hosted pages to disguise a bogus root certificate, catching developers off guard.
Booking.com Breach Exposes User Data, Prompts PIN Resets
Booking.com recently suffered a data breach, admitting that hackers accessed sensitive reservation and user information - as a precaution, the company has reset PINs for affected bookings.

OpenAI Revokes macOS Certs Amid Supply Chain Breach Fallout
A recent supply chain breach has raised concerns about software trustworthiness, prompting OpenAI to revoke its macOS code-signing certificates after a malicious package was executed in its build pipeline. This swift action highlights the vulnerability of even the most secure systems to supply chain attacks.
Cloud Breaches Persist as Detection Gaps Remain Unaddressed
Cloud security breaches continue to fly under the radar, leaving us to wonder who's left to sound the alarm. Uncover the reasons behind persistent detection gaps in cloud intrusions by exploring the insightful GovInfoSecurity webinar.
Banks Urged to Unite Against AI-Driven Fraud Networks
Generative AI has created a haven for fraudsters, allowing them to organize and scale their operations like never before - and experts warn that banks must adapt quickly or risk being left behind. To stay ahead, financial institutions must unite against these AI-driven fraud networks and respond with the same level of sophistication.
FBI Disrupts W3LL Phishing Network Behind $20 Million Fraud Attempts
In a major breakthrough, the FBI and Indonesian National Police joined forces to dismantle a global phishing network that had harvested thousands of account credentials in a bid to scam over $20 million. The operation, which used a ready-made toolkit called W3LL, was successfully disrupted, and the alleged developer was detained.
Cybersecurity Risk Outpaces Corporate Defenses
As companies pour more resources into AI and technology, a pressing question remains: can they defend what matters most? Despite escalating investments, many firms admit they're ill-equipped to tackle growing cybersecurity risks, which now rank among the top business threats.

Adobe Fixes Zero-Day Flaw in Acrobat Reader Exploited in Attacks
Adobe has rushed out an emergency patch for a critical vulnerability in Acrobat Reader that's been exploited by attackers since at least December, forcing users to rethink their document reader's security. This zero-day flaw, tracked as CVE-2026-34621, highlights the rapid discovery and weaponization of software flaws.

Mirax Trojan Hijacks Android Devices for Proxy Network
Meet Mirax, a sneaky new Android banking trojan that's not only stealing credentials, but also hijacking devices to create a powerful proxy network - putting European users at risk. This emerging malware is a triple threat, combining a malware-as-a-service model, remote access capabilities, and residential proxies to wreak havoc on infected phones.

Booking.com Exposes Reservation Data Breach Risk
Did you know that a recent data breach at Booking.com may have exposed sensitive trip details, including your name, contact info, and private messages to hotels, to unknown attackers? This incident is a stark reminder that even major travel platforms can be vulnerable to data breaches, putting your personal info at risk.