Tag: emerging threats
8458 articles

US Steers Cybersecurity Scholarship Program Toward AI
The US government is overhauling its CyberCorps Scholarship For Service program, rebranding it as CyberAI SFS, to prioritize AI skills in cybersecurity. Students enrolled in the program will now need to be proficient in using AI to stay employable after graduation.
xrdp Vulnerability Exposes Remote Code Execution Risk
A critical vulnerability, CVE-2025-68670, was discovered in the xrdp remote desktop server, allowing for remote code execution - a flaw that was thankfully patched in January 2026. This security risk was found during a routine audit, highlighting the importance of regular security checks to protect against potential threats.
Australia's Grey-Zone Vulnerability Exposes Thinking Gap
The rules-based international order has always been more myth than reality - and Australia is already living in the grey zone, where state actors are quietly buying up land, stealing intellectual property, and wielding economic and digital influence to get their way. From farm land grabs to disinformation campaigns, this ambiguous battleground is the new normal.

CISA Mandates Patching of Ivanti Flaw Exploited in Zero-Day Attacks
The US Cybersecurity and Infrastructure Security Agency (CISA) is requiring immediate patching of a high-risk Ivanti flaw, CVE-2026-6973, that allows attackers with admin privileges to remotely execute code on vulnerable systems. This critical vulnerability affects Ivanti Endpoint Manager Mobile (EPMM) version 12.8.0.0 and earlier.

Linux RAT Quasar Exploits Developer Credentials for Supply Chain Compromise
Meet QLNX, a sneaky Linux malware that's targeting developers and DevOps teams to gain control of the software supply chain by stealing sensitive credentials. This stealthy threat operates from memory, masquerading as a harmless system process while secretly exfiltrating data and awaiting commands from its controllers.
ShinyHunters Breach Exposes Educational SaaS Canvas
ShinyHunters hackers have claimed responsibility for taking down educational software platform Canvas in a cyberattack that left users offline. The group didn't hold back, giving the developer a scathing "F for security" in their criticism of the breach.
Linux Backdoor Exploits PAM Modules to Harvest SSH Credentials
Meet PamDOORa, a sneaky Linux backdoor that's being sold on the dark web for $1,600, allowing hackers to harvest SSH credentials using a clever combination of a magic password and TCP port. This stealthy threat leverages PAM modules to gain persistent access to your system.

Zara Breach Exposes Data of 197,000 Customers Worldwide
A recent data breach at a former technology provider exposed the sensitive information of 197,400 Zara customers worldwide, including email addresses, product details, and order IDs. The breach, revealed by data-breach notification service Have I Been Pwned, highlights the importance of securing customer data.
ShinyHunters Breach Educational SaaS Canvas
A recent cyberattack has left Canvas, a popular educational software-as-a-service platform, offline, with hackers group ShinyHunters taking credit for the breach and raising serious concerns about the platform's security. The incident has disrupted learning and left many wondering about the safety of sensitive data.
Low-Severity Alerts Expose Hidden Threats in Enterprise Security
Don't let low-severity alerts fly under the radar - nearly 1% of confirmed incidents come from these seemingly minor warnings, translating to around one missed breach per week for a typical enterprise. This small but significant gap in enterprise security can have big consequences.
Contractor Convicted for Destroying Dozens of Federal Databases
A contractor's reckless actions led to the destruction of dozens of federal databases, showcasing a staggering disregard for the security and integrity of sensitive government information. After being terminated on February 18, 2025, the contractor and his twin brother intentionally caused chaos by accessing computers without authorization and deleting crucial data.
PCPJack Disrupts TeamPCP's Cloud Footprint with Credential Theft
Meet PCPJack, a sneaky new credential theft framework that's wreaking havoc on TeamPCP's cloud operations by stealing sensitive credentials and clearing out the competition. This malicious tool is quietly moving through cloud environments, leaving a trail of compromised systems in its wake.
Linux 'Dirty Frag' Zero-Day Exposes Root Flaw in Major Distros
A newly discovered Linux zero-day, dubbed "Dirty Frag," allows hackers to instantly gain root access on major distributions by chaining two separate kernel vulnerabilities. This flaw enables attackers to alter protected system files in memory without authorization, putting countless systems at risk.
US Army Modernization at Crossroads
The next Chief of Staff of the Army will face a critical challenge: navigating a heated debate in the Pentagon that will determine the course of the US Army's modernization and its ability to effectively fight future wars. This incoming leader will have to quickly resolve a contentious dispute among administration officials that's already influencing how modernization funds are allocated.

War Powers Resolution Loopholes Undermine Congressional Oversight
Defense Secretary Pete Hegseth recently revealed that a cease-fire pauses the 60-day War Powers Resolution clock, highlighting loopholes that undermine Congressional oversight. This gray area allows military operations to continue with minimal accountability, blurring the lines between action and inaction.

Woot-Tech Unveils Juggernaut Gunship Drone with Advanced Firepower
Meet the Juggernaut Gunship, a game-changing drone that's packed a punch with advanced firepower and has already been inducted into the Pakistan Navy and special operations forces. This powerhouse can carry a hefty 25kg payload, cruise at 55km/h, and stay airborne for up to 45 minutes.
Saab Accelerates Gripen Production Amid Ukraine Deal Talks
Saab is ramping up production of its Gripen fighter jets as talks with Ukraine on a potential deal gain momentum, with both sides making significant progress on training, production, and financing. A finalized agreement could be just months away, with Saab's CEO hoping for a deal to be sealed by the end of the year.
CISA's Election Security Support Plummets Ahead of Midterms
As the midterms approach, Senator Mark Warner is sounding the alarm on a concerning decline in federal election security support, warning that states can't go it alone in protecting their elections from growing physical and cyber threats. Without robust federal backing, states are left vulnerable to attacks, despite their best efforts to safeguard the democratic process.

US Duo Sentenced for Hosting Laptop Farms for North Korean IT Workers
The FBI, along with its partners, is cracking down on North Korea's efforts to evade sanctions and fund its regime, with two US nationals recently sentenced to 18 months in prison for running laptop farms that enabled North Korean IT workers to operate remotely. The duo, Matthew Issac Knoot and Erick Ntekereze Prince, were also ordered to pay restitution and forfeit gains made from their scheme.
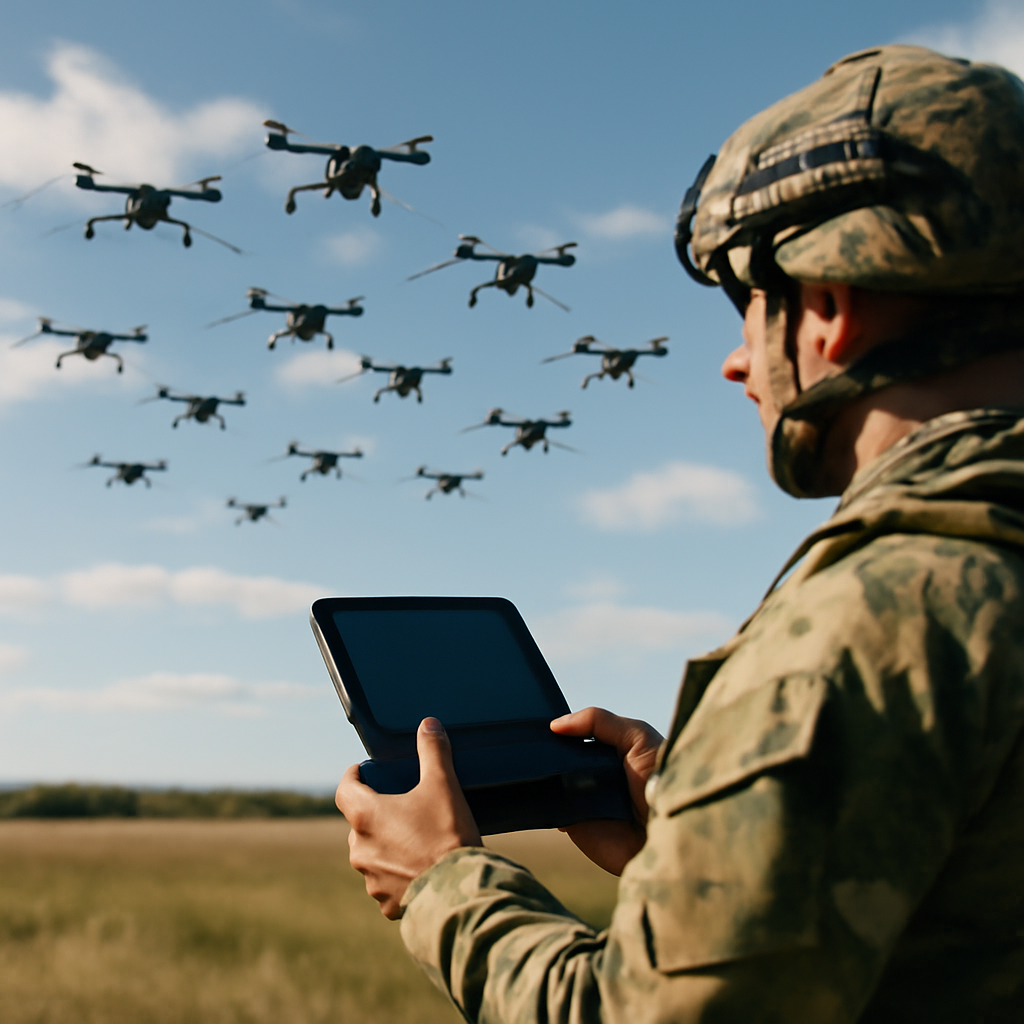
Woot-Tech Unveils SHARDS Infantry-Portable Drone Swarm System
Imagine being able to unleash a devastating, synchronized attack with just the push of a button - Woot-Tech's SHARDS drone swarm system makes it possible, allowing one person to deploy a fleet of mini drones that can overwhelm targets with a thousand tiny, lethal strikes. This game-changing tech lets a single operator command a swarm of expendable drones with simple, intuitive commands.
Pentagon Disrupts AI Vendor Lock-in with Multi-Provider Deals
The Pentagon is shaking up its AI strategy, ditching the single-vendor approach and embracing a multi-provider model to ensure seamless integration with classified systems. This bold move follows a hard-won lesson: relying on one AI vendor just won't cut it.

Congress Weighs Defense Spending Boost Amid Budget Reconciliation Talks
The White House is pushing for a massive $1.5 trillion defense budget, sparking a heated debate on Capitol Hill over how to make it happen. Lawmakers are now racing to find a legislative route to deliver on this hefty request, with the Pentagon's final funding hanging in the balance.
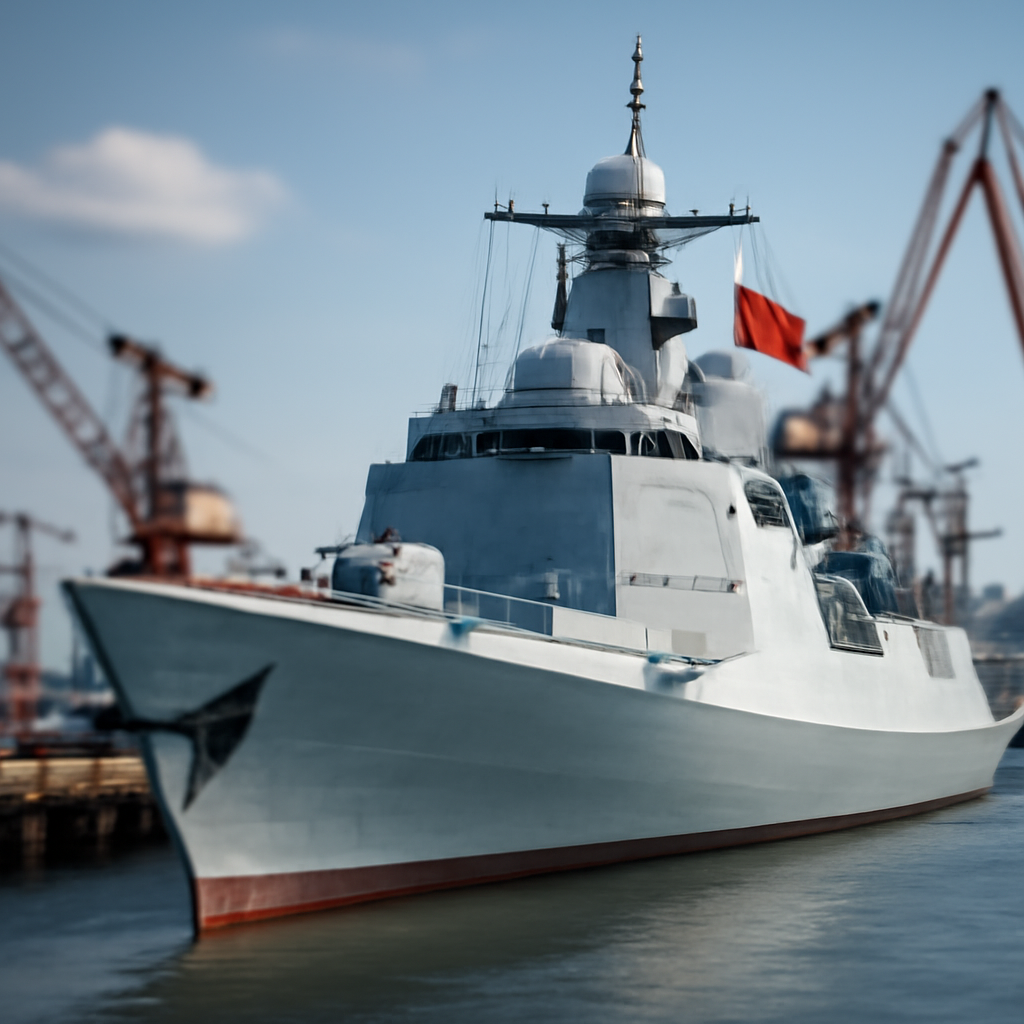
China's PLAN Nears Addition of Advanced Type 052DL Destroyer
Get ready for a major boost to China's naval power: the Type 052DL destroyer, also known as the Extended Mod class, is expected to join the People's Liberation Army Navy (PLAN) by the end of 2026. Recent photos from Dalian Shipyard show the advanced warship nearing completion.
Ivanti Discloses Actively Exploited Zero-Day in Endpoint Manager
Ivanti has confirmed that hackers are actively exploiting a zero-day vulnerability, CVE-2026-6973, in its Endpoint Manager Mobile (EPMM) software, allowing them to run code remotely with administrative privileges. The company has issued patches for this and four other EPMM flaws to protect its customers.