Tag: emerging threats
8358 articles
Prinz Eugen Ransomware Targets Critical Files in Hands-On Attacks
Meet Prinz Eugen, a sneaky ransomware that uses hands-on tactics to target critical files, evading detection by deliberately leaving no ransom note behind. Its operators use stolen RDP credentials and remote monitoring tools to manually infiltrate and take control of systems.
Microsoft attributes Mastra AI supply chain attack to North Korean hackers Sapphire Sleet
Microsoft warns that a recent supply chain attack on the Mastra AI npm environment was carried out by Sapphire Sleet, a notorious North Korean hacking group known for targeting the financial sector. This latest incident is part of a larger pattern of attacks that exploit open-source distribution channels.
Hackers Exploit Gravity SMTP Plugin Bug to Expose API Keys
Malicious hackers are racing to exploit a vulnerability in the Gravity SMTP plugin, which has been installed on around 100,000 WordPress sites, to get their hands on sensitive API keys. Over 17 million exploit attempts have already been blocked by Wordfence, highlighting the urgent need for site owners to update to version 2.1.5.
Credential Attacks Target Fortinet, Sophos, MSSQL Devices in Large-Scale Campaign
A large-scale password spraying and credential theft campaign, dubbed "FortiBleed," is targeting Fortinet devices, with attempts also seen against MSSQL services and Sophos devices, warns Unit 42. This coordinated attack has sparked concerns over widespread credential attacks.
Klue OAuth Breach Expands as Icarus Hackers Claim Multiple Victims
Klue's CEO Jason Smith revealed that on June 12, unauthorized activity was detected in their integration infrastructure, prompting a thorough investigation with cybersecurity experts to understand the breach and support affected customers. The incident allowed hackers to steal OAuth tokens through a compromised legacy credential, impacting connections to third-party platforms like Salesforce.
Hackers Exploit Gravity SMTP Plugin Bug on 100,000 WordPress Sites
A critical bug in the Gravity SMTP plugin is being exploited by hackers on over 100,000 WordPress sites, putting sensitive information at risk. Update to version 2.1.5 or later to patch the vulnerability.
Gentlemen Ransomware Targets 400 Security Processes with GentleKiller EDR Framework
Meet GentleKiller, a sophisticated EDR-killer framework used by The Gentlemen ransomware-as-a-service operation to evade detection by targeting 400 security processes from 48 distinct programs. This framework comes in eight variants, each designed to mimic a legitimate product and exploit a vulnerable driver.
Apple SecureROM Exploit Bypasses Patching on A12, A13 Chips
Security researchers have uncovered a major vulnerability in Apple's A12 and A13 chips, exploiting a flaw in the Synopsys DWC2 USB controller to gain bootROM-level control and bypass patching. This breakthrough could pave the way for new avenues of attack on Apple devices.
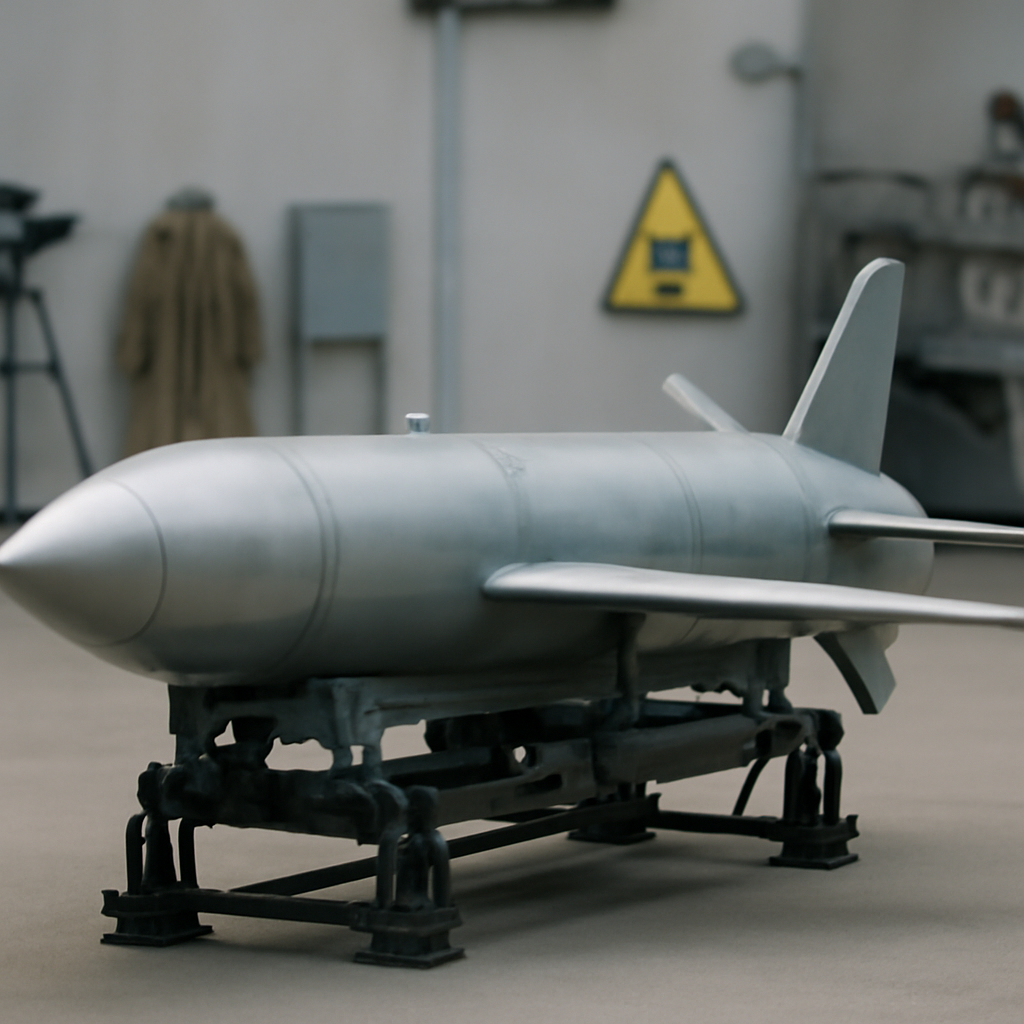
Russia's Burevestnik Missile Exposes Radioactive Risks
Researchers Jake Hecla and R. Scott Kemp warn that Russia's Burevestnik missile likely poses significant radioactive risks, with its nuclear reactor probably venting large quantities of radioactive material into the atmosphere. This alarming finding was made possible by clever analysis of open-source imagery and performance data.
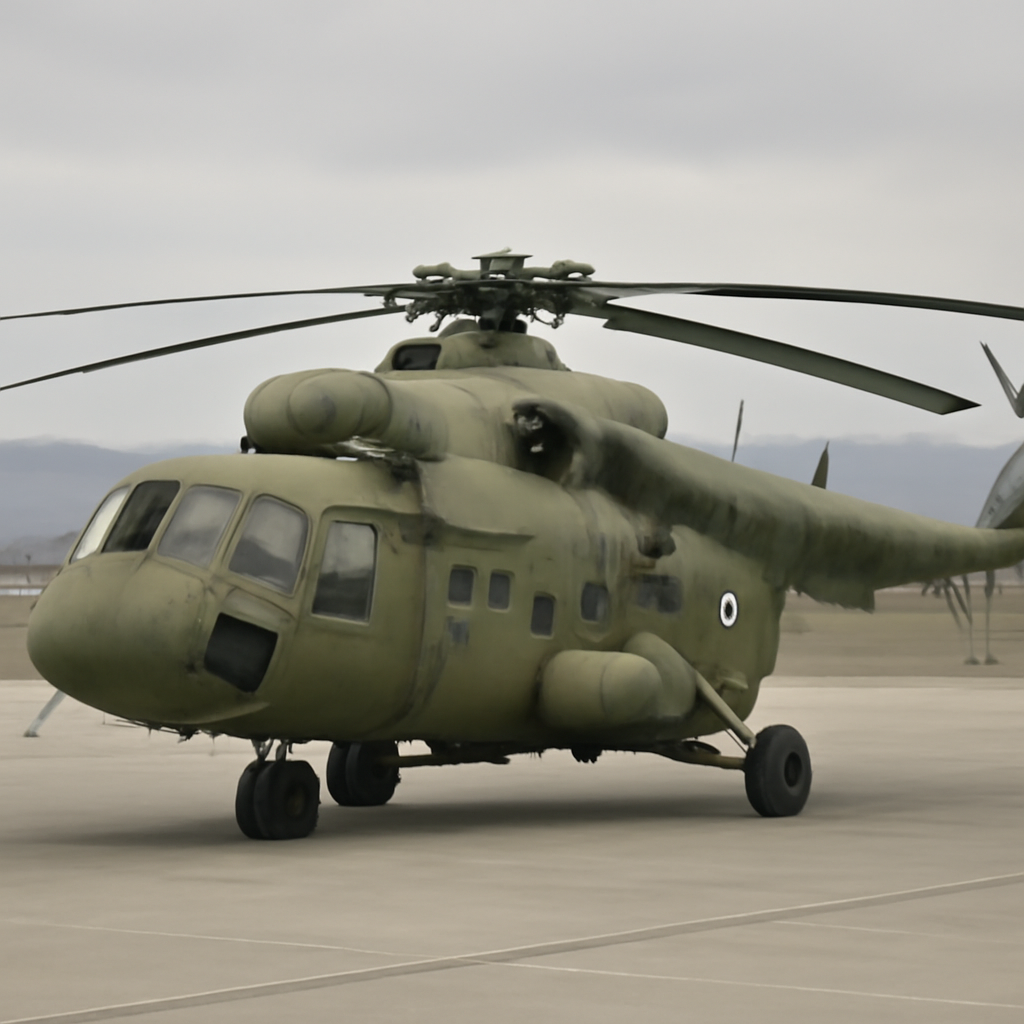
Pakistan Army Aviation Struggles to Find Purpose
The Pakistan Army Aviation Corps is struggling to find its footing, with a recent fatal helicopter crash near Muzaffarabad raising questions about its future direction. Despite being a crucial part of the military, the PAA has seen little modernization since the mid-2010s, leaving its aging fleet and uncertain role in need of a strategic overhaul.
Generative AI Models Expose Limits of Export Controls
In a whirlwind sequence of events, Anthropic released its Fable generative AI model on June 9, only to have the US government slap export controls on it three days later, effectively shutting off access for everyone. The rapid clash between AI innovation and national authorities left Anthropic with no choice but to restrict access to its groundbreaking model.
US Army Unveils Drone-Focused Unit to Counter Pacific Adversaries
The US Army has launched a game-changing unit that combines cutting-edge drone technology with advanced maneuver capabilities to counter threats in the Pacific - meet the 7th Infantry Division Multi-Domain Command – Pacific. This powerful new unit will blur the lines between land, air, and digital battlefields, making it a major force multiplier in the region.
Saudi Arabia Upends Pakistan's African Arms Push
Saudi Arabia pulled the plug on a $1.5 billion arms deal between Pakistan and Sudan, effectively shutting down Islamabad's ambitious plans to expand its defense exports and influence in Africa. This sudden move was part of a larger shift in Saudi Arabia's Gulf strategy.
Pakistan Taps Private Sector to Accelerate Drone Development
Pakistan is taking a giant leap in drone technology, bringing together the country's top defence officials and private sector innovators to revolutionize its unmanned capabilities. By joining forces, they're set to supercharge the development of homegrown drones for warfare and surveillance.
Texas Data Breach Exposes 3 Million Driver's Licenses
A massive data breach has hit Texas, exposing the driver's license information of over 3 million hunting and fishing license customers, leaving them vulnerable to identity theft and other cyber threats. The breach occurred through a third-party license system used by the Texas Parks and Wildlife Department.
BootROM Exploit Targets Millions of iPhones
Millions of iPhones are vulnerable to a newly discovered BootROM exploit, known as "usbliter8", that can't be fixed with software updates because it's embedded in the device's hardware. This means iPhones with A12 and A13 processors will be at risk for the rest of their lifespan.
CISA Warns of Widespread FortiBleed Attacks on 86,644 Devices
The US Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning after a massive cyberattack, dubbed FortiBleed, compromised a staggering 86,644 FortiGate devices, putting countless networks at risk. Take immediate action to protect yourself: shut down active SSL VPN and admin sessions, reset passwords, and enforce strong password policies.
Law Enforcement Disrupts SocGholish Malware Network, Cleans 15,000 WordPress Sites
In a major win for cybersecurity, an international team of law enforcement agencies has dismantled a notorious malware network, freeing 15,000 WordPress sites from infection and dealing a significant blow to cybercriminals. This decisive action is just the beginning, with authorities vowing to continue the fight against botnets and cybercrime.
AI Agents Emerge as Unchecked Identities in Enterprise Security
The equation for enterprise security is no longer simple: with AI agents now connected to critical business services, controlling identities is no longer enough to control risk. These emerging insiders have quietly become privileged - and potentially invisible - attack paths that security and identity programs must urgently address.
Texas Breach Exposes 3 Million Records
A massive data breach at a Texas vendor has exposed the personal information of over 3 million Texans, prompting swift action from the Texas Parks and Wildlife Department to bolster security measures and protect customer data. The breach, which affected 3,087,721 individuals, highlights the importance of robust safeguards in today's digital landscape.
AI Shifts Threat Management from Reactive to Proactive Stance
With a sprawling security stack of 40+ tools, enterprise teams are drowning in overlapping alerts and manual handoffs, leaving gaping holes for adversaries to exploit. This disjointed approach leaves teams scrambling to respond to threats, with attackers enjoying a lengthy 43-day window to wreak havoc.
Rights Groups Warn UK Over Biased AI Age Estimator for Asylum Seekers
Sixty-two leading rights organisations, including Amnesty International and Human Rights Watch, are urging the UK government to ditch its plans to use biased AI-powered facial age estimation on asylum seekers, citing substantial concerns about its fairness and accuracy. They're demanding answers on the technology's testing, training, and safeguards before it's rolled out in 2027.
Microsoft Updates Trigger Recycle Bin Filename Glitch
Microsoft just revealed a frustrating glitch in the Recycle Bin that displays a confusing filename when you permanently delete an item, showing a cryptic code instead of the file's original name. Luckily, the issue only affects the deletion confirmation dialog and doesn't change the file's name in the Recycle Bin or when it's restored.
UK Privacy Watchdog Resigns Amid Poor Judgment Admission
UK Privacy Watchdog John Edwards has resigned with immediate effect, admitting his position had become untenable after being under investigation since February. He announced his decision on LinkedIn, bringing a sudden end to a months-long probe.