Tag: emerging threats
8354 articles
ASELSAN Builds Sovereign Military 5G Core with GÖKBAĞI Satellite Network
ASELSAN is revolutionizing military communications with GÖKBAĞI, a game-changing system that combines a low-Earth orbit satellite network with a dedicated military 5G core for secure, high-capacity, and resilient connectivity. This cutting-edge architecture enables uninterrupted communication on the move, even in electronic warfare conditions.
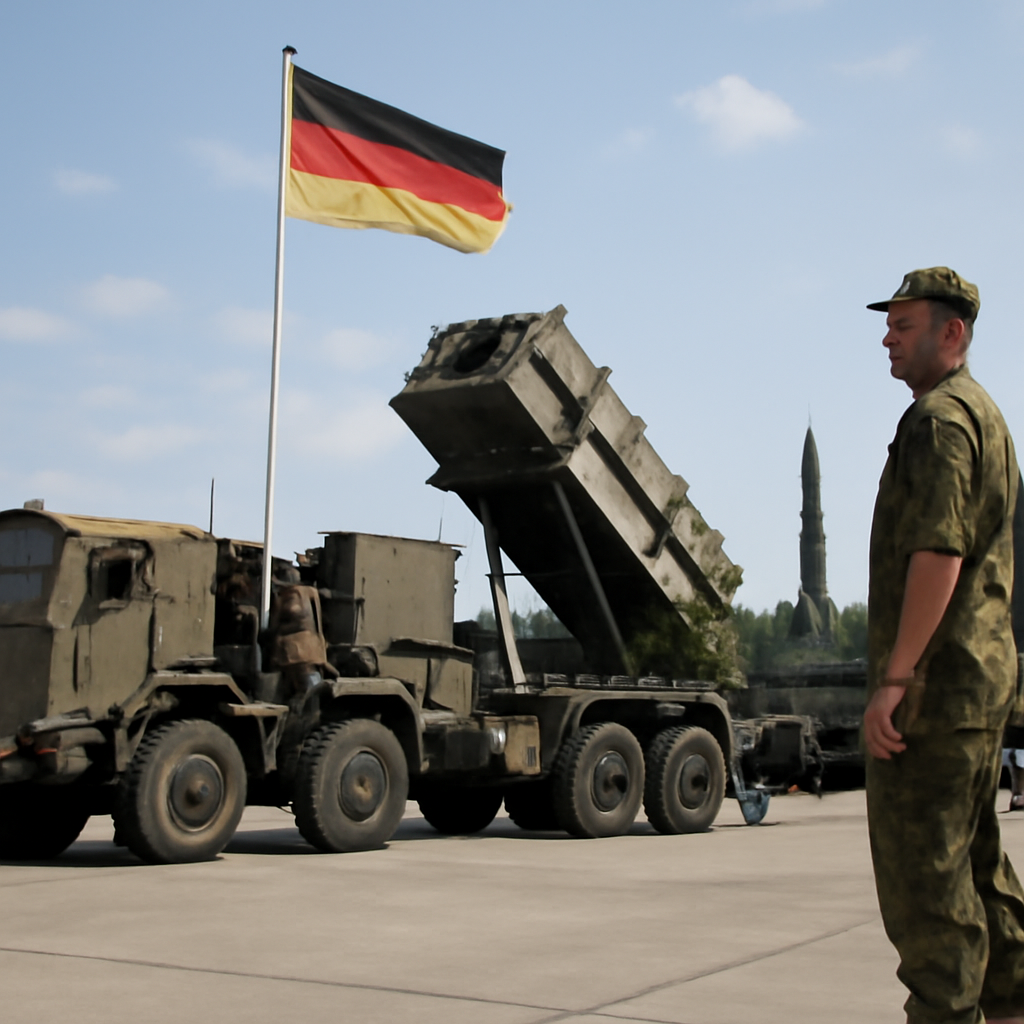
Germany Bolsters Strike Capabilities with US Tomahawk Missiles
Germany is set to significantly boost its strike capabilities with the acquisition of US Tomahawk missiles, a strategic move that will help bridge a critical defense gap while the country works on developing its own European systems. This deal, valued at over $1 billion, marks a major milestone in strengthening Germany's defense, with plans to procure up to 400 of the advanced Tomahawk Block Vb missiles.
Turkey's TEI Advances Domestic Turbofan to Break Ukraine Engine Chokepoint
Turkey's TEI is making significant strides in developing its domestic turbofan engine, with plans to deliver the TF6000 to Baykar and Turkish Aerospace Industries by early 2027 for pre-integration testing. This milestone marks a crucial step towards breaking Ukraine's engine chokepoint and advancing Turkey's aerospace capabilities.
Violent Extremist Sentenced for Exploiting Children in 764 Network
A 19-year-old San Antonio man, Alexis Aldair Chavez, has been sentenced to 40 years in federal prison for leading a violent extremist group that exploited children, a heinous crime that showcases the dark heart of such nihilistic organizations. Chavez, who used aliases "Zack" and "Zack8884," will also pay $10,000 in restitution and face lifetime supervision.
Microsoft Exposes GigaWiper Backdoor's Triple Threat
Microsoft has uncovered a highly destructive backdoor, dubbed GigaWiper, which poses a triple threat to Windows systems, allowing attackers to silently spy and destroy machines in three different ways. This multi-purpose threat doesn't just crash systems - it gives attackers the power to choose how and when to render a machine irrecoverable.
GitHub Accounts Used to Map Corporate Orgs in Stealthy Campaigns
Cyber attackers are using sneaky tactics, leveraging old or compromised GitHub accounts, to secretly map out corporate organizations and steal sensitive data. They're exploiting loopholes with automated tools and stolen tokens to quietly gather intel from GitHub APIs.
Cloud Bucket Hijacking Exposes Data Streams to Silent Compromise
In a major global sting operation, INTERPOL's Operation First Light 2026 led to the arrest of 5,811 individuals and the seizure of $293 million in illicit assets, highlighting the growing threat of transnational social engineering and money-laundering schemes. This coordinated effort involved 97 countries and territories, and resulted in the identification of over 142,000 victims and 15,606 suspects.
Microsoft Ramps Up Windows Security Updates with AI-Discovered Flaws
Microsoft is supercharging its Windows security updates with the help of AI, which is turbocharging the discovery of flaws and enabling the company to identify more issues faster than ever before. This means you can expect a higher volume of fixes to keep your Windows experience safer and more secure.
GitHub npm Tightens Security With Disabled Install Scripts
GitHub's latest npm update takes a giant leap in security by disabling install scripts by default, reducing supply-chain risks and giving developers more control. To adapt, plan to switch to trusted publishing or staged publishing with human approval for automated publishing.
Helix Group Exploits SharePoint with Advanced Vishing Tactics
Helix Group hackers are using clever voice phishing tactics, often impersonating managers, to trick victims into handing over account access. They use a simple yet effective playbook, starting with a convincing phone call that sets the stage for a device-code phishing scheme.
Forg365 Phishing Platform Exploits AI to Target Microsoft 365 Accounts
Meet Forg365, a sneaky new phishing platform that uses AI to make it easy for hackers to target Microsoft 365 accounts and steal sensitive info. This phishing-as-a-service operation offers a range of tools, including AI-generated lures, to help cybercriminals launch convincing attacks.
AI-Generated Malware Targets Active Directory Environments
Criminals are now leveraging AI to create malicious software, as seen in a recent case where an attacker used an AI-assisted PowerShell script to infiltrate an Active Directory environment. This emerging threat, dubbed "vibe coding," allows attackers to generate software by simply prompting a large language model in plain language.
Microsoft Fixes RoguePlanet Zero-Day in Latest Security Update
Stay safe online with Microsoft's latest security update, which just patched a critical zero-day vulnerability known as RoguePlanet. This crucial fix helps protect your digital world from potential threats.
Cyberattacks Exploit Summer Staffing Gaps
Cyberattacks surge by 40% during holiday periods, with summer being a prime target due to lighter staffing and slower business operations that create the perfect storm for cybercriminals to exploit. When teams are on vacation, attackers see an opportunity to probe for vulnerabilities and test response times.
GodDamn Ransomware Exploits Signed Driver to Disable Endpoint Defenses
Ransomware attackers have taken a disturbing new tactic, using a malicious kernel driver signed by Microsoft to disable endpoint defenses and wreak havoc on systems. The PoisonX driver, identified as g11.sys, is a game-changer in ransomware operations, making it harder for security teams to detect and respond to threats.
Interpol Crackdown on Cybercrime Yields 5,800 Arrests Worldwide
In a major global sting operation, authorities in Eswatini seized 240 electronic devices, foreign currency, and a stunning replica of a Brazilian police station - complete with fake uniforms and equipment - as part of Interpol's Operation First Light 2026, which has led to 5,800 arrests worldwide. This massive crackdown on cybercrime was made possible through collaboration between 97 countries and territories, with support from Europol, Aseanapol, and GGCPol.
Clearinghouses Race to Remediate Pre-Disclosure Vulnerabilities
Chainguard's Athena clearinghouse has been quietly remediating vulnerabilities for months, converting findings into fixes at an incredible pace, with a one-day SLA on actively exploited vulnerabilities and over 100,000 issues resolved so far. This swift action comes as the threat landscape accelerates, with the mean time to exploit now estimated at just -7 days.
CISOs Warn of Executive Disconnect on Cybersecurity Risks
A whopping 78% of CISOs believe their board-level decision makers are in the dark about employee-driven cyber risks, leaving companies vulnerable to attacks. The disconnect is alarming, especially as AI-powered scams and social engineering attacks become increasingly sophisticated.
AI Coding Assistants Expose Flaw in Approval Process
Researchers have uncovered a shocking flaw, dubbed GhostApproval, that affects six major AI coding assistants, allowing malicious code to bypass approval prompts and wreak havoc on a developer's machine. This vulnerability can be exploited through a clever use of symbolic links, posing a significant risk to developers who rely on these tools.
Microsoft to Phase Out OWA Light in Exchange Server Update
Microsoft is bidding farewell to OWA Light, shifting its focus to the full Outlook on the web experience, which promises a more seamless and modern way to access your inbox. By August 2026, the tech giant will retire OWA Light, streamlining its engineering efforts and enhancing the overall user experience.
Microsoft Fixes Defender Flaw That Exposes Systems to SYSTEM Privileges
Microsoft has patched a critical flaw in its Defender software, known as RoguePlanet, that could have allowed hackers to gain SYSTEM privileges and take control of vulnerable systems. The vulnerability, tracked as CVE-2026-50656, has been fixed with the latest security updates.
Cybersecurity Firms Back AI Charter to Guide Secure Use
CREST has launched a groundbreaking AI Charter, outlining nine essential principles to ensure the secure and responsible use of AI in cybersecurity, with industry leaders rallying behind the initiative as a crucial step towards a safer digital landscape. The charter's nine points provide a comprehensive framework for accountability, transparency, and security in AI-driven cybersecurity activities.
Global Crackdown Nets 5,800 Arrests in Anti-Fraud Operation
In a massive global sting operation, authorities arrested 5,811 suspects and seized $293 million in illicit assets, dealing a significant blow to social engineering fraud and money laundering. The sweeping crackdown, dubbed Operation First Light 2026, spanned 97 countries and identified over 142,000 victims.
Pentagon CIO Ramps Up Cybersecurity, Tech Modernization for Warfighters
The Pentagon's CIO is turbocharging cybersecurity and tech modernization to empower warfighters, with a focus on four key pillars to drive transformation. This initiative has already seen rapid adoption, with 1.3 million users on board with GenAI.mil.