Tag: emerging threats
8354 articles
Microsoft Tracks ShinyHunters' Salesforce Data Theft Via OAuth Flaws
Microsoft uncovered a sneaky year-long operation by the ShinyHunters extortion group, who exploited trust in Salesforce's OAuth system to steal sensitive data, using clever vishing tactics to trick employees into granting access to a malicious app. The attackers posed as IT support, convincing victims to authorize a fake Data Loader tool that allowed them to make API calls and search for valuable credentials.
US Military Deploys Kamikaze Drone Boats in Combat Against Iran
In a historic first, US forces have launched a daring combat operation against Iran using kamikaze drone boats, successfully striking a submarine and ship maintenance facility at Bandar Abbas Naval Base. The bold move, carried out by CENTCOM forces, marks a significant escalation in the use of sea drones in military operations.
Russian Hackers Target Network Devices With Exploits
Russian hackers, linked to the Federal Security Service's Center 16, have been actively targeting critical US and foreign networks across multiple sectors, including defense, energy, and healthcare, for over a decade. This ongoing threat has compromised networks in various industries, posing significant risks to national security and global stability.
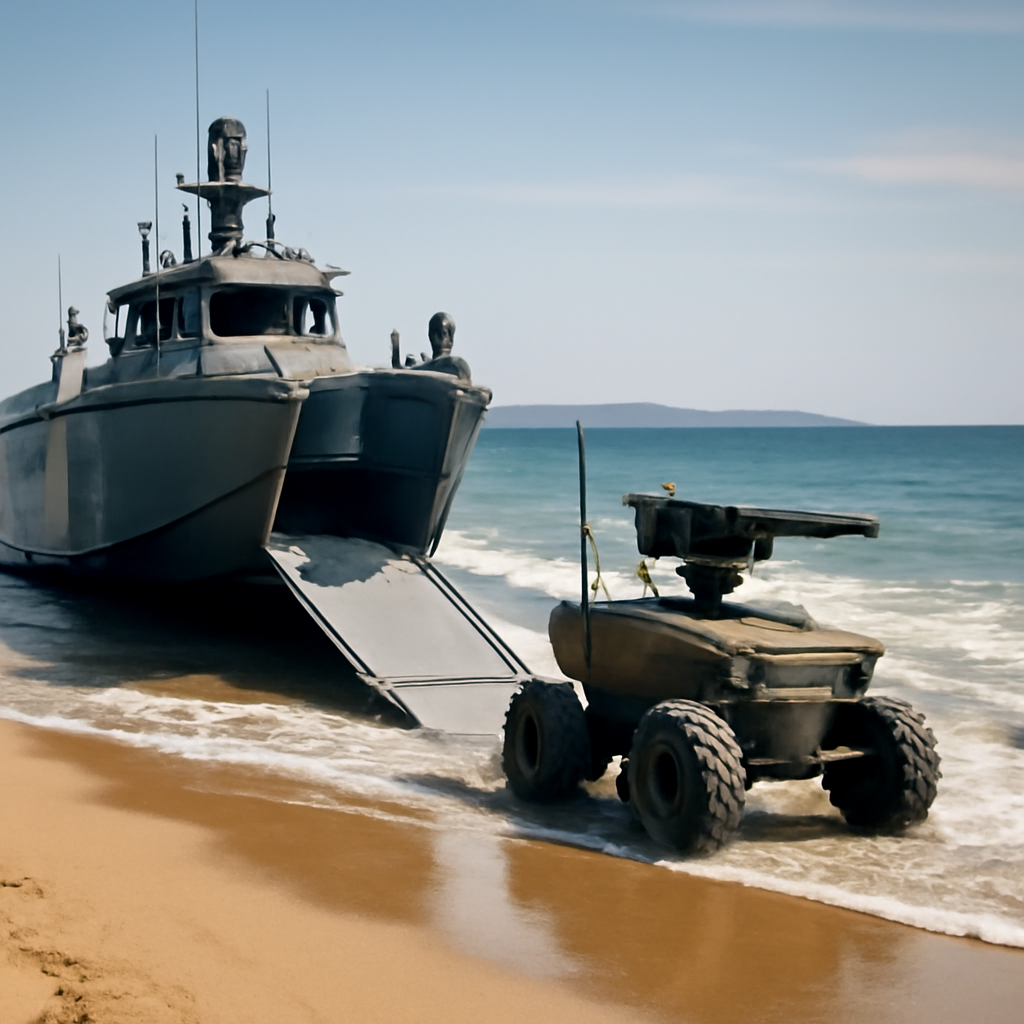
Ukraine Deploys Armed Robot Behind Russian Lines via Drone Boat
In a groundbreaking operation, Ukraine's 123rd Separate Territorial Defense Brigade has successfully deployed an armed robot behind Russian lines using a drone boat, marking a new era in modern warfare. The daring mission was captured on video, showing the robot, armed with a 7.62mm machine gun, engaging a target on the occupied Kinburn Spit.
Europe Targets Russia's Turla in Coordinated Cyber Sanctions
The European Union is cracking down on Russia's notorious cyber-espionage group, Turla, with coordinated sanctions aimed at disrupting their years-long campaign of malicious activities. Nine Russian individuals and four entities, including the FSB's Center 16, have been targeted in the punitive measures.
Nihon Kotsu Cyberattack Disrupts Taxi Operations
Nihon Kotsu, Japan's largest taxi operator, suffered a devastating cyberattack that forced an emergency shutdown of its systems, disrupting taxi operations nationwide. The malware infection was detected on Saturday morning, prompting swift action to contain the breach.
Jscrambler npm Package Infected with Infostealer Malware
A malicious version of the Jscrambler npm package was published, infecting nearly 1,500 downloads with infostealer malware within a two-hour window before being removed and replaced with a safe version. The incident was quickly contained, but users who downloaded the compromised package between releases 8.14 and 8.20 may be at risk.
Malware Disguises as Apple Tool to Steal macOS Credentials
Beware of a sneaky malware that's masquerading as a legitimate Apple tool to steal your macOS credentials! This malicious software, known as CrashStealer, can infiltrate your password managers and even target over 80 browser-based cryptocurrency wallets.
Google and Microsoft Remove ModHeader Extension Exposing Dormant Browsing History Collector
A shocking discovery was made about the popular ModHeader extension, used by 1.6 million Chrome and Edge users, which contained a hidden browsing history collector that thankfully remained dormant. Fortunately, both Google and Microsoft swiftly removed the extension from their stores after it was uncovered.
macOS Malware CrashStealer Exploits Notarization to Evade Gatekeeper Checks
Meet CrashStealer, a sneaky new macOS malware that uses clever tactics to evade detection, including validation of the victim's login password to harvest sensitive data. This native C++ stealer quietly fetches a second-stage payload to steal a broad range of secrets from compromised machines.
MemGhost Attack Plants AI Agent False Memories via Single Email
Imagine giving an attacker the keys to manipulate your AI assistant's memories - and all it takes is one ordinary-looking email to rewrite what it thinks it knows about you. With a new tool called MemGhost, hackers can plant false memories in AI agents, altering their responses and actions over time.
Misconfigured Server Reveals Evilginx Phishing Operators
A shocking security blunder exposed the inner workings of a massive Evilginx phishing campaign, revealing 218 victims across 12 countries, with nearly 94% being corporate targets, who were quietly harvested over the course of a year. The careless mistake, made on a Budapest virtual private server, gave researchers a rare glimpse into the sophisticated phishing ecosystem.
UK, EU Attribute Poland Cyberattack to Russian Spies, Warn Infrastructure Operators
The UK and EU have called out Russia's Federal Security Service for a brazen cyberattack on Poland's power grid, saying it's just another example of their reckless attempts to wreak havoc across Europe. The attack, attributed to FSB's Centre 16, was foiled, but serves as a stark warning for infrastructure operators to stay vigilant.
Citrix Bleed 2 Exploit Fuels Ransomware Attacks
Ransomware attacks are on the rise, fueled by a new exploit that has already made a significant impact, and now a major software company has ordered its customers to take critical systems offline due to a credible security threat. Progress has urged customers to shut down vulnerable Windows servers to prevent potential breaches.
CISA Warns of Exploited Flaws in Joomla Extensions
Stay safe online: a critical vulnerability in the iCagenda extension for Joomla can allow attackers to upload malicious files and take control of your website, leading to data theft and total site compromise. CISA warns that this flaw, tracked as CVE-2026-48939, is being actively exploited, so take action now to protect your site.
Chinese and Indian Spies Target Pakistani Police Systems
Suspected Chinese and Indian spies launched a targeted attack on Pakistani police systems, specifically focusing on the Balochistan Police, between February 2024 and April 2026. The intrusion campaigns compromised sensitive data, including biometric records, criminal case files, and national identity information.
Lidl Online Shop Breach Exposes Customer Data After Service Provider Hack
Lidl's online shop was hit by a data breach after a service provider was hacked, exposing customer information - but fortunately, the online shop's system itself remained secure. The company has notified affected customers and taken steps to address the issue.
Forg365 Phishing Service Targets Microsoft 365 with Advanced Device Code Theft
Meet Forg365, a sophisticated phishing service that's targeting Microsoft 365 users with advanced device code theft capabilities, offering a disturbingly user-friendly operator panel and a subscription-based model starting at just $400 a month. This illicit toolkit is being sold on Telegram, putting sensitive data at risk with its legitimate email delivery infrastructure and AI-powered email generation.
UK Charges Five in Crackdown on Russian Coms Spoofing Platform
In a major crackdown on cybercrime, five London residents have been charged in connection with Russian Coms, a notorious caller-ID spoofing platform that enabled scammers to swindle tens of millions from an estimated 170,000 victims since 2020. The accused allegedly helped fraudsters pose as trusted institutions to trick people into handing over cash and sensitive information.
Threat Actors Leverage AI-Generated Scripts to Accelerate Active Directory Attacks
Cyber attackers are now using AI-generated scripts to supercharge their Active Directory attacks, allowing them to quickly map and exploit sensitive domains, users, and computers. This alarming trend was uncovered by Huntress researchers, who analyzed a sophisticated PowerShell script that bore hallmarks of AI assistance.
Autonomous AI Transforms SOC with Analyst Copilots
Imagine sitting with a Fortune 50 CISO, witnessing a critical moment of clarity: "This is exactly what is wrong with how most security teams are designing their AI architecture right now." It turns out, current AI designs in the SOC are misguided, asking the wrong part of the decision process to do the wrong work.
Cyber-attackers Exploit OAuth Client ID Spoofing in Cloud Environments
Cyber-attackers are increasingly using OAuth Client ID spoofing to infiltrate cloud environments, with multiple campaigns emerging, each with unique tools and infrastructure. This technique allows attackers to cleverly abuse Microsoft Entra ID by mimicking legitimate authentication requests.
Infostealer Infection Enables Argentine FA Breach
A single compromised computer with high-level access likely gave hackers the keys to the Argentine Football Association's database and internal email system, thanks to an infostealer infection that went undetected for months. The breach, traced back to September 8, 2025, highlights the devastating impact of a simple infection on a high-privilege machine.
Progress Software Probes External Threat to ShareFile Storage
Progress Software has alerted ShareFile customers to a credible external security threat targeting its Storage Zone Controllers, and is urging immediate action to protect sensitive data. The company has promised to provide an update within 24 hours and recommends that affected customers disable account access and shut down servers.