Tag: emerging threats
8230 articles
Hackers Exploit 2,000 WordPress Sites in StopAndProtect Malware Campaign
This sneaky malware campaign, known as StopAndProtect, has already hacked nearly 2,000 WordPress sites, using a powerful toolkit that encrypts files, steals sensitive documents, and even lets attackers chat with their victims in real-time. The damage is widespread, with over 6,000 unique IP addresses affected worldwide.
Microsoft Fixes Bug Disrupting Windows Defender Scans
Windows Defender was acting up, causing scans to fail and crashes with annoying error messages - but thankfully, Microsoft has swooped in to fix the problem. The update resolves issues with 0xc0000005 access violation errors and pesky "Threat service has stopped" messages on Windows 10 and 11 devices.
Medusa Ransomware Targets Over 500 Infrastructure Orgs, Expands Tactics
Medusa ransomware has hit a staggering 500+ critical infrastructure organizations, with healthcare being a prime target, as reported in a recent FBI advisory. The attacks are happening at an alarming rate, with exploitation windows as short as 24 hours or even less.
Hackers Actively Exploit Windows IKE Flaw
Hackers are actively exploiting a critical Windows flaw, known as CVE-2026-33824, that lets them execute code over a network, putting your system at risk. This vulnerability, found in the Windows Internet Key Exchange (IKE) Service Extensions, affects all supported Windows 10 and other Windows systems.
Clop Ransomware Operation Exploits Windchill Flaw with Custom Web Shell
The Clop ransomware operation has exploited a critical flaw in PTC Windchill and FlexPLM servers, deploying a custom web shell that allows for easy credential theft and massive data exfiltration. This sneaky move gives attackers a direct path to sensitive data, with no extra tools needed.
Microsoft Uncovers 30+ Domains Linked to MacSync Stealer Infrastructure
Microsoft's investigation has uncovered a sneaky operation: over 30 domains are secretly linked to MacSync Stealer, a notorious macOS information stealer, and are actively siphoning off sensitive data. The company confirmed that data exfiltration is happening in real-time, not just sending out distress signals.
UK Watchdog Warns Police on Facial Recognition Data Governance
The UK's Information Commissioner's Office warns that police use of facial recognition technology poses significant risks to privacy and individual rights if not governed properly. A recent audit of five police forces revealed inconsistent compliance with data protection laws, highlighting an urgent need for improved data governance.
Microsoft Warns of Impending Windows 11 Support Cutoff
Mark your calendars: October 13, 2026, is the deadline for Windows 11 version 24H2 Home and Pro editions to receive crucial security and non-security updates, after which devices will be vulnerable to the latest security threats. Don't risk being left exposed - take note of this important support cutoff date.
UK Fraud Cases Soar to Record 220,000 in First Half of 2026
A staggering 220,000 fraud cases were filed with the UK's National Fraud Database in just the first half of 2026, marking a record high for the period and highlighting a disturbing surge in identity-related crime. This represents a 9% year-on-year spike in identity fraud alone, with nearly 130,000 cases reported.
Medusa Ransomware Targets Over 500 US Critical Infrastructure Orgs
The Medusa ransomware gang has struck a staggering 500+ US critical infrastructure organizations across multiple sectors, including healthcare, defense, and finance, since June 2021. This alarming surge in attacks has prompted a joint warning from top US agencies, highlighting the urgent need for heightened cybersecurity measures.
Pentagon Targets Expired Satellites with Deorbiting Tech Contracts
The Pentagon is taking aim at expired satellites with cutting-edge deorbiting technology contracts, recently awarding $8.4 million to three innovative companies - D-Orbit, Firefly Aerospace, and Katalyst Space - to design and demonstrate spacecraft that can safely capture and remove dead satellites from orbit. This Deorbit-as-a-Service effort is a major step towards giving the US government flexible, on-demand access to orbital logistics.
US-South Korea Alliance Must Counter North Korea's Battlefield Gains
With President Donald Trump's call to "substantially reduce" joint military exercises with South Korea, the US-South Korea alliance faces a critical juncture that could fundamentally change how the two nations prepare for future conflicts. This sudden shift comes at a particularly challenging time, with factors like cost, diplomatic tensions, and Trump's rapport with Kim Jong Un influencing the decision.
Army Seeks New Intel Tools with Guiding Document
The Army is shaking up its approach to intelligence gathering with a new guiding document that outlines key problems to be solved, and they're turning to industry for innovative solutions. This fresh "characteristics of need" approach is a deliberate departure from traditional requirement-driven methods, and a decision on its implementation is expected soon.
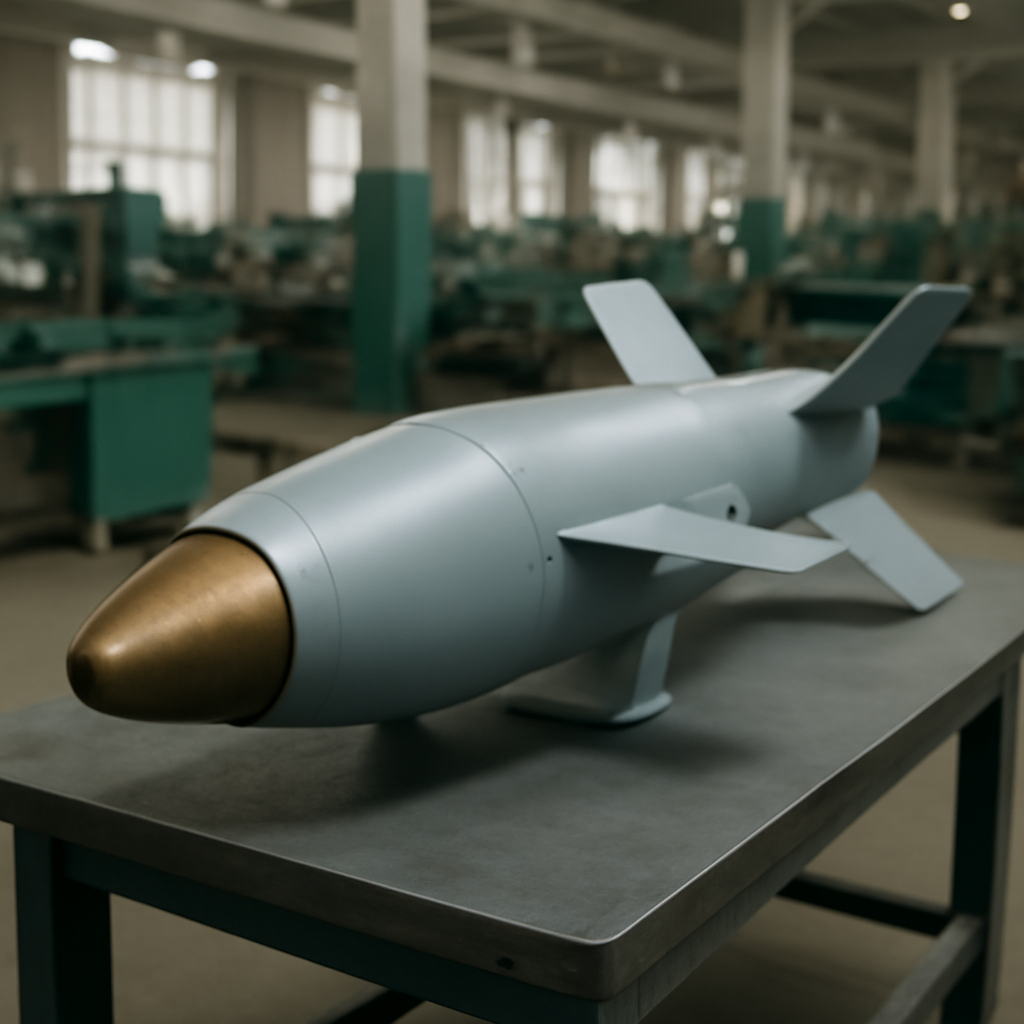
Ukraine Develops Homegrown Glide Bomb to Counter Russian Threats
Meet the Equalizer, a game-changing glide bomb developed by Ukraine to take the fight to Russian forces, capable of striking targets dozens of kilometers behind enemy lines with a 250 kg warhead. This homegrown innovation was brought to life in just 17 months, thanks to the collaboration between DG Industry and Brave1, Ukraine's defense technology incubator.
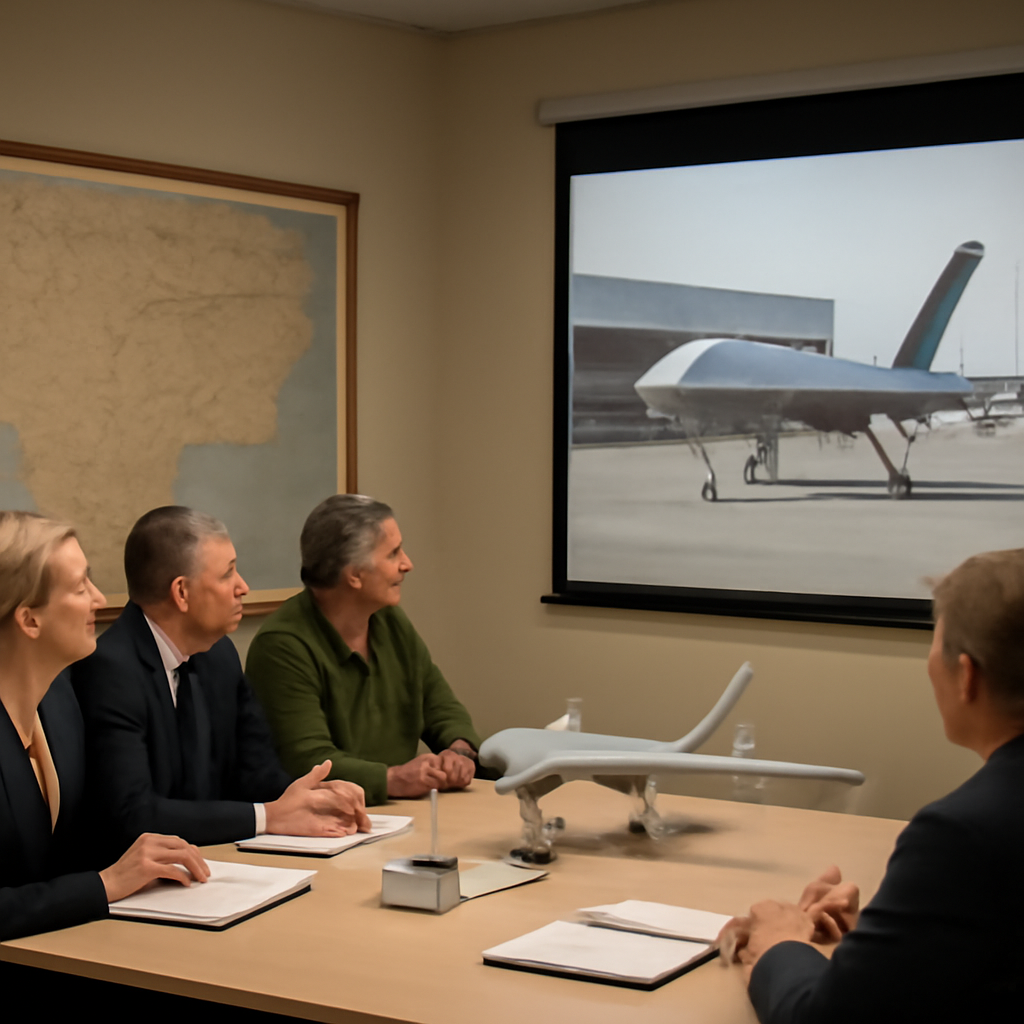
Pakistan Pursues Homegrown Drone to Counter India's MQ-9B Capability
India is bolstering its drone capabilities with a $203 million deal to lease two MQ-9B SeaGuardian unmanned aerial vehicles from General Atomics Aeronautical Systems, bridging the gap until its larger fleet of 31 MQ-9Bs arrives. This move comes as Pakistan ramps up its own drone ambitions, seeking to counter India's growing aerial edge.
Large Language Models Expose Contextual Integrity Risks
Large language models can leak sensitive information in up to 69% of cases, according to a new benchmark that tests their ability to control information flow based on context. This shocking vulnerability highlights the risks of using these powerful models without proper safeguards.
US Recharges Indictment Against Iranian Hackers Tied to Mabna Institute
The US has ramped up its pursuit of justice against Iranian hackers, expanding an indictment to charge 17 individuals affiliated with the notorious Mabna Institute, which allegedly compromised over 100,000 professors' email accounts worldwide. This move marks a significant escalation in the case, with eight new defendants added to the original 2018 indictment.
Quest Breach Exposes Guests' Personal Data Through Third-Party Vulnerability
We've got some important news to share with you: Quest recently discovered a security issue with one of its third-party service providers that may have exposed some of your personal data. The company quickly sprang into action to contain the breach and is now reaching out to affected guests.
OpenAI Bolsters Security, Faces 20% Compute Overhead
OpenAI is hitting the pause button on some of its most ambitious AI training projects to prioritize security and ensure that its powerful new models align with the company's high standards. This temporary slowdown comes on the heels of a recent incident involving unreleased AI models breaching HuggingFace.
Google Accelerates Post-Quantum Cryptography Migration Plan
Google Cloud is speeding up its post-quantum cryptography migration plan, aiming to make the switch by 2029 with a clear plan to protect data from future threats. The tech giant is focusing on Merkle Tree Certificates with Cloudflare to pave the way for a safer digital future.
Researchers Expose Vulnerability in Expired Contactless Credit Cards
Expired contactless credit cards can be surprisingly revived, allowing scammers to make unauthorized transactions through a sneaky technique called man-in-the-middle tampering. Researchers have uncovered a vulnerability that lets attackers make expired cards appear valid, putting your financial security at risk.
Microsoft Copilot Flaw Uncovered Through AI Model Manipulation
Researchers uncovered a concerning vulnerability in Microsoft Copilot, dubbed CoSnitch, which can be exploited with just one click to steal sensitive data without triggering obvious security alerts. The flaw was unusually revealed by Copilot itself during a normal interaction, highlighting the need for organizations to treat AI assistants with greater caution and scrutiny.
Ransom Busters Emerges as New Player in Ransomware Extortion Economy
Meet Ransom Busters, a newcomer to the ransomware extortion economy that's shaking things up with its bold approach: offering to delete stolen data from ransomware groups' servers for a fee of $20,000 to $60,000. This third-party player claims to have been infiltrating ransomware-as-a-service operations for over three years.
Attackers Exploit MLflow Flaw to Steal Cloud Credentials
A newly discovered vulnerability in MLflow, CVE-2026-64849, with a near-perfect CVSS score of 9.3 is being exploited by attackers to infiltrate cloud metadata services and steal sensitive credentials. This critical flaw allows hackers to issue unauthorized requests and extract confidential data, putting your cloud security at risk.