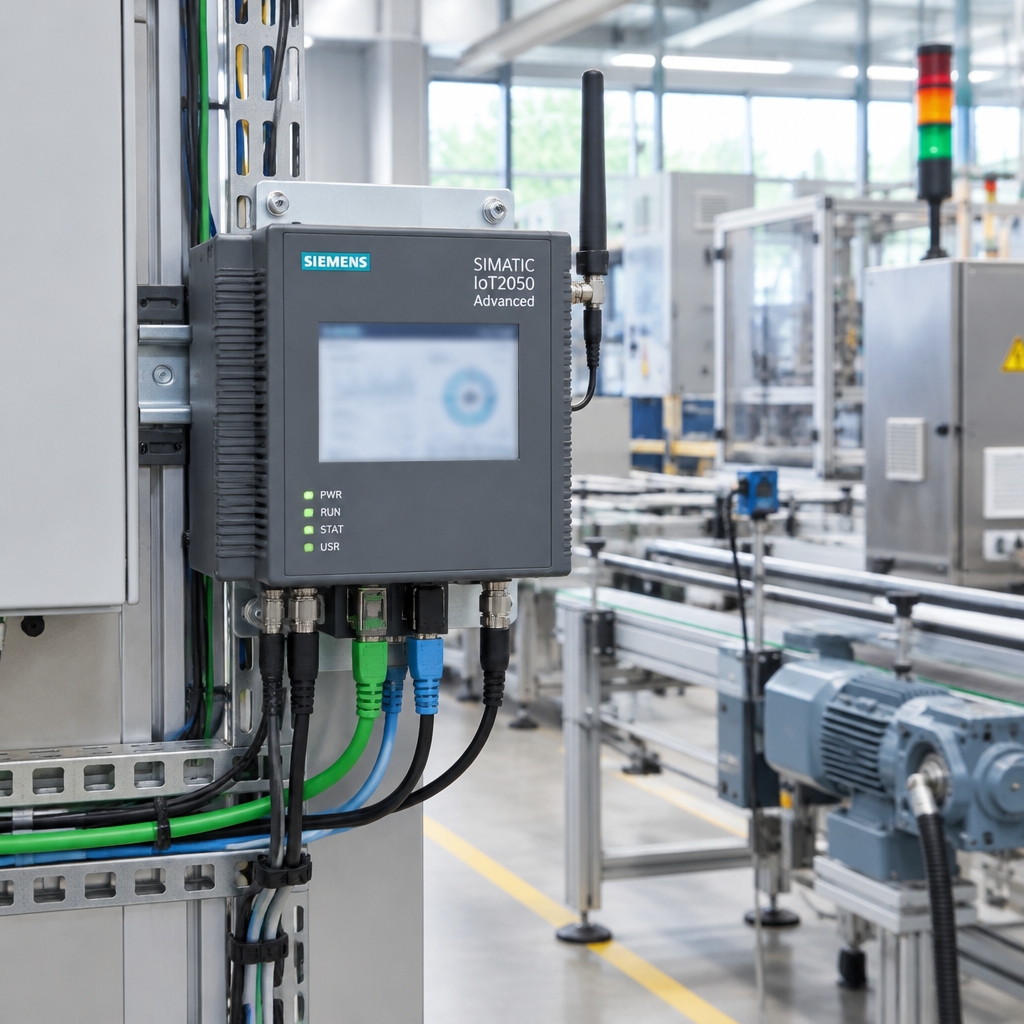
"SIMATIC IoT2050 Advanced devices running Industrial OS with Node-RED installed contain a missing authentication vulnerability in the Node-RED HTTP interface that could allow an unauthenticated remote attacker to create malicious flows and execute arbitrary code on the underlying server with maximum privileges," Siemens said in an advisory released back in August 2026.
CVE-2026-58115: a maximum-severity, unauthenticated code‑execution hole
The vulnerability tracked as CVE-2026-58115 carries a CVSS score of 10.0 and impacts Siemens SIMATIC IoT2050 Advanced devices that run Industrial OS with Node-RED installed. Siemens published a remediation path in August 2026: update to Industrial OS version 4.3.4.1 or later. Where immediate updating is not possible, Siemens advised either uninstalling Node-RED or hardening its installation by enabling HTTPS access, securing the editor and admin API with credential-based authentication or an OAuth/OpenID provider, and protecting HTTP Nodes and the Node-RED Dashboard with basic authentication.
VulnCheck observed live exploitation on October 30, 2026
As of October 30, 2026, security researcher Patrick Garrity and the team at VulnCheck reported attacks against their honeypot network that attempted to weaponize CVE-2026-58115. Garrity described the initial exploit as "a complete exploit" that deployed a Node-RED flow, triggered it automatically, and fetched a Linux bot binary from an attacker-controlled server, all encoded behind multiple layers.

Nobody's watching your logs at 2 AM.
Full SOC coverage without building one. Nubivance deploys and manages Rapid7 InsightIDR and MDR for organizations that need detection and response, not another dashboard.
Get coverageHow the malicious Node-RED flows delivered and ran payloads
VulnCheck captured specific delivery mechanics. Early exploit traffic used a Node-RED flow that executes a shell-script wrapper which attempts to download an AMD64 bot binary from 85.215.73[.]250 using wget, with curl as a fallback. The downloaded file was written to /dev/shm/.b and executed. Attackers later moved to a two-stage technique in which the initial wget retrieves a second shell script named "wget.sh" from the same server.
In another observed request, actors used wget or curl to fetch a payload hosted at 45.194.90[.]57:38472, saving it as .sys_update on disk and then writing it to /tmp/.kworker—an apparent attempt to disguise the executable as a benign kernel worker thread—before executing it. VulnCheck could not retrieve either "wget.sh" or ".kworker," so the exact behavior of those second-stage payloads remains unknown.
Backdoors that persist beyond memory-resident implants
Not every exploit attempt fetched a downloader. VulnCheck found multiple requests that deployed Node-RED flows exposing an HTTP input endpoint (for example, /cmd or a randomly named path) wired through a function node to an exec node with addpay enabled. That design lets an attacker pass arbitrary commands later via a query parameter and execute them with the server’s privileges. Garrity warned that "This backdoor survives even if a memory-backed implant is lost on reboot," underscoring that attackers can create persistent remote-command access without leaving a conventional file-based implant.
What this means for SIMATIC IoT2050 operators, security teams, and procurement leaders
- SIMATIC IoT2050 operators: If devices run Industrial OS with Node-RED, they face a direct, unauthenticated remote-code-execution risk unless patched to 4.3.4.1 or later or Node-RED is removed. Operators should check for unexpected Node-RED flows, exposed HTTP endpoints such as /cmd, and binaries placed under /dev/shm or /tmp with names like .b or .kworker.
- Security teams and incident responders: Because attackers can deploy flows that accept commands via HTTP query parameters and survive reboot, detection cannot rely solely on memory-resident implant checks. Teams should correlate network indicators (connections to 85.215.73[.]250 and 45.194.90[.]57:38472 were observed) with host artifacts and Node-RED flow configurations, and treat unknown shell scripts retrieved by Node-RED as high-risk.
- Procurement leaders and asset owners: The advisory offers two paths—remediate by upgrading Industrial OS to 4.3.4.1+ or remove Node-RED. Where Node-RED is a required component, contract and procurement decisions should ensure timely patch windows and the option to enforce hardened Node-RED configurations (HTTPS, credential or OAuth/OpenID admin protection, and basic auth on HTTP nodes).
The observed campaign shows a straightforward but effective exploitation lifecycle: unauthenticated flow deployment, automated execution, and payload retrieval from attacker-controlled hosts, plus an evolution toward multi-stage downloads and remote-command backdoors that persist across reboots. Key unknowns remain limited to the contents of the second-stage scripts and payloads that VulnCheck could not fetch; those gaps change the calculus only in degree, not in kind. The immediate, actionable facts are clear: patch to 4.3.4.1 or later or remove and harden Node-RED, inspect Node-RED flows and exposed endpoints, and block or monitor the observed command-and-control hosts.
Source: https://thehackernews.com/2026/11/attackers-exploit-critical-siemens.html