"They said they 'tested the complete chain only with US accounts and vehicles.'" That restrained line, supplied by researchers Shubham Shah and Sam Curry, underscores both the reach of what they found and the limits of what they demonstrated: a few lines of default configuration left exposed a path from a web login server to the ability to unlock and start cars.
The flaw in ForgeRock OpenIDM and Apache Felix
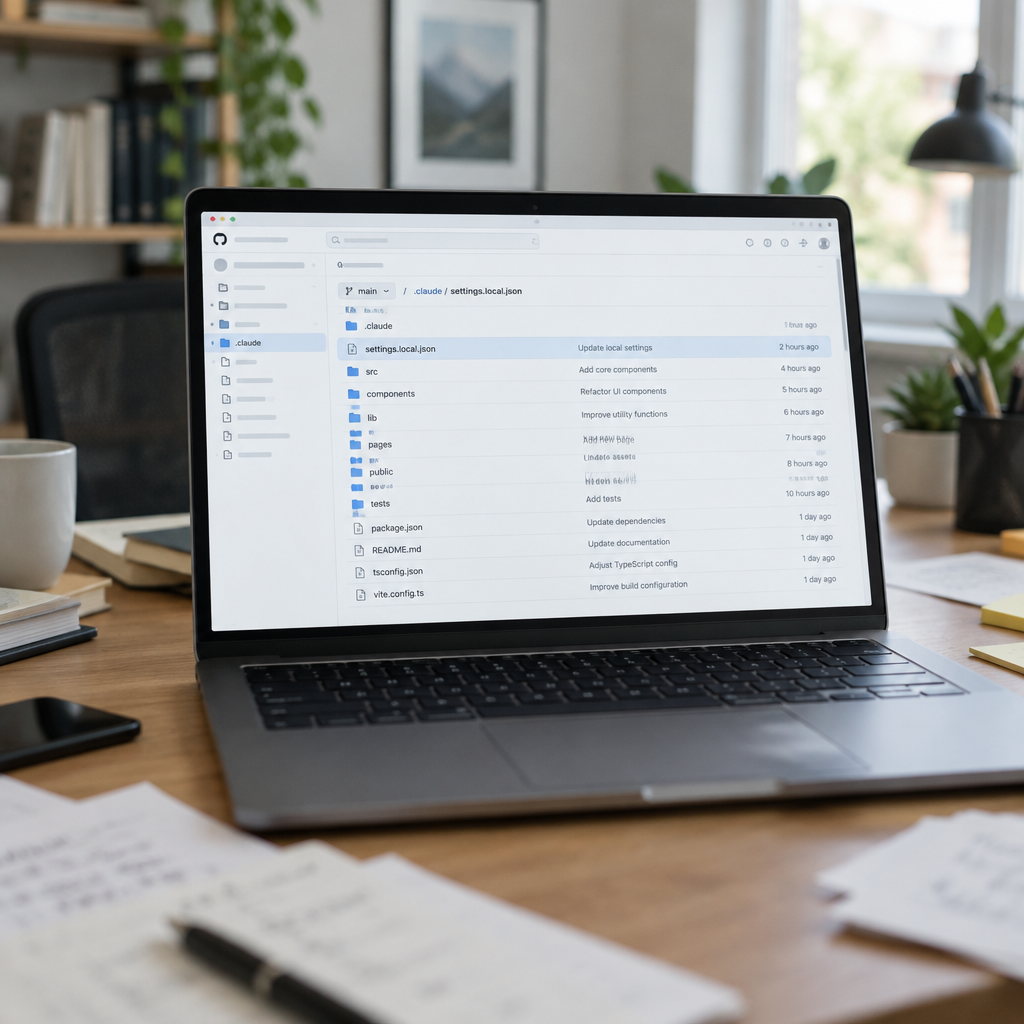
Both automakers' mobile apps authenticated customers using ForgeRock (now part of Ping Identity). The identity platform runs two parts: one for login and one called OpenIDM that stores customer records. OpenIDM includes an administrator console powered by the Apache Felix tool at /system/console. That console stores its own credentials separately from the rest of the system.
ForgeRock's production hardening guide already instructs operators to remove the console or protect it before going live. In the affected deployments the console was still present and still protected by the documented default: the username and password were both the word admin.
Attack chain: from console to car
The researchers reported a multistep, entirely server-side takeover. The console itself was blocked from the open internet, but the edge device protecting the service and the Java application on the server interpreted request paths differently. By adding encoded slashes and extra characters the researchers caused the edge to classify a request as a safe static file while the server treated it as a request to the console. With the default credentials, they logged in.
Inside the console they used a built-in scheduler to run small scripts that executed code on the identity server, gaining a command prompt on the machine that holds customer records for both brands' logins. From there they changed a target account's email address and password, signed in as that customer through the normal app, and obtained the same access tokens the real app uses.
Those tokens provided the vehicle-control keys. Using the account's vehicle commands, the researchers unlocked the doors and started the engine of a test car (with the owner standing next to it), then stopped the engine and locked it again. Their write-up emphasizes they ran vehicle commands only on cars they owned or were allowed to use.

Audit-ready is a season. It shouldn't be.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scrambleScope, timing, and additional findings
Shah and Curry published their U.S. tests and said the full chain was tested only with U.S. accounts and vehicles in February 2026. They said both affected systems were fixed about two hours after they reported the problem. Shah published a separate analysis targeting the Australian systems for the same two brands; there, the vector was different: admin credentials for the identity server had been left in the app's code for a test setup.
Taken together, the researchers said they could send unlock and engine-start commands to the brands' cars in Australia, the United States, and Canada. The Australian post does not give a date for when those systems were fixed. The researchers also noted the attack leaves little for an owner to notice: changing the email and password does not log the owner out of their app, and alerts can be redirected to the attacker's phone. They returned the real email address after their tests. Neither write-up states whether anyone else discovered or abused the same path before it was closed.
What Identity Teams Should Check
- Look for the Apache Felix console at /system/console and remove it or change its default password before going live; the console's existence and default credentials are documented and warned against in ForgeRock's hardening guide.
- Do not rely on edge or WAF path rules alone to hide an admin page. A path the edge and the server parse differently can slip past controls, as it did here; operators should validate that protections are effective end to end, not only at the perimeter.
What this means for technologists, vehicle owners, and vendors
Technologists and security teams should treat deployment configuration as part of the product’s attack surface: a documented, default admin account on an identity server is not a software bug but an operational risk that can be exploited remotely. Vehicle manufacturers and their identity operators will need to audit production instances of OpenIDM/PingIDM and remove or secure the Apache Felix console.
Vehicle owners have little visibility into this class of problem; Shah and Curry's test shows that a takeover of the identity layer can be used to send legitimate vehicle-control commands without leaving obvious traces on the owner's app. Vendors must ensure that alerts and session handling cannot be silently redirected by changes to account records.
The case is a blunt reminder that long-documented configuration guidance matters. The console and its default password are known, the hardening steps exist, and yet the components remained exposed across multiple regions. One concrete open question remains in the public record: neither write-up says whether anyone else found or used the path before it was closed.