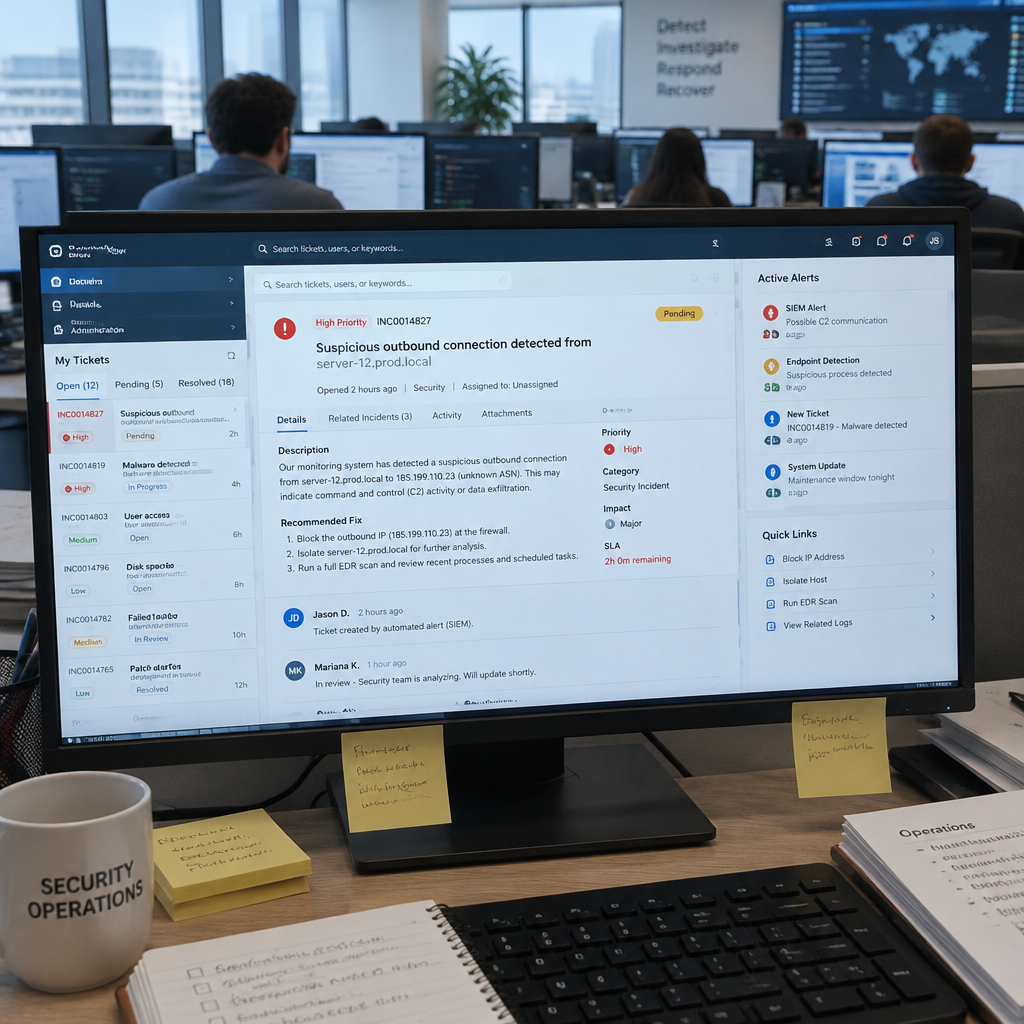
"The alert is critical. The fix is known. And the ticket sits in a queue for days." — The Hacker News
The Observe, Prove, Act, Confirm cycle
Security teams and operations groups too often diverge when a known fix collides with production risk. The Safe Remediation approach described in the source breaks the path from recommendation to enforcement into four concrete stages: Observe, Prove, Act, and Confirm. Observation uses existing telemetry — vulnerability scans, IPS traffic, device utilization, endpoint policy states and configurations — to show the context around a proposed change. Proof tests how a protection will behave in that context, using methods appropriate to each control (for example, IPS protections run in Detect mode to collect false-positive and performance data; OS hardening is trialed on a selected test group). Act executes the approved change through the systems that manage the control. Confirm verifies the result — policy installation, host checks, and execution records that document user, timestamp, and the associated exposure.
Why protections stay in Detect mode
Many organizations already own defenses they do not enforce. The white paper cited in the source found that 47% of measured organizations had less than 50% protection enablement. The reasons are practical: teams fear false positives, lack inspection capacity, and worry about disruptions to business continuity. That reluctance produces a growing gap between capability and enforcement — signatures remain inactive, policies drift, and exceptions accumulate — leaving environments exposed despite having controls on the shelf.

Audit-ready is a season. It shouldn't be.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scrambleUse virtual patches and existing controls while patching
Patching fixes vulnerabilities at their root, but testing, coordination, and deployment schedules can delay full patch rollout. During that window, the source recommends using compensating controls already present in the environment. An existing IPS signature or a virtual patch can be correlated with vulnerability data to determine whether a suitable protection exists and whether it is inactive, in Detect mode, or already enforced. The remediation record should distinguish interim protection from the permanent fix: a compensating control reduces immediate exposure while the underlying vulnerability remains open and "requires follow through."
Keep approval and execution connected through existing tooling
Safe remediation ties the approval of scope to the systems that apply the change. Where appropriate, organizations can require human sign-off or permit automated execution through configured workflows. The approved change then runs through the technology responsible for that control: IPS changes via the security management server, operating-system hardening through patch-management infrastructure, and supported endpoint changes via the vendor API. Confirmation completes the loop: policy installation can show an IPS protection reached enforcement, host checks can verify hardening changes, and execution records reveal failed or pending actions alongside the responsible user and timestamp.
Measured outcomes: enforcement that shows results
The source reports strong, quantifiable outcomes for the environments analyzed. Across measured organizations, remediation actions recorded a 99.5% success rate. Over one month, protections applied through remediation subsequently blocked 703.56 million attacks, including 21 million blocked within 24 hours of remediation. These figures are presented as evidence that enforcement — when carried out with validation and confirmation — produces measurable reduction in exposure and active blocking of malicious activity.
What this means for security teams and infrastructure and application owners
- Security teams: Use observation and proof stages to build the evidence operations teams need. Correlate vulnerability findings with control coverage to identify protections that can be validated and activated as interim or permanent responses.
- Infrastructure and application owners: Expect decisions to be tied to test evidence. The approach recommends running hardening or configuration changes on selected hosts first and relying on execution records and host checks to confirm outcomes before broad enforcement.
Safe remediation reframes the familiar trade-off between security and availability as a procedural challenge: gather evidence, test in-place protections, execute through the systems already responsible for the control, and verify the result. The source points to Check Point Exposure Management as an implementation that links exposure prioritization to environmental validation, controlled execution, and confirmation through existing security technologies. For organizations that already have protections sitting in Detect mode, the pragmatic question is not which controls to buy, but how to convert those dormant capabilities into verified, enforced protections without breaking production. The white paper makes a case that a structured, evidence-driven path can do just that.