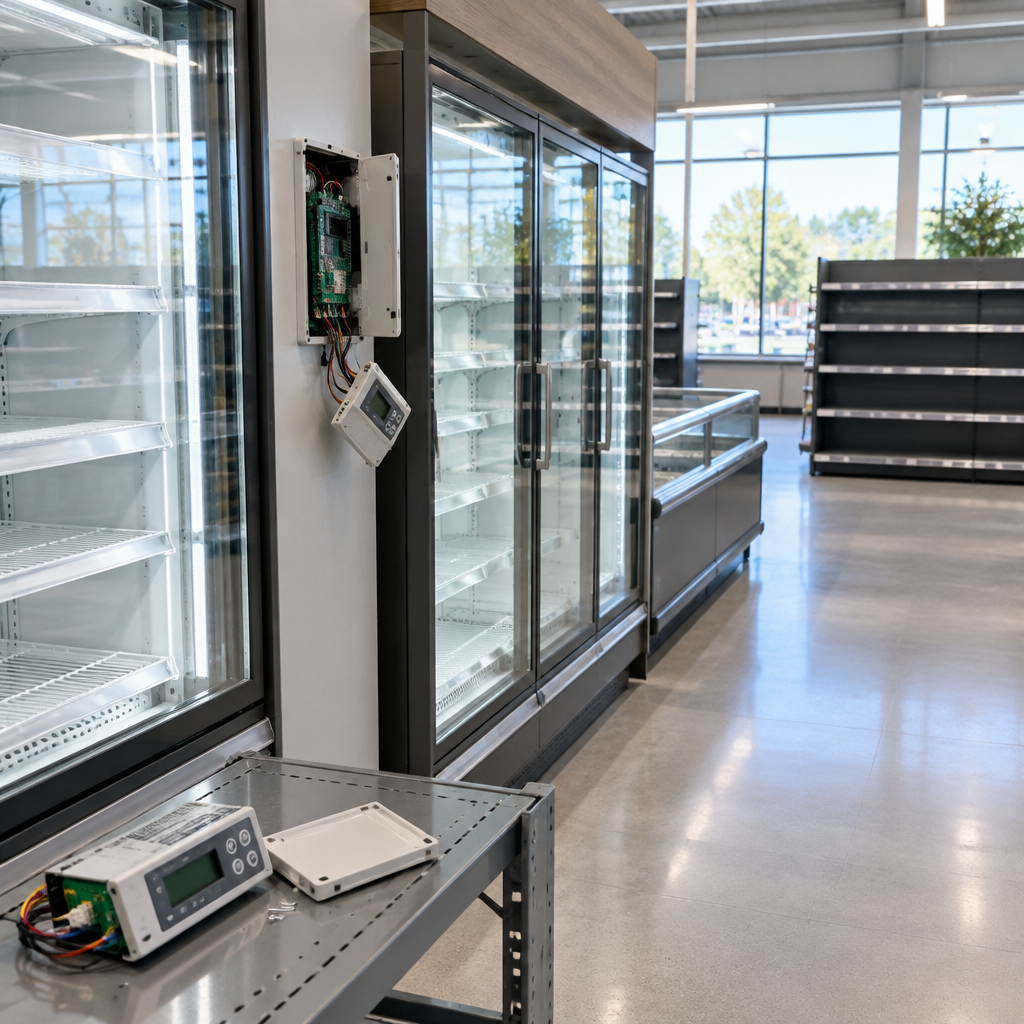
About 700 French retail sites had their refrigeration controllers sabotaged on the night of October 11, a campaign that the French government says was carried out by Shahid Kaveh, a cyber unit of Iran's Islamic Revolutionary Guard Corps (IRGC).
France's attribution: Shahid Kaveh and the IRGC
The government’s public statement, coordinated through France’s cyber crisis coordination center (C4), attributes the October sabotage to Shahid Kaveh, a cyber unit the authorities say operates under the IRGC. C4 — which brings together ANSSI, the DGSE and DGSI security services, the armament directorate and the cyber defense command — cited four indicators tying the operation to the unit and to an IRGC sponsorship.
The unit is known publicly through hacktivist personas such as CyberAveng3rs and Cyber Isnaad Front, and a propaganda outlet called CyberbanNews reported on the incident as early as October 13, France said. Prosecutors running the criminal inquiry, led by France’s anti-cybercrime office (OFAC) and the DGSI, reported attack methods, the use of Persian language, and IP addresses tracing to devices in Iran among the evidence used for attribution.
How the attackers did it: controllers, defrost cycles and linked reconnaissance
According to a prosecutor’s press release, attackers took remote control of Danfoss and Dixell refrigeration controllers through exposed web interfaces. They started abnormal defrost cycles with no time limit and disabled the temperature probes’ safety alerts that should trigger when temperatures climb above a safe threshold. The prosecutor’s office said the attack “caused about 20 fires.” Earlier government commentary described food losses and, in at least 15 cases, fires.
C4 also tied the operation to simultaneous reconnaissance of Schneider Electric equipment at several small hydroelectric installations; the effects on that equipment were described as moderate. Investigators noted the attackers used the FOFA scanning tool and reconnaissance techniques Shahid Kaveh has employed since at least April, and that the same attack infrastructure was used for both refrigeration and Schneider Electric probing.

Audit-ready is a season. It shouldn't be.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scrambleTargets and the scale of the damage
C4 said most victims were large retail chains, naming Casino, Leclerc, Coopérative U, Metro, Carrefour and Intermarché. Smaller operations — butcher shops, a slaughterhouse and cooperative food plants — were also affected. The ministry estimated food losses at “several tens of millions of euros” and called the operation the first offensive cyber campaign on French soil carried out purely for sabotage.
Legal and diplomatic steps: prosecutions, arrest requests and sanctions
Paris prosecutors opened a judicial investigation against the head of Shahid Kaveh, the head’s two deputies and anyone else identified, and have requested international arrest warrants. The offenses under investigation include illegally interfering with computer systems and causing damage by means dangerous to people, with both charges made more serious by an asserted aim of serving a foreign power, Iran.
The Foreign Ministry plans to summon Iran’s ambassador and to ask European partners to adopt new sanctions against the Iranian organizations and individuals involved in the attack, France said.
What operators should do: CERT-FR guidance for Danfoss, Dixell and Copeland controllers
France’s CERT-FR issued an incident alert identifying compromises across four product families: Danfoss AK-SM and AK-SC series, the Copeland xweb, and the Dixell xweb. The alert warned campaign activity was probably still underway and stressed that exposing a controller management interface to the internet “goes against good practice.”
- For controllers not yet compromised: remove internet exposure and any unit reachable at a public IP address; check insurance contract terms before cutting off a contractor’s data feed; review the full configuration with special attention to defrost ranges; restore access only via secure VPN or a protected network; as an emergency measure, firewall-filter contractors’ IP addresses but treat that as temporary; follow vendor guidance — for Danfoss this includes updating firmware, setting security level to Strict and changing default passwords.
- For compromised controllers: remove internet exposure and check insurance terms; restart Danfoss equipment or restore devices to factory settings; restore access only through a secure VPN or protected network; reconfigure before returning devices to service and follow the maker’s recommended practices.
- CERT-FR warned that end-of-life devices receiving no security fixes face very high risk if they remain internet-exposed: a factory reset removes attacker persistence but does not eliminate the underlying vulnerability, and such devices will almost certainly be re-compromised if left exposed.
France’s attribution statement did not address a new wave of refrigeration attacks that struck supermarkets in several other European countries the previous week, leaving open the question of links beyond French territory. For now, prosecutors have opened investigations, diplomats will summon an ambassador, CERT-FR has published concrete remediation steps, and C4 has placed the incident at the center of France’s cyber-safety and legal response.