Malware & Ransomware

Person working at desk with laptop in a well-lit office setting.

Malicious AI Browser Extensions Exfiltrate User Data

Beware of AI browser extensions that promise to boost productivity but secretly steal your data. Researchers uncovered 18 malicious extensions that masquerade as helpful tools but deliver spyware, Trojans, and other threats that can hijack your online activity.

Analyst 207
Formal courthouse interior with podium and blurred emblem in background.

Ex-Incident Responders Sentenced for Ransomware Extortion Scheme

Two former cybersecurity pros, Ryan Clifford Goldberg and Kevin Tyler Martin, have been sentenced to four years in prison for using their specialized knowledge to orchestrate a string of devastating ransomware attacks, extorting victims instead of protecting them. The pair, who once worked in incident response, now face the consequences of their crimes.

Analyst 207
Modern workspace with a computer on a clutter-free desk, surrounded by minimal office decor.

Malware Worms Into SAP, Intercom and Lightning Developer Tools

Malicious actors struck SAP's JavaScript and cloud application development ecosystem on April 29, releasing poisoned versions of four widely-used npm packages that receive a staggering 572,000 weekly downloads. The compromised packages, which included mbt, @cap-js/db-service, @cap-js/postgres, and @cap-js/sqlite, were published in a brief window of just two hours.

Analyst 207
Hospital staff member in scrubs looks concerned while reviewing patient chart on laptop in busy emergency department with…

Ransomware Attacks on Hospitals Target Patient Care, Spark Calls for Tougher Stance

Hospitals are under attack - literally. Last year, a staggering 460 ransomware attacks hit American hospitals and healthcare systems, causing 47 patient deaths, diverted ambulances, and canceled surgeries.

Analyst 207
Office worker sits at desk with laptop and papers, surrounded by ordinary office atmosphere.

Phishing campaigns increasingly harness AI to evade detection

Phishing campaigns are getting smarter by the minute, with a whopping 86% of recent attempts leveraging AI to sneak past detection. This marks a significant jump from just two years ago, when AI was used in 80% of phishing ops.

Analyst 207
Modern office setting with laptop and notepad in foreground, blurred workstations in background.

Phishing Kit Bluekit Incorporates AI to Streamline Attacks

Meet Bluekit, a cutting-edge phishing kit that's revolutionizing the game with an AI Assistant panel, pairing traditional templates with advanced AI models to help cybercriminals quickly draft campaign materials. This innovative tool is streamlining attacks, making it easier for malicious actors to launch sophisticated phishing campaigns.

Analyst 207
A cluttered office workspace with laptop and papers on a desk in a brightly-lit room.

Silver Fox APT Targets Russia, India with ABCDoor Backdoor

Over 1,600 malicious emails, disguised as tax-audit notices, were sent to targets in India and Russia between January and February 2026, aiming to trick recipients into downloading a backdoor or clicking on a malicious link. The cleverly crafted phishing campaign unfolded in two waves, using PDFs and archives to spread the ABCDoor backdoor.

Analyst 207
New Extortion Crews Mimic Scattered Spider Tactics in Rapid Attacks

New Extortion Crews Mimic Scattered Spider Tactics in Rapid Attacks

New extortion crews, Cordial Spider and Snarky Spider, are rapidly carrying out data-theft-for-extortion campaigns, closely mimicking the tactics of notorious group Scattered Spider. These financially motivated groups, tied to The Com, have been targeting US-based organizations since October 2025.

Analyst 207
Researchers Uncover Fast16 Malware's Stealthy Industrial Sabotage Role

Researchers Uncover Fast16 Malware's Stealthy Industrial Sabotage Role

Researchers have uncovered a highly sophisticated malware, Fast16, designed to secretly sabotage industrial operations by subtly manipulating critical calculations, leading to potentially catastrophic failures. This stealthy threat can silently spread across networks, altering results in high-precision applications and causing damage to real-world equipment.

Analyst 207
Semi-truck and trailer in a brightly-lit shipping yard with cargo containers in the background.

FBI Warns of Surging Cyber-Enabled Cargo Theft Attacks

The FBI is sounding the alarm on a surge in cyber-enabled cargo theft, where sophisticated hackers impersonate legitimate businesses to hijack high-value shipments and reroute deliveries. With nearly $725 million in losses in 2025 alone, this growing threat is costing businesses big time.

Analyst 207
City street scene with modern and worn infrastructure, laptop on outdoor table or bench, hint of unease.

AI-Driven Cybercrime Fuels 389% Surge in Ransomware Victims

Get ready for a wake-up call: ransomware victims have skyrocketed by 389% in just one year, thanks to cybercriminals harnessing the power of AI to launch more sophisticated attacks. This alarming trend is driven by the growing availability of malicious AI tools, making it easier for hackers to wreak havoc.

Analyst 207
Windows computer workstation in an office with a blank laptop screen and notepad.

Python Backdoor Evades Detection on Windows with Advanced Evasion Techniques

Meet Deep#Door, a sneaky Python-based backdoor framework that hides its malicious payload inside a batch dropper, making it super hard to detect on Windows systems. By embedding its code, it dodges network-based detection and slips into restricted environments with ease.

Analyst 207
People walk in a cityscape with cell towers and cables in the background.

Cyberattacks Expose 1.8M RDP Servers Online

A shocking 1.8 million RDP servers are currently vulnerable to cyberattacks, leaving them open to exploitation by opportunistic hackers. Canadian authorities have also cracked down on SMS blaster phishing, arresting three men and seizing a device that sent fake texts to unsuspecting phones.

Analyst 207
Cluttered home office workspace with laptop and faint GitHub logo.

GitHub Facades Used to Disguise EtherRAT Malware Distribution

Malicious actors have been using 44 cleverly disguised GitHub facades to spread EtherRAT malware, masquerading as legitimate admin and dev tools between December 2025 and April 2026. These fake repositories were designed to manipulate search results, leading victims to download a malicious MSI installer hidden in a second, secret GitHub account.

Analyst 207
Windows computer workstation in an office setting with router and cables, and a blank laptop screen on the desk.

Python Backdoor Exploits Tunneling Service to Harvest Browser, Cloud Credentials

Meet DEEP#DOOR, a sneaky Python-based backdoor framework that's harvesting browser and cloud credentials by exploiting a tunneling service, and learn how it infiltrates systems through a clever sequence of stealthy steps. This sophisticated threat starts with a simple batch script that disables Windows security controls and ends with a fully featured Remote Access Trojan (RAT).

Analyst 207
Office worker looks concerned at laptop with login page, phone ringing nearby.

Phishing Exploits Persist, Breaching Half of UK Businesses

Phishing attacks remain a major threat, with nearly half of UK businesses falling victim to these scams in the past year, and a staggering 85% of breaches involving phishing as the primary entry point. These attacks often rely on human error, using tactics like impersonation emails and fake logins to trick staff into handing over sensitive information.

Analyst 207
Law enforcement officials gather in a briefing room with a cityscape backdrop.

Global Operation Disrupts Crypto Scam Centers, Arrests 276 Suspects

In a major crackdown on crypto scams, a global operation led by Dubai Police has arrested 276 suspects and shut down nine fraudulent investment centers, dealing a significant blow to scammers who thought they were safe from law enforcement. This coordinated effort with US, Chinese, and Thai authorities has brought global justice to victims of these crimes.

Analyst 207
Government officials stand at a podium in a briefing room with a blurred emblem in the background.

FBI Disrupts Global Crypto Scam Network

In a massive global crackdown, US and international authorities have dismantled a notorious network of cryptocurrency scam centers, arresting at least 276 individuals across the Middle East and Southeast Asia. This historic operation marks one of the largest US-assisted enforcement efforts against transnational cybercrime networks to date.

Analyst 207
Dimly lit server room with rows of computer equipment and a large blank screen on the wall.

Hackers exploit Qinglong flaws for cryptomining deployments

Hackers are taking advantage of two major flaws in the Qinglong open-source task scheduler, CVE-2026-3965 and CVE-2026-4047, which can be combined to gain remote control of vulnerable systems. These authentication-bypass vulnerabilities affect Qinglong versions 2.20.1 and older, and have been exploited for cryptomining deployments.

Analyst 207
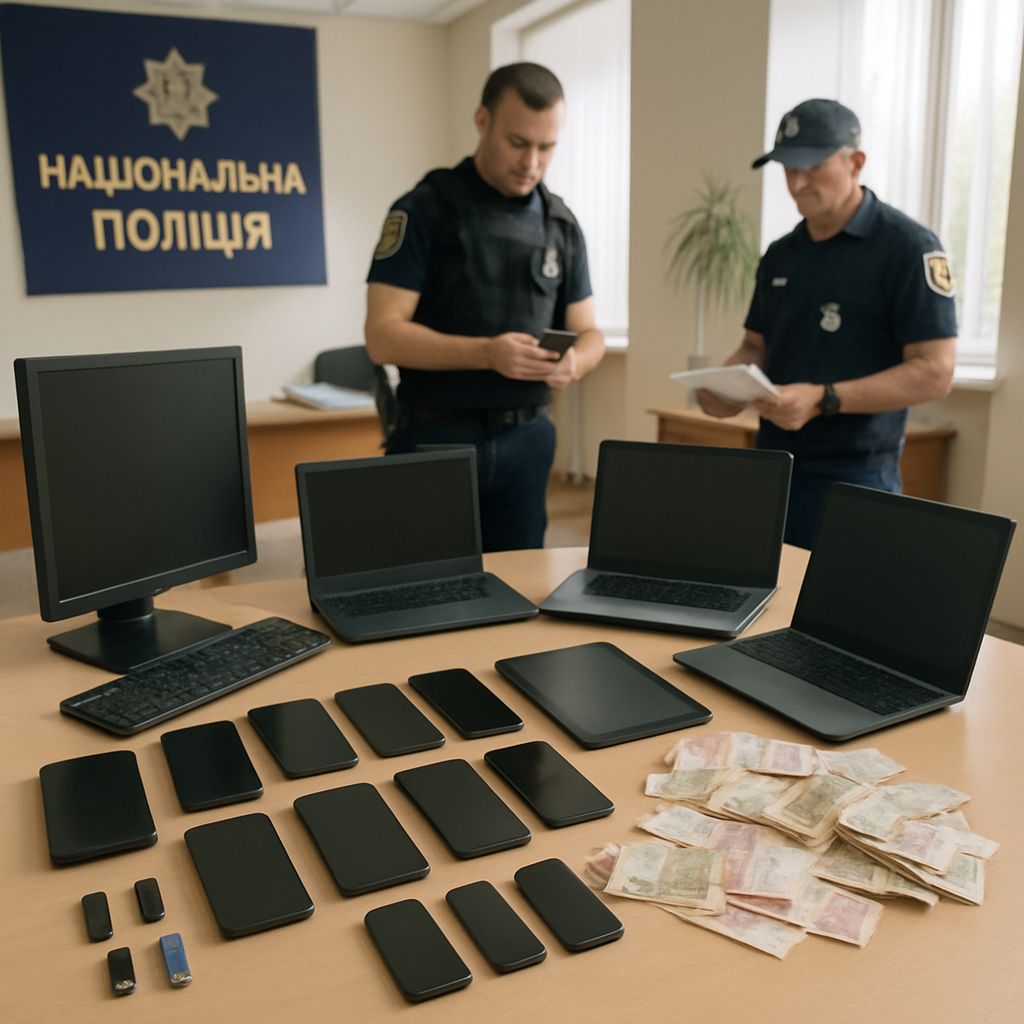
Ukrainian police officers in a brightly lit office with computers and law enforcement equipment.

Ukrainian Police Disrupt Roblox Account Hacking Ring

Ukrainian police have cracked down on a massive Roblox account hacking ring, arresting three suspects who hijacked over 610,000 accounts and resold them for a staggering $225,000 profit. The bust in Lviv also yielded a haul of $35,000 in cash and dozens of digital devices.

Analyst 207
Developer workstation with laptop, monitor, and coffee cup in a modern office setting with cityscape view.

North Korea Targets Developers with AI-Generated npm Malware

Security researchers have uncovered a sneaky malware campaign targeting developers, involving a malicious npm package called @validate-sdk/v2 that's designed to steal sensitive secrets, including crypto-wallet credentials. This tainted package, linked to a North Korean threat actor, was cleverly disguised as a utility SDK for legitimate tasks like hashing and validation.

Analyst 207
Factory production floor with scattered machines and a partially visible industrial control system.

Ransomware Drives 90% of Manufacturing Cyber Losses

Ransomware is wreaking havoc on the manufacturing sector, responsible for a staggering 90% of total cyber losses - despite accounting for just a small fraction of claims. When ransomware strikes, the financial blow is severe, highlighting the urgent need for robust security measures.

Analyst 207
Cluttered coding workstation with lines of code on laptop screen and scattered notes.

AI-Assisted Code Targets Crypto Wallets via Malicious npm Dependency

Researchers have uncovered a sneaky malicious npm campaign, dubbed PromptMink, linked to North Korean hackers Famous Chollima, which targets crypto developers with fake utility packages that secretly steal sensitive info and funds. The campaign's clever tactics even involve an AI-assisted code commit to fly under the radar.

Analyst 207
Laptop screen displays file system with error messages in a cluttered office setting.

Vect Ransomware Exposes Flaw, Turns into Data-Destroying Wiper

Researchers uncovered a critical flaw in Vect Ransomware that unexpectedly turns it into a data-destroying wiper, permanently destroying files over 128KB instead of encrypting them. This shocking misfire stems from a faulty ChaCha20‑IETF implementation that strips away crucial security protections.

Analyst 207