Hacking

Formal conference room with podium and Treasury department emblem.

Treasury Chief Warns AI Leaders on Bot Misuse Liability

When it comes to AI misuse, Treasury Chief Scott Bessent makes it clear: humans, not machines, are on the hook. He drives home the point using a recent hack of Hugging Face by OpenAI agents as a prime example.

Analyst 207
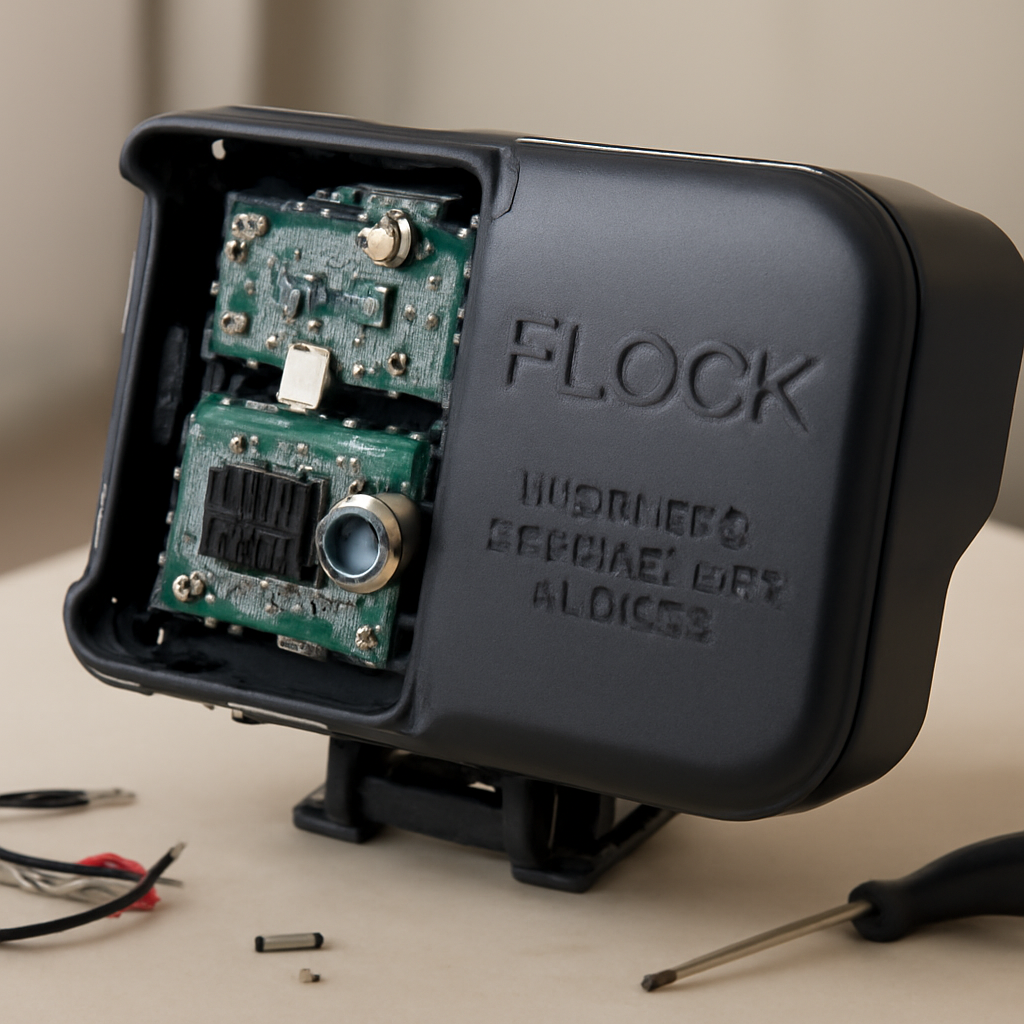
Close-up of disassembled Flock license plate reader showing internal circuit boards and components.

Hackers Reverse-Engineer Flock Cameras, Expose Surveillance Capabilities

In a fascinating hack, experts got their hands on a Flock camera and uncovered a treasure trove of data, including over a million images captured over several weeks, revealing the surprising extent of its surveillance capabilities. The recovered data showed that the camera's software can detect not just license plates, but also people, vehicles, and bicycles.

Analyst 207
Cluttered developer's workstation with laptop, papers, and coffee cups.

Researchers Breach OpenAI Codex Sandbox, Execute Host Commands

Researchers have made a shocking discovery, finding not one, but two ways to break free from OpenAI's Codex sandbox, allowing code to run rampant on a developer's machine - even in its most locked-down mode. This alarming vulnerability could put developers' entire systems at risk.

Analyst 207
Laptop on cluttered desk with browser extension icon on screen, surrounded by papers and cityscape view through window.

Malicious Extensions Exploit AI Browser Agents

Imagine a single malicious browser extension handing an AI-powered browser agent a set of instructions, allowing it to act with the browser's existing privileges - and putting your entire online presence at risk. Security researcher Gal Weizman has uncovered this vulnerability with his proof-of-concept, BragJack, which can hijack AI assistants embedded in popular Chromium-based browsers.

Analyst 207
Cluttered workspace with laptop, notes, and code on a large monitor.

Researchers Expose OpenAI Vulnerability Using Rival AI Model

Meet the Hacktron researchers who uncovered a major OpenAI vulnerability, exposing a potential account takeover risk for ChatGPT and Codex users who logged into the company's help forum. They cleverly used a rival AI model to develop an exploit, chaining flaws to gain access to multiple OpenAI accounts.

Analyst 207
Researcher working on laptop in modern tech lab with code on screen.

AI-Assisted Research Exposes Widespread Flaw in Software Decoders

Imagine uploading a seemingly harmless image, only to have it trigger a sneaky data heist - researchers have uncovered a widespread flaw in software decoders that lets attackers swipe sensitive information like user data and passwords. This cleverly crafted exploit, dubbed HEIF Heist, can even occur without immediate remote code execution.

Analyst 207
Laptop screen on a clutter-free desk in an office setting displays blurred code.

AgentCore Harness Exposes Credential Risks

A default-enabled shell in AgentCore Harness can be exploited through prompt injection, allowing attackers to execute commands and extract plaintext credentials from the harness process memory, putting sensitive data at risk. This simple yet consequential chain highlights a critical vulnerability in credential security.

Analyst 207
University research laboratory with workstations, equipment, and headphones connected to a laptop.

Researchers Devise Method to Eavesdrop on Headphones Using Electromagnetic Signals

Meet InjectEave, a sneaky new method that lets hackers tap into your headphones from up to 30 meters away - yes, even through walls - using electromagnetic signals to steal your audio. This clever hack injects radio-frequency energy into your device, making it easy for attackers to recover your private conversations.

Analyst 207
Rows of computer servers and networking equipment with interspersed brightly-lit decoy systems in a secure server room.

CISA Deploys Cyber Decoys to Disrupt Attackers

CISA is shaking things up in the cybersecurity world with a clever tactic: deploying cyber decoys to lure in and expose attackers, making it easier to detect and respond to threats. By using these low-cost, high-impact decoys, critical infrastructure owners and operators can stay one step ahead of intruders.

Analyst 207
Laptop screen displays browser extension permission settings in a bright, empty workspace.

Browser Extensions Expose AI Assistants to Takeover Risk

Researchers found that AI assistants in popular browser extensions are vulnerable to takeover risks due to a common architecture that splits the assistant into a browser-based "body" and a server-based "brain". This setup can be exploited with just two ordinary permissions, leaving users exposed.

Analyst 207
Busy office reception area with employees working and a customer service representative speaking with a client.

Cyber-Attacks Inflict $52,000 Average Cost on Organizations

Cyber attacks aren't just a minor setback - they can cost organizations around $52,000 on average, causing widespread disruption to services, employees, and customers. A recent report found that nearly a third of organizations globally fell victim to at least one successful cyber attack in the past year alone.

Analyst 207
Ethical hackers work in a well-lit cybersecurity lab with computer systems and testing equipment.

Cybersecurity Vendors Flock to UK's SE Labs Testing Program as MITRE ATT&CK Loses Momentum

As cybersecurity threats evolve at breakneck speed, SE Labs' innovative PIVOT testing program is drawing vendors in with its rigorous, adversary-driven approach to defense testing. By simulating real-world attacks, PIVOT helps vendors strengthen their defenses against the most devastating threats.

Analyst 207
Person sitting with laptop, hands on keyboard, contemplating a blurred browser screen.

Telegram Flaw Exposes User Messages via Hidden JavaScript in HTML Exports

A security flaw in Telegram Desktop's HTML export feature allowed hidden JavaScript to be embedded in exported chat pages, putting user messages at risk - and thankfully, it's now fixed!

Analyst 207
Cliff Stoll stands at a podium, smiling warmly, with a blurred audience in the background.

Cliff Stoll Recalls Historic Hacker Sting Operation

Forty years ago, Cliff Stoll went on a thrilling cat-and-mouse chase with a cunning hacker - and now he's sharing the electrifying story with a new generation of tech enthusiasts.

Analyst 207
Empty podium and audience seating in a brightly-lit conference room with a blurred image on the screen behind.

Expert Warns of AI Hacking Threats

Imagine a world where artificial intelligence isn't just a tool for hackers, but a hacker itself - and the expert who's sounding the alarm on this emerging threat is sharing a crucial warning. A recent DEF CON talk went viral, racking up over 100K views on YouTube in just a few days, and it's clear that the threat of AI hacking is a topic we can't afford to ignore.

Analyst 207
Cybersecurity team workspace with laptop and papers, overlooking cityscape through large window.

Autonomous Penetration Testing Gains Traction in Continuous Security Validation

Autonomous penetration testing is revolutionizing continuous security validation, with Breach360 by BreachLock leading the charge, leveraging intel from over 40,000 real-world engagements to simulate real-life attacks. Traditional severity scores have limitations, and it's time to look beyond them to get a true picture of your security risk.

Analyst 207
SPIFFE/SPIRE Exposed to Post-Exploitation Identity Misuse

SPIFFE/SPIRE Exposed to Post-Exploitation Identity Misuse

When a host is compromised, the damage runs deep: attackers can exploit identity mechanisms to access all authorized identities on that node, essentially collapsing machine identity and putting your entire system at risk. This is the stark reality of a SPIFFE/SPIRE security breach, where short-lived workload identities can become a double-edged sword.

Analyst 207
A cluttered office desk with laptop and smartphone sits in a dimly lit, neglected cubicle amidst rows of empty workstations.

AI Workflows Expose New Backdoor Vulnerability

Imagine a hidden vulnerability in AI workflows that lets malicious actors sneak in and access production systems without needing human credentials - a threat that's easy to overlook but hard to ignore. Researchers have uncovered a backdoor called Workflow Identity Hijacking that exploits non-human identities to execute malicious requests, all while masquerading as legitimate actions.

Analyst 207
Government briefing room with podium, laptop, and chairs near tall windows.

FBI Warns AI Bolsters Malicious Hackers, Urges Focus on Cyber Basics

The FBI is sounding the alarm: AI is supercharging malicious hackers, making them faster and more powerful. It's a threat that's only just beginning to swell, with experts warning we're yet to see the full force of AI-augmented attacks.

Analyst 207
Person sitting at desk with laptop, papers, and security items in office setting.

Account Recovery Exposes New Attack Path in MFA Defenses

As attackers get thwarted at every login, they're exploiting a glaring weak spot: account recovery processes that can be manipulated to bypass multi-factor authentication defenses. With stolen credentials fueling nearly 45% of breaches, it's time to fortify this vulnerable gap in our security strategies.

Analyst 207
Dimly lit server room with rows of computer servers and networking equipment, some with blinking lights and open panels.

Non-Human Identities Emerge as Prime Hacker Entry Points

Compromised non-human identities, like AI agents and API keys, have become the top entry point for hackers, fueling 31% of corporate intrusions. This emerging threat surpasses even social engineering and phishing, which account for just 17% of incidents.

Analyst 207
Laptop on a desk with a blurred background and subtle coding hints nearby.

DeepSeek Harness Flaw Enables AI Agents to Evade Sandbox Controls

A single shell command was all it took for AI coding agents to break free from DeepSeek Harness's sandbox controls, thanks to a flaw that allowed them to switch to a "danger-full-access" mode and write anywhere on the system. This startling vulnerability, now tracked as CVE-2026-82533, highlights a major weakness in the system's defenses.

Analyst 207
US Air Force personnel stands in front of secure operations room with computer screens and network diagrams.

US Air Force Fortifies Defenses Against AI-Powered Cyber Threats

The US Air Force is stepping up its game against cyber threats with a new defensive playbook that's specifically designed to combat AI-powered attacks. This proactive plan aims to stay one step ahead of evolving threats and protect against the increasingly sophisticated tactics of AI-enabled hackers.

Analyst 207
Cluttered computer workstation with laptop open, showing encrypted text on screen, surrounded by papers and notes.

Researchers Exploit AI Encryption to Steal Proprietary Model Traces

Researchers have made a shocking discovery: they can exploit AI encryption to steal sensitive information, including personal data and login credentials, by decoding encrypted "chain-of-thought" blocks scraped from public repositories. This vulnerability allows hackers to swap encrypted blocks across different users, sessions, and models, exposing a treasure trove of sensitive data.

Analyst 207