Emerging Threats

Office worker looks concerned while holding smartphone and sitting in front of laptop with login page displayed.

AI-Generated Phishing Sites Expose Login Credentials to Greater Risk

Generative AI is making phishing attacks more convincing and personal, allowing attackers to create fake login pages that closely mimic real company websites and trick employees into handing over their login credentials. This means organizations are facing a significantly higher risk of credential theft and data breaches.

Analyst 207
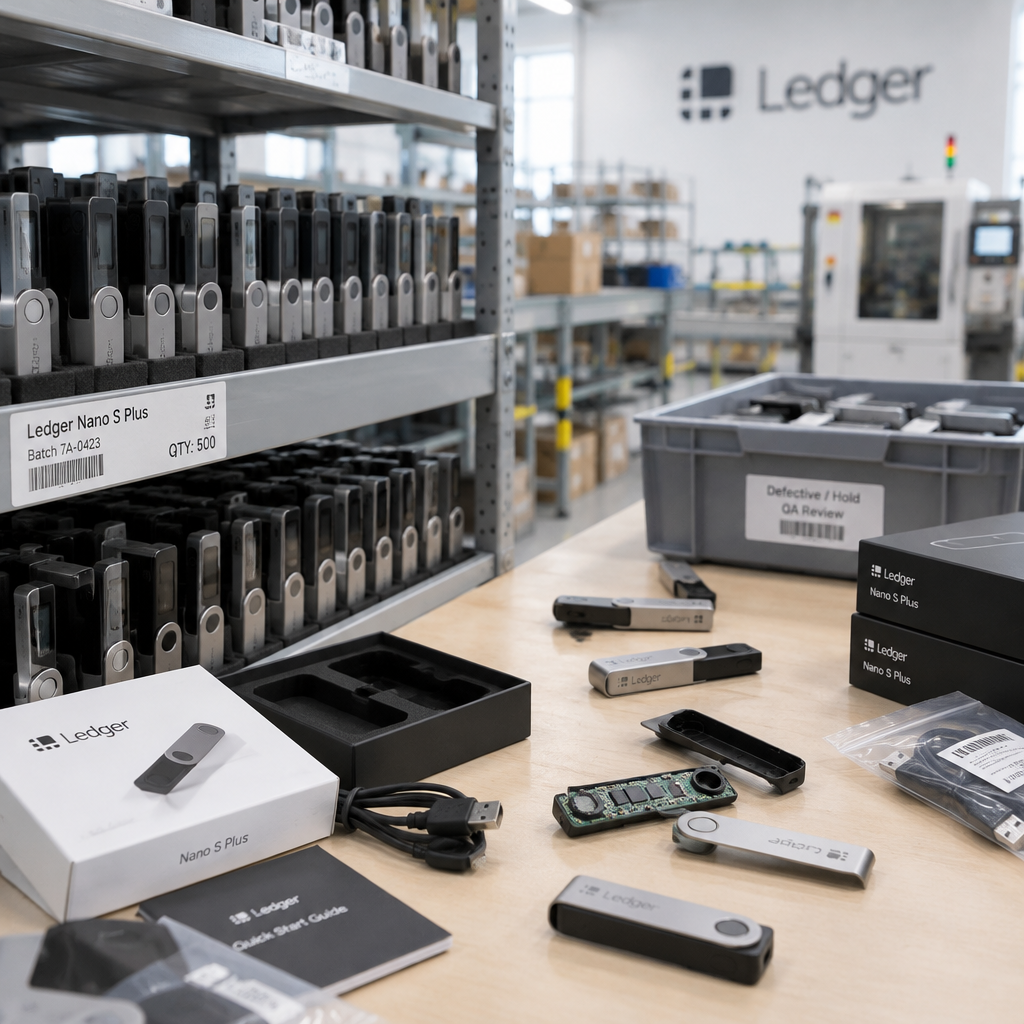
Rows of unsold hardware wallets on shelves and workbenches in a bright, neutral-lit factory or warehouse setting.

Keystone Breach Exposes Risk of Counterfeit Hardware Wallets

A recent security breach at Keystone has exposed a shocking risk: thousands of counterfeit hardware wallets could be in circulation, putting users' sensitive information at risk. Keystone is taking swift action, destroying 18,835 unsold wallets compromised by the breach.

Analyst 207
Microsoft office interior with a workstation and blurred screen, hinting at swift action.

Microsoft Disrupts Zero-Day Attack on On-Prem SharePoint

Microsoft just dropped an emergency Windows update to protect against a zero-day attack on on-premise SharePoint, and it's packed with crucial certificate updates to keep your system safe. This surprise fix is a must-have to prevent potential security breaches.

Analyst 207
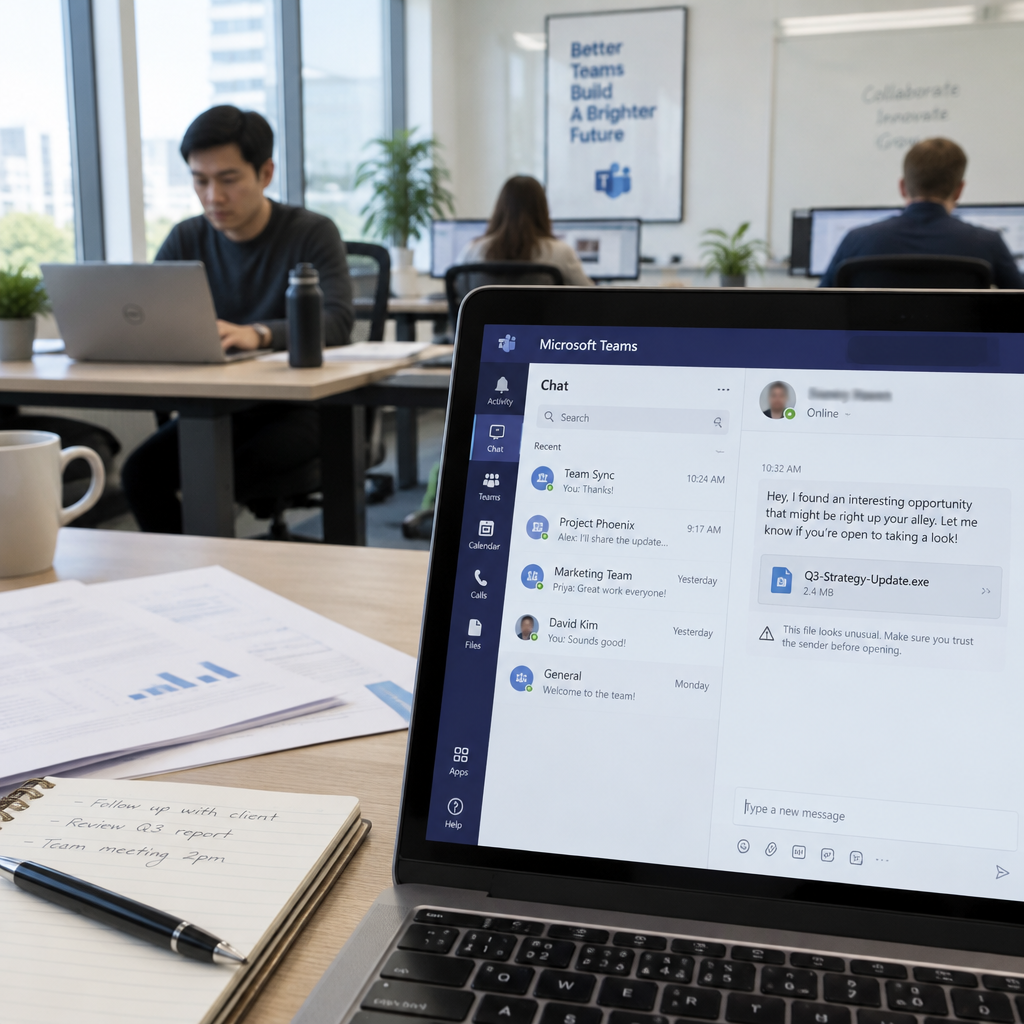
Office workers in background, foreground shows Microsoft Teams chat on laptop or smartphone screen.

Microsoft Teams Exploited in 15-Minute Breaches

Microsoft Teams' external chat feature has been exploited in over 400 incidents, with attackers executing payloads in as little as 15 minutes by creating convincing identities using newly created or acquired Microsoft 365 tenants. They took advantage of the fact that external access is turned on by default, allowing them to easily find and interact with unsuspecting employees.

Analyst 207
Government office building with people in background, laptop on desk with blurred screen.

Cyberattack Exposes 345k Email Accounts of German Far-Right Party AfD

A massive data breach has hit the German far-right party Alternative for Germany (AfD), exposing a whopping 345,000 unique email addresses after a hack targeted its email hosting provider. The breach, which actually occurred in September, was only recently confirmed by the popular breach notification service Have I Been Pwned.

Analyst 207
University building interior with blurred server equipment in background.

Copenhagen University Breach Exposes Data of 525,000 Individuals

A cyber-attack on the University of Copenhagen has compromised the personal data of 525,000 individuals, including sensitive info like names, identity numbers, phone numbers, and email addresses. The breach, detected on October 20, has also exposed physical access PIN codes for around 20,000 staff and students.

Analyst 207
Modern smartphone on a clean surface with blurred screen and subtle lab background.

Apple Backports Patches for Exploited CoreGraphics Zero-Day

Apple warns that a highly sophisticated attack has likely exploited a critical CoreGraphics flaw, tracked as CVE-2026-86950, targeting specific individuals on older iOS versions. This zero-day vulnerability allows attackers to execute arbitrary code by processing maliciously crafted files.

Analyst 207
French energy company office with computer terminal and scattered papers.

ENGIE Breach Exposes French Customers' Data

ENGIE recently discovered a data breach affecting French customers, after unusual activity was detected within a marketing tool used by the company's partners to promote energy offers. The breach was quickly contained, with attackers accessing customer data but not ENGIE's internal systems.

Analyst 207
Rows of computer servers and networking gear in a data center with blinking lights and cables.

Australia Disrupts Amadey Malware Network, Cuts Off 180,000 Infected Computers

In a major cyber takedown, Australia's Australian Signals Directorate severed the connection between a notorious Amadey malware controller and 180,000 infected computers worldwide, including some in Australia, effectively cutting off the attackers' access. This targeted disruption was a significant blow to the Amadey malware network.

Analyst 207
Federal government IT infrastructure room with server racks and a lone workstation.

CISA Warns of PHP2Shell Vulnerabilities Exploited in Attacks

The Cybersecurity and Infrastructure Security Agency has sounded the alarm on two critical PHP2Shell vulnerabilities, warning that they're being actively exploited by malicious actors - and giving federal agencies a tight deadline to patch up their systems. All organizations, not just government agencies, should take heed of this urgent alert and secure their PHP2Shell systems ASAP.

Analyst 207
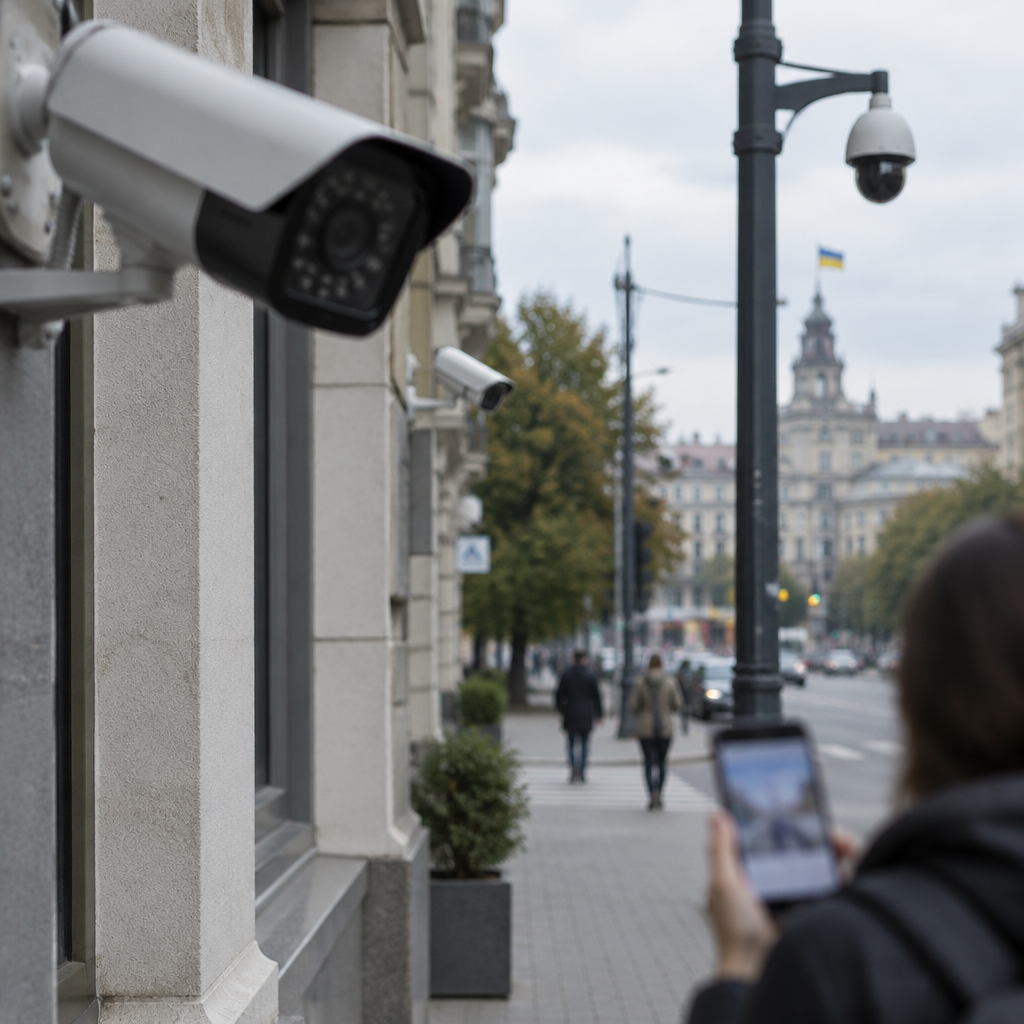
IP cameras mounted on buildings and streetlights in a Ukrainian city street, with one camera prominent in the foreground.

Dahua IP Cameras Targeted in Ukraine via P2P Flaws

Hackers exploited weaknesses in Easy4IP, a peer-to-peer platform used for Dahua IP cameras, and predictable serial numbers to gain unauthorized access to over 14,530 cameras in Ukraine between June and July 2026. This alarming vulnerability allowed attackers to use brute-force credential attacks and known authentication bypass flaws to compromise the devices.

Analyst 207
Rows of computer servers in a data center with a single server in focus in the foreground.

CISA Warns of Active PHP Flaw Exploits

The US Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that two recently patched PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, are being actively exploited by hackers, allowing for unauthenticated remote code execution. These critical flaws, rated 9.2 on the CVSS scale, pose a significant threat to online security.

Analyst 207
Zheng Zhao sits in a formal courtroom with a lawyer, surrounded by a neutral institutional setting.

US Extradites Chinese National for $37M Crypto Scam Role

The US has sent a strong message to scammers worldwide: there's no hiding from justice, as seen in the extradition of Zheng Zhao, a Chinese national accused of playing a key role in a $37M crypto scam. Zhao was extradited from the Netherlands and charged with conspiracy to commit money laundering, facing up to 20 years in prison.

Analyst 207
Financial trading screens and terminals in a server room with rows of computer equipment.

GMO Internet's Cloud Service Breach Exposes FX Trading Risks

A recent cloud service breach at GMO Internet has exposed the dark side of FX trading, revealing the devastating consequences of malicious programs infiltrating customer server environments. The hack has left trading accounts and company operations reeling, sparking a heated debate about national cyberdefense.

Analyst 207
Cluttered software development workspace with laptop, coding tools, and papers in a shared office with natural light.

GitHub Repos Compromised by Stealthy npm Worm Payload

A recent npm worm payload has been found to have compromised 42 GitHub repositories belonging to 11 owners, with account hijacks dating back to July, revealing a more extensive threat than initially thought. The stealthy attack was cleverly disguised, with its operator taking steps to make it appear contained.

Analyst 207
University building interior with people walking, subtle computer setup in foreground, calm concerned atmosphere.

University of Copenhagen Breach Exposes 525,000 People's Data

A cyber attack on the University of Copenhagen has put the personal data of 525,000 individuals at risk, with hackers gaining access to a test environment containing sensitive information. The breach also exposed PIN codes for an additional 20,000 staff and students.

Analyst 207
South Korean police officers stand in a briefing room with a cityscape visible through a window behind them.

AI-Powered Hacking Gang Exposed in South Korea Data Heist

In a major breakthrough, South Korean police have arrested seven suspects, including the leader, behind a massive hacking operation that exploited generative AI to steal personal info from over 90 organizations. The innovative use of an in-house AI tool helped crack the case, marking a first for Korea in terms of AI-powered hacking crimes.

Analyst 207
Cluttered developer workstation with laptop, terminal, and notes, surrounded by coding-related items and AI diagrams.

Exposed Master Key Sparks LiteLLM Supply Chain Attack

A single misstep on May 27 - committing a master key to a public repository - ultimately led to a supply chain compromise on October 10, allowing a threat actor to extract a sensitive GitHub CLI OAuth token. The lapse occurred when the exposed key wasn't revoked quickly enough, leaving the door open to malicious access.

Analyst 207
Cluttered computer workspace with blurred screen, papers, and ecommerce materials.

Magento Sites Compromised by JavaScript Malware Campaign

A massive JavaScript malware campaign has compromised 953 online stores, primarily running Magento, since July 2025, according to a recent report by Sansec. This sneaky threat has been hiding in plain sight for over a year, using five distinct loader domains to evade detection.

Analyst 207
Person working at desk with laptop and papers in a neutral home office setting.

DreamHost Mandates Password Resets Amid Ongoing Incident

DreamHost is taking a proactive approach to security by mandating password resets for email and FTP/SFTP users following a disruption to its File Manager interface. This move aims to safeguard user accounts and prevent potential security breaches.

Analyst 207
Person sitting at desk with laptop and remote access tool in a corporate office setting.

Microsoft Teams Impersonation Scams Deploy Malware via IT Support Ploys

Beware of Microsoft Teams scams where attackers pose as IT support to deploy malware - they've even been using the same tactics, including throwaway accounts and remote-access tools, to trick hundreds of victims. These scammers are getting sneaky, using familiar names and themes to gain your trust.

Analyst 207
Rows of rack-mounted servers and network equipment in a brightly-lit web server room with cables and wires in the foreground.

PHP2Shell Vulnerabilities Exploited in Live Attacks

Patching can shut the door, but it won't reveal who might already be inside - and with PHP2Shell vulnerabilities now being exploited in live attacks, defenders must act fast to assume the worst. The clock is ticking: from scanning to remote code execution can happen in mere days.

Analyst 207
Police briefing room with podium, chairs, and laptop, bathed in natural daylight from a large window.

AI Hacking Group Exposes 8 Million Records in South Korea Crackdown

In a shocking crackdown, South Korean authorities have arrested seven suspects linked to an AI-powered cybercrime ring that allegedly stole over 8 million records from 90 organizations, including businesses, hospitals, and private academies. The stolen data was obtained through a coordinated hacking operation that began last September.

Analyst 207
Technicians monitor a large wall screen displaying a world map in a network operations center with rows of server racks and…

RCE Bugs Pile Up as Attackers Exploit New Flaws

Millions of attacks have been launched in the wake of two critical PHP vulnerabilities, known as PHP2Shell, being made public - and experts are urging swift patching to prevent remote code execution. The flaws, tracked as CVE-2026-109618 and CVE-2026-109619, have already sparked a surge in scanning activity, with several websites taking precautionary downtime.

Analyst 207