[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
A simple mistake has led to a massive data breach, exposing sensitive personal info of 1,300 county employees and their families, and now taxpayers may face a $25,000 bill to clean up the mess. County Records Manager Mike Bridges accidentally attached a confidential spreadsheet with Social Security numbers to a public-records response, and it only came to light after the error was too late.
GitHub has disrupted a sneaky attack that used automation to steal sensitive secrets from thousands of repositories. Over 13,500 branches were created to carry out the secret-stealing scheme, which was cleverly designed to operate under the radar.
A Chinese national has been extradited to the US and charged with masterminding a crypto scam that swindled nearly $37 million from 174 American victims. The suspect, Zhen Zhao, faces up to 20 years in prison if convicted of conspiracy to commit money laundering.
A working exploit for a Linux kernel flaw has been made public, putting systems at risk before a fix was available or a CVE identifier assigned. This sequence of events creates a narrow window of vulnerability, leaving Linux systems potentially exposed to attack.
UK Biobank has finally restored security to its Research Analysis Platform after a massive data leak exposed sensitive information on 500,000 volunteers, forcing months of lockdown and remediation efforts. The breach had made the highly valuable biomedical dataset available for sale on a Chinese e-commerce site.
Be cautious when using Telegram and WeChat on your mobile device, as a potent spyware called uCreator can hijack your account if you install tampered app versions or run WeChat in a third-party container. This sneaky malware embeds its code into working app copies, allowing it to run with the app's own identity and permissions.
A recent security breach campaign, dubbed Gheist, used stolen GitHub tokens to infiltrate over 850 accounts, exposing secrets from private repositories by cleverly hiding its tracks. The attackers created over 13,500 planted branches, printing sensitive data to GitHub Actions logs before erasing evidence.
In a massive token-replay attack campaign, hackers exploited a vulnerability in Microsoft 365 to compromise 97 accounts across 79 organizations, using a clever trick to bypass even multi-factor authentication. By capturing and replaying access tokens, the attackers gained unauthorized access to sensitive data, highlighting a new level of sophistication in cyber threats.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Despite available patches, hackers are actively exploiting PHP2Shell flaws to achieve remote code execution, with recent attacks confirmed through Perplexity's honeypots, showcasing a worrying trend of usable memory disclosure. This allows attackers to execute malicious code and gain unauthorized access, posing a significant threat to vulnerable systems.
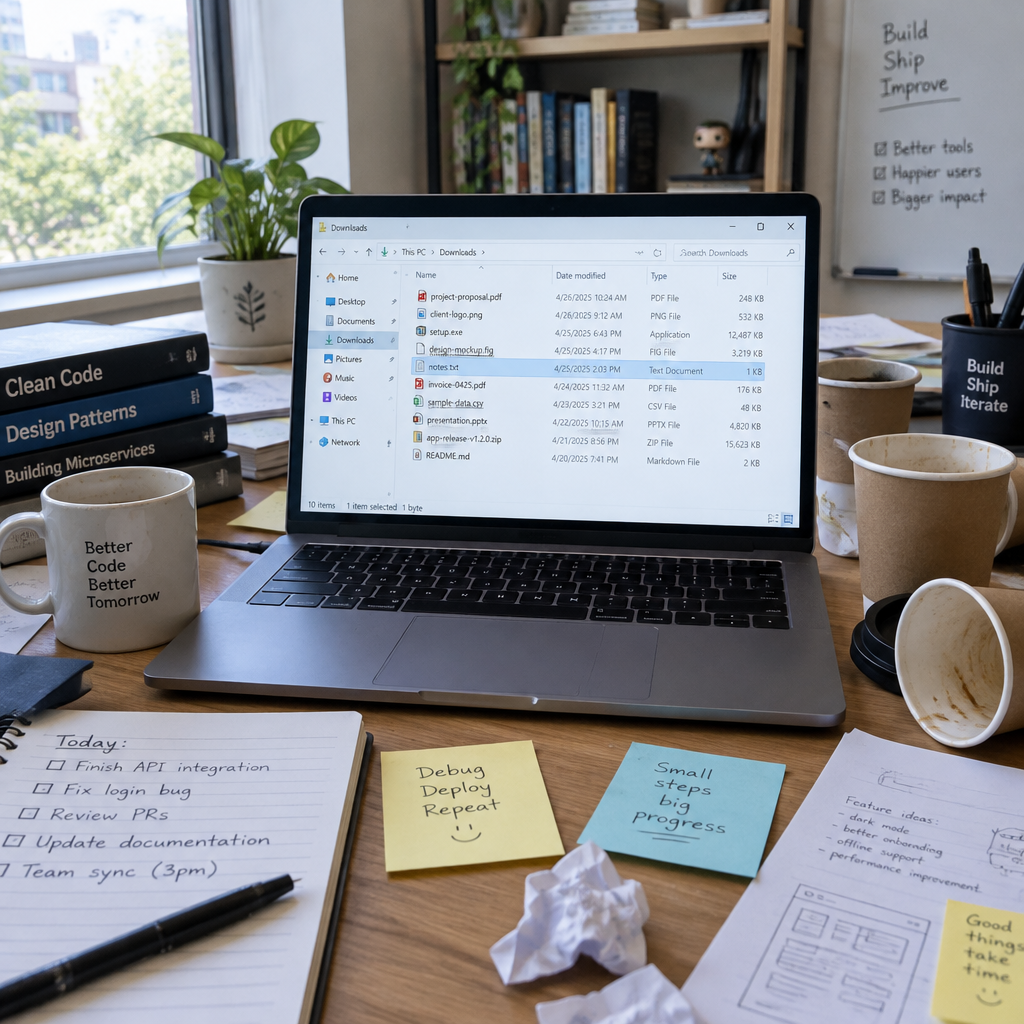
A single stray file in the Downloads folder can unwittingly turn an AI coding agent into an installer, posing a significant security risk - and it's surprisingly easy to happen, with nearly half of Forever Security's customers storing coding agents in this vulnerable location.
In a shocking display of speed, attackers exploited the PHP2Shell flaw to breach a European government entity in just two hours, swiftly swiping password hashes and multi-factor authentication secrets. Palo Alto Networks Unit 42 revealed this alarming rapid escalation, which also involved establishing an NT LAN Manager relay tunnel into Active Directory and attempting Domain Admin privilege escalation.
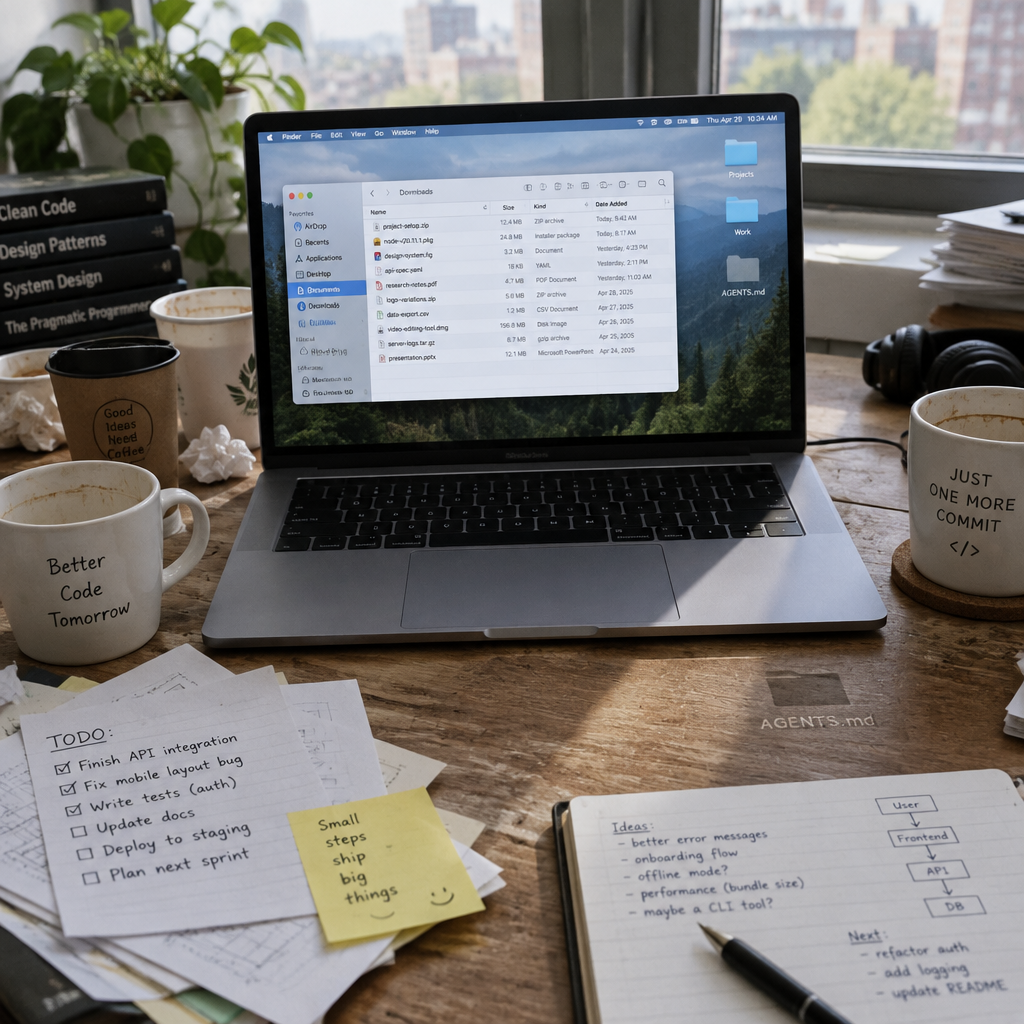
Beware of a sneaky vulnerability in AI coding agents that can be hijacked by malicious markdown files, allowing hackers to secretly download and execute rogue commands on your system. A simple download of a malicious AGENTS.md file into your Downloads folder could put your entire system at risk.
Meet BlackX, a sneaky new UEFI bootkit that's exploiting the Baton Drop flaw to outsmart Secure Boot and install a malicious kernel driver that cripples endpoint defenses. This stealthy threat has already been used in a targeted espionage campaign aimed at diplomatic agencies in Central Asia.
Symantec's Threat Hunter Team caught a sophisticated AI attack agent in the wild, designed to autonomously scan the internet for vulnerable endpoints and exploit them without human intervention. This autonomous tool was built using off-the-shelf jailbreak and exploitation techniques, and could run unattended for up to 100,000 steps.
A careless mistake on May 27, 2026, led to a master key being accidentally exposed in a public repository, putting sensitive data at risk. This tiny error opened the door for an unknown attacker to wreak havoc using the unrevoked key.
CISA has added two critical vulnerabilities to its Known Exploited Vulnerabilities catalog, warning that they're being actively exploited in the wild - and it's crucial to patch them ASAP. Federal agencies have a deadline to apply the fixes by October 26, 2026, to secure their networks.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
Senator Cory Booker warns that Americans are vulnerable to sophisticated online spyware threats, hidden in targeted ads, and urges stronger privacy protections to stay ahead of these evolving surveillance risks. Online ads can now deliver zero-click spyware, making robust cybersecurity measures a pressing need.
Microsoft may have patched the Secure Boot bypass known as Baton Drop, but attackers have found a way to exploit it on systems that haven't applied manual revocation mitigations, thanks to a sneaky new UEFI bootkit called BlackX. This bootkit can persist on patched Windows hosts, putting diplomatic organizations and others at risk.
Meet Phantom, an AI-powered framework that's automating large-scale intrusions with alarming ease, using 18 skill modules to execute complex attacks on vulnerable systems like FortiClient EMS and VPN gateways. This autonomous red team kill chain is being deployed in live operations, making it a formidable tool for ransomware affiliates.
A security breach at Quest Diagnostics has put patient records at risk, with hackers gaining unauthorized access to the company's Quanum LSM system, used by healthcare professionals to manage lab services and access test results. The breach, discovered on October 21, 2026, has exposed sensitive patient information, leaving many to wonder what data was compromised.
Banks are in a high-stakes battle against AI-driven credential abuse, where irresponsible individuals are handing over sensitive banking credentials to AI software, putting customer accounts at risk. To combat this, major US banks are scrambling to distinguish between legitimate customer activity and autonomous agents operating with valid credentials.
A massive data breach has exposed over 70,000 credentials, thanks to a large-scale campaign that targeted vulnerable firewalls and VPN appliances, allowing hackers to steal sensitive information. The culprit behind this cyberattack is a threat actor known as k0t, who's been linked to notorious ransomware groups.
A recent cyber breach at Quest Diagnostics has put patient records at risk, with hackers gaining unauthorized access to the company's Quanum LSM system, used for ordering tests and receiving results. This breach is particularly concerning, as it sits at the intersection of sensitive patient information and everyday lab work.
ESET researchers have uncovered a groundbreaking case of a novel backdoor, MythicRatatoskr, used by Russian hackers in a Ukraine attack, which may indicate a new trend in stealthy cyber threats. This sophisticated backdoor leverages a peer-to-peer network to evade detection.