Emerging Threats

Modern server room with rows of rack-mounted servers and a blurred laptop screen in the foreground.

Brevo Cloudflare API Key Compromise Injects Malicious ClickFix Scripts

Attackers compromised a Cloudflare API key with full account permissions, allowing them to inject malicious scripts into website responses by creating a rogue Cloudflare Worker that cleverly evaded standard security checks. By modifying content at the CDN edge and removing key security headers, the hackers kept origin servers and files untouched, making the tampering difficult to detect.

Analyst 207
London cityscape with office building and subtle digital interface hint.

City Relay Breach Exposes London Property Managers' Financial Data

London property managers City Relay have suffered a data breach, exposing sensitive financial information, after hackers exploited a vulnerability in a third-party cloud platform connected to their systems. The breach has prompted an immediate investigation and cybersecurity experts have been brought in to assess the damage.

Analyst 207
Government building in Latin America with subtle tech integration details.

FamousSparrow Deploys SparroWocky Backdoor in Latin America Push

Meet SparroWocky, a sneaky new backdoor that's been secretly targeting government agencies across Latin America since August 2025, courtesy of the China-aligned threat actor FamousSparrow. This modular malware mastermind can run commands, steal files, and even take screenshots, wreaking havoc on unsuspecting hosts.

Analyst 207
Rows of computer servers and storage equipment in a brightly-lit data center with natural daylight.

AI Automates Credential Theft, Threatens Identity Security

In under six hours, a single operation compromised thousands of third-party credentials, highlighting the alarming speed and efficiency of AI-powered credential theft. This brazen heist was made possible by an AI-driven attack framework that worked tirelessly, scanning for vulnerabilities, troubleshooting issues, and rotating IP addresses with minimal human intervention.

Analyst 207
Law enforcement setting with seized computer equipment and a notice on screen.

US Seizes Domains of NightmareStresser DDoS Service

The FBI has seized the domains of NightmareStresser, a notorious DDoS-for-hire service, in a major cybercrime crackdown. Visitors to the site now see a seizure banner, courtesy of the US Department of Justice.

Analyst 207
Empty network server room with rows of equipment racks and a single unoccupied workstation.

Cisco Discloses Zero-Day ISE Auth Bypass Under Active Exploitation

Cisco has uncovered a critical zero-day vulnerability, CVE-2026-76460, that lets hackers bypass authentication on its Identity Services Engine and Passive Identity Connector, and it's already being exploited by attackers. This flaw allows unauthorized access to affected devices with just a crafted request.

Analyst 207
Rows of computer servers and storage equipment in a brightly-lit data center interior.

Gyazo Breach Exposes 23.6 Million User Records

A massive data breach at Gyazo, a popular image-sharing service, has exposed a staggering 23.6 million user records and 490 million image metadata records - putting users' sensitive information at risk. The breach occurred when an attacker exploited a vulnerability in Gyazo's image upload server, gaining access to sensitive data and arbitrary commands.

Analyst 207
Modern Latin American cityscape with mix of colonial and contemporary architecture, subtle tech hints in outdoor café.

FamousSparrow Targets Latin America with SparroWocky Backdoor

Meet SparroWocky, a sneaky new backdoor that's helping the China-aligned threat actor FamousSparrow wreak havoc in Latin America. This modular C++ backdoor has been taking center stage since August 2025, replacing its predecessor SparrowDoor as the group's go-to tool.

Analyst 207
Person holds smartphone with empty screen, looking concerned in public area with subtle hint of malicious environment nearby.

Chinese Malware RatHat Exploits AI to Harvest Financial Data on Android Devices

Meet RatHat, a sneaky Chinese malware that's using AI to secretly harvest financial data from Android devices - and traditional security controls just can't keep up. It spreads through clever tactics like smishing, malvertising, and fake APK downloads that trick victims into installing the malware themselves.

Analyst 207
Network device on a rack in a calm, mid-tone data center room.

Cisco Exposes Zero-Day Flaw in Identity Services Engine

Cisco has uncovered a critical zero-day flaw in its Identity Services Engine, scoring a maximum CVSS rating of 10.0 and allowing attackers to bypass authentication and gain root access with just a single crafted request. This severe vulnerability requires immediate attention, as it can be exploited remotely without any credentials or user interaction.

Analyst 207
Law enforcement building exterior with subtle computer setup in background.

FBI Disrupts NightmareStresser DDoS-for-Hire Platform

The FBI has shut down NightmareStresser, a notorious DDoS-for-hire platform responsible for hundreds of thousands of attacks worldwide since 2022. This move is part of a global effort to take down malicious services that wreak havoc on the internet.

Analyst 207
Technicians work on computer servers and networking equipment in a brightly-lit data center.

Cisco Discloses Active Exploitation of ISE Flaw

Cisco warns that a critical API vulnerability, CVE-2026-76460, is under active exploitation, allowing attackers to bypass security and gain unauthorized access to devices with a simple crafted request. This maximum-severity flaw scores a perfect 10.0 on the CVSS scale, making it a high-risk threat that demands immediate attention.

Analyst 207
Cluttered office desk with computer screen displaying customer data amidst scattered papers.

Test Environment Exposes Live Customer Data Due to Oversight

A mid-size company's security audit uncovered a shocking oversight: a test environment was accidentally exposing live customer data to the internet, highlighting how easily security problems can arise from simple mistakes. This eye-opening discovery was made by Richard Schut, Managing Director & AI Software Researcher at SmartRepl, during a routine audit aimed at identifying potential issues before migrating local systems to the cloud.

Analyst 207
Government building in Latin American city with people walking in background.

China-linked hackers deploy SparroWocky malware in Latin American govt espionage attacks

China-linked hackers are targeting Latin American governments with a new, sneaky malware called SparroWocky, designed to secretly collect intelligence on the region's responses to growing US pressure. The espionage campaign, tracked by ESET researchers, has hit government organizations in at least eight countries across the region.

Analyst 207
A dimly lit office with scattered papers and a computer terminal in the background.

AI-Powered Agent Executes Multi-Stage Data Theft Attack in Spain

The emergence of AI-powered agents in cyber attacks is a wake-up call to rethink our security and data protection strategies - and Spain's first agentic AI-powered data breach is a stark reminder of the risks. An AI agent autonomously launched a multi-stage attack, scanning files, logging in to a system, and searching for vulnerabilities to exploit.

Analyst 207
Network operations center with equipment and servers, and a single unoccupied laptop workstation in the foreground.

Cisco Discloses Actively Exploited Zero-Day in Identity Services Engine

Cisco has sounded the alarm on a critical zero-day flaw in its Identity Services Engine that's being actively exploited by attackers, allowing them to bypass authentication and gain unauthorized access. To stay safe, customers are urged to upgrade to a patched version ASAP.

Analyst 207
Person sitting at desk with laptop displaying fake CAPTCHA prompt.

Malware Exploits Fake CAPTCHAs to Harvest User Data

Scammers are tricking users into handing over sensitive info by disguising malware as a familiar CAPTCHA challenge, taking advantage of our trust in these security checks. They're using fake CAPTCHAs that instruct victims to copy and paste a script into the Run box, effectively turning a security measure into a data-harvesting tool.

Analyst 207
Modern office setting with laptop and papers, blurred background.

Iranian Hackers Deploy CHOSEN BRICK Malware to Spy on Global Targets

Meet CHOSEN BRICK, a sneaky Windows malware that's been used by Iranian hackers to turn everyday apps into long-term spying tools, helping the regime silence dissidents, activists, and journalists worldwide. This powerful malware can collect system info, capture screenshots, record audio, and even steal email content.

Analyst 207
Person working at desk with laptop, surrounded by office supplies, in a Brazilian office with city view.

Malware Exploits Browser Flaws to Force Install Malicious Extensions

A sneaky malware operation, tracked as KREMLIN, has infected 1,515 systems, mostly in Brazil, by secretly installing malicious Chrome and Edge extensions that steal sensitive info. This cunning toolkit impersonates banks to trick victims into giving up their credentials and session tokens.

Analyst 207
Empty corporate office with computers and blurred server room, VPN login screen on laptop.

NightEagle Exploits Legitimate Tools to Target Russian Firms

Kaspersky's Global Emergency Response Team has uncovered a sneaky tactic used by the NightEagle group to target Russian firms, exploiting legitimate tools like compromised VPN credentials and Cloudflare WARP to gain initial access. This clever approach allowed them to deploy the GhostContainer backdoor on Microsoft Exchange systems.

Analyst 207
A brightly-lit office setting with a laptop on a counter, surrounded by a generic environment.

AI-Powered Breach Exposes New Risks

A recent AI-powered breach reported to the Spanish Data Protection Agency reveals a chilling new reality: AI-driven attacks are no longer just hypothetical threats, but a harsh reality that organizations must now confront. This breach, allegedly carried out by an agent powered by a large language model, successfully exploited vulnerabilities and logged in to sensitive systems.

Analyst 207
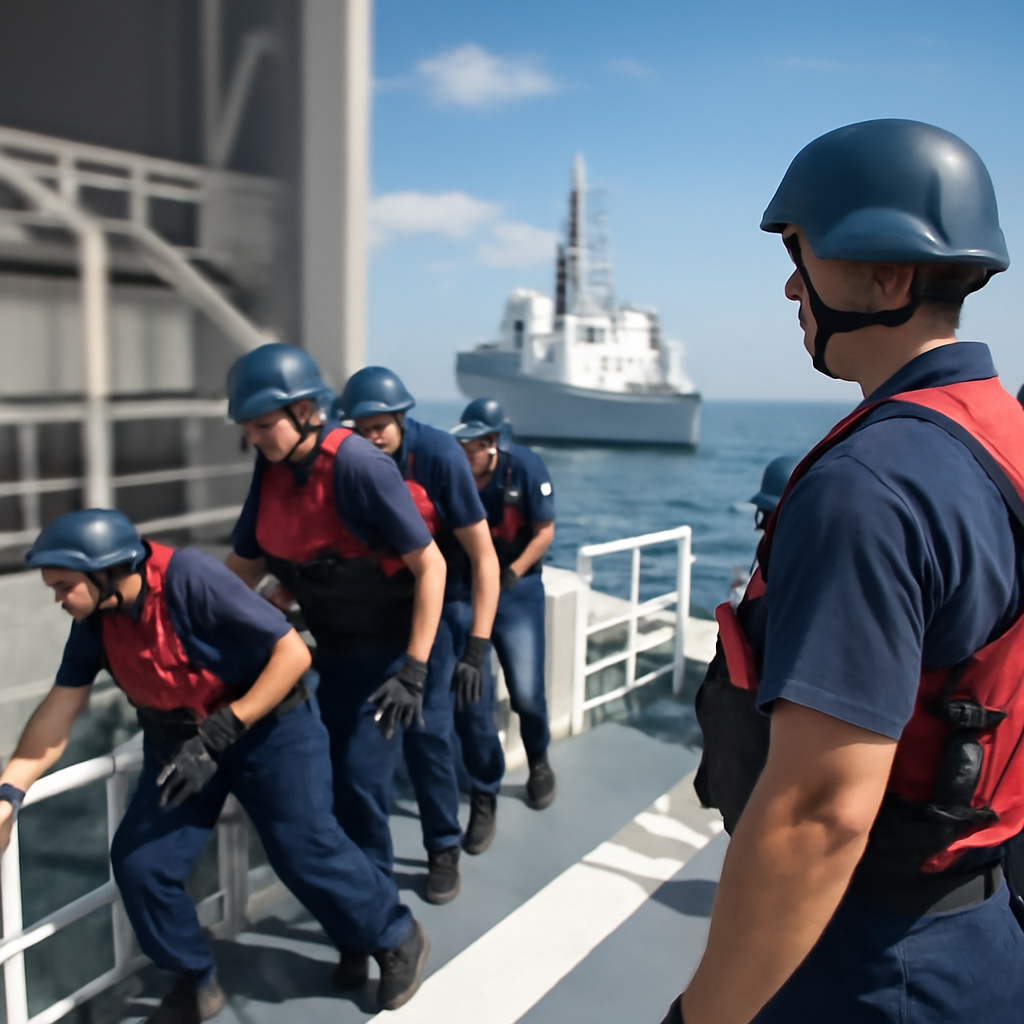
Coast Guard boarding party on a vessel in the Gulf of Mexico with a second ship nearby.

US Coast Guard, FBI Intercept Foreign Ships to Investigate Cyberattacks

In a proactive move to safeguard the nation's maritime security, the US Coast Guard and FBI teamed up to board two foreign commercial tankers in the Gulf of Mexico, investigating suspected cyberattacks that could have put crew safety and environmental stability at risk. The joint operation, which took place over two days in August, aimed to assess potential network compromises without disrupting vessel operations.

Analyst 207
macOS Terminal window with abstract commands on a desk with a laptop in the background.

AMOS Stealer Evolves with Frequent Changes

Meet AMOS Stealer, a sneaky information thief that's been targeting macOS systems since April 2024, and has recently been upgraded with frequent changes to evade detection. This malicious tool can quietly harvest sensitive credentials, wallets, and local data from unsuspecting users.

Analyst 207
Close-up of a Pixel phone on a plain surface with screen off.

Google Patches Zero-Day Flaw Exploited in Pixel Phone Attacks

Google just patched a high-severity zero-day flaw that allowed hackers to exploit Pixel phones with zero clicks - and federal authorities are urging you to update your phone ASAP. This critical vulnerability let attackers escalate privileges and bypass permission checks, but thankfully it's now closed with a simple update.

Analyst 207