[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it alongGeneral cybersecurity news and analysis
Cal.com is ditching open source, citing AI-driven security risks that make transparent code a liability. Its CEO claims open source is dead, as AI tools empower attackers to exploit published code like never before.
Microsoft has heard your frustration loud and clear: the unpredictable rollout of new features in the Windows Insider Program has left many testers feeling confused and left behind. The company is now shaking things up to bring simplicity and reliability back to the program.
The US Cybersecurity and Infrastructure Security Agency (CISA) has flagged four actively exploited vulnerabilities, urging Federal Civilian Executive Branch (FCEB) agencies to patch or discontinue use of affected systems by May 8, 2026. These critical flaws, detailed in CISA's Known Exploited Vulnerabilities (KEV) catalog, pose a significant threat to cybersecurity and must be addressed promptly.

A clever journalist working for Omroep Gelderland successfully tracked a Dutch naval ship for nearly a day using a sneaky hidden Bluetooth tracker sent via postcard - all thanks to publicly available instructions on how to pull off the trick. This eye-opening experiment reveals just how easy it can be to compromise security with a little creativity and some off-the-shelf tech.

TekStream is taking a proactive approach to security with its acquisition of ImagineX's cyber business, expanding its services to help prevent incidents and align security strategies with business goals. This strategic move bolsters TekStream's offerings with advisory, GRC, and vulnerability management capabilities.
As companies rush to adopt AI, a hidden risk is emerging: shadow AI agents operating outside of traditional IT control, leaving many organizations in the dark about where they exist, what they're connected to, and what actions they're taking. This growing visibility gap poses a significant operational risk, driven by teams experimenting with AI independently, often without fully understanding the security implications.
Microsoft is shaking up its Windows Update process to put you in the driver's seat, giving you more control over when updates happen and minimizing those pesky, disruptive restarts. The change comes after hearing from thousands of users, with 7,621 verbatims, about the need for a smoother update experience.
Say goodbye to passwords! Microsoft is bolstering Entra with passkey support on Windows, allowing users to authenticate with a face scan, fingerprint, or PIN for added security and convenience.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
A major Linux flaw, dubbed "Pack2TheRoot," has been hiding in plain sight for 12 years, allowing attackers with local access to gain root permissions and wreak havoc on your system - but a patch has finally been released to squash it. This medium-severity vulnerability, scoring 8.8 out of 10, highlights the importance of staying on top of software updates to protect your Linux setup.
A newly discovered technique allows hackers to easily escalate their privileges to SYSTEM level on Windows systems, using a vulnerability in the Remote Procedure Call stack. This alarming exploit relies on clever manipulation of Security Quality of Service parameters and impersonation levels.
The Linux kernel is set for a major overhaul, with plans to cut support for dozens of outdated devices, including ancient network cards and legacy parallel-port hardware, freeing up thousands of lines of code and reducing the maintenance burden. This could slash nearly 30,000 lines of code, just from Ethernet device removals alone.

The impressive performance of Anthropic's Mythos in automated bug finding, which uncovered 271 Firefox flaws, has been called into question by Ari Herbert-Voss, who argues that open-source models can be just as effective. Herbert-Voss suggests that Mythos's success can be attributed to its ability to detect both simple and complex vulnerabilities, thanks to a phenomenon he terms "supralinear scaling".
Microsoft's latest update aimed at boosting Remote Desktop security may have an unintended consequence: a display-scaling bug that makes crucial security warnings hard to read or even unreadable. This glitch comes at a critical time, as the update was designed to protect against phishing attacks that exploit .rdp files.
To safely deploy AI agents, enterprises must first tighten up governance for the humans, bots, and machine identities that serve as their authority sources, since AI agents aren't independent actors but rather delegated ones. By reframing AI governance as a delegation issue, we can shift the focus from novelty to effective oversight.
As organizations rush to adopt AI, they're reviving long-standing cybersecurity failures, warns Mandiant VP Jurgen Kutscher, who urges a focus on basic security controls over new AI-specific threats. Neglecting these fundamentals leaves AI-enabled environments vulnerable to measurable operational weaknesses.

Microsoft just made it easier for IT admins to breathe a sigh of relief: you can now uninstall Copilot from enterprise devices without any disruptions. The new RemoveMicrosoftCopilotApp policy setting is here to give you more control over your organization's devices.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
A security researcher recently demonstrated how easily electric vehicle chargers can be hacked, leaving cities vulnerable to denial-of-service attacks with just a few clicks. In a stunning Black Hat Asia presentation, he showed how typing a simple charger ID into a custom-built script could instantly render a charging port useless.
Imagine having the power to replicate a full year’s worth of manual penetration testing in just three weeks - that's the reality with frontier AI, which has exposed significant gaps in traditional security programs. Palo Alto Networks and Unit 42 have revealed that advanced models like Anthropic Mythos can autonomously identify software vulnerabilities and adapt to defensive controls in near-real-time.
In a surprising forensic discovery, the FBI was able to extract Signal messages from an iPhone's notification database, even after the app was deleted, by exploiting a loophole that stores message previews on the lock screen. This finding raises significant concerns about iPhone users' message security.
Cloudsmith just secured $72 million to supercharge its artifact management platform and take software supply-chain security to the next level. With a strong artifact management layer in place, companies can enjoy the added benefit of a secure software supply chain.
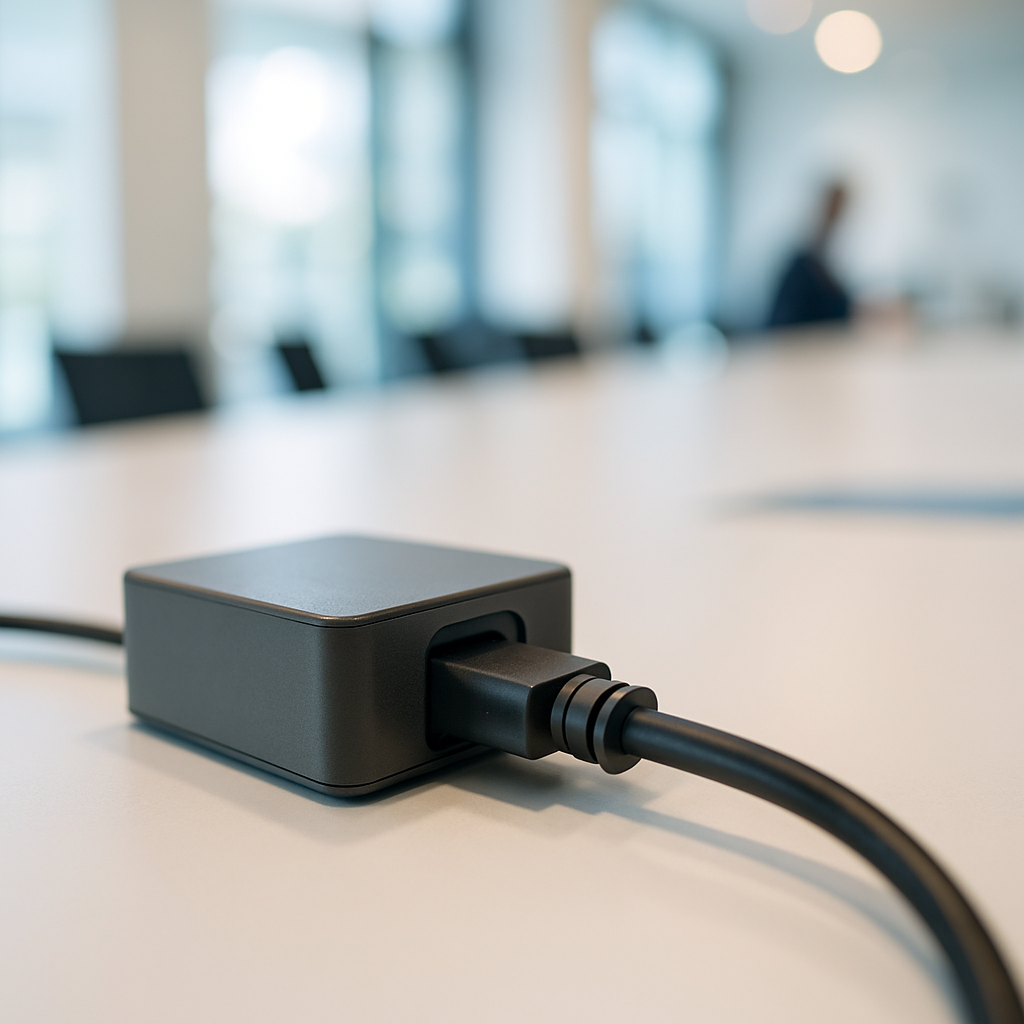
Meet SilentGlass, a game-changing plug-and-play device that easily secures computer monitors from cyber threats, protecting vulnerable IT infrastructure like never before. Developed by the UK's National Cyber Security Centre, this innovative gadget is set to revolutionize desktop security.
Proton CEO Andy Yen warns that mandatory online age checks could spell the end of anonymity, forcing every adult to surrender their ID just to access the internet. He argues that efforts to protect minors will inevitably sweep in adults, creating an ID checkpoint that threatens online freedom.
The recent exposure of Anthropic's Claude Mythos highlights a chilling reality: AI tools designed to improve software quality can be easily repurposed to accelerate vulnerability discovery for malicious ends. This underscores the growing threat of AI-powered attacks, as malicious actors exploit commercial tools with minimal friction.
Did you know that password resets can cost companies a whopping $70 each, and with stolen credentials involved in nearly 45% of breaches, it's clear that corporate security is vulnerable to attack.