Cybersecurity

General cybersecurity news and analysis

UK factory floor with industrial equipment, workers, and integrated computer screens.

UK Manufacturers Lag in Cyber Incident Response Planning

UK manufacturers are leaving themselves exposed, with almost a third having experienced a cyber incident in the past year, resulting in reduced production capacity, operational delays, and supply chain disruptions. The alarming reality is that many factories are flying blind, unable to see and respond to cyber threats.

Analyst 207
Water utility worker stands in front of industrial control systems and computers in a brightly-lit rural office.

DEF CON Bolsters Water Utility Cyber Defenses With AI, Managed Detection

DEF CON and the National Rural Water Association are teaming up to revolutionize cyber defenses for small water utilities, which make up 98% of the nation's water systems, by launching the Water Watch Center, a managed cybersecurity program. This game-changing initiative will bring AI-powered protection and expert support to these vulnerable yet critical organizations.

Analyst 207
Laptop screen displays blurred code on a modern office desk.

AI Agents Expose Enterprises to Growing Prompt Injection Risk

A recent security audit revealed a staggering 36% of AI agent skills contain critical-level security issues, including malware distribution, prompt injection attacks, and exposed secrets. This widespread risk can have serious consequences for enterprises that deploy these skills in their production workflows.

Analyst 207
Empty chair sits in front of blurred courthouse emblem, symbolizing a verdict.

UK Hacker Behind The Com Network Sentenced for Abuse of 117 Victims

Justin Swaddle, a 20-year-old UK man, has been sentenced to two years in prison for terrorizing 117 vulnerable victims worldwide with online abuse, forcing them to perform shocking acts of self-harm and sexual activity for his own twisted online popularity. He must also register as a sex offender.

Analyst 207
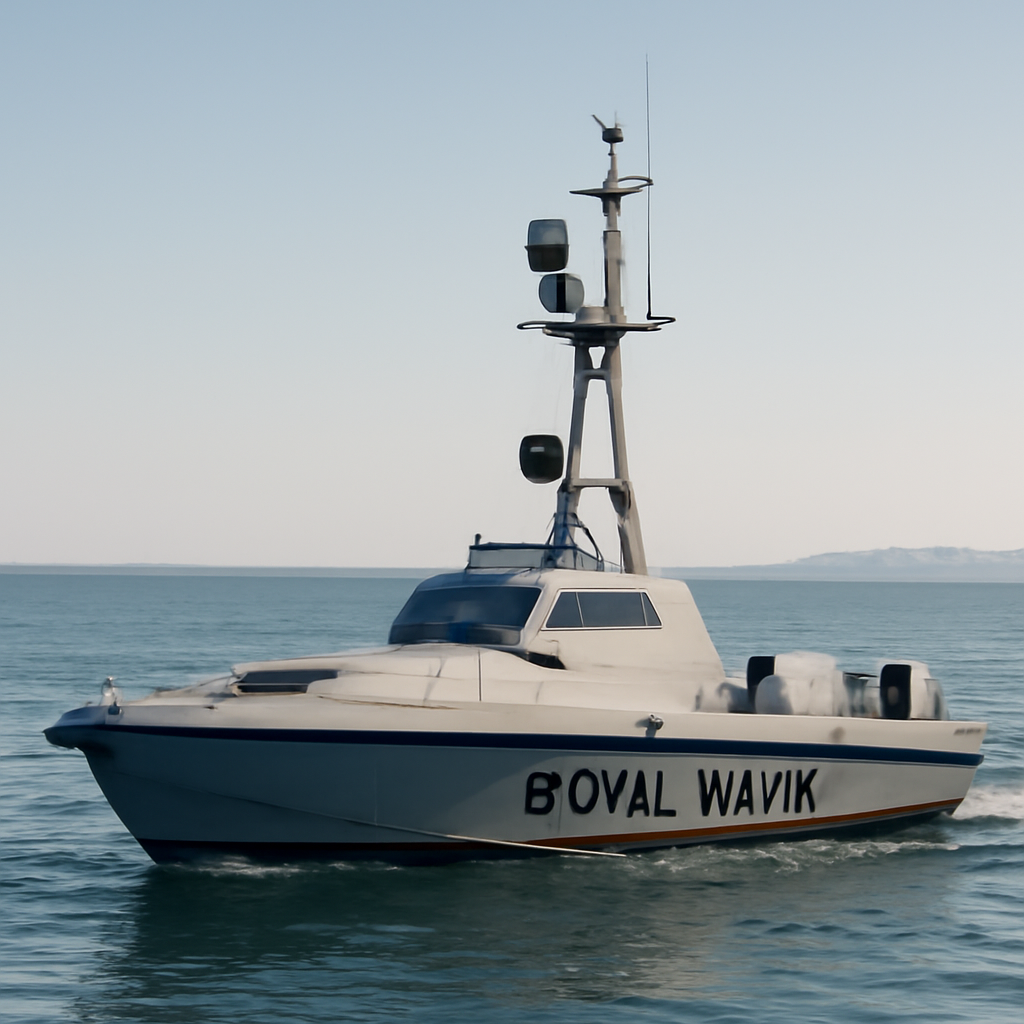
Royal Navy's unmanned surface vessel on calm waters with camera system mounted.

Royal Navy's Drone Boats Expose Cyber Vulnerabilities

The Ministry of Defense swiftly addressed a cyber vulnerability in the Royal Navy's Kraken K3 Scout unmanned surface vessels after a routine check exposed a weakness in the camera system, and promptly cut off internet connectivity to prevent any potential breaches. The MOD assured that its quick action and follow-up investigation found no evidence of data or system compromise.

Analyst 207
Diverse team in conference room with whiteboard and modern technology.

NATO, AI Startup Gain Power to Track Software Vulnerabilities

The cybersecurity landscape just got a major boost: NATO's Cyber Security Centre and AI startup AISLE have joined forces with ENISA to supercharge vulnerability management, bringing the total number of CVE numbering authorities to 20. This powerful collaboration aims to revolutionize the way we track software vulnerabilities and stay one step ahead of cyber threats.

Analyst 207
Blurred laptop screen on cluttered office desk with hand hovering over keyboard.

AI Compresses Identity Attacks, Forces Device Trust Reassessment

Identity security is buckling under the strain of increasingly sophisticated threats, with stolen credentials remaining a top vulnerability - a whopping 44.7% of breaches involve compromised login details. AI is now compressing the time and effort attackers need to launch identity attacks, forcing a urgent reevaluation of device trust.

Analyst 207
Smart glasses sit on a table in a bustling pub interior surrounded by scattered items.

Wetherspoons Targets Smart Glasses Over Covert Surveillance Concerns

Wetherspoons is taking a stand against covert surveillance by asking customers to switch off their smart glasses' cameras, citing concerns over secret filming of patrons and staff. The pub chain is opting for a camera-off approach rather than an outright ban on the wearable tech.

Analyst 207
Royal Navy drone boat on calm waters with clear sky background.

Royal Navy drones transmit data to China in cyber vulnerability test

Royal Navy drones recently raised eyebrows when their cameras started sending signals to a Chinese IP address during a routine cyber vulnerability test, sparking concerns over data security. The Ministry of Defence quickly stepped in to reassure that no sensitive data was compromised, and the transmission was just a harmless "heartbeat" signal.

Analyst 207
Windows laptop with login screen sits next to YubiKey device on a modern desk.

Passkey Defenses Targeted in Novel Attacks

Researchers at Black Hat USA 2026 revealed a shocking vulnerability in passkey defenses, demonstrating how attackers can bypass FIDO2 cryptography and exploit a flaw in Windows Event Logging Service (CVE-2026-34348) to defeat passkey protections. This security gap was found to allow unauthorized users to access and replay sensitive YubiKey signatures.

Analyst 207
Researcher looks concerned while examining laptop screen amidst coding tools and notes.

Researchers Warn of Security Gaps in AI Coding Tools

Researchers analyzed 1.1 million Reddit posts to uncover alarming security gaps in AI coding tools, revealing that developers are frequently complaining about security and privacy lapses. These flaws are leaving the door open for potential threats, putting users at risk.

Analyst 207
Laptop screen displays a webmail interface in a quiet, well-lit setting.

CSS Attacks Break Webmail Defenses to Steal Passwords and Tokens

Researchers have discovered alarming proof-of-concept techniques that allow attackers to exploit styled HTML in emails, breaking through webmail defenses to steal passwords, tokens, and even hijack trusted actions. This vulnerability affects major email services including Outlook, Gmail, and Yahoo Mail, and public proof-of-concept code is readily available.

Analyst 207
Modern office setting with laptop on desk and blurred screen.

Atlassian Rovo Exposes Data Risk Via Prompt Injection Flaw

A critical flaw in Atlassian's Rovo assistant could allow attackers to siphon off sensitive Jira and Confluence data, thanks to a prompt injection vulnerability that two separate security teams were able to exploit. Fortunately, Atlassian has patched one of the two paths used to carry out the attack, but the incident highlights the risks of data exposure via AI-powered tools.

Analyst 207
Modern tech company server room with rows of racks and a laptop screen in foreground.

N-able Bolsters Defenses as Attackers Exploit RMM Flaw

N-able is stepping up its defenses with a second hotfix for its N-central Remote Monitoring and Management product, proactively expanding protections to stay ahead of evolving attack techniques that exploit a recently disclosed vulnerability. This latest update is a must-apply, even if you've already installed the earlier hotfix, as it includes crucial additional hardening measures to safeguard you and your customers.

Analyst 207
Senior officials examine a futuristic server rack in a modern, secure network operations center.

GDIT Secures $1.3 Billion National Guard IT Cybersecurity Contract

General Dynamics Information Technology has landed a $1.3 billion contract to bolster the Army National Guard's IT and cybersecurity defenses, ensuring resilient networks that support communities, government partners, and national security. This major deal, dubbed the Enterprise Network Operations and Cybersecurity Support contract, will safeguard the nation's interests with cutting-edge tech.

Analyst 207
Secure government facility's network operations center with rows of computer servers and cybersecurity equipment.

DoD Accelerates Zero Trust Push Beyond Users, Devices

The Pentagon is making swift strides in implementing Zero Trust principles for its IT systems, focusing on users and devices, and is now poised to take this momentum to the next level. A upcoming webinar will assess progress and explore the future of Zero Trust across the Department of Defense.

Analyst 207
Dimly lit office cubicle with cluttered desk, scattered papers, and slightly ajar file cabinet.

Identity Compromise Fuels 90% of Cyber Incidents

Nearly 9 out of 10 cyber incidents involve identity compromise, with attackers exploiting weaknesses in credentials, multifactor authentication, and social engineering to gain access to enterprise environments. Identity has become the new front door for cyber threats, making it a critical area of focus for protecting your organization's security.

Analyst 207
Control room with industrial equipment and computer screens at a water treatment plant.

Ex-NSA Chief Warns of Water System Cyber Risks

Retired General and ex-NSA chief Paul Nakasone warns that water systems are vulnerable to cyber threats, urging stricter defenses and cautioning that PLCs should be kept offline. He calls for higher standards and new partnerships to protect critical infrastructure.

Analyst 207
Security researcher working at desk with laptop and notes in a well-lit office.

AI-Generated Patches Found Flawed in Testing

Researchers put AI-generated patches to the test and found that ChatGPT and Claude only succeeded in fixing high-impact vulnerabilities about 47% of the time, leaving a significant gap in remediation. This surprisingly low success rate raises important questions about the reliability of AI-generated solutions for critical security flaws.

Analyst 207
Researcher examines laptop screen in university lab setting.

MIT Researchers Expose TONTOU Attack Bypassing Spectre Defenses on Intel, AMD CPUs

MIT researchers have uncovered a clever new attack, dubbed TONTOU, that can bypass Spectre defenses on Intel and AMD CPUs, revealing a practical exploit on AMD Zen 2. This innovative technique, presented at DEF CON 34, challenges current security assumptions and opens up new avenues for exploration.

Analyst 207
Laptop on a minimalist desk displays a blurred login screen in a quiet office setting.

WordPress Fixes Pre-Auth XSS Flaw That Enables PHP Code Execution

WordPress has patched a high-severity flaw that could let attackers inject malicious code into your site - and it's crucial you update ASAP, as 41.2% of all websites are potentially vulnerable.

Analyst 207
Calm server room interior with computer equipment and network gear under fluorescent lighting.

Linux Flaw Exposes Host to Root Access

A critical 18-year-old flaw in Linux's SCTP networking code, dubbed "SCTPhantom," has been discovered, allowing hackers to gain root access to a host; the vulnerability, tracked as CVE-2026-64564, has been present in every Linux kernel released since 2008.

Analyst 207
Small, rustic lemonade stand with scattered leaves and IOU notes nearby.

Open Source Software Faces Reckoning

Open source software had a carefree adolescence, running wild and free for two decades, but its idyllic era is now coming to an abrupt end, forcing it to confront a harsh new reality. It's time for open source to grow up and face the challenges of a rapidly changing world.

Analyst 207
Research setting with laptop displaying code, surrounded by papers and technical instruments.

AI Research Exposes Novel HTTP Desync Techniques and Apache Zero-Day

Meet HTTP Terminator, an AI-powered research system that generated 30,000 candidate desync vectors and helped uncover novel HTTP desynchronization techniques, including an Apache Traffic Server zero-day. This groundbreaking tech scanned 30,000 websites, pushing the boundaries of vulnerability discovery.

Analyst 207