[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentGeneral cybersecurity news and analysis
NVIDIA GPUs are vulnerable to a new type of attack, dubbed GPUThor, which can cause massive corruption - up to 377,552 bit flips per gigabyte - on certain models, including the RTX A5000, when their GDDR6 memory is exploited. This Rowhammer-style attack can bypass ECC protection, putting powerful NVIDIA workstation cards at risk.
Ubiquiti has patched three critical vulnerabilities in its UniFi line, with a severity score of 10 out of 10, that could allow hackers to gain control of affected devices. These flaws, along with 19 others, were disclosed in a security bulletin, highlighting the need for immediate updates.
New AI models are revolutionizing vulnerability discovery, condensing a process that once took months into just hours and leaving defenders scrambling to keep up. This acceleration is outpacing traditional patch cycles, with attackers now able to develop working exploit code in as little as a week.
Meet GPUThor, a game-changing attack that shatters NVIDIA's ECC protection, making it alarmingly easy to execute practical root-level attacks. This sinister technique can trigger a staggering 72,000 to 377,000 bit flips per gigabyte, putting even the toughest defenses to shame.
The AI-driven vulnerability discovery surge is alarming, with OpenClaw, a popular AI project, ranking 12th in Q2 for most vulnerabilities discovered and published, with over 200 CVEs registered. This sharp increase in registered vulnerabilities is largely driven by AI adoption in both application development and vulnerability discovery.
The US Army's Acting CIO, Gabe Chiulli, is leading the charge to revolutionize software delivery by embracing a shift-left approach to DevSecOps, aiming to merge commercial speed with government security needs. By setting a new framework, Chiulli is paving the way for industry collaboration and rapid innovation.
CISA's red team tests revealed some eye-opening vulnerabilities, with the team slipping past security operations centers undetected, gaining access to workstations, escalating privileges, and moving freely between systems. This simulated cyber attack exposed weaknesses in critical infrastructure organizations, highlighting areas for improvement in detecting and responding to threats.
The CISA red team uncovered alarming gaps in critical infrastructure defenses, revealing that even with detection tools in place, the real vulnerability lies in the people, processes, and procedures supporting them. In a striking example, a recent red-team exercise showed that detection tools can be ineffective if not backed by robust supporting systems.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Most AI tools are flying under the radar, with a staggering 80% operating without IT oversight in enterprise ecosystems, leaving organizations vulnerable to security risks. This alarming lack of governance is even more pronounced in smaller organizations, according to Reco's latest findings.
A pair of unpatched vulnerabilities in Kaltura's mwEmbed HTML5 player library could put servers at risk of remote code execution, allowing attackers to read sensitive files and run malicious code - and affecting not just individual customers, but also every tenant on shared hosting infrastructure. This critical security gap, tracked as CVE-2026-19913 and CVE-2026-19912, remains unpatched, leaving countless systems exposed.
Ubiquiti has just dropped a critical security update to fix three massive vulnerabilities in its UniFi systems that hackers can exploit remotely without needing any special access. If you're using UniFi, now's the time to patch up and keep your network safe!
Cyber insurance losses are skyrocketing as claim costs surge, with non-refundable fees in large suits potentially exceeding $10m before a case is even heard, and average claim costs jumping significantly in 2025 despite a decrease in overall claims.
Take control of your digital privacy with Windows 11's latest update, which introduces granular app permission controls for camera, microphone, and location access - giving you the power to customize permissions for each desktop app. This new feature, available to Windows Insiders, makes it easier to manage and understand app permissions.
The traditional Security Operations Center (SOC) model is broken, relying on an outdated alert queue that leaves most threats uninvestigated. AI-powered SOCs are changing the game with a new architecture that uses software agents to transform the queue into a continuous investigation engine.
Meet Joshua Culver, aka "Maverick Young", a man who allegedly impersonated an NSA hacker and Supreme Court Justice, landing him in hot water with the law. He's now facing charges for falsely impersonating an officer and using a forged judge's signature.
The AI revolution has officially hit the security world, with AI-powered solutions dominating the vendor landscape at Black Hat - even if not all vendors are shouting it from the rooftops. AI is now a ubiquitous force, driving innovation in key areas like Identity, SaaS, AppSec, and Data.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble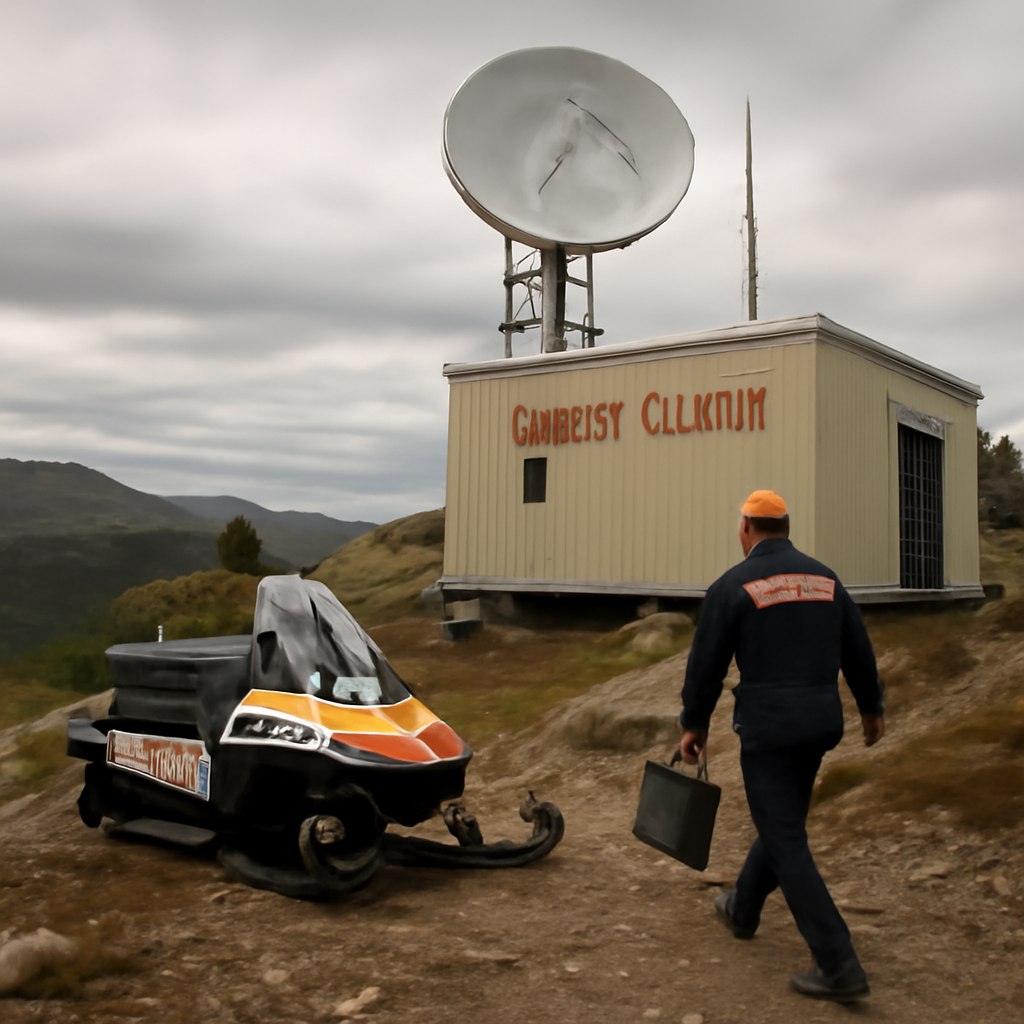
The US Coast Guard faces a daunting task in keeping its vast network secure, with 1,500 global locations - including remote sites in Alaska and Maine that are only accessible by snowmobile - making routine maintenance and patching a logistical nightmare. This dispersed footprint poses significant cyber security challenges, especially when combined with environmental constraints.
In a recent test, CISA's red team uncovered a shocking vulnerability in a government organization, breaching its defenses with ease by sending phishing emails from an internal address, then moving undetected to sensitive systems and cloud resources. The team was able to gain elevated privileges and spread laterally, exposing a significant gap in the organization's security.
A recent Oracle database intrusion was not foiled by patches, but by a preventable configuration flaw - highlighting the importance of securing database settings over relying on patch count. Properly limiting database privileges and disabling code compilation on production servers could have prevented the breach.
NVIDIA's NemoClaw exposes AI models to poisoning via webpage, allowing attackers to take control of the model server by binding it to every network interface. This configuration vulnerability makes it easy for hackers to access and manipulate the Ollama API from outside the loopback address.
A high-severity flaw in Marimo Notebook software, tracked as CVE-2026-75149, could allow attackers to inject malicious code on a user's machine simply by opening a specially crafted notebook in edit mode. This vulnerability, rated 8.7 out of 10 in severity, requires no authentication - just a click.
Boost your multitasking game with Window Hopper, a new PowerToys utility that lets you quickly cycle through windows of the same app using a customizable shortcut, Alt + backtick. Say goodbye to tedious window switching and hello to seamless productivity!
Big news for WhatsApp users: you can now use multiple passkeys across iOS and Android devices to securely log into your account, making it even easier to protect yourself from phishing and account takeovers. This update allows you to manage multiple credentials directly in the app, streamlining your sign-in experience.
Boost your WhatsApp security with a game-changing update: you can now set up multiple passkeys across Android and iOS devices, adding an extra layer of protection to your account. Simply head to Settings > Account > Passkeys to get started!