[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it alongCybersecurity intelligence, threat analysis, and national security reporting.
Researchers revealed Sni5Gect, an open-source toolkit that can silently force 5G phones onto older, less secure networks — and in some cases crash them — exposing users to interception, tracking and service loss. While the release aims to spur fixes, it also risks putting a powerful downgrade tool into the wrong hands unless vendors and regulators act fast.

A new Hook Android Trojan variant now combines banking fraud with ransomware-style lockouts, letting attackers both steal credentials and hold phones hostage. Millions of users should tighten app sources, review permissions, and keep backups as defenders scramble to catch up.

Citrix has released urgent patches for three actively exploited NetScaler flaws, but fixing them often means juggling downtime, complex dependencies, and the worry that attackers may already be inside — update your appliances now, monitor logs, and apply recommended mitigations if you can’t patch immediately.

As global tensions and supply‑chain shocks put chips at the center of national security, SUSHI@NIST is bringing engineers, industry and policy makers together to create measurable standards that make next‑gen hardware verifiably secure. If successful, those standards could turn trust into a testable feature of every device — lowering risk for buyers and raising the bar for attackers.

Researchers warn of a global phishing campaign that uses highly personalized emails and convincing fake sites to slip UpCrypter-wrapped downloads that install remote access trojans, giving attackers persistent control of machines. Stay cautious—verify unexpected requests, avoid untrusted downloads, enable MFA, and keep endpoint defenses tuned to block obfuscated threats.
When the alleged leader of a cross-border crypto theft ring assaulted a witness, jurors added decades to the sentence — a stark reminder that violence to silence witnesses not only invites harsher punishment but also makes tracing and prosecuting digital theft far harder.
Attackers behind the ZipLine campaign are skipping noisy phishing emails and weaponizing corporate “Contact Us” forms to trick procurement staff into running an in-memory, fileless loader called MixShell that evades detection and targets U.S. supply-chain manufacturers. Treat unexpected vendor downloads with skepticism, verify requests through known channels, and beef up memory-level detection—because human trust is now a favorite attack vector.

When a vendor breach exposed personal data for more than 1.1 million Farmers customers, it proved outsourcing can make even trusted brands vulnerable — even if their own systems weren’t hit. This is a wake‑up call for stronger vendor security, smarter contracts, and practical steps customers should take now.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Maryland has confirmed a cyber incident affecting parts of its transportation system, but officials say all scheduled trips this week will be honored while investigators work to determine the scope. Commuters should stay alert for updates as authorities probe the issue and protect essential services.
A new CIISec poll shows most security professionals want tougher, clearer cybersecurity laws—urging policymakers to create practical, enforceable rules that boost defenses without stifling innovation. If lawmakers listen and invest in enforcement and workforce skills, stronger regulation could deliver real protection for businesses and citizens.

When Data I/O took systems offline after a ransomware attack, it showed how a single supplier can ripple delays through entire production lines — a wake-up call for manufacturers to shore up supplier cyber-hygiene, backups, and contingency plans before the next outage.
Got a scary “your phone is infected” pop-up despite downloading from Google Play? A new Zscaler report found over 19 million installs of malware-laden Android apps that slipped past scans via malicious SDKs, repackaging and delayed activation — a reminder to keep apps updated, check permissions, and stay a little skeptical even in official stores.

Could we build a thriving market in orbit where satellites are repaired, parts recycled, and space resources harvested—without turning Earth’s skies into a junkyard? At NIST’s second seminar, engineers, policymakers, and industry leaders pushed the conversation from big ideas to practical standards, incentives, and next steps to make that vision real.
At the DoD’s 4th Annual AI for Defense Summit, experts are turning the question Can you trust a machine with a soldier’s life? into practical solutions—AI-driven triage, predictive maintenance, and smarter logistics that save lives, boost readiness, and keep humans firmly in control.

Think twice before downloading “help” tools from ads—attackers are using convincing fake macOS support sites and malvertising to deliver the Atomic macOS Stealer (AMOS) and quietly scoop up credentials, cookies and crypto wallets. Verify support pages with vendors directly and treat unsolicited downloads like risky strangers offering to fix your device.

Struggling to keep sprawling hybrid IT systems running as change outpaces human monitoring? Forrester’s Wave shows how AIOps—blending machine learning, streaming telemetry, and automation—cuts noise, speeds triage and remediation, and scales operations while flagging real concerns around governance, explainability, and security.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
A trusted developer secretly embedded a “kill switch” into a U.S. company’s systems and has now been sentenced to four years — a stark wake-up call to tighten access controls, code reviews and insider defenses.
If your SIEM only spots one in seven simulated attacks, the Picus Blue Report’s 160M+ simulations are a wake‑up call that gaps in telemetry, brittle rules, and alert fatigue are creating a dangerous illusion of security. The fix is practical: treat detection as continuous measurement—improve instrumentation, run regular attack simulations, and adopt disciplined detection engineering to turn that wake‑up call into measurable improvement.

CISA is revisiting its 2021 SBOM minimums and asking stakeholders for input to strike the right balance between useful, machine-readable inventories that speed vulnerability response and safeguards that prevent sensitive detail from aiding attackers. The update could nudge industry toward interoperable, automatable SBOMs while building practical options for protecting proprietary or security-sensitive information.
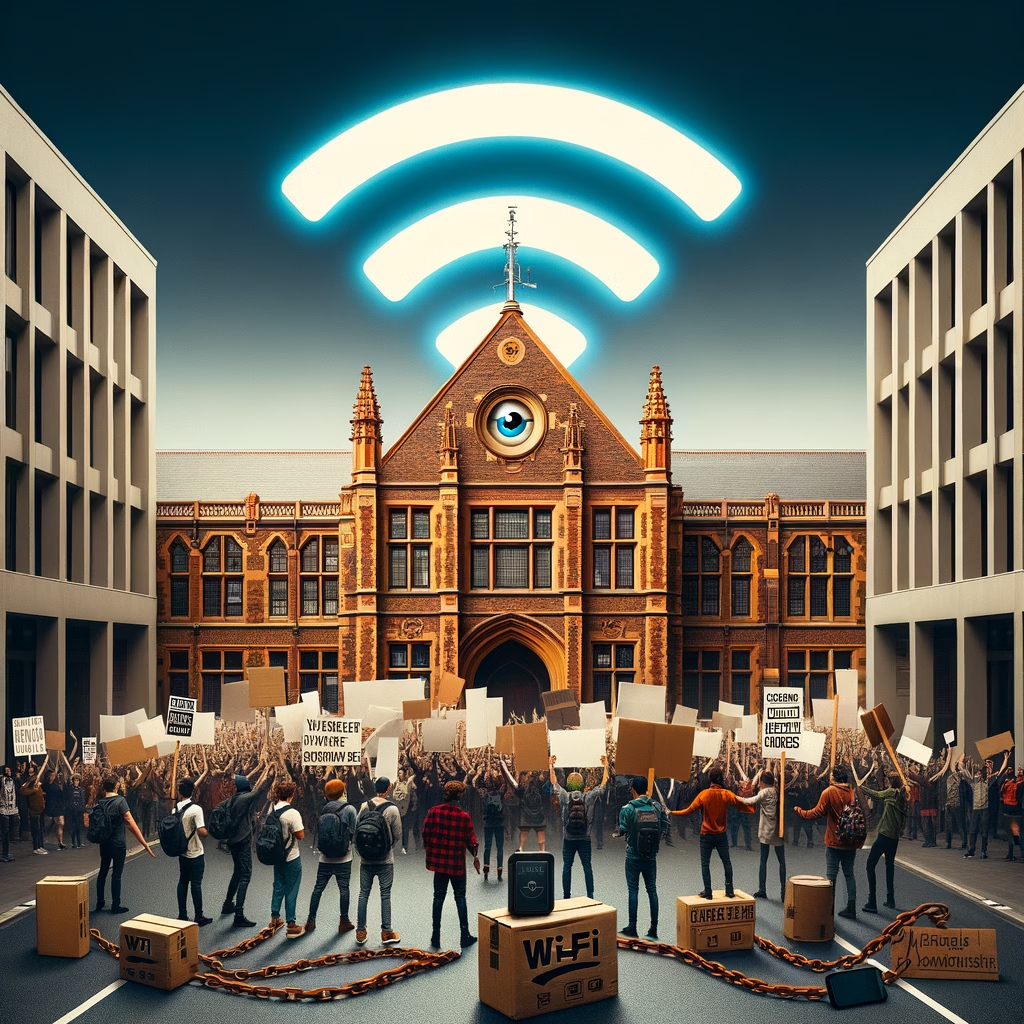
The University of Melbourne reportedly used campus Wi‑Fi logs to identify student protesters, turning everyday network access into a powerful surveillance tool. That episode raises urgent questions about privacy, academic freedom and how universities should balance security with transparent, limited data governance.

When a DDoS bot tied to a rapper’s online persona was unmasked, it wasn’t a darknet mastermind but major cloud platforms that helped federal agents follow the trail—raising urgent questions about privacy, accountability and the growing role of cloud firms as both protectors and informants.

A trojanized Go module posing as an SSH testing tool was found quietly exfiltrating successful login IPs, usernames and passwords to a hard‑coded Telegram bot—proof that convenience in open‑source can hide dangerous supply‑chain risks. Audit and pin dependencies, verify modules, and monitor outbound traffic to stop silent credential leaks before they become breaches.

Bug bounties can be brilliant — they turn curious outsiders into powerful allies who find and help fix real-world flaws before attackers do — but when programs are poorly scoped, underpaid, or legally hostile they breed frustration, public disclosures, and real risk. Get the incentives, triage, and policies right and they strengthen security; get them wrong and the results can be expensive, embarrassing, or downright ridiculous.

Old misconfigs plus a fresh GeoServer RCE (CVE‑2024‑36401) are letting attackers turn exposed GeoServer and Redis instances into botnets, proxy farms, and covert miners—patch now, lock down management interfaces, and assume compromise until you can prove otherwise.