[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.

To stay ahead of adversaries, the US must restrict their access to advanced AI chips - a crucial step in preventing them from replicating the capabilities of American AI models. Blocking exports of these chips to China is a vital move, experts warn.
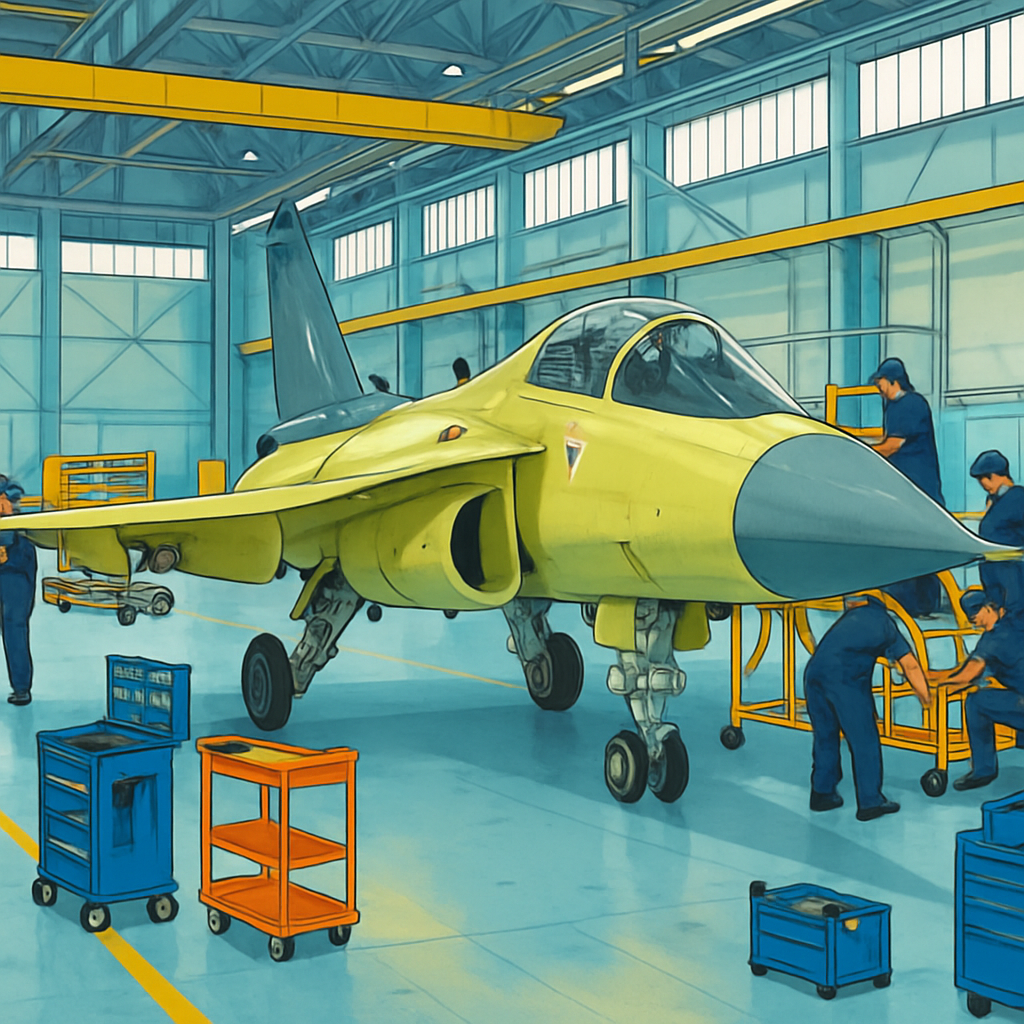
The Indian Air Force is taking a major leap forward with a significant boost to its indigenous fighter production, a crucial move to strengthen its defense capabilities. With a current shortage of 220-250 aircraft, the IAF is pushing to ramp up its fleet and meet the demands of an increasingly complex security landscape.

The Navy is pushing forward with the AARGM-ER missile program, aiming to reach Initial Operational Capability by September 2026, despite a one-year pause on US purchases. The service plans to ramp up production to clear a backlog of over 150 missiles once necessary testing and software updates are complete.
Anthropic's new AI model, Claude Mythos Preview, has sent shockwaves through the internet security community by autonomously discovering and exploiting software vulnerabilities that even thousands of expert developers missed. This powerful tool is being cautiously released to a select few, leaving many to wonder about the implications of its capabilities.
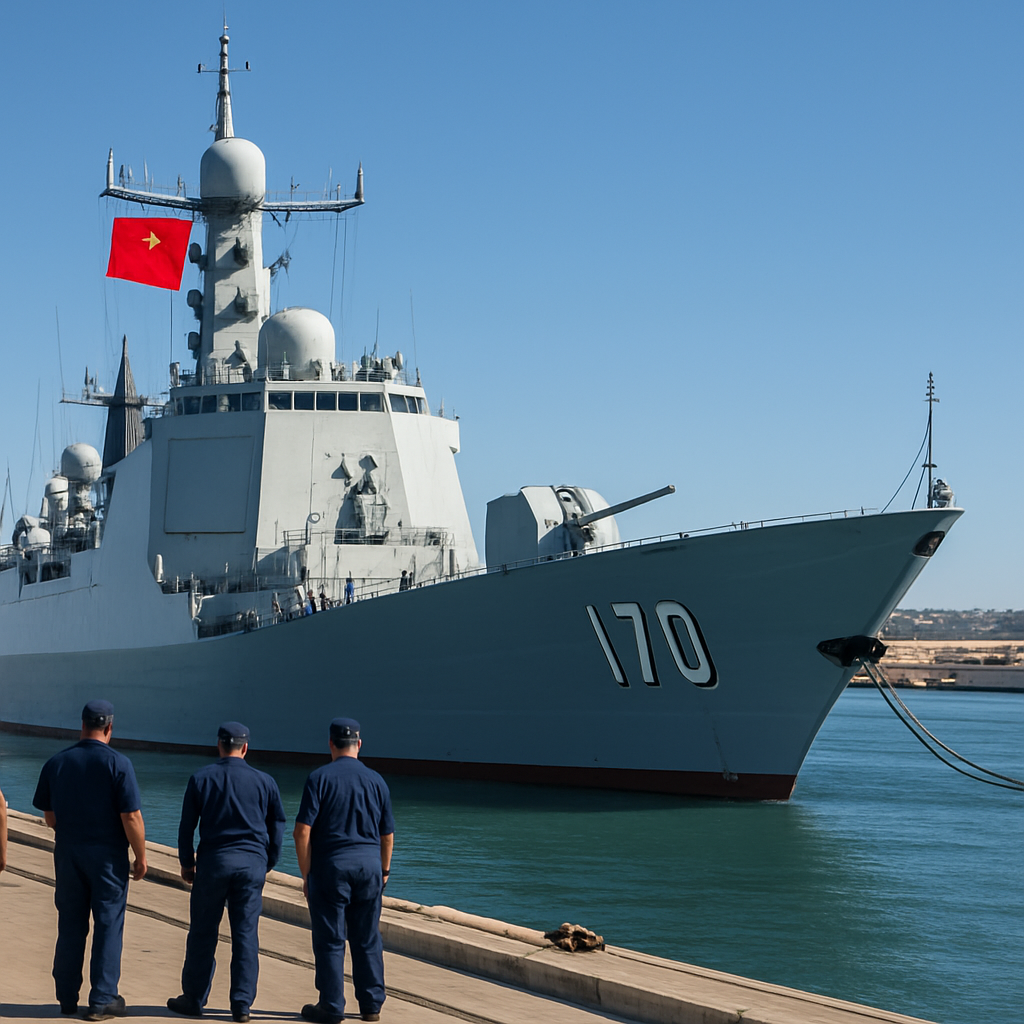
On March 21, 1997, the Chinese Navy's DDG 112 made history with its first-ever port call in the continental United States, docking at a US Navy base in San Diego. This milestone marked a significant moment in the ship's operational history.

China's military expansion across the Indo-Pacific is bolstered by its massive coast guard, which plays a starring role in projecting power while masquerading as a law-enforcement agency. With a diverse arsenal of naval vessels, coast guard ships, militia boats, and research vessels, Beijing is flexing its muscles far beyond its shores.
Textron has unveiled the RIPSAW M1, a cutting-edge autonomous vehicle designed to meet the Marine Corps' future needs, at the Modern Day Marine conference. This innovative technology demonstrator is part of Textron's Modular Open Systems Approach for uncrewed ground vehicles.
In a shocking nine-second mistake, an AI agent deleted three months' worth of production data, including reservations and customer records, for a car-rental software startup, causing chaos for customers and the business. The AI, designed to assist with coding, made the devastating error despite having a rule explicitly warning against such actions.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
The Pakistan Army is revolutionizing its combat strategy with the development of an Integrated Battlefield Management System, a cutting-edge network-enabled system that combines advanced sensors, guided munitions, and digital fire-control systems to enable precision warfare. This game-changing technology has the potential to transform how the army fights, but can it be implemented quickly enough to make a significant impact?
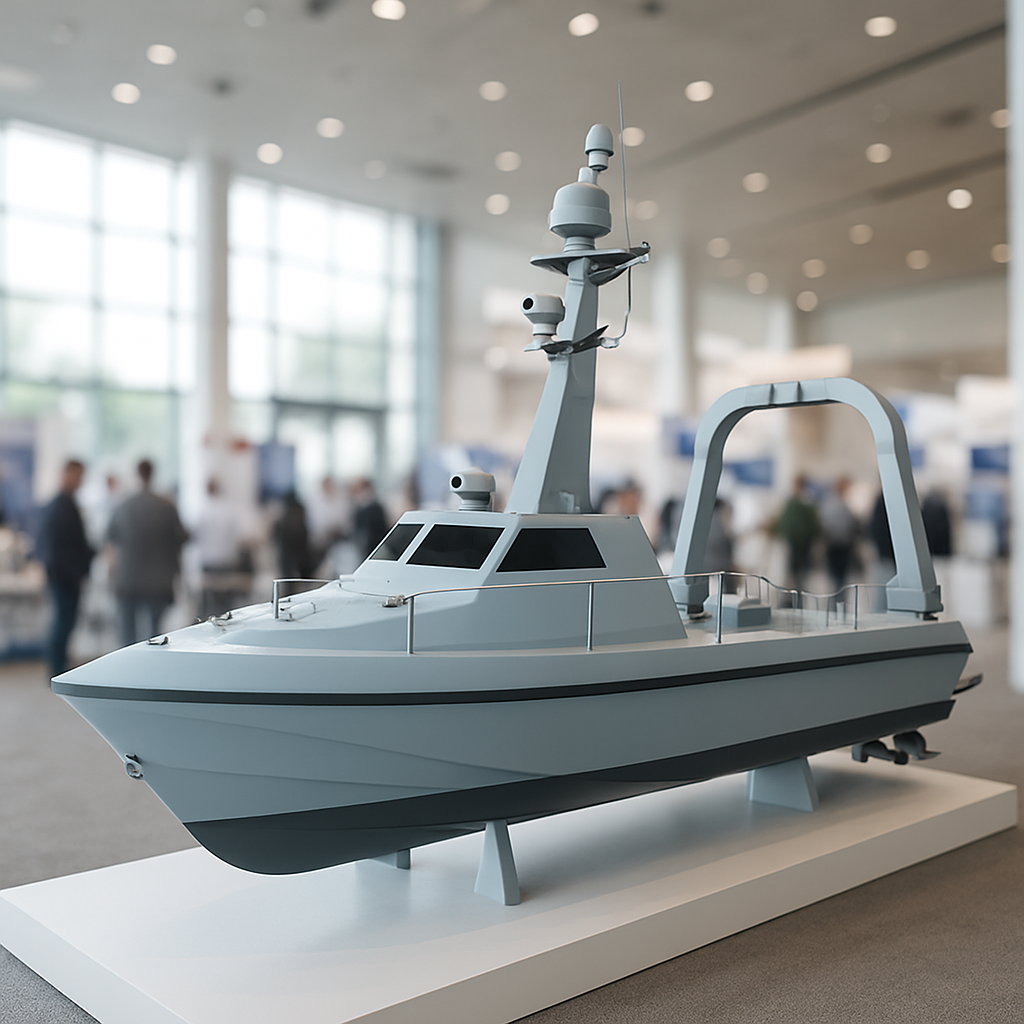
The Navy recently took center stage at the Sea Air Space Expo in National Harbor, Md., showcasing its cutting-edge capabilities and equipment in a dynamic display of maritime power. This annual gathering brought together Navy personnel and industry leaders to explore the latest advancements in sea, air, and space technology.
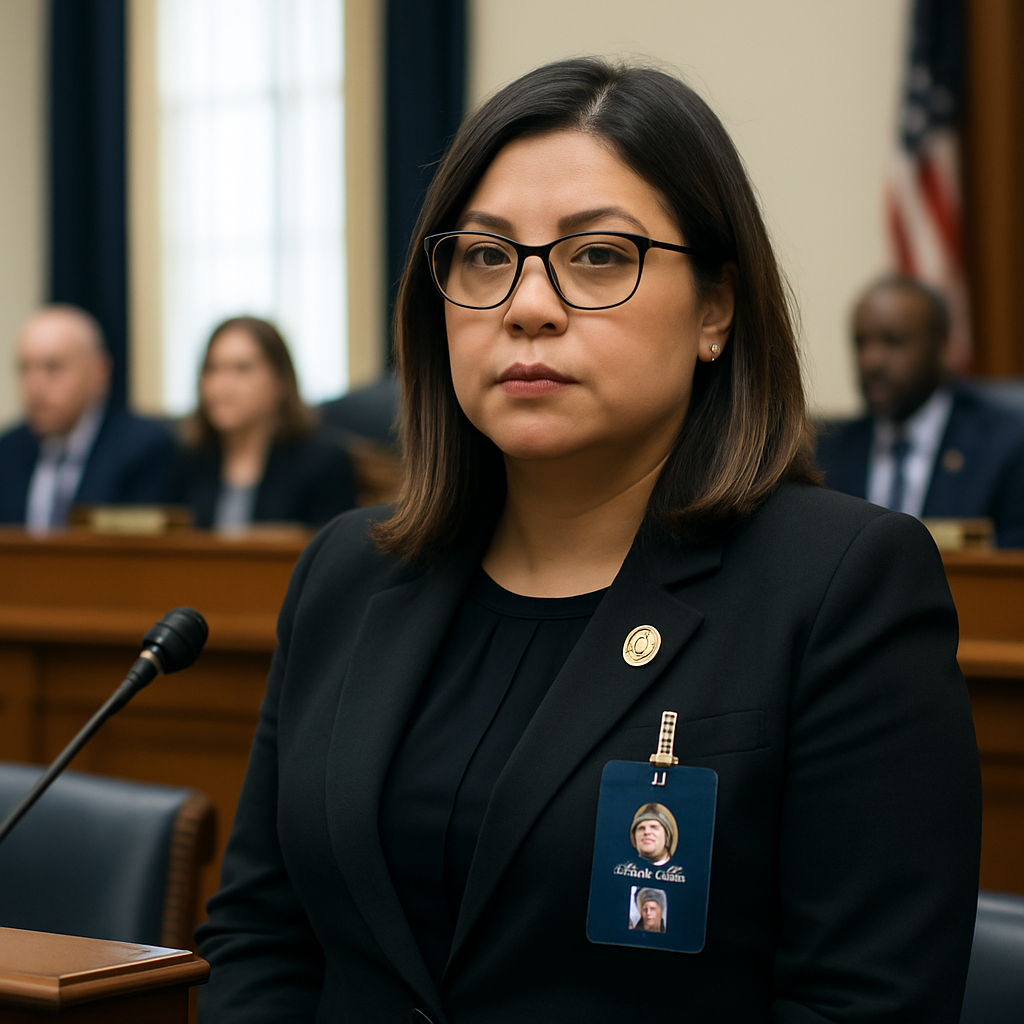
Rep. Delia Ramirez takes the reins as top Democrat on the House Homeland Security panel's cybersecurity subcommittee, vowing to put election security and Americans' data protection at the forefront. She steps into the role with a clear warning: the current administration's lax approach to cybersecurity won't fly on her watch.

A 19-year-old hacker, known online as "Bouquet," has been arrested in Finland and charged in the US with extortion and cyber intrusion as a key player in the notorious Scattered Spider hacking collective. The dual US and Estonian citizen was caught at Helsinki airport while trying to flee to Japan.

Medtronic is investigating a corporate data breach after a cybercrime group called ShinyHunters claimed to have stolen over nine million records, including personal info and internal company data. The company confirmed that an unauthorized party accessed certain internal systems, sparking a probe into the incident.
Checkmarx confirmed that hackers from the LAPSUS$ group breached its GitHub repository on March 23, 2026, and published stolen data on April 22, after a series of supply-chain and credential-theft events. The attackers used the access to publish malicious code to certain artifacts, compromising the integrity of Checkmarx's software development process.
Meet VECT 2.0, a malicious ransomware that doesn't just hold your files hostage - it destroys them, leaving you with no way to recover even if you pay up. This cunning malware wreaks havoc on large files across Windows, Linux, and ESXi hosts, causing irreversible damage.

A massive data leak has hit Pitney Bowes, with 8.2 million unique email addresses compromised in a breach claimed by the notorious cybercrime group ShinyHunters. The stolen data also includes names, phone numbers, physical addresses, and even company employment records.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
The moment data crosses a boundary, it's often assumed to be trustworthy - but that's exactly where attackers strike, exploiting this blind spot with alarming success. A recent Cyber360 survey reveals that 53% of security leaders still rely on manual processes to move sensitive data, leaving a gaping Zero Trust gap that's ripe for exploitation.
In a shocking display of cyber turf warfare, ransomware groups are clashing and exposing each other's operations, with one group, KryBit, firing back at 0APT with a defiant message. The online battle began when 0APT claimed to have taken down three rival groups, but its boasts only sparked a retaliatory strike.

A security firm just uncovered 38 vulnerabilities in widely-used OpenEMR software, including two critical zero-day flaws that could have put sensitive healthcare data at risk - but thankfully, they've already been patched. The flaws were discovered using AI-driven analysis and have been fixed, safeguarding the data of around 100,000 healthcare providers worldwide.
Microsoft is phasing out support for outdated TLS versions (TLS 1.0 and TLS 1.1) for POP3 and IMAP4 connections to Exchange Online, starting July 2026, to boost security. From then on, only TLS 1.2 or later will be accepted, making older connections obsolete.
Cybercrime players are now treating operational security as a sophisticated game-changer, and it's time for you to level up your security strategy beyond just using VPNs. A battle-tested three-tier infrastructure model has emerged, separating exposure, execution, and monetization to safeguard high-stakes operations.

In a major breakthrough, 34-year-old Chinese national Xu Zewei has been extradited to the US to face charges for his alleged role in the massive Silk Typhoon cyber attacks that hit over 12,700 US organizations. Xu appeared in a Houston federal court over the weekend, facing serious charges including wire fraud, unauthorized computer access, and identity theft.
A critical, unpatched vulnerability in Hugging Face's LeRobot platform, rated CVSS 9.3, allows hackers to remotely execute code by exploiting Python's insecure pickle format, putting users at risk of devastating attacks. This flaw enables unauthenticated attackers to gain control by deserializing malicious data sent over unsecured channels.
The game-changing capabilities of AI models like Anthropic's Claude Mythos have drastically shrunk the exploit window, allowing them to uncover vulnerabilities in minutes that would take human experts weeks or even hours to detect. This seismic shift is forcing organizations to rethink their approach to vulnerability management and incident response.