[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it alongCybersecurity intelligence, threat analysis, and national security reporting.

Elon Musk's lawsuit against OpenAI has been dismissed by a jury in Oakland, not due to the validity of his claims, but because it was filed outside the statute of limitations. The verdict marks a significant setback for Musk, who had alleged wrongdoing by OpenAI and its CEO Sam Altman.

Researchers at SentinelOne have uncovered a sneaky new variant of the SHub macOS infostealer, called Reaper, which cleverly bypasses Apple's latest security updates by using a malicious AppleScript to trick users. This crafty malware uses fake installers to lure victims in, making it a serious threat to macOS users.

Employees are quietly embracing AI tools to boost productivity, with 80% using unapproved generative AI applications at work - but only 12% of companies have a formal policy in place to manage this growing trend. This creates a shadow AI gap that leaves organizations vulnerable to security risks.

In a major crackdown on cybercrime, INTERPOL's Operation Ramz has led to 201 arrests and identified 382 more suspects across 13 countries in the Middle East and North Africa. The operation, which ran from October 2025 to February 2026, dealt a significant blow to malicious cyber networks, also seizing 53 servers and helping 3,867 victims.
Malicious actors have unleashed a new wave of chaos with the Shai-Hulud malware, using typosquatting tactics to spread four malicious npm packages that can steal sensitive info and wreak havoc on systems. The packages, published under the account deadcode09284814, masquerade as legitimate tools, but are actually designed to siphon off credentials, cloud configs, and more.

Ransomware attacks have skyrocketed, with over 343 million blocked by Kaspersky products in just the first quarter of 2026 alone, highlighting a surge in threats from the notorious Clop gang and other malicious players. This alarming trend underscores a quarter marked by intensified ransomware activity and rapidly evolving cyber threats.
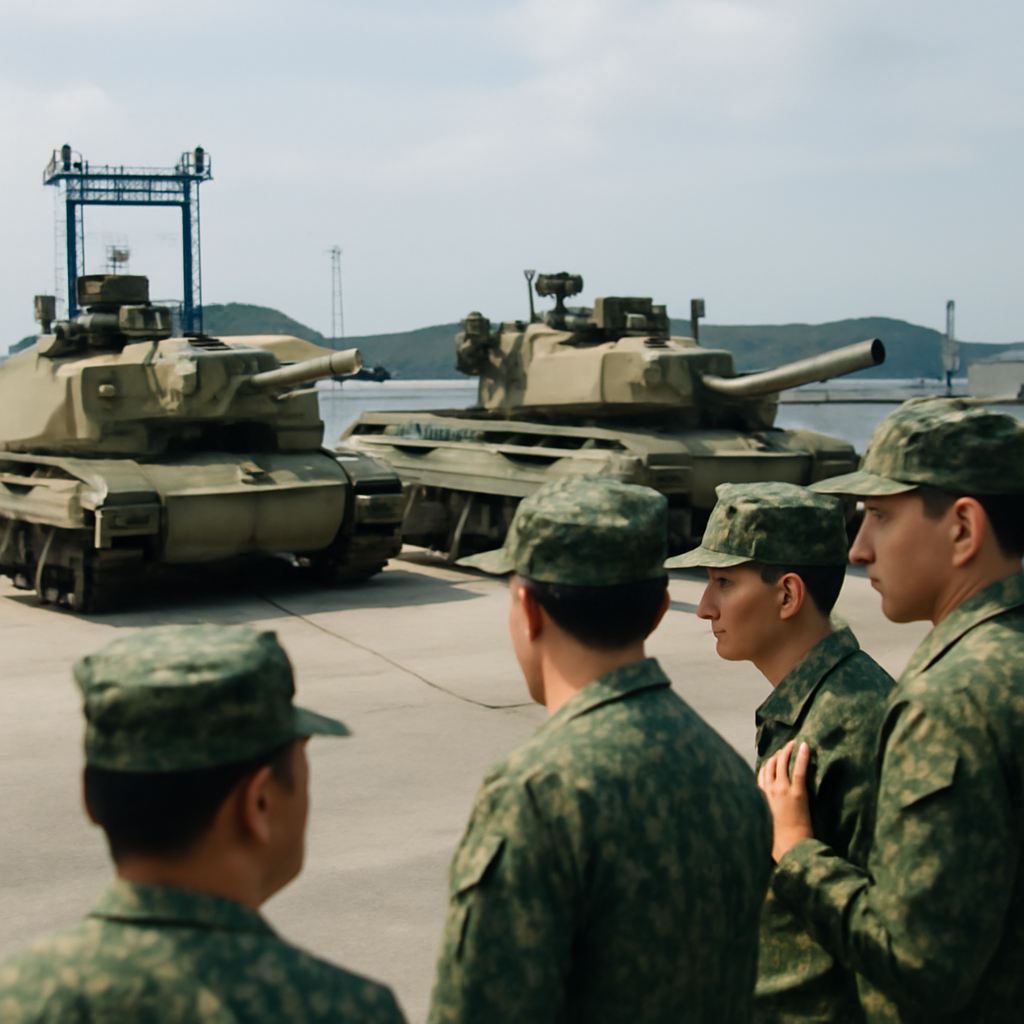
Taiwan's latest shipment of 28 M1A2 Abrams tanks marks a bittersweet milestone, as the island nation grapples with the limitations of its legacy armour in an era dominated by cheap, autonomous strike weapons. The cutting-edge tanks, weighing 74 tons and costing $1.3 billion, now sit alongside a fleet of outdated systems that are rapidly becoming obsolete.
Taiwan's plans to boost its drone capabilities have hit a roadblock after a significant cut to its defense budget, with zero new domestically produced drones set to be procured in 2026. The budget slash, resulting from a Legislative Yuan vote, has stalled the island's ambitious unmanned buildup.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Mobile malware attacks may be on the decline, but banking Trojans are surging, with over 162,000 malicious packages detected in Q1 2026, putting your financial security at risk. Kaspersky's Q1 2026 report reveals a concerning shift in mobile threats, with 306,070 Android malware samples and 439 mobile ransomware Trojans also discovered.
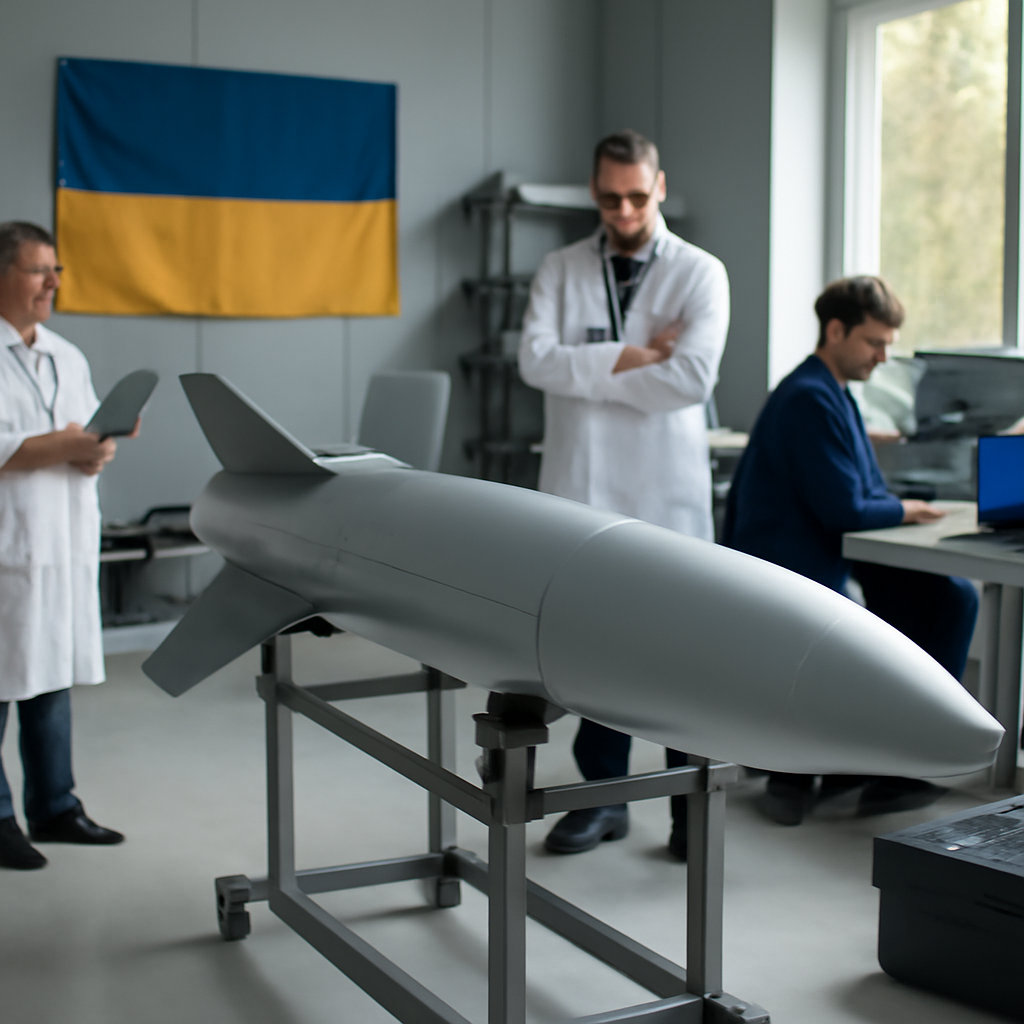
Ukraine just took a major leap in its defense capabilities with the unveiling of its very first homegrown glide bomb, developed in just 17 months and now cleared for combat deployment. The 250-kg warhead-equipped bomb has completed all trials and is set to be deployed imminently, with pilots already rehearsing its use.

In a shocking display of vulnerability, ShinyHunters breached Instructure's Canvas platform not once, but twice in a single week, siphoning off a staggering 3.65 terabytes of data from 275 million users across 8,000 institutions. The brazen attacks left hundreds of schools reeling during final exams, forcing Canvas offline and lining the attackers' pockets with a ransom payment.

The Senate is pushing for a game-changing approach to fighter jet procurement, with a new bill that could pave the way for multiyear buys of F-35 and F-15EX aircraft. This move could help the US military build up its airpower while also saving time and resources.

A ransomware attack on American Lending Center compromised the personal data of 123,000 individuals after a threat actor infiltrated the company's internal network and accessed sensitive files. The breach was discovered nine months prior to notification, on July 27, 2025, but consumers weren't alerted until April 28, 2026.

A critical flaw in the Linux kernel has been discovered, allowing unprivileged users to access files that should be restricted to root accounts, putting system security at risk. This bug puts a spotlight on the importance of kernel access controls for system operators and users who rely on them.

Microsoft has sounded the alarm on a critical vulnerability in on-premise Exchange Servers, known as CVE-2026-42897, that's currently being exploited by hackers - and the company is urging affected users to act fast. A temporary fix is in place, with a permanent patch on the way.

In a groundbreaking move, the MENA region has launched a historic crackdown on cybercrime, resulting in the arrest of 201 individuals in a multi-month operation hailed as a first-of-its-kind success. This major milestone marks a significant victory in the fight against online crime.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
The TanStack project is weighing a drastic measure to protect its code: switching to invitation-only pull requests, after a sneaky Shai-Hulud worm exploited a GitHub Actions misconfiguration to contaminate a shared cache. This supply chain breach has raised red flags about the integrity of downstream code.
Get ready to witness the future of cybersecurity as five innovative startups take the stage at Infosecurity Europe 2026 to pitch their game-changing ideas and compete for a coveted prize package. The event will also feature a dedicated Cyber Startups Zone, where you can discover the latest solutions and meet the minds behind them.

Grafana Labs revealed that hackers breached its GitHub environment using a stolen access token, downloading the company's source code, but fortunately, took swift action to invalidate the token and beef up security measures. The incident is currently under investigation, with more details to be shared once complete.

In a major win against cybercrime, Interpol's Operation Ramz has led to the arrest of 201 individuals and identification of 382 suspects across the Middle East and North Africa. This cross-border crackdown, involving 13 countries, has brought relief to 3,867 victims and dismantled key cybercrime networks.
In just 40 seconds, ANY.RUN's interactive sandbox exposed the full attack chain of a phishing attack, revealing redirects, fake pages, and signs of possible remote access. This game-changing tool helps teams detect phishing threats early, providing concrete evidence of business exposure before it's too late.

Poland is swapping out Signal for a state-developed messaging app touted as more secure, amid rising concerns over targeted social engineering attacks on government officials. The move marks a significant shift in how officials communicate, prioritizing security over popular choice.
Malicious actors are already probing and exploiting a long-standing vulnerability in NGINX web server software, just days after its disclosure - highlighting the urgent need for organizations to update their systems and safeguard against cyber threats. This 18-year-old flaw has quickly become a prime target for attackers seeking unauthorized access to exposed servers.
A critical flaw in Ivanti Xtraction, tracked as CVE-2026-8043, allows remote attackers to read sensitive files and launch client-side attacks - but fortunately, patches are now available to fix this high-risk vulnerability.