[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
The UK's National Cyber Security Centre warns that attackers are using AI to supercharge their cyber offensives, speeding up vulnerability discovery and reconnaissance to alarming levels. In response, the UK has unveiled an AI-powered Cyber Shield to bolster its national defense and stay ahead of the threats.
Adobe has issued a warning to patch a critical flaw, CVE-2026-48282, in ColdFusion versions 2025.9, 2023.20, and earlier, as attackers have already begun exploiting it just two hours after disclosure. Admins are urged to deploy the updates within 72 hours to prevent code execution on unpatched systems.
The US Cybersecurity and Infrastructure Security Agency (CISA) has sounded the alarm on four high-severity vulnerabilities in Adobe, Joomla, and Langflow that are being actively exploited by hackers. Federal agencies have until July 10, 2026, to patch these flaws and avoid potential breaches.
A shocking 15-year-old flaw in the Linux kernel, dubbed GhostLock, allows any logged-in user to gain full root control of a machine in just five seconds - if it hasn't been patched. This vulnerability, which affects most Linux distributions, is a serious wake-up call for developers and users alike.
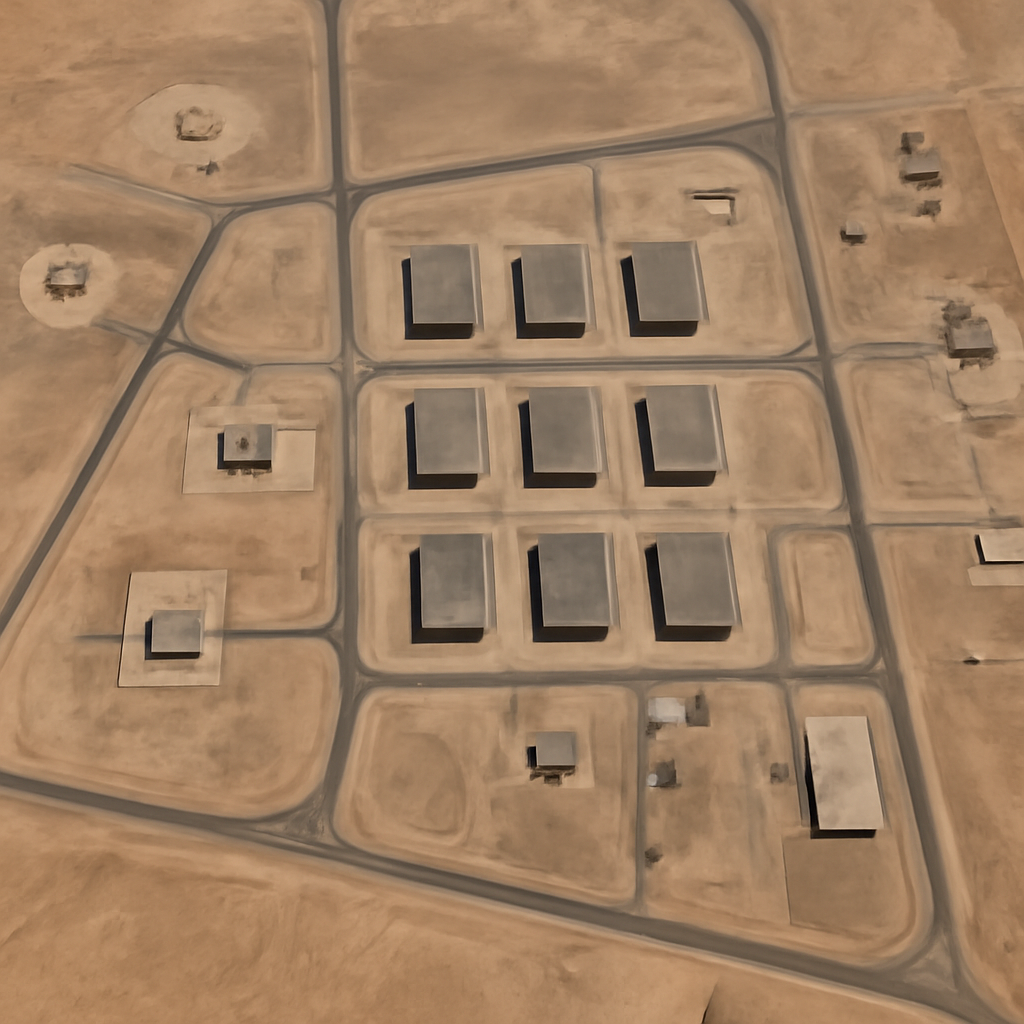
China has built mysterious hardened structures at a missile test base in Inner Mongolia, sparking intrigue over their purpose and capabilities. New satellite images reveal a pattern of rectangular structures with retractable roofs, potentially capable of launching multiple missiles.
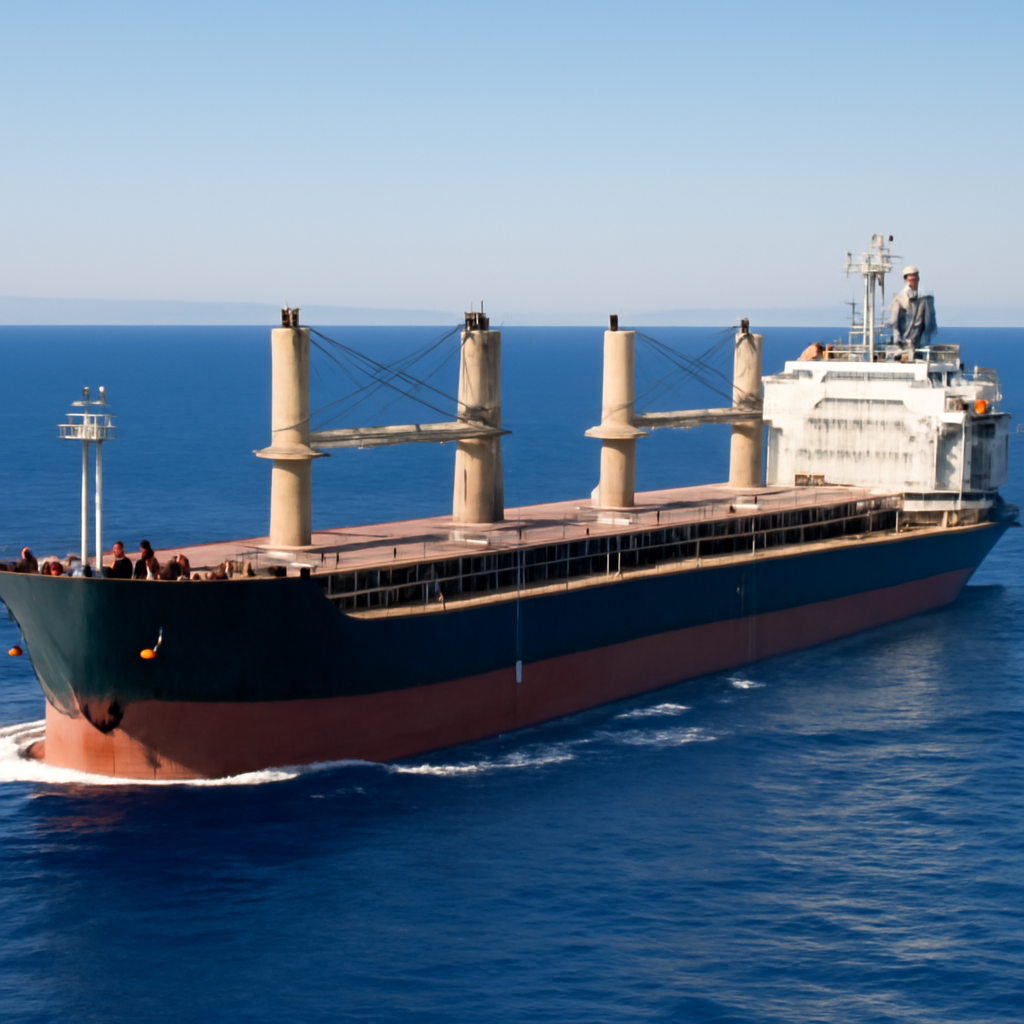
Somali pirates are once again wreaking havoc on shipping routes off the Horn of Africa, with a recent attack on a Palau-flagged bulk carrier in the Red Sea serving as a stark reminder to stay vigilant. Shipowners and operators must remain alert and take precautions to protect their vessels and crews.
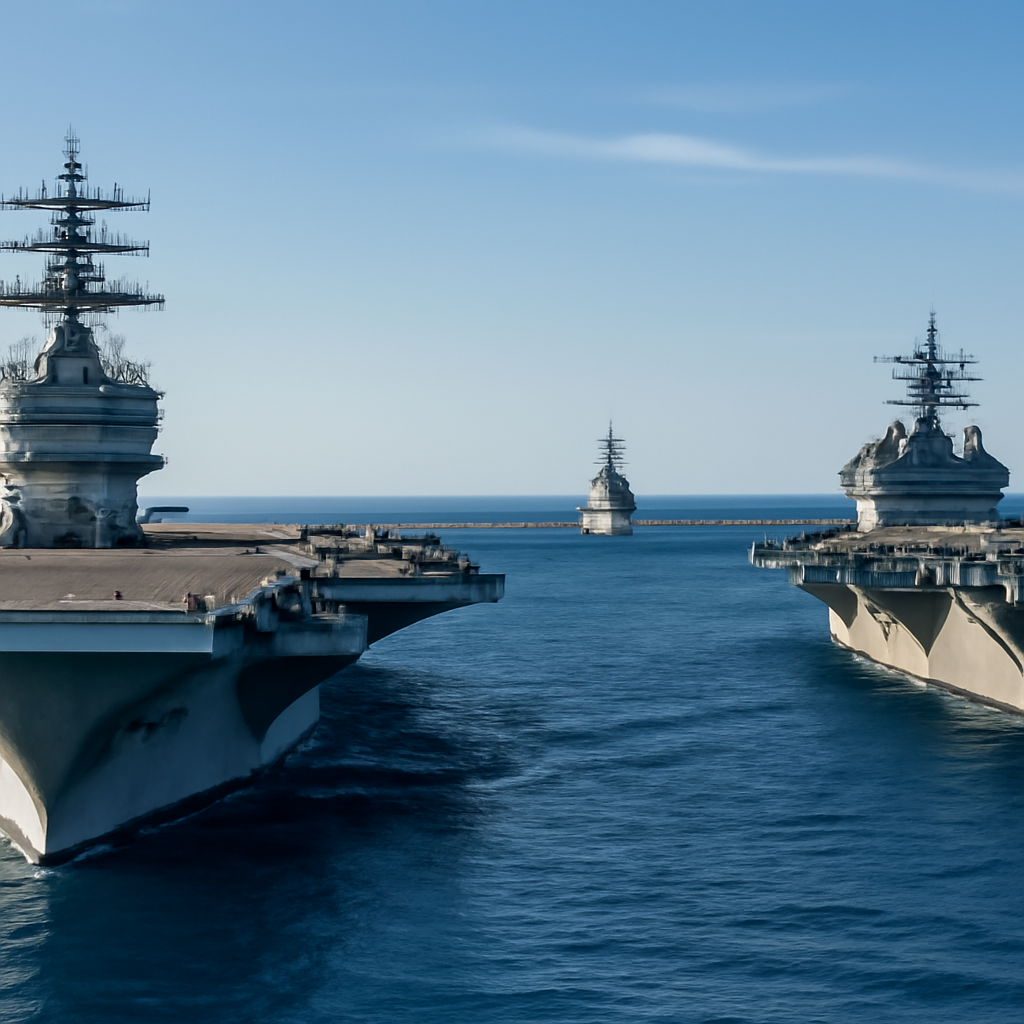
The US has beefed up its naval presence in the Middle East with four major warships on station, including two aircraft carriers, as tensions rise during ongoing Iran talks. This strengthened force posture features the USS Abraham Lincoln, USS George H.W. Bush, and amphibious assault ships USS Tripoli and USS Boxer.
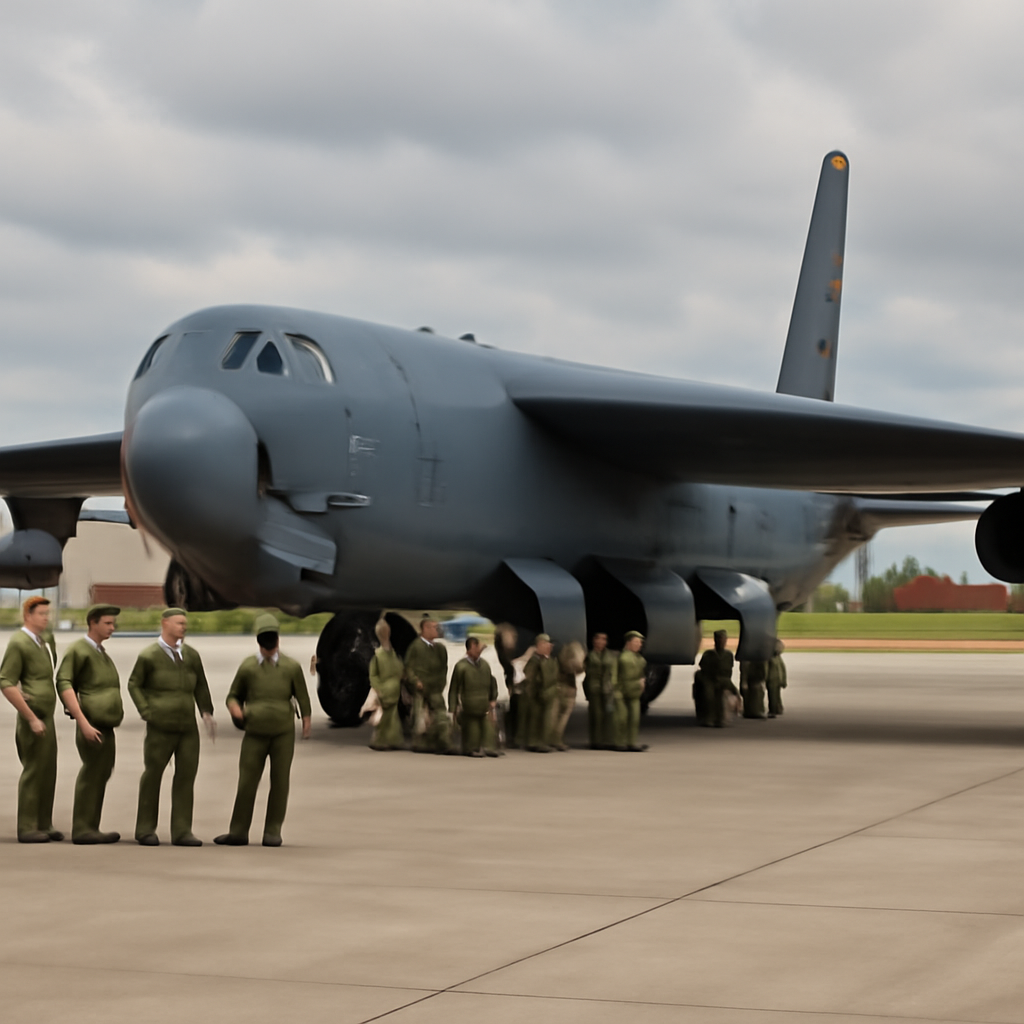
The AGM-181A Long-Range Standoff missile testing has hit a roadblock due to B-52 readiness issues, causing a four-month delay and unfavorable cost and schedule changes. The setbacks have forced the Air Force to push back its initial operational capability target to November 2030.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
A shocking new lawsuit reveals that AI firms are enabling the creation of over 7,000 deepfake images of child abuse, leaving victims feeling humiliated and ashamed. The alarming case has been expanded to include two new anonymous plaintiffs, highlighting the devastating impact of this nonconsensual exploitation.
The Pacific seabed, once a vast and empty space, has become a hotly contested zone as a growing number of nations and interests converge on its valuable resources, transforming the way power and risk are distributed in the region. This emerging crowded landscape is sparking new tensions, as mining, military operations, and other activities increasingly overlap and collide.
Malicious activity on industrial systems has hit a 3-year low, with only 19.6% of ICS computers encountering malicious objects in Q1 2026 - a significant drop of 1.4 times from Q2 2023. However, beneath the calm surface, localized spikes of threats persist, warranting close attention.
In a clever April 2026 campaign, cyber attackers used malvertising to trick victims into downloading seemingly cracked software versions, which actually unleashed the Vidar stealer and XMRig malware via a sneaky loader called Factory-v3. The attackers cleverly hid their malware in password-protected .bin archives to evade detection.
The US has launched a strong retaliatory response against Iran, striking over 80 targets in a bid to hold the country accountable for its attacks on innocent civilians and commercial shipping in international waters. This decisive action aims to impose significant costs on Iran for its aggressive actions.
China's recent submarine-launched ballistic missile test was downplayed by Beijing as a routine annual training exercise, not targeting any specific country. The launch has sparked concerns about China's rapidly expanding nuclear capabilities.
NATO has chosen Saab's cutting-edge GlobalEye aircraft to replace its aging fleet of Airborne Warning and Control Systems, selecting up to 10 of these advanced radar planes over Boeing's E-7 Wedgetail. This game-changing decision marks a significant shift in the alliance's defense strategy.
In a major cybercrime crackdown, Spanish authorities have arrested a suspect linked to a notorious pro-Russian hacktivist group, following a nearly year-long investigation sparked by a tip from the FBI. This breakthrough is a testament to global law enforcement collaboration, with the FBI vowing to continue disrupting cybercriminals worldwide.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
China just took a major leap in its nuclear capabilities, publicly acknowledging the successful test launch of a long-range submarine-launched ballistic missile from a submerged nuclear-powered submarine on July 6. The impressive display of tech validated China's newest missile, the JL-3, and showcased its growing strategic prowess.
The Department of Veterans Affairs sets a shining example with its mission-centered approach to service delivery, and Maximus President and CEO Bruce Caswell believes this mindset should be the standard across all federal contact centers. By modernizing these hubs, government can turn frustrating interactions into enjoyable experiences that better serve citizens and federal employees alike.
Accenture swiftly responded to a data breach, confirming that a security issue was isolated and resolved, with no disruption to their operations or client services. The company remains tight-lipped about the breach's scope and impact, leaving many questions unanswered.
Microsoft's sharp-eyed telemetry has helped track down a suspect linked to the notorious Scattered Spider group, a prolific gang that allegedly raked in over $100 million in ransom payments by infiltrating more than 100 US company networks.
A shocking vulnerability in GitHub's AI-powered Agentic Workflows has been discovered, allowing attackers to expose private repositories with just a cleverly crafted issue and some plain English instructions - no coding skills or credentials required. This flaw lets hackers fetch and publicly share sensitive files, putting organizations at risk.
Chinese hackers known as UAT-7810 are ramping up their game with a powerful new malware called LONGLEASH, designed to infiltrate unpatched internet devices and expand their Operational Relay Box (ORB) network. This upgraded threat is a significant leap from its predecessor, SHORTLEASH, with added capabilities like reverse shell access and advanced proxying.
A security flaw in Google Dialogflow, dubbed "Rogue Agent," allowed hackers to hijack chatbots, but thankfully, a fix was rolled out after Varonis reported the issue through Google's Vulnerability Reward Program. The flaw was cleverly exploited through custom Code Blocks in Dialogflow CX, highlighting the importance of robust security measures in chatbot development.
A new, ready-to-use bank-fraud tool called RedWing is being rented on Telegram, allowing even novice criminals to hijack Android users' phones and steal their banking information. This malicious kit is sold as a complete package, complete with step-by-step guides and how-to videos, making it alarmingly easy for scammers to get started.