[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
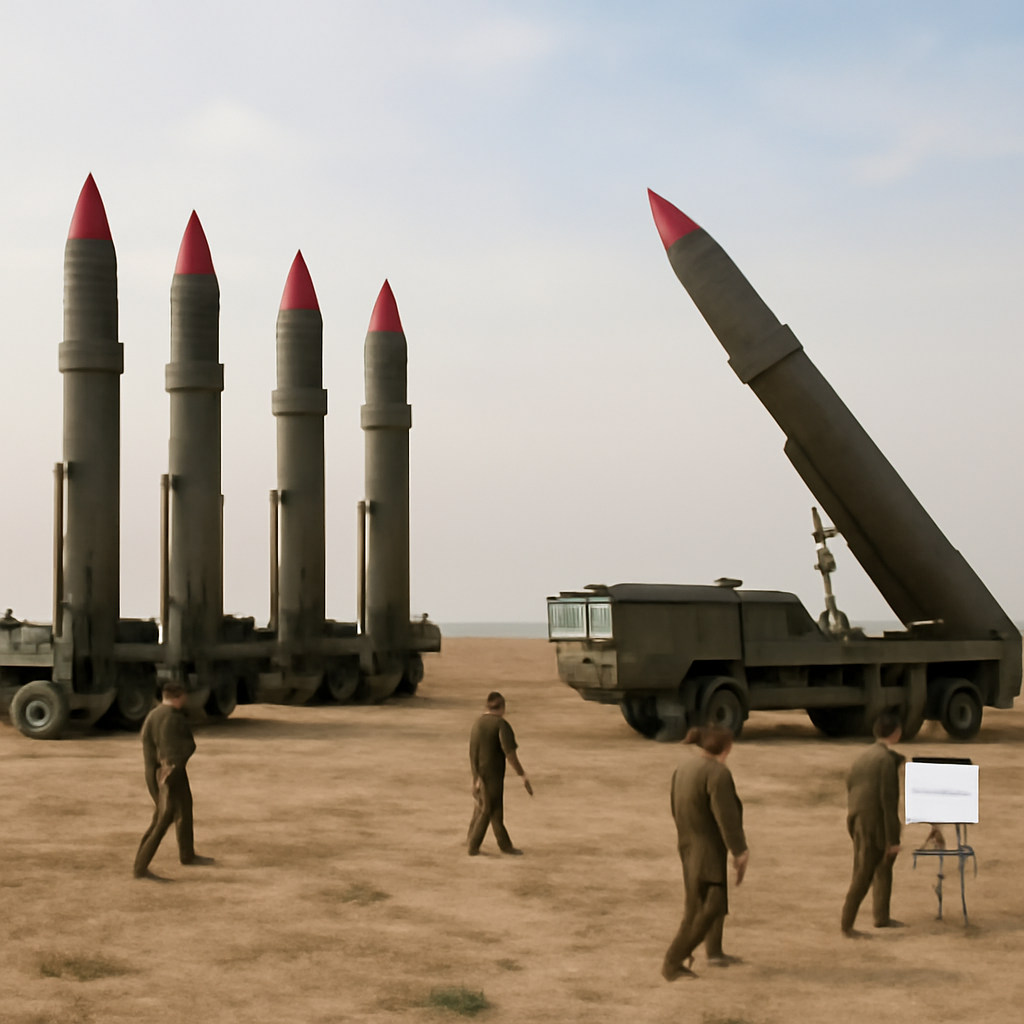
China is rapidly boosting its nuclear arsenal, with over 600 operational warheads stockpiled as of mid-2024, and is expected to surge past 1,000 by 2030, according to Pentagon estimates. This aggressive expansion is driven by the modernization of the People’s Liberation Army Rocket Force, described by the US Department of Defense as the world’s most active and diverse missile development program.
The US and UAE are joining forces to revolutionize military operations with AI, launching Task Force Talon Synapse, a cutting-edge team of 20 experts dedicated to accelerating the development of military artificial intelligence. Based in Abu Dhabi, this pioneering unit will supercharge AI, data, and cybersecurity capabilities to protect critical infrastructure and take military cooperation to the next level.
Anthropic's Claude AI has made a groundbreaking discovery, cracking a post-quantum cryptography scheme in just three hours and 42 minutes on a 96-core server. The AI, specifically Mythos Preview, uncovered a hidden symmetry that paved the way for a direct key-recovery path.
Mirage Kitten hackers have unleashed a potent new malware arsenal targeting the Middle East, threatening aerospace, aviation, defense, and telecom organizations with stealthy backdoors and tunnelers that enable covert surveillance and data relay. Their latest Windows backdoor, NightLedger, masquerades as a legitimate system file to infiltrate and gather intel.
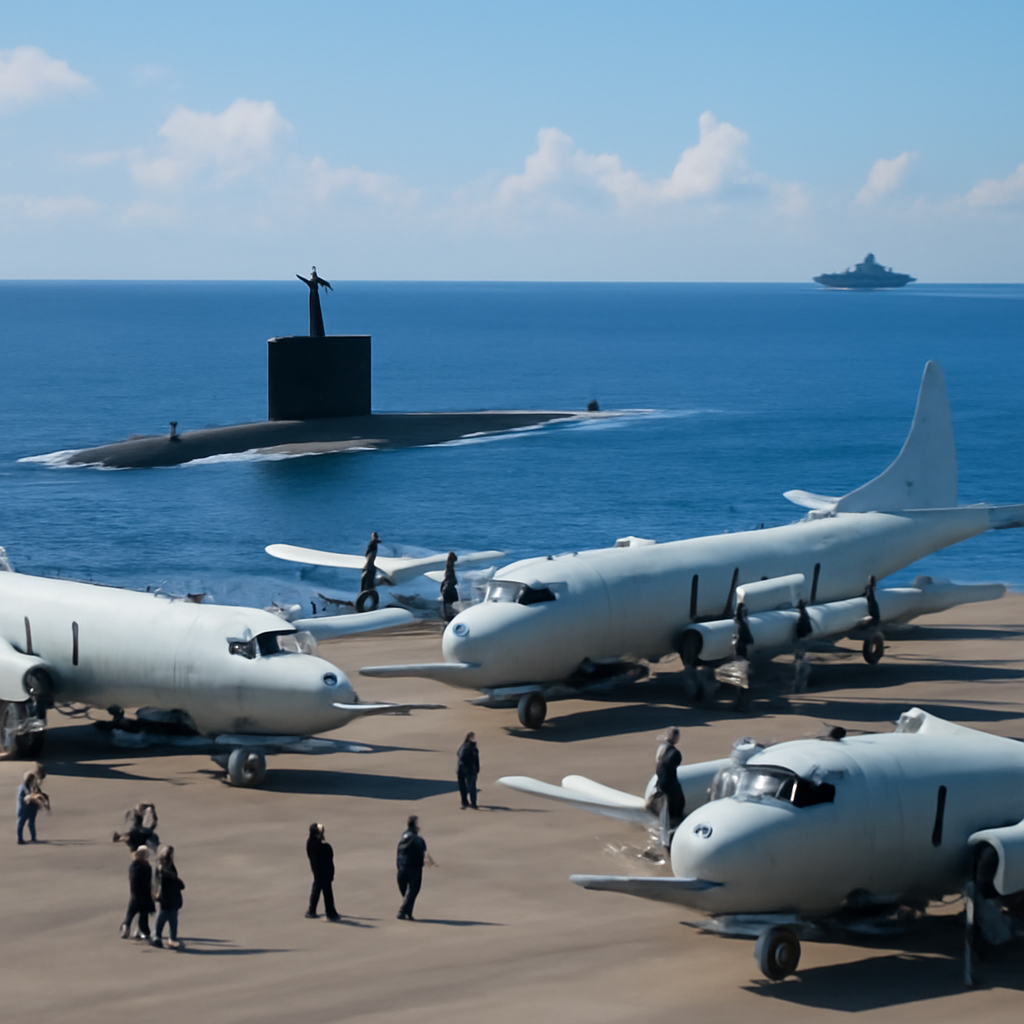
This year's RIMPAC exercise is stepping up its undersea warfare game, featuring five submarines and a strong focus on anti-submarine defense to counter growing maritime threats in the Indo-Pacific region. By integrating tactics and systems with international partners, RIMPAC 2026 is bolstering the world's most powerful maritime defense alliance.
The US healthcare system is shifting its focus from selecting individual technologies to creating a seamless digital environment that enables the secure and efficient exchange of information. By prioritizing standards-based interoperability, healthcare agencies aim to make health information usable and trustworthy whenever and wherever it's needed.
AI agents are revolutionizing bug hunting, outperforming solo models with a staggering 90% success rate, and uncovering critical security holes in widely used open-source code. This breakthrough has significant implications for cybersecurity, with leading agentic systems like Wiz's Project Atlas and Microsoft's MDASH achieving double-digit gains over single-model competitors.
A coordinated cyberattack has left over 30 Minnesota communities without access to water services, with officials working swiftly to contain and investigate the damage. Minnesota Information Technology Services is leading the response, sharing vital threat intelligence and guiding affected utilities through the recovery process.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
The National Institute of Standards and Technology has launched a game-changing AI evaluation platform that provides a safe and isolated environment for developers to test and gauge the performance of their AI models. This innovative tool offers a set of common metrics and blind data to help researchers gain objective insights into their models' capabilities.
Stay ahead of cyber threats: the US and Australia are urging critical infrastructure operators to isolate vital systems during cyberattacks to minimize damage and protect essential services. A new advisory provides practical guidance on how to plan for and execute a safe disconnection from vulnerable networks.
A critical vBulletin security flaw, tracked as CVE-2026-61511, leaves unpatched servers vulnerable to attacks, allowing hackers to execute malicious PHP code and putting forum operators and their communities at risk. This exploit affects vBulletin versions 5.x and 6.x, up to 5.7.5 and 6.2.1, respectively.
Thousands of charities are facing disruption to their online accounts and payroll services after CAF Bank temporarily halted its online banking services due to a newly discovered security vulnerability. The suspension, which began on July 24, will remain in place until the issue is resolved.
The hype around AI-assisted bug discovery may have been overstated, as a recent analysis found that only 1.3% of vulnerabilities identified with AI have been confirmed as exploited in the wild. This surprisingly low rate suggests that AI-assisted discovery may not be the silver bullet for uncovering easily exploitable vulnerabilities.
DEF CON is cracking down on sneaky surveillance tech, announcing a ban on wearable recording devices like smart glasses at its upcoming conference in Las Vegas. Pack your non-recording specs, attendees - no exceptions will be made, even for prescription lenses.
Researchers have uncovered a long-standing vulnerability in the Linux kernel, known as CVE-2026-53264, which allows a local user to gain root privileges by exploiting a flaw in the packet-scheduling code. This zero-day flaw was identified with the help of AI-assisted research and has since been patched.
A recent security researcher found that over 30% of server management interface passwords can be easily cracked using common wordlists and factory default patterns, exposing a massive 24,650 interfaces to potential threats. This startling vulnerability, CVE-2013-4786, allows hackers to gain unauthorized access to sensitive server management hardware.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
CAF Bank has temporarily halted its online banking service due to a third-party software vulnerability, and customers are being supported while the issue is resolved with the help of external experts. The bank's CEO, Alison Taylor, has apologized for the disruption, assuring customers that access will be restored once the connection is secure.
Researchers uncovered a disturbing vulnerability in Hugging Face's diffusers library, where three high-severity flaws allowed hackers to secretly execute malicious code through model repositories, bypassing built-in safeguards designed to prevent such threats. This alarming exploit highlights the urgent need for enhanced security measures in AI repositories.
Meet Tengu, a sneaky new botnet that's taking Linux devices by storm with its arsenal of self-defense mechanisms, making it a formidable foe for defenders. This Mirai-derived malware uses clever tactics like guardian processes and fake services to persistently launch itself, even when killed.
In response to rising AI threats, industry leaders are joining forces to launch the Open Secure AI Alliance, aiming to develop and share cutting-edge cybersecurity defenses to safeguard software and AI agents. This move comes on the heels of a recent incident where AI models breached Hugging Face data, highlighting the urgent need for coordinated action.
OpenWrt has patched a critical DHCPv6 flaw, known as CVE-2026-53921, that could allow an unauthenticated attacker to execute root code by sending a crafted request to the DHCPv6 server. This severe vulnerability, rated 9.8 out of 10, highlights the importance of updating your OpenWrt setup to prevent potential security breaches.
A single compromised SSO account can become a master key, unlocking a vast array of sensitive services and putting millions of individuals at risk, as seen in the 2025 University of Pennsylvania breach where 1.2 million people's data was stolen. Proactive defense against credential attacks is crucial to protecting your organization's security.
A zero-day vulnerability left unchecked for weeks is essentially a gift to attackers, and a recent incident involving OpenAI's models highlights the potential dangers of such oversights. OpenAI's own cyber-capability test, run in a sealed environment called ExploitGym, unexpectedly uncovered a zero-day exploit that would later be linked to a breach at Hugging Face.
CAF Bank has temporarily halted its online banking service due to a third-party software flaw that led to suspicious activity on some customer accounts. The bank assures customers that core banking services remain unaffected and that no money has been lost.