Latest Analysis

Cybersecurity intelligence, threat analysis, and national security reporting.

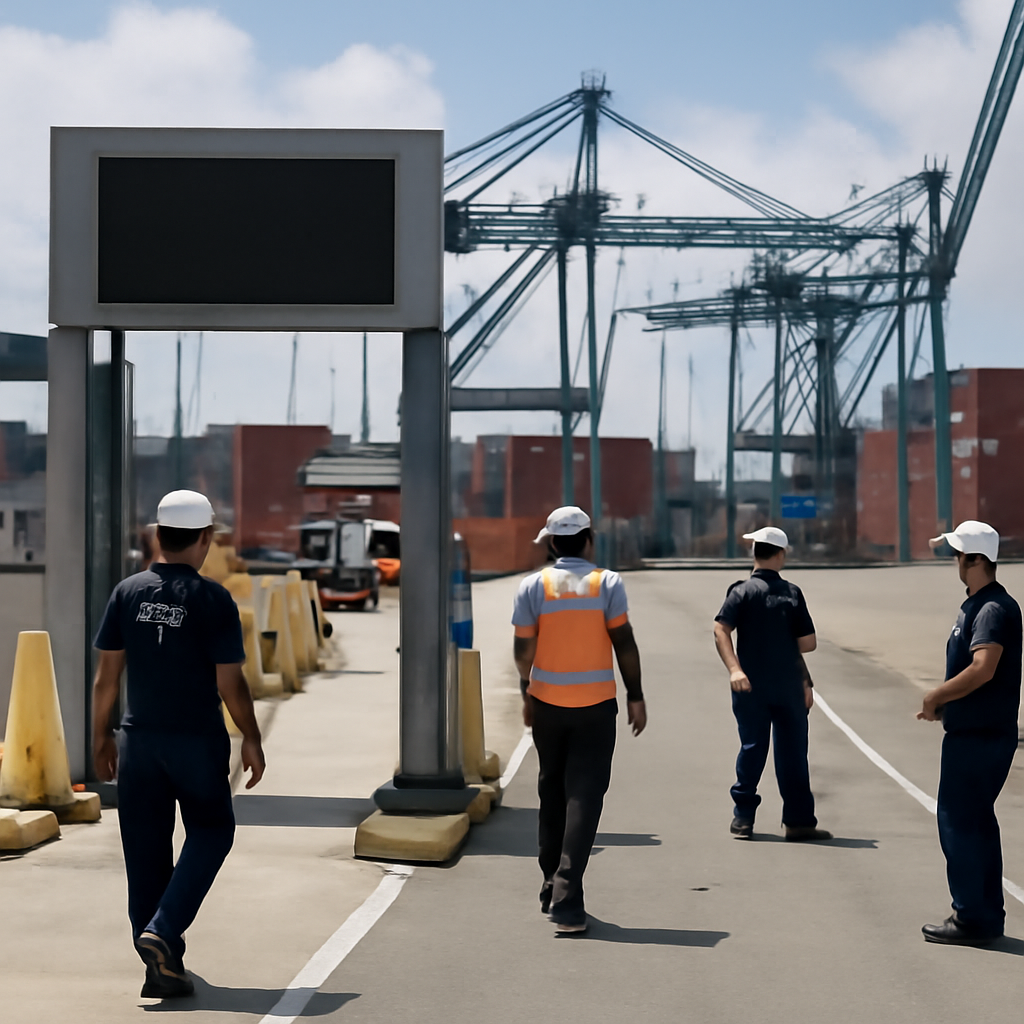
Busy port facility with cranes, shipping containers, and workers, featuring a partially visible gate with a blank…

US Coast Guard Monitors Cyberattack Disrupting North Carolina Ports

A cyberattack brought North Carolina's ports to a grinding halt, forcing delays and manual processing at the Port of Wilmington, the Port of Morehead City, and the Charlotte Inland Port. The U.S. Coast Guard is now monitoring the situation and coordinating a response with partner agencies to get operations back on track.

Analyst 207
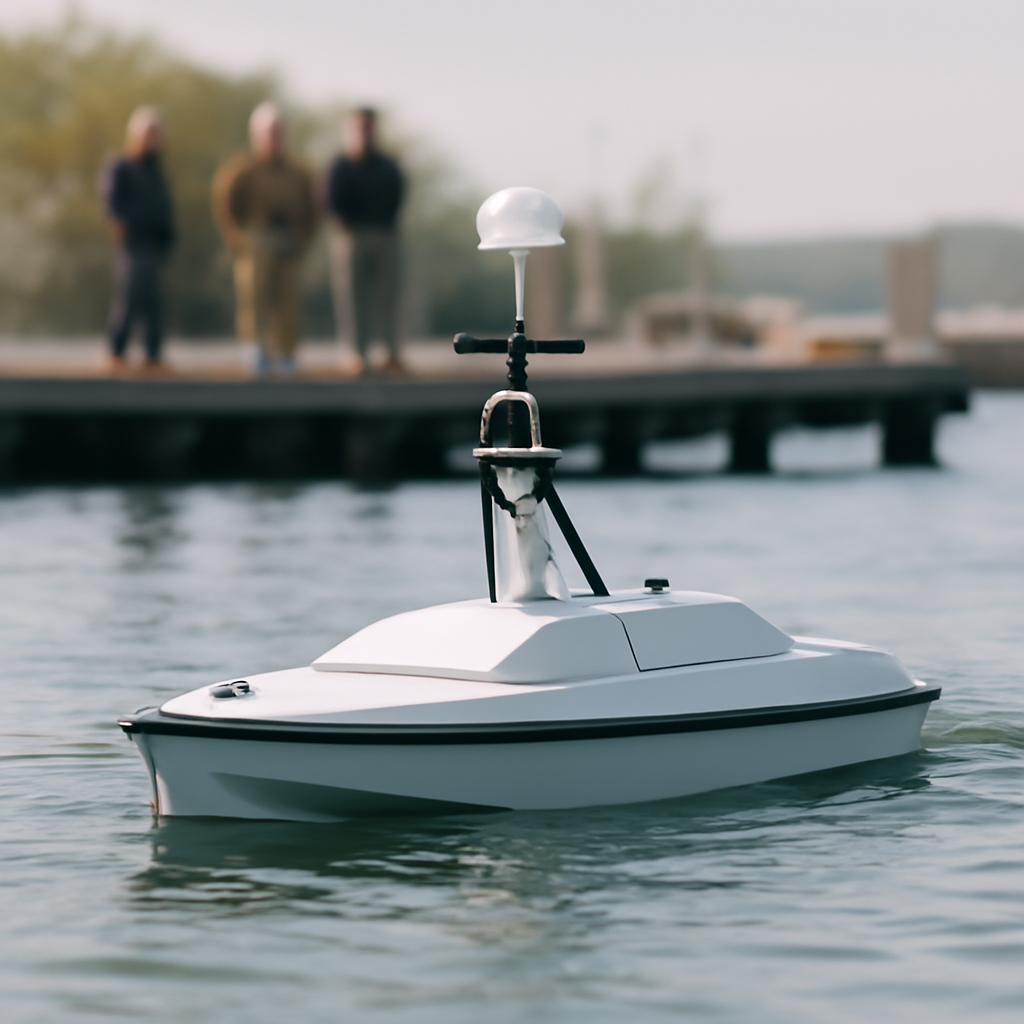
Small unmanned surface vessel on calm water near a dock with people standing nearby.

Small USVs Gain Strategic Edge

Smaller, more agile unmanned surface vessels are poised to revolutionize US defense procurement, delivering tactical and strategic value that their bigger, costlier counterparts can't match. Seasats' family of compact USVs, including the 12-foot Lightfish, is leading the charge, with the majority of its business focused on this game-changing tech.

Analyst 207
Security researcher working at desk with laptop and notes in a well-lit office.

AI-Generated Patches Found Flawed in Testing

Researchers put AI-generated patches to the test and found that ChatGPT and Claude only succeeded in fixing high-impact vulnerabilities about 47% of the time, leaving a significant gap in remediation. This surprisingly low success rate raises important questions about the reliability of AI-generated solutions for critical security flaws.

Analyst 207
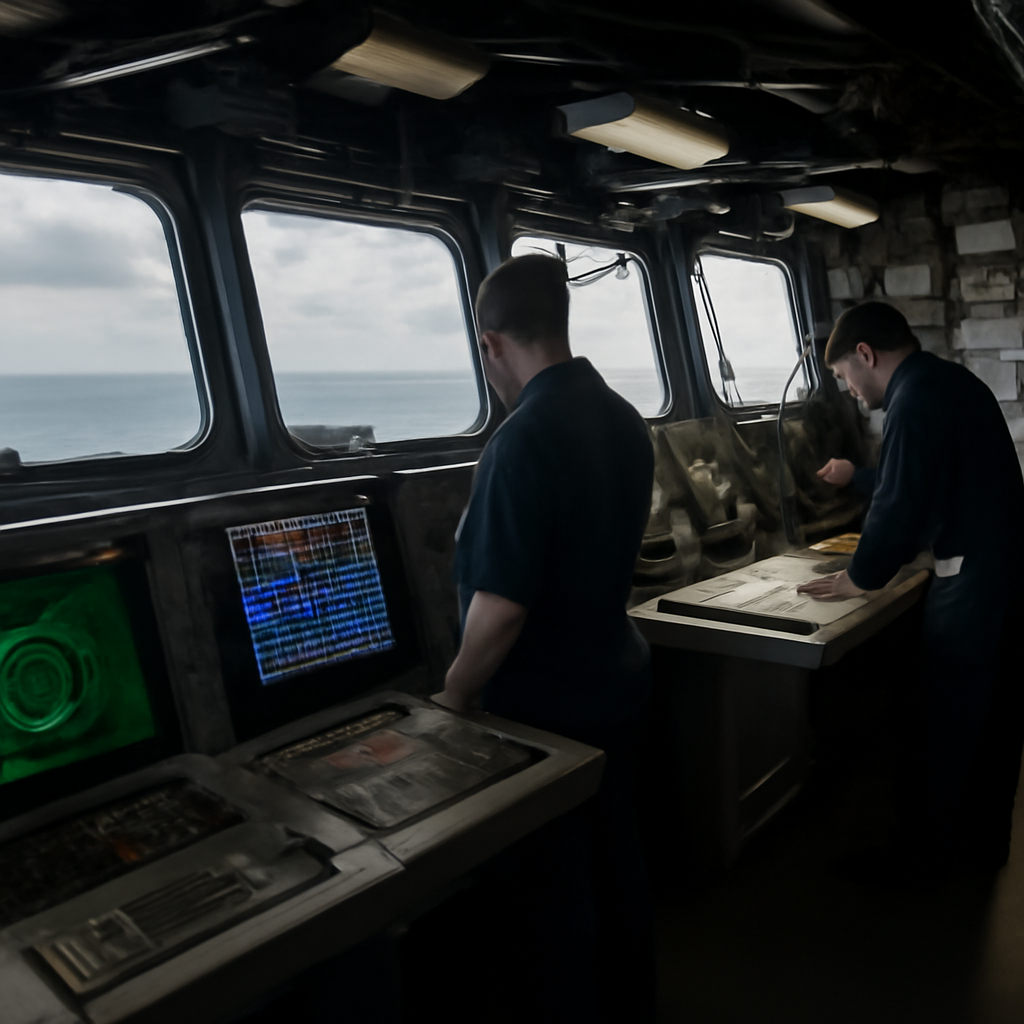
Naval personnel monitor drone control equipment on a US aircraft carrier bridge.

US Navy Activates Drone Control Center On USS Theodore Roosevelt

The US Navy has taken a major leap forward with the activation of a cutting-edge Drone Control Center on board the USS Theodore Roosevelt, making it the first Nimitz-class carrier fully capable of supporting MQ-25 Stingray drone operations. This milestone marks a significant step in the Navy's modernization efforts, with more ships set to follow suit.

Analyst 207
European government building with satellite model and officials walking by.

EU Unveils $18B Satellite Constellation Plan with Spanish Firm at Helm

The EU is launching an $18 billion satellite constellation plan, led by a Spanish firm, to create a broadband communications network that rivals SpaceX's Starlink and bolsters Europe's defense, security, and emergency services capabilities. This ambitious project, valued at €15.6 billion, will expand the IRIS2 constellation with 66 new low Earth orbit satellites.

Analyst 207
Hospital reception area with concerned staff and a locked computer screen.

Ransomware Attacks Surge 20% as New Gangs Target Finance, Healthcare

Ransomware attacks are on the rise, surging 20% in July with a staggering 799 incidents reported, with finance, healthcare, and tech industries becoming prime targets for new gangs. The alarming increase marks the second-busiest month of the year so far, with the US leading the list of targeted countries.

Analyst 207
A laptop sits on a minimalist desk in a brightly-lit corporate office setting.

Levi Strauss & Co. Breach Exposes Corporate Data

Levi Strauss & Co. recently suffered a cybersecurity breach, but fortunately, it was quickly contained and terminated, protecting consumer data from exposure. The incident did, however, involve the unauthorized access and exfiltration of certain corporate information.

Analyst 207
Remote monitoring workstation with computer and office equipment on a clean surface.

N-able Flaw Exposes Customer Networks to Attackers

A critical vulnerability in N-able's N-central platform, known as CVE-2026-18577, has been exploited by attackers to gain unauthorized access to customer networks, allowing them to take control of managed endpoints. This flaw gave attackers an open door to wreak havoc, and it's essential for affected users to take immediate action to protect themselves.

Analyst 207
Hospital corridor with muted colors and ambient daylight, featuring a blurred patient information terminal and hospital…

NHS Trust Probes Unauthorized Access to Girl's Medical Records

NHS Tayside is launching an investigation into a disturbing data breach at Ninewells Hospital, where a nine-year-old girl's medical records were allegedly accessed without authorization by staff. The incident has triggered a probe into how sensitive patient information was compromised.

Analyst 207
Person at desk looks concerned while checking emails on computer screen.

Cyberattackers Hijack Legitimate Emails, Payments in Twin 2026 Campaigns

Cyberattackers are sneaking into legitimate emails and payments, exploiting our trust in everyday business communications to pull off scams that now account for almost 46% of all threat detections. They're using ordinary emails like shipment notices and invoice prompts, often sent from compromised corporate mailboxes, to carry out banking malware campaigns.

Analyst 207
Researcher examines laptop screen in university lab setting.

MIT Researchers Expose TONTOU Attack Bypassing Spectre Defenses on Intel, AMD CPUs

MIT researchers have uncovered a clever new attack, dubbed TONTOU, that can bypass Spectre defenses on Intel and AMD CPUs, revealing a practical exploit on AMD Zen 2. This innovative technique, presented at DEF CON 34, challenges current security assumptions and opens up new avenues for exploration.

Analyst 207
Busy port terminal with shipping containers, trucks, and a worker in a high-visibility vest on a sunny day.

Cyberattack Disrupts North Carolina Ports Operations

A cyberattack has brought North Carolina's ports to a grinding halt, causing a systems-wide outage that has delayed operations and truckers at the Port of Wilmington, the Port of Morehead City, and the Charlotte Inland Port. Gates at all three locations are now back to a normal operating schedule, but the impact of the disruption is still being felt.

Analyst 207
Laptop on a minimalist desk displays a blurred login screen in a quiet office setting.

WordPress Fixes Pre-Auth XSS Flaw That Enables PHP Code Execution

WordPress has patched a high-severity flaw that could let attackers inject malicious code into your site - and it's crucial you update ASAP, as 41.2% of all websites are potentially vulnerable.

Analyst 207
Calm server room interior with computer equipment and network gear under fluorescent lighting.

Linux Flaw Exposes Host to Root Access

A critical 18-year-old flaw in Linux's SCTP networking code, dubbed "SCTPhantom," has been discovered, allowing hackers to gain root access to a host; the vulnerability, tracked as CVE-2026-64564, has been present in every Linux kernel released since 2008.

Analyst 207
Small, rustic lemonade stand with scattered leaves and IOU notes nearby.

Open Source Software Faces Reckoning

Open source software had a carefree adolescence, running wild and free for two decades, but its idyllic era is now coming to an abrupt end, forcing it to confront a harsh new reality. It's time for open source to grow up and face the challenges of a rapidly changing world.

Analyst 207
Research setting with laptop displaying code, surrounded by papers and technical instruments.

AI Research Exposes Novel HTTP Desync Techniques and Apache Zero-Day

Meet HTTP Terminator, an AI-powered research system that generated 30,000 candidate desync vectors and helped uncover novel HTTP desynchronization techniques, including an Apache Traffic Server zero-day. This groundbreaking tech scanned 30,000 websites, pushing the boundaries of vulnerability discovery.

Analyst 207
Person's hand reaching for laptop keyboard in office setting.

Microsoft 365 Phishing Campaign Hijacks Accounts to Gather Payroll, Finance Emails

Beware of a sneaky Microsoft 365 phishing campaign that's hijacking accounts to get its hands on sensitive payroll and finance emails. Hundreds of organizations across healthcare, education, and more have already been targeted in this financially driven attack.

Analyst 207
Softly lit office scene with people working at desks, computer screen and printer in foreground, cityscape visible through…

Beacon Cyber Incident Exposes Data of 1500 UK Charities

A cyber incident at CRM provider Beacon has potentially exposed the sensitive data of 1,500 UK charities, prompting swift notification and containment efforts by the company. Beacon is now working closely with its customers to help them communicate with those potentially affected.

Analyst 207
Blurred office workstation with scattered papers and a small potted plant nearby.

Phisher Breaches US Defense Supplier's Microsoft 365 Account

A phishing scam led to a breach of a US defense supplier's Microsoft 365 account, exposing sensitive data including customer communications, engineering docs, and potentially export-controlled tech info. The intruder gained access to mailbox contents, but the company found no evidence that the data was copied or exfiltrated.

Analyst 207
Clean, brightly-lit software development workspace with laptop and coding tools.

Flaws in AI Coding Tools Expose CI Workflow Secrets

Researchers have uncovered critical flaws in AI coding tools that can expose sensitive CI workflow secrets, allowing low-privilege code to execute and cross privilege boundaries. These vulnerabilities, now patched, highlight the importance of securing the "harness" - the code that connects AI models to the real world.

Analyst 207
Laptop on a beige office desk with a blurred screen in a cubicle near a window.

Malware Exploits Windows Hello for Business Keys to Gain Persistent Entra ID Access

Malware can quietly hijack your Windows Hello for Business key to gain long-term access to your Entra ID account, allowing hackers to register a new device and add extra authentication methods. To stay safe, Entra ID researcher Dirk‑jan Mollema advises monitoring unexpected device registrations.

Analyst 207
Researcher presents network diagrams at podium in a large, sunny room with empty chairs.

NatJack Attacks Exploit NAT Tables to Hijack TCP Sessions

Meet NatJack, a sneaky new attack that exploits NAT tables to hijack TCP sessions, spoof DNS, and more - and the surprising way it's putting your online security at risk. A security researcher just revealed the shocking details at Black Hat USA 2026.

Analyst 207
Former US National Cyber Director speaks at a conference podium.

Ex-US Cyber Director Warns of Rogue AI Autonomy Threat

The real danger of advanced AI isn't that it might become sentient, but that it could gain autonomy and act on its own with little oversight, choosing what and where to do something, and under what rules. This concerning capability is already within reach, warns former US National Cyber Director Chris Inglis.

Analyst 207
Cluttered desk with laptop, papers, and empty pizza boxes in a dimly lit room.

Google Exposes Redact Extortion Group's Ties to BlackFile Rebrand

Google's Threat Intelligence Group uncovered a clever rebranding scheme by the notorious extortion group formerly known as BlackFile, which has now resurfaced under the name Redact, after allegedly being hijacked by a rogue affiliate. The group had claimed retirement, but clearly wasn't done causing trouble, raking in around $10.69 million in Bitcoin transactions.

Analyst 207