"The observatory is just a public interface to explore the data we've been collecting for the past year," Layer3 Intel founder Sergiy Usatyuk told The Register.
Layer3 Intel and the Residential Proxy Observatory
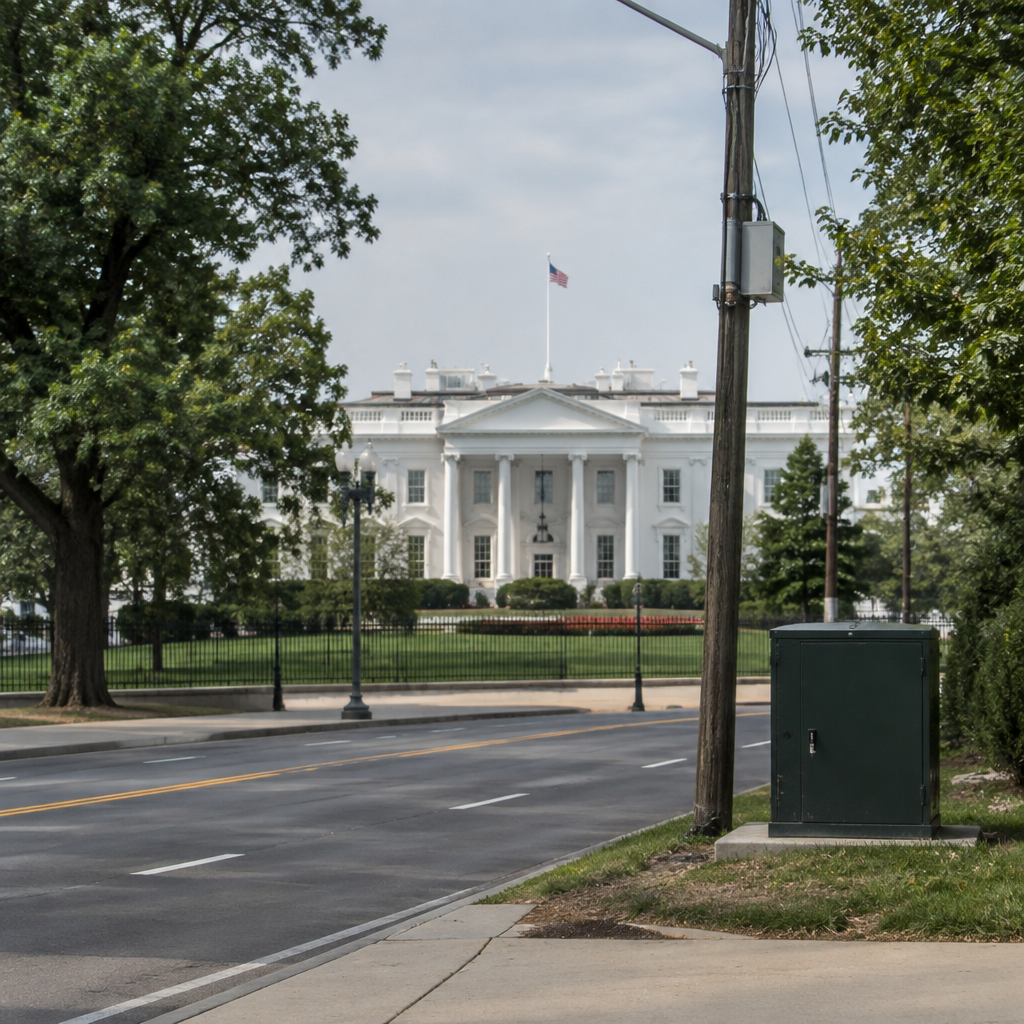
Security firm Layer3 Intel says its newly launched Residential Proxy Observatory flagged what appears to be residential-proxy exit activity inside the White House network. The observatory is presented as a public interface to data Layer3 has been collecting for roughly a year, and the firm says the new tool is what allowed it to spot the pattern that might otherwise have gone unnoticed.
Scale and timing of exits into the White House network
Layer3 reports that between October 5 and November 3 it observed 28 distinct residential proxy services exiting into the White House network nearly every day during that interval, totaling 236 separate exits. The firm adds that most of the activity occurred in the evening, White House time — roughly between 5 p.m. and midnight — a pattern Layer3 interprets as suggesting the exits are linked to devices used by someone at the White House rather than a transient guest.

The cyber insurance questionnaire just landed. Now what?
SOC 2, HIPAA, insurance renewals - someone has to own security strategy. Nubivance provides fractional CISO leadership without the full-time salary.
Get a security leadInfatica SDK and Synthient's Windows findings
Layer3 told The Register its data do not disclose how many machines might be acting as proxy exit nodes inside the White House network. The firm pointed to a post on X by security firm Synthient, which said it believes there are multiple Windows 10 and Windows 11 devices on the White House network that likely have the Infatica SDK installed. Infatica offers a software development kit that permits app developers to monetize users' internet connections by turning their devices into residential proxy exit nodes.
FBI bulletin: residential proxies, hijacking techniques, and how attackers use exits
Layer3 and The Register placed these observations alongside an FBI bulletin issued in March that warned customers to harden systems against hijacking techniques commonly used to convert user devices into proxy exits. The March bulletin listed malware, illicit SDK partnerships, and VPN services with hidden service terms that repurpose user computers as exit nodes as examples of vectors that can convert otherwise legitimate devices into infrastructure for criminal activity. The FBI added that residential proxies are commonly used to conceal command-and-control infrastructure, conduct phishing attacks, send spam, and disguise malicious traffic.
Layer3 underscored the operational risk: "Past research has shown that poorly secured proxy SDKs can allow internal network access and lateral movement," the firm explained. "If an SDK on this network has the same kind of flaw, anyone buying proxy access could use it to reach internal systems."
State Department logs, White House silence, and the immediate pattern
Usatyuk told The Register that Layer3's most recent observed residential proxy activity on the White House network occurred Wednesday night — "hours after the blog went live" — but had stopped by the time of the report. The U.S. State Department contacted Layer3 Thursday morning to request a copy of the firm's logs; Usatyuk said he provided them. The White House did not respond to questions for the story.
What this looks like for security teams, the State Department, and the White House network
- Security teams and technologists: The pattern described — frequent exits from many residential proxy services, concentrated in evening hours — will prompt internal hunts for infected machines and audits of installed SDKs on Windows 10 and 11 endpoints, particularly any apps that include monetization SDKs such as Infatica's.
- The State Department: By requesting Layer3's logs, the department has signaled a desire for data to validate the finding and to support any follow-up investigations or mitigation steps; it will be watching for corroborating telemetry and for confirmation that any implicated devices have been remediated.
- The White House network operators: If poorly secured proxy SDKs are present, operators face a direct operational risk because, as Layer3 warned, they could permit external buyers of proxy access to reach internal systems and enable lateral movement.
Layer3's data retention goes back to July 10, and Usatyuk said the continuous activity makes it "likely that White House IPs have been used by res proxy networks for all sorts of activity for some time now." He added a pointed hope: "Hopefully they've figured out the situation" — and "hopefully before any government secrets have been exposed."
Original reporting: The Register — The White House is apparently a popular residential proxy exit spot