Tag: vulnerability management
685 articles
xrdp Vulnerability Exposes Remote Code Execution Risk
A critical vulnerability, CVE-2025-68670, was discovered in the xrdp remote desktop server, allowing for remote code execution - a flaw that was thankfully patched in January 2026. This security risk was found during a routine audit, highlighting the importance of regular security checks to protect against potential threats.

CISA Mandates Patching of Ivanti Flaw Exploited in Zero-Day Attacks
The US Cybersecurity and Infrastructure Security Agency (CISA) is requiring immediate patching of a high-risk Ivanti flaw, CVE-2026-6973, that allows attackers with admin privileges to remotely execute code on vulnerable systems. This critical vulnerability affects Ivanti Endpoint Manager Mobile (EPMM) version 12.8.0.0 and earlier.
Mozilla Reveals AI-Powered Bug Detection Boosts Firefox Security Fixes
Mozilla's April bug cull was massive, with 423 Firefox security fixes - a whopping five times more than the previous month and 20 times the usual monthly average, thanks in part to a boost from AI-powered bug detection. This huge spike in repairs is a testament to the power of innovative technology in keeping Firefox users safe and secure.
Ivanti EPMM Flaw Exploited, Grants Admin-Level Access
A critical flaw in Ivanti's Endpoint Manager Mobile (EPMM) has been exploited, allowing attackers to gain admin-level access - and the government is taking swift action to mitigate the threat. Federal agencies are now required to remediate the vulnerability, known as CVE-2026-6973, by May 10, 2026.
Ivanti Discloses High-Severity EPMM Flaw Exploited in Zero-Day Attacks
Ivanti has disclosed a high-severity flaw in its Endpoint Manager Mobile (EPMM) product, which has been exploited in limited zero-day attacks requiring admin authentication. To protect against this vulnerability, customers are advised to patch to Ivanti EPMM versions 12.6.1.1, 12.7.0.1, or 12.8.0.1.
vm2 Library Vulnerabilities Enable Sandbox Escape and Code Execution
A dozen critical vulnerabilities in the vm2 Node.js library can be exploited by hackers to break free from sandbox restrictions and run malicious code on vulnerable systems. This serious security flaw has been assigned high CVSS scores, emphasizing the urgent need for users to patch their systems.
Palo Alto Networks Zero-Day Exploited in Wild, Firm Warns
Palo Alto Networks has warned of a critical zero-day vulnerability, CVE-2026-0300, being exploited in the wild, allowing unauthenticated attackers to execute code with root privileges on certain firewalls. This flaw affects a limited number of customers with exposed User-ID Authentication Portals.

Anthropic Exposes Tens of Thousands of Unpatched Flaws in Software Platforms
Tens of thousands of unpatched software flaws are lurking in the shadows, threatening cybersecurity, after Anthropic's AI tool Mythos uncovered nearly 300 vulnerabilities in Firefox alone. This astonishing discovery highlights the urgent need for rapid action to address the alarming gap in software security.
Vm2 Sandbox Flaw Exposes Host Systems to Code Execution Risk
A critical vulnerability, CVE-2026-26956, in the popular vm2 Node.js library can allow attackers to break free from the sandbox and execute malicious code on your host system, putting your entire environment at risk. To stay safe, upgrade to vm2 version 3.10.5 or later, or 3.11.2 for the latest protection.
Apache HTTP Server Flaw Enables DoS and Potential RCE Attacks
A critical flaw in the Apache HTTP Server, known as CVE-2026-23918, can be exploited to launch devastating denial-of-service (DoS) and potential remote code execution (RCE) attacks, putting your online security at risk. This high-severity bug has been patched in Apache HTTP Server version 2.4.67, so updating is crucial to prevent attacks.

CVE Feeds Overlook End-of-Life Software Vulnerabilities
The blind spot in CVE feeds is leaving end-of-life software vulnerabilities flying under the radar, with a staggering 167,286 false negatives identified in 2025 alone. This oversight can have serious consequences, as outdated software can still be exploited, even if it's no longer receiving patches.
AI Infrastructure Exposes Widespread Security Gaps
A staggering 2 million hosts and 1 million exposed services were uncovered through a simple scan of certificate transparency logs, revealing alarming security gaps in AI infrastructure. The findings painted a concerning picture: most AI projects lack even basic authentication, leaving them vulnerable to exploitation.
Weaver E-cology Flaw Exploited Through Debug API Endpoint
A critical bug in Weaver E-cology, known as CVE-2026-22679, is being actively exploited - allowing hackers to take full control of your system with a CVSS score of 9.8. This severe vulnerability lets attackers execute commands without needing login credentials, putting your entire system at risk.
Microsoft Updates Disrupt Third-Party Backup Apps on Windows
Microsoft's latest Windows security update has caused disruptions to third-party backup apps, adding a vulnerable kernel driver to its blocklist to protect users from potential exploits. This change aims to prevent attackers from escalating privileges or executing arbitrary code, but has unfortunately caused failures in some backup products.
Anthropic Expands Claude Security Model to Cybersecurity Platforms
Anthropic's Claude Security Model just got a major upgrade, now helping cybersecurity platforms detect and fix software flaws faster than ever. With its advanced capabilities, Claude Security provides detailed vulnerability explanations, confidence rankings, and even generates step-by-step patch instructions.
cPanel Vulnerability Exploited, Ransomware Attacks Reported
A critical cPanel vulnerability, CVE-2026-41940, has been exploited, putting servers at risk of full takeover and ransomware attacks - with a near-worst-case severity score of 9.8. This flaw affects cPanel, WebHost Manager, and WP Squared, and has already been flagged by the US government's cybersecurity agency as being exploited in the wild.
Anthropic Unveils Claude Security for AI-Powered Vulnerability Scanning
Boost your organization's security with Claude Security, now in public beta, which scans codebases to detect and fix software vulnerabilities with just a few clicks. Say goodbye to tedious API integrations and custom agent builds - simply access the feature from the Claude.ai sidebar and start scanning today!
AI Agents Expose Identity Security Gaps
Imagine an AI agent that can uncover thousands of hidden security vulnerabilities, some of which have gone undetected for nearly 30 years - and the potential risks that come with it falling into the wrong hands. A single powerful AI agent can scan for weaknesses faster and more persistently than hundreds of human hackers, highlighting a pressing need for secure deployment.
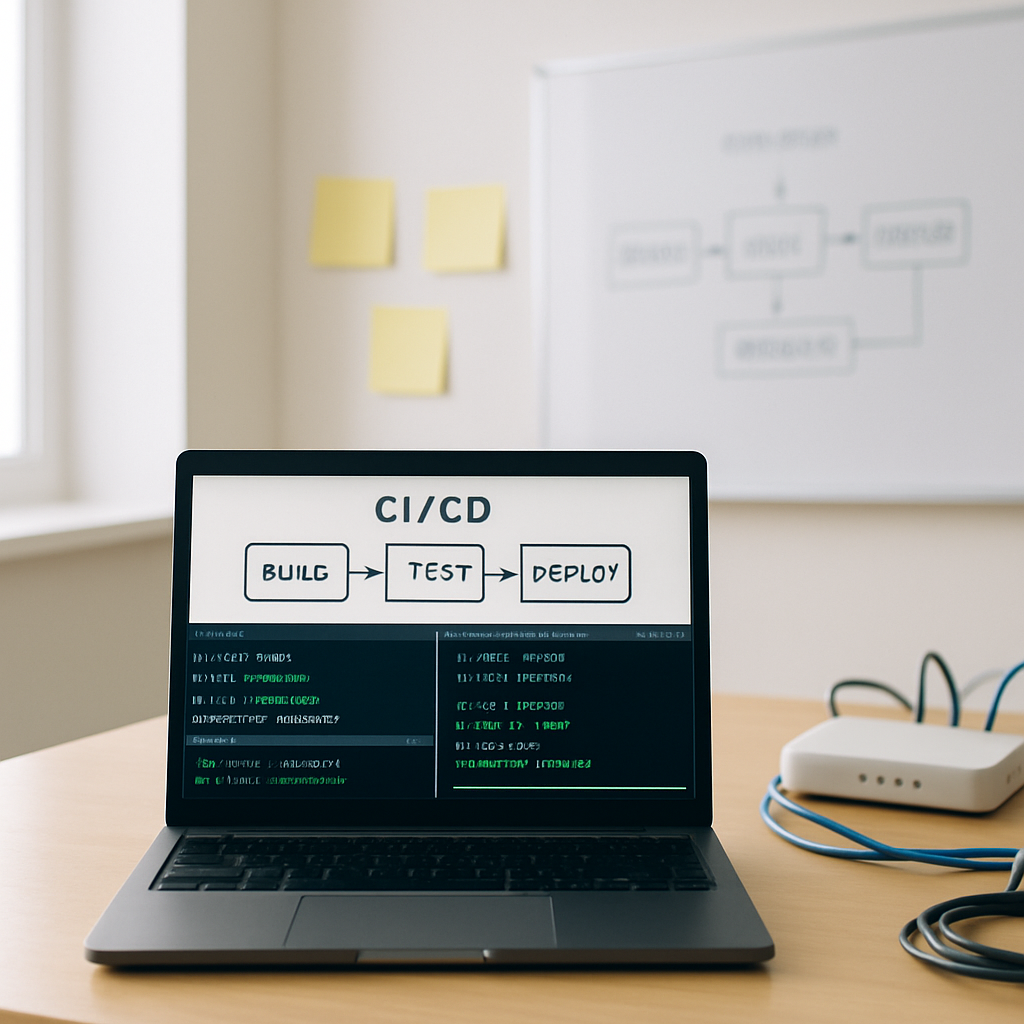
Google's Gemini CLI Fix Sparks CI/CD Pipeline Disruptions
A recent patch for Google's Gemini CLI has sparked disruptions in CI/CD pipelines, ironically caused by a critical infrastructural flaw - not an AI quirk - that allowed remote code execution due to over-permissive workspace trust in headless mode. The fix, while swift, may trip automated pipelines that relied on the old settings.

Attackers Target New Assets Within Minutes of Exposure
The moment a new asset goes live with a public IP address, the clock starts ticking - and within minutes, attackers are circling, waiting to pounce on unsuspecting targets. In just 24 hours, a newly exposed asset can go from discovery to compromise, with threat actors exploiting vulnerabilities at an alarming rate.
Firefox Exposed: AI Model Uncovers 271 Zero-Day Vulnerabilities
Meet the AI model that just supercharged Firefox security, uncovering a whopping 271 zero-day vulnerabilities that have now been squashed in the latest update to Firefox 150. This game-changing collaboration between Firefox and Anthropic's cutting-edge tools has made the browser safer than ever.
AI-Assisted Bug Hunt Exposes High-Severity GitHub Flaw
In a thrilling example of AI-powered detective work, a team of researchers uncovered a high-severity flaw in GitHub's infrastructure, dubbed CVE-2026-3854, which could have allowed hackers to access private repositories with just one command. The researchers cracked the code in under 48 hours, and GitHub swiftly patched the issue within six hours of disclosure.
GitHub swiftly patches flaw exposing millions of private repos
GitHub quickly squashed a massive security flaw, CVE-2026-3854, that could have let hackers access millions of private repositories with just one sneaky git push. The vulnerability allowed attackers to inject malicious code by exploiting how GitHub handled user-supplied options during git push operations.

Exposure Management Platforms Face Validation Test
Are you tired of filling dashboards with green and closing hundreds of tickets, only to wonder if your organization is truly safer? The harsh reality is that most exposure management platforms fall short in connecting remediation to real risk reduction.