Tag: supply chain
1740 articles
Agents Expose Blind Spots in AI Security Controls
The surprising truth is that about 1,000 AI-powered agents are hiding in plain sight, operating outside the view of your identity infrastructure - and it's not because they're trying to evade detection. They're simply embedded in the software you already use, creating a blind spot in your security controls.
GitHub Repositories Targeted in Credential-Stealing Workflow Attack
Malicious actors have launched a sneaky credential-stealing attack on GitHub repositories, using hijacked accounts to spread a malicious workflow that hit 345 repositories in just a few hours. The GhostAction campaign is back with a vengeance, putting developer credentials at risk.
Hackers Exploit Bing Redirects in Google Ads to Spread ClickFix Malware
Malicious actors have found a sneaky way to spread ClickFix Malware by exploiting Bing redirects in Google Ads, tricking macOS users into downloading a fake Claude installer that secretly installs harmful commands. This clever tactic, dubbed Adception, uses legitimate search-ad and redirect infrastructure to evade security checks.
US Army Wrestles with Zero Trust Identity Challenge
The US Army faces a daunting task: folding 5,000 disparate IT systems into a single, secure platform that verifies the identity of every connected user and device, a crucial step towards achieving Zero Trust Identity by 2027. To get there, they're developing flexible onboarding pathways to bring all systems under one roof.
Chinese Hackers Exploit AI-Powered Tool to Breach Korean Banks
Chinese hackers have breached South Korean financial institutions using an AI-powered tool, with CrowdStrike Intelligence uncovering evidence of exfiltrated data and a sophisticated campaign that went beyond mere reconnaissance. The alarming breach, active from late September to early October, highlights the growing threat of AI-fueled cyberattacks.
States Expose TP-Link's Router Security Risks, China Ties
TP-Link is pushing back against a wave of lawsuits from five US states that claim the company misled consumers about its router security and ties to its former Chinese affiliate, allegations that TP-Link vehemently denies. The company vows to fight the suits in court, calling the claims false and unfair.
Citrix Warns of Zero-Day Attack on Unpatched NetScaler Systems
Citrix is warning users of a zero-day attack targeting unpatched NetScaler systems, so if you haven't updated yet, now's the time to take action and protect your systems from potential harm.
Ransomware Attacks Soar to Record High in Q3 2026
Ransomware attacks have skyrocketed to a record high, with 2,627 claimed incidents in Q3 2026 - a 27% surge from the previous quarter and a 61% jump from the same period last year. This alarming trend signals a significant escalation of the threat landscape across all major sectors.
Citrix Patches Flaw That Enables RCE in SAML Deployments
Citrix has patched a critical vulnerability, CVE-2026-107406, with a near-perfect score of 9.5, that could allow devastating remote code execution or denial-of-service attacks in SAML deployments. The flaw can be triggered under specific configuration conditions when NetScaler instances are set up as a SAML identity provider or service provider.
UK Warns of China's Integrity Tech Cyber Threat Tactics
China's Integrity Tech is raising red flags with its shady cyber activities, including building and selling malicious tools, hosting infrastructure, and compromising global networks. This tech group's ties to Beijing-backed cyber threats like Flax Typhoon have prompted a joint warning from the US, UK, and allied countries.
Microsoft Warns of Security Update Cutoff for Outdated Windows Devices
Don't wait until it's too late: if you're running an outdated version of Windows, you'll lose access to crucial security updates after May 17 and June 19, 2027, when key certificates expire. Upgrade to a supported version now to stay protected.
GoBalance Flaw Exposes Dark Web Sites to Hijacking
A careless mistake made by GoBalance has put numerous dark web sites at risk of hijacking, with a developer reportedly uploading a crucial private key into a software update. This simple error exposed the sites to potential takeover, highlighting the importance of secure coding practices.
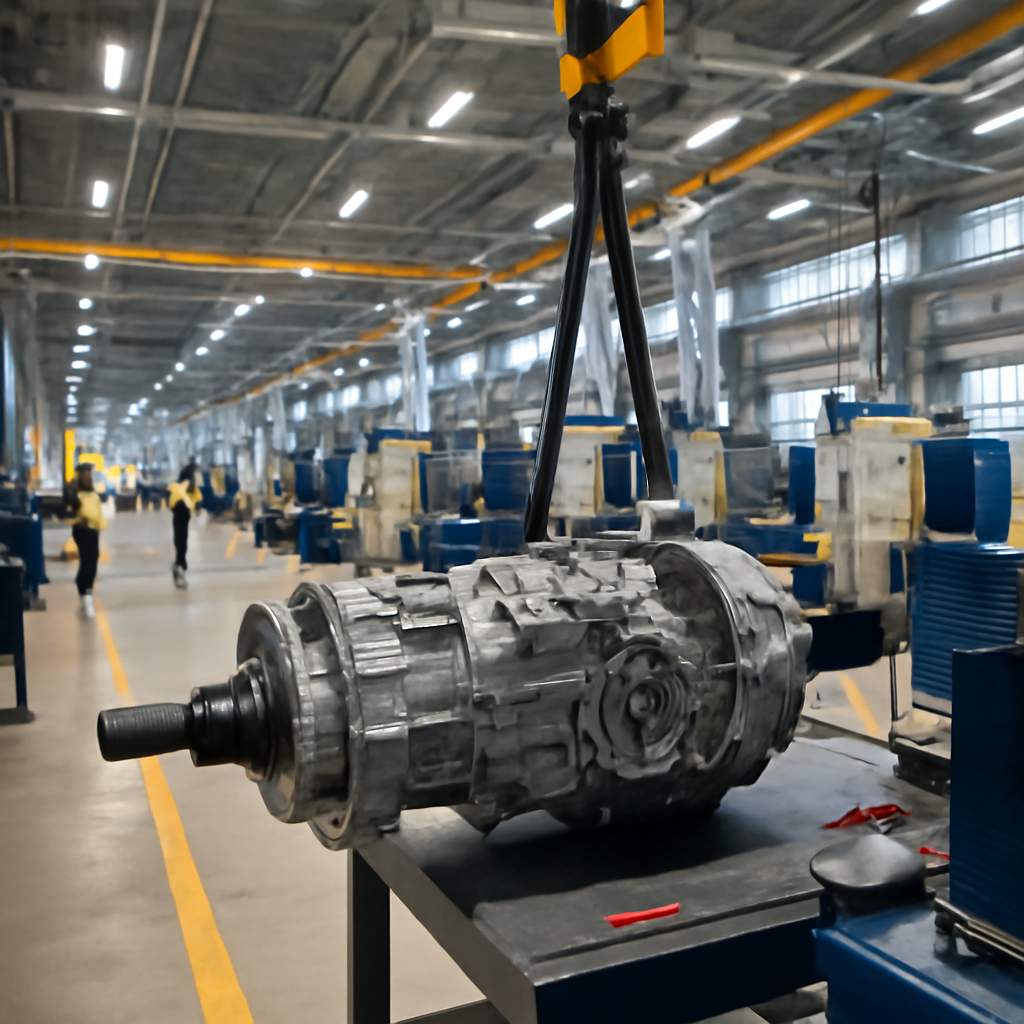
SAPA Transmission Targets US Defense Industrial Base Revitalization with Advanced Military Vehicle Tech
SAPA is revolutionizing the US defense industry with cutting-edge military vehicle tech, including a massive 200,000-square-foot manufacturing center that will create over 200 jobs. By addressing legacy transmission gaps, they're tackling a critical issue that's held back military vehicle performance for decades.
Anthropic Launches Cybersecurity Program to Fortify Critical Infrastructure
Anthropic is stepping up to support defenders of critical infrastructure and open-source software, who are rich in experience but often low on resources, by launching a long-term cybersecurity program to identify and fix vulnerabilities. By combining its Claude models, engineering expertise, and threat research with partner cybersecurity firms, Anthropic aims to help safeguard critical infrastructure from exploitation.
FBI Disrupts Chinese Hacking Tools, Warns of PRC Spies Targeting Global Networks
The FBI has struck a blow against Chinese hackers, seizing seven web domains linked to a suite of hacking tools, including the notorious FishHub malware, which was used to target global networks, including roughly 20 Taiwanese universities. This malware was designed to facilitate phishing activity, allowing hackers to gain a foothold in vulnerable systems.
Ransomware Attack Targets Japan's IDCF Cloud, Disrupts Government Clients
A massive ransomware attack has hit Japan's IDCF Cloud, crippling services for 495 companies and local governments, with hackers claiming to have encrypted a staggering 3.6 PB of data. The breach, which began on October 7, forced IDCF Cloud to immediately shut down its East Japan Region 1 cluster to prevent further damage.
Ransomware Affiliate Betrayal Exposes Insider Threats
A shocking 94% of Internet of Medical Things devices are vulnerable to future "harvest-now, decrypt-later" attacks due to their inability to be upgraded to post-quantum cryptography, leaving sensitive health data at risk. This stark gap in security exposes a critical weakness in healthcare systems.
China-Linked Hackers Expose Email Portal With Stolen Data
Meet Integrity Technology Group, a China-based company with ties to the government that's been caught red-handed running a web portal that lets others snoop on stolen emails. The US and UK have already slapped sanctions on the company, but the details of its shady operation are only now coming to light.
Nvidia Bug Exposes Thousands of GPU Servers to Potential Disruption
A newly discovered vulnerability in Nvidia's DCGM Exporter, tracked as CVE-2026-47483, has left around 2,100 GPU servers exposed to potential disruption, with a staggering 12,000 GPU UUIDs and $100M in hardware at risk. Researchers warn that unauthenticated actors could exploit this flaw to crash the GPU monitoring service, making a swift patch to version 4.8.2 or later a top priority.
Shai-Hulud Worm Compromises AI Platform Tensorlake
A malicious version of the Tensorlake SDK, downloaded around 12,000 times per week, was briefly infected with the Shai-Hulud worm, which could have allowed attackers to hijack credentials and sensitive data. Fortunately, the issue was quickly detected and resolved, with the package being pulled and updated to a safe version.
Breaches Expose Sensitive Data at Dropbox, Healthcare Firms
Massive data breaches are making headlines, with over 150 million driver's licenses compromised and around 5,000 Dropbox accounts exposed through a third-party vulnerability. These staggering incidents highlight the vulnerability of our sensitive information in today's digital landscape.
Cisco Discloses Critical Flaws in Nexus Switches
Cisco has uncovered five critical vulnerabilities in its Nexus switches that could let hackers run malicious code with root access or bring down entire networks, causing major disruptions. This security threat affects Nexus 3000 and 9000 Series switches, putting your network at risk of remote code execution and denial-of-service attacks.
Chinese Hacker Exploits AI in South Korean Bank Data Heist
Meet the new face of cybercrime: AI-powered hacking. A Chinese hacker recently used agentic AI tooling, alongside traditional tactics, to pull off a massive data heist at a South Korean bank.
FBI Warns of Ongoing FortiBleed Threat to Fortinet Devices
The FBI and US Secret Service have sounded the alarm: a whopping 86,644 Fortinet devices across 194 countries are compromised, and the FortiBleed threat is still very much active, leaving organizations at risk of being locked out of their own systems. This widespread campaign targets Fortinet FortiGate firewalls and SSL VPN gateways, putting businesses and individuals on high alert.