Tag: supply chain risk
79 articles

Security Leaders Exclusive: Critical AA Subsidiary Breach
Envoy Air endured a sudden cyberattack that disrupted internal systems and may have exposed passenger and loyalty data — a wake-up call that regional carriers are critical cogs in global air travel. As teams race to contain the breach and restore services, the bigger challenge will be rebuilding passenger trust while ripple effects touch flights, baggage and communications.

Security Leaders Exclusive: Critical Subsidiary Cyberattack
Imagine waiting in line as screens go dark—Envoy Air’s recent critical subsidiary cyberattack forced airports into paper processes and left passengers in limbo. Its a wake‑up call that a single vendor breach can ripple across the entire aviation system, spurring urgent containment, recovery and renewed focus on supply‑chain risk.
Security Leaders Exclusive: 77% Data Loss Is Costly
Insider-related data loss has hit 77% of organizations in the last 18 months — a costly, everyday emergency playing out in email threads, cloud buckets and third‑party integrations. Cloud sprawl, identity proliferation and siloed tooling — plus human shortcuts — turn trusted channels into easy exit ramps for sensitive data.
Unified View: Must-Have for Best Crisis Response
When crises cascade, alerts alone create noise — a Unified View gives teams one real-time picture so actions align, forensics stay intact, and damage is contained. Consolidated dashboards, clear escalation rights and joint drills turn fragmented responses into fast, coordinated action.
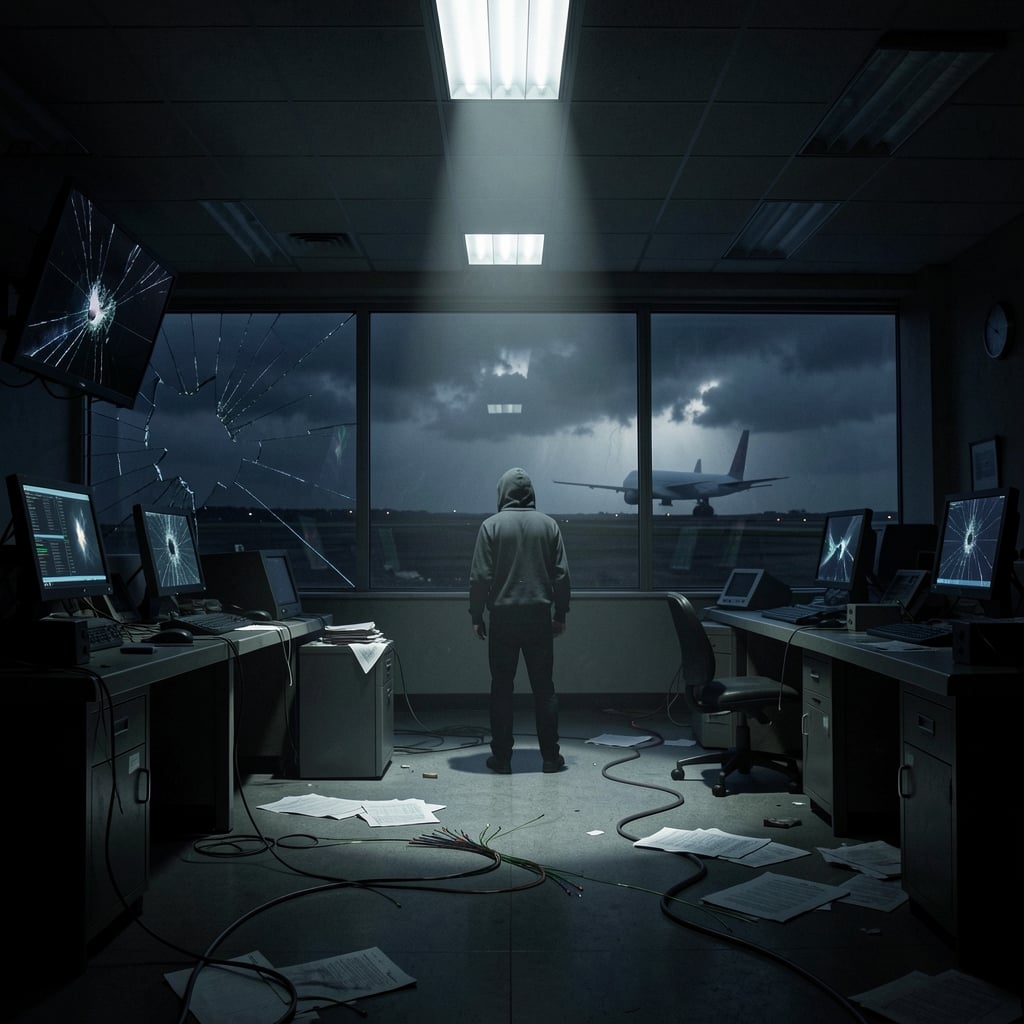
Cyberattack Cripples EU Airports: Exclusive Response
When the screens went black and check‑in kiosks died at multiple European airports, staff reverted to paper and long queues — a stark reminder that a single cyberattack can paralyze travel. As IT teams, CERTs and Europol raced to contain ransomware and trace the perpetrators, experts say this disruption must spark urgent, industrywide cybersecurity reform.
Lanscope Endpoint Manager Exclusive: Critical Bug Exploited
A critical, actively exploited flaw in Motex Lanscope Endpoint Manager (CVE-2025-61932) — now on CISA’s KEV list — can turn your endpoint manager into an attacker’s shortcut. If you run on‑prem Lanscope Client, act now: patch immediately, isolate affected hosts, and hunt for suspicious activity.
typosquatted npm package: Shocking Dangerous Heist
A single malicious line in a typosquatted npm package quietly CC’d thousands of Postmark emails to an attacker—turning a routine dependency into a stealthy data leak. It’s a wake‑up call: strong dependency hygiene, provenance checks, and runtime protections are essential to keep outbound messaging safe.