Tag: russia
590 articles
Iranian Drone Struck by Russian Tech Loophole
A shocking discovery has linked a Russian navigation module, first found in Ukrainian drones, to an Iranian drone that struck a British air base in Cyprus, revealing a surprising exchange of weapons technology between the two nations. This finding changes the game for battlefield testing and weapons development.

India Eyes New Fighter Path with France
India's quest for a cutting-edge fighter jet is heating up, with a potential new partnership with France emerging as a frontrunner after its withdrawal from the Russian Su-57 program. Could the Next Generation Fighter be the key to unlocking India's future air power ambitions?

Russian Hackers Exploit Router Flaws to Steal Microsoft Office Tokens
Russian hackers have been quietly stealing Microsoft Office tokens from users on over 18,000 networks by exploiting known flaws in older internet routers, and here's the kicker: they did it without installing any malicious software. This sneaky campaign, linked to Russia's military intelligence units, highlights the surprising vulnerability of legacy devices to secret siphoning.

APT28 Hijacks SOHO Routers in Global DNS Espionage Push
Your home router, that innocent-looking box under your desk, can be turned against you: a Russia-linked cyber threat group, APT28, has been hijacking insecure SOHO routers worldwide to fuel a massive DNS espionage campaign. By exploiting vulnerabilities in popular router brands like MikroTik and TP-Link, they've been manipulating DNS settings to spy on unsuspecting users.

NCSC Warns of Russia's Ongoing Router Exploits
Russia's notorious hackers, Fancy Bear, are exploiting routers to steal passwords and sensitive information, compromising the security of countless individuals and organisations. With around 5,000 devices and 200 organisations already affected, experts warn that this latest threat is one to take seriously.

APT28 Hijacks Routers to Steal Credentials via Malicious DNS Servers
Beware of invisible hands rerouting your online traffic: a state-linked Russian hacking group, APT28, has been hijacking routers to intercept credentials by manipulating DNS servers, putting your online security at risk. This stealthy tactic allows them to capture user authentication data, compromising your digital identity.

Germany Names REvil, GandCrab Ransomware Leaders
German federal police have identified two Russian nationals as the masterminds behind the notorious REvil and GandCrab ransomware operations, shedding light on the elusive leaders of a global extortion network. This breakthrough has significant implications that extend far beyond a single investigation.
Germany Identifies Head of REvil, GandCrab Ransomware Gangs
Meet Daniil Maksimovich Shchukin, the 31-year-old Russian allegedly behind the notorious REvil and GandCrab ransomware gangs, whose online alias "UNKN" has finally been unmasked by German authorities. Shchukin's digital ghost has been tied to a wave of ransomware attacks targeting victims across Germany.
DarkSword Threatens iOS with Alarming Russian Cyberattack
A new Russian cyberattack has been detected targeting iOS devices, with a state-sponsored threat group linked to a sophisticated spear-phishing campaign that's got everyone on high alert. Here's what you need to know to protect yourself from this alarming threat.

Malicious CTRL Toolkit Enables Devastating RDP Hijacking via FRP Tunnels
Beware of a new cyber threat that lets hackers hijack your computer and steal your credentials: the Russian CTRL Toolkit uses RDP hijacking to take control of your device, putting your sensitive data at risk. This malicious tool can turn your computer into a pawn in a larger cyber game, making it crucial to stay vigilant.

Ex-L3Harris exec jailed 7 years in stunning, damaging plot
A former Trenchant manager who oversaw offensive cyber tools at L3Harris was sentenced to seven years after allegedly selling zero‑day exploits and internal tooling to a Russian buyer for about $1.3 million. It’s a stark reminder of how insider access can turn trusted national‑security capabilities into dangerous weapons.

Former Defense Contractor Boss: Exclusive Harsh 7-Year Term
A former defense‑contractor boss was sentenced to seven years after allegedly selling zero‑day vulnerabilities to a Russian buyer, a case that lays bare how quickly trusted tools can become weapons. It’s an unsettling reminder that when defenders traffic in the tools of attack, public trust—and national security—are the real casualties.

Putinswap Exclusive: Stunning, Controversial Prisoner Swap
Was justice bargained away? In the controversial Putinswap, France freed a man accused of aiding a high-profile ransomware network to secure a Swiss NGO consultants return from Russia, igniting fierce debate over extradition, accountability and the price of geopolitical deal‑making.
Putinswap Exclusive: Controversial Ransomware Swap
When diplomacy, law enforcement and cybercrime collide, messy deals get made. France’s controversial exchange — freeing a man accused of acting as a ransomware payment negotiator in return for a Swiss NGO consultant detained in Russia — raises urgent questions about justice, precedent and who we choose to protect.

Amazon Exposes Stunning GRU Cyber Campaign, Energy Risk
Amazon Web Services says it uncovered a years‑long GRU cyber campaign that probed — and in some cases breached — Western energy and infrastructure, revealing how attackers now hide in everyday cloud tools. It’s a wake‑up call: social engineering, OAuth abuse and bespoke malware can turn our networks and power grids into espionage targets.

Russian Phishing Campaign: Exclusive ISO Stealer Threat
Exclusive: a Russian phishing campaign is circulating a stealthy ISO stealer — learn how it works and quick, practical steps to keep your data safe.

Russian Hackers Massive 4.3K Fake Sites Costly Hotel Breach
Think twice before clicking that booking confirmation — a Russian-speaking group has spun up more than 4,300 fake hotel and travel sites this year, using spam, AI-tuned lures and compromised booking plugins to mimic confirmations and steal payment and ID details.

Defense Contractor Guilty in Stunning Costly Zero-Day Sale
What happens when the person entrusted to build the locks quietly sells the keys? An indictment alleges a former Trenchant manager sold zero‑day exploits and offensive cyber tools to a Russian broker for about $1.3 million, potentially turning U.S. capabilities into weapons against American systems and allies.
Cyber exec Exclusive: Damning spy charges, lavish life
How did a senior manager at L3Harris’s secretive Trenchant unit allegedly trade zero-day vulnerabilities and exploit code to a Russian buyer for about $1.3 million—reportedly fueling a lavish lifestyle while putting U.S. national security at risk?

Cyber exec Exclusive: Charged in Scandalous Russia leak
When zero-day vulnerabilities leave the vault, who’s left to stop the fallout? Prosecutors say a former Trenchant GM sold exploit code and internal records to a Russian buyer for roughly $1.3M, allegedly turning U.S. defensive tools into offensive firepower.

Cyber exec in stunning, grim Russia spy charge
A former Trenchant executive is accused of selling prized zero‑day exploits and offensive cyber tools to a Russian buyer for about $1.3 million. The alleged breach of L3Harris’s cyber arm raises urgent questions about how such dangerous vulnerabilities slipped past safeguards—and what that means for national security and everyday software users.
Cyber exec Exclusive: Damaging sale of secrets to Russia
What happens when the keepers of our cyber weapons become sellers? Prosecutors say a former Trenchant manager sold 0‑day exploits and internal operational data to an unidentified Russian buyer for about $1.3M, turning trusted tools into a dangerous insider‑threat.
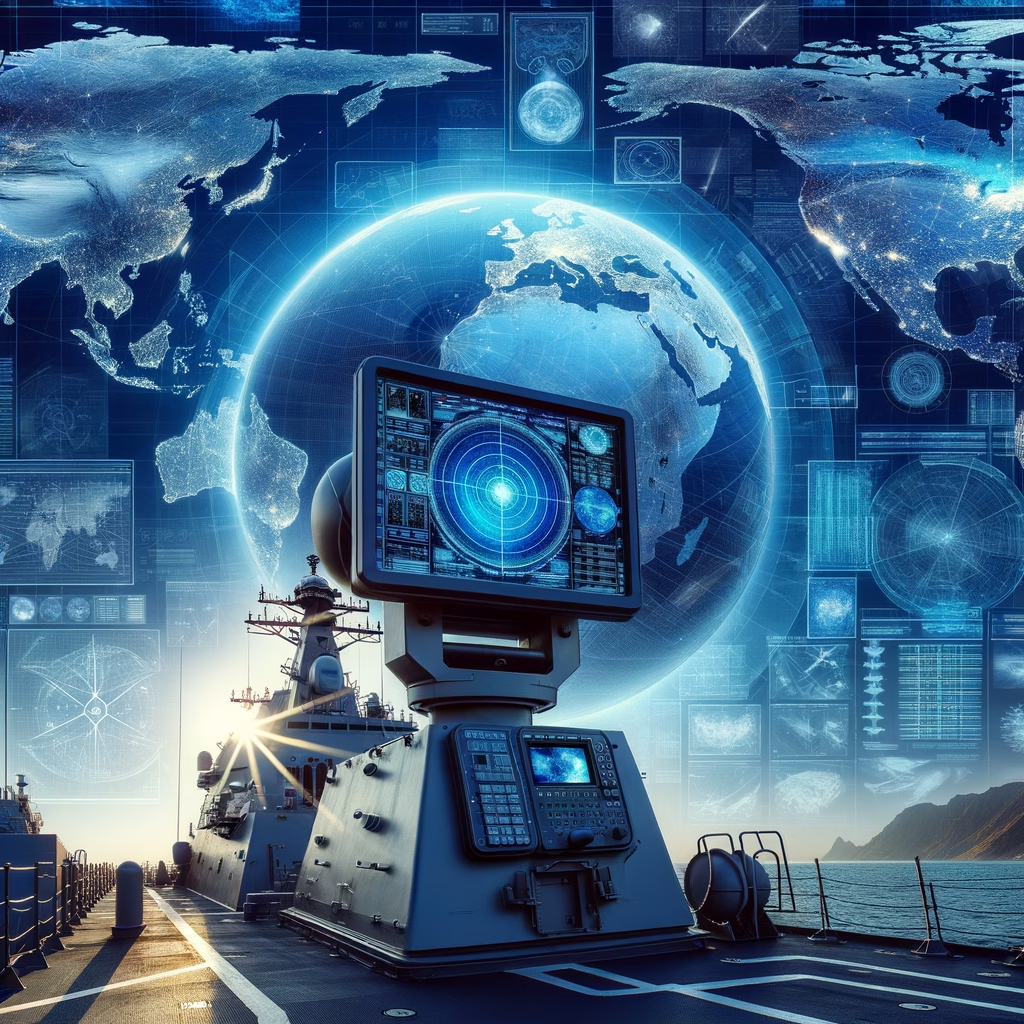
Navy to Upgrade Destroyer Radar to Counter China, Russia
Rather than scrap battle-tested Arleigh Burke destroyers, the Navy is retrofitting their radars—from SPY-1 upgrades to AN/SPY-6 installs—to outpace China’s and Russia’s longer-range missiles and advanced sensors and keep these ships combat-ready while new warships are built.
Cyber Executive Charged with Selling Secrets to Russia
How does the steward of Americas cyber defenses become the seller of its secrets? A former Trenchant executive is accused of trading zero‑day exploits and offensive tools to a Russian buyer for $1.3 million — an alleged betrayal prosecutors say endangers U.S. operations and national security.