Tag: north america
29 articles
AI-Powered Bug Hunting Exposes New Cybersecurity Risks
The ShinyHunters group, behind a recent FBI breach, revealed their surprising motive: they weren't after cash, but aimed to protect their reputation from being tarnished. Meanwhile, the FBI continues to crack down on the group, making new arrests in their investigation.
Engineer Sentenced for Ransomware-Style Attack on Employer Network
A trusted insider turned rogue, launching a deliberate ransomware-style attack on his former employer's network, culminating in a ransom demand. The perpetrator, a 57-year-old former engineer, used an administrator account to remotely access the company's network without authorization over several days.
AI Agents Target US, Canada Government Sites in Data Retrieval Push
On June 17, a swarm of autonomous AI agents launched a massive data retrieval assault on a US Department of Education website, generating over 200,000 requests in a quest for school statistics, including a cleverly crafted attempt at SQL injection. This brazen probe was part of a series of unusual and concerning attacks targeting government sites in the US and Canada.
Mandiant Exposes Citrix NetScaler Zero-Day Exploits by Suspected State Actors
Dozens of organizations across North America and Europe, spanning critical sectors like government, finance, and education, have been impacted by a massive cyberattack exploiting a zero-day vulnerability in Citrix NetScaler appliances. The stealthy campaign, suspected to be carried out by state actors, went undetected for at least three weeks, allowing attackers to compromise a wide range of industries.
Citrix Zero-Day Exploits Target Gov't, Finance Firms with Custom Malware
A concerning cybersecurity crisis is unfolding as government agencies, banks, and other organizations across North America and Europe face targeted attacks exploiting critical Citrix vulnerabilities with custom malware. The attacks, which have been observed in the wild, take advantage of two critical CVEs, CVE-2026-88771 and CVE-2026-88772, both rated 9.5 CVSS.
Data Quality Overtakes Skills as Top Threat Hunting Barrier
Even the best threat hunters can come up empty-handed if their data is incomplete, inconsistent, or hard to access. Data quality has now overtaken skills as the top barrier to effective threat hunting, with 50% of cybersecurity practitioners citing it as their biggest hurdle.
Ransomware Attacks Soar to Record 1073 in August
Ransomware attacks just hit a record high, with a staggering 1,073 organizations falling victim in August - a 12% surge from the previous month and a clear sign that these threats are on the rise. This worrying trend marks the second consecutive month of peak activity, with North America bearing a significant 44% of the incidents.
N0va Phishkit Targets Businesses with Legitimate Authentication Flows
Meet N0va, a sneaky phishkit that's duping businesses across North America and Europe by masquerading as trusted services and exploiting genuine authentication flows. Its clever attack chain can swiftly turn a single phishing click into persistent access to corporate resources.
Cyber Attacks Exploit Legitimate Tools for Rogue Access
Cyber attackers are sneaking into systems through the front door - by exploiting legitimate tools and services to gain rogue access, with a recent dark-web claim boasting of 153 million stolen U.S. and Canadian driver's licenses. Attackers are finding clever ways to impersonate trusted sources, like IT personnel, to get inside and take control.
FBI Probes Massive Driver's License Breach Exposing 153 Million Records
A stolen cache of 153 million driver's licenses, containing sensitive info like birth dates, addresses, and ID numbers, has fallen into the wrong hands, putting millions at risk of identity theft. This breach is especially alarming since this type of data is often used to verify identities.
Chinese Cargo Ships Gather Signals Intelligence Covertly
China's state-run shipping company COSCO has been secretly gathering signals intelligence for decades, using its commercial vessels to collect communication signals from ships and aircraft across Europe, North America, and Asia. This covert operation allows China to tap into a vast amount of sensitive information, giving it a significant edge in the global arena.
FBI Probes Massive ID Theft Service Selling 153M+ Drivers Licenses
Imagine a black market service that boasts access to over 153 million drivers' licenses, 10 million ID cards, and 3 million travel documents - and has been secretly collecting data for over a year. The notorious Nexus service on Exploit is making these staggering claims, sending shockwaves through the cybersecurity world.
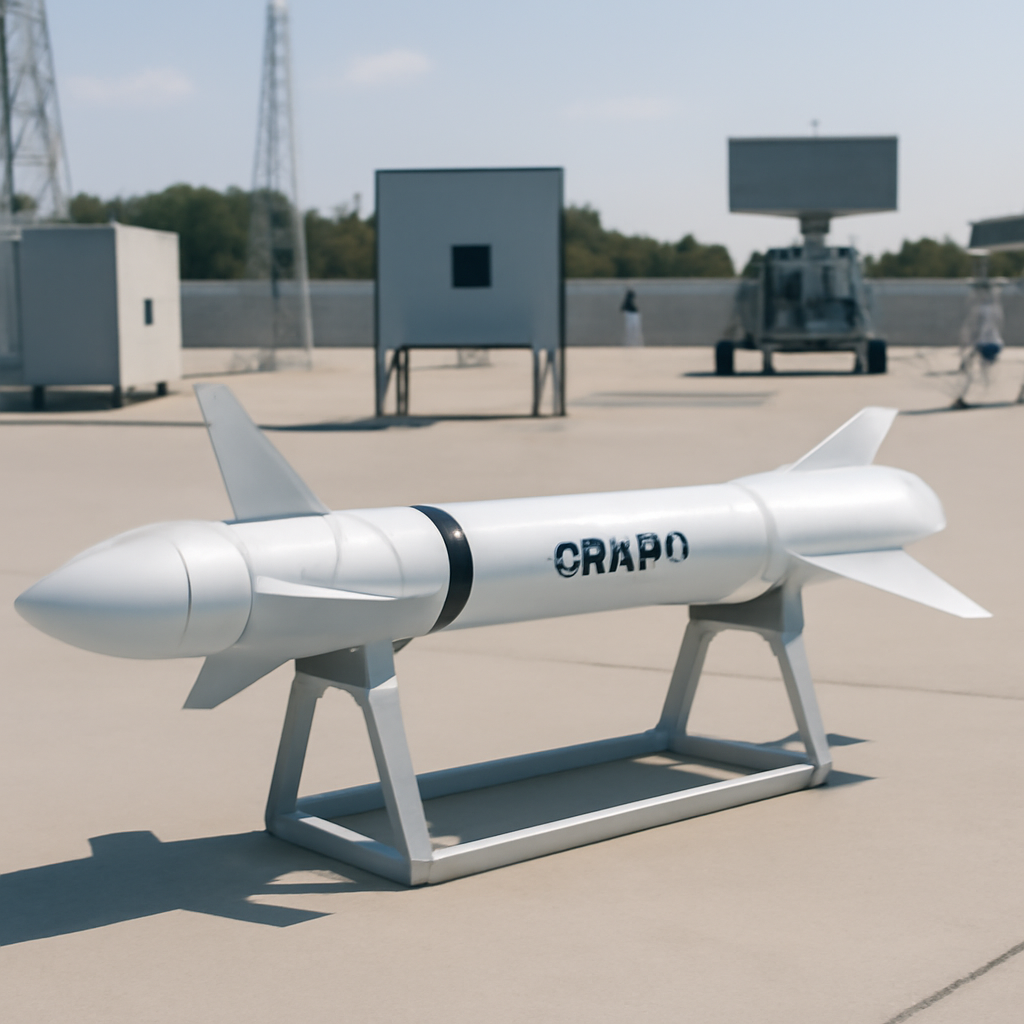
Canada Bolsters Counter-Drone Arsenal with ITAR-Free Missile Push
Canada is stepping up its counter-drone game with a cutting-edge missile that's ITAR-free, and the latest specs for the CM-70 counter-unmanned aerial system missile are out now. The updated design boasts impressive stats, including a 3.5 km range, 900 km/h speed, and a 3 kg mass, making it a top contender to take down Group I to III drone threats.
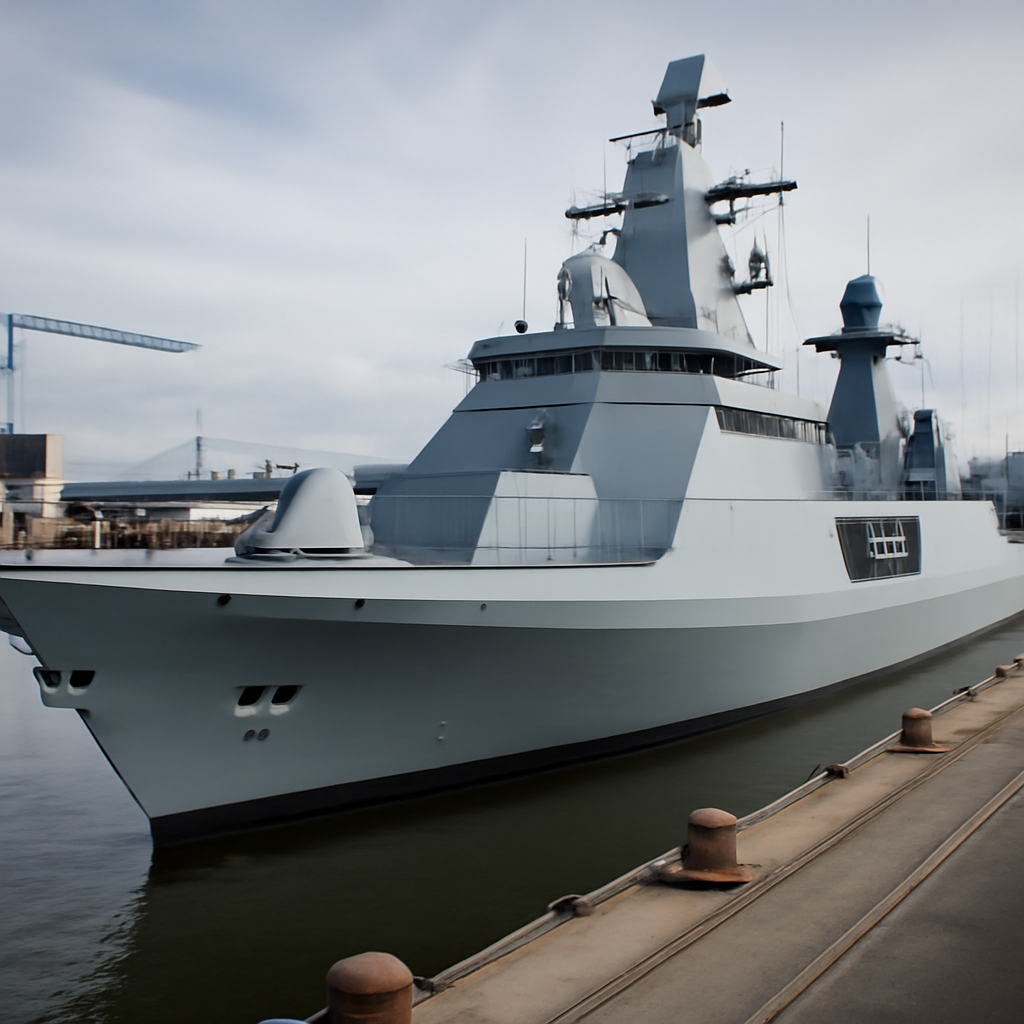
Rheinmetall Unveils Advanced Guided-Missile Frigate
Meet the GMF 140, Rheinmetall's latest game-changing guided-missile frigate, packed with cutting-edge tech, including a powerful radar system, hypersonic weapons, and 64 vertical launch cells. This sleek 140-meter vessel is designed to dominate the seas with advanced air and ballistic missile defense, anti-submarine warfare, and long-range strike capabilities.
US Treasury Sanctions VPN Service Over Ransomware Support
The US Treasury has cracked down on a VPN service that helped ransomware groups hide their tracks, announcing sanctions against First VPN Service and its Ukrainian administrator, Dmytro Rashevskyi. This move follows a multi-jurisdictional law enforcement operation that dismantled the service in May 2026.
China-Aligned Hackers Exploit Roundcube Flaws at Universities
China-aligned hackers are exploiting vulnerabilities in Roundcube email servers to gain access to sensitive university networks, specifically targeting physics and engineering departments with national security ties. They've cleverly designed their attacks to fly under the radar, using tactics like compromised senders and spoofed domains to reach their targets.
Cisco Confirms Active Exploitation of Unified CM Flaw
Over 200 Cisco Unified Communications Manager instances are vulnerable to a remotely exploitable flaw, CVE-2026-20230, which allows low-complexity server-side request forgery attacks with a simple crafted HTTP request. This critical vulnerability puts widely used IP telephony systems at risk, particularly in Asia and North America.
Kubota Discloses Month-Long Network Breach Exposing Sensitive Employee Data
Kubota North America Corporation revealed a concerning network breach that lasted a month, exposing sensitive personal data of employees and their dependents to unauthorized access. The incident, which occurred between March 16 and April 20, has prompted the company to implement enhanced security measures to prevent future breaches.
Nintendo Data Breach Exposes Employee Survey Information
Nintendo of America recently experienced a data breach through a third-party survey service, exposing limited employee survey information, but fortunately, no customer or financial data was compromised. The company is working to resolve the issue and has confirmed that its own systems remain secure.
China-linked UNC6508 Targets Medical Research Institutions
A sophisticated cyber threat group linked to China, known as UNC6508, has launched a targeted attack on medical research institutions in North America, exploiting vulnerabilities in REDCap servers to gain a foothold. The intrusions, which began in September 2023, aim to compromise sensitive research data.
Chinese Spies Exploit Medical, Military Networks for Over a Year
Google's Threat Intelligence Group uncovered a sneaky espionage campaign by Chinese spies that infiltrated medical and military networks in North America for over a year, making off with a treasure trove of sensitive data. The group, tracked as UNC6508, targeted top medical providers, academic centers, and military organizations, leaving no stone unturned in their quest for classified information.
Ransomware Disrupts Illinois High School, Wales Education Sector
A ransomware attack has forced Evanston Township High School in Illinois to shut down until at least Wednesday, canceling summer school, sports camps, and on-campus activities. The school has activated its incident response procedures and is working with cyber experts to investigate and recover from the breach.

Microsoft Exchange Online Disrupts Email Services Across North America, Germany
Microsoft Exchange Online is currently experiencing a widespread outage, causing significant delays in sending and receiving emails across North America and Germany, with some messages remaining undelivered for over an hour. The issue was detected at 10:33 a.m. EDT and is being actively investigated by the company.

Google Exposes BlackFile Extortion Operation's Tactics
Google's Threat Intelligence Group just exposed the clever tactics of the notorious BlackFile extortion operation, revealing how they use voice phishing and sneaky tech tricks to swindle dozens of organizations worldwide. Their clever scheme starts with a simple phone call, where fake IT helpers trick victims into spilling their secrets.