Tag: network security
208 articles
Check Point Flaw Enables Hackers to Execute Code with Root Privileges
A critical flaw in Check Point's Security Management Server has been discovered, leaving all deployments vulnerable to hackers who can exploit it to execute code with root privileges, putting the entire firewall estate at risk. This severe vulnerability, tracked as CVE-2026-91843, requires immediate attention with Check Point releasing security updates to fix the issue.
Security Teams Struggle to Connect Dots in Cross-Environment Attacks
Attacks are getting more complex, with 43% of incidents spreading across four or more environments - and in some cases, as many as eight. Security teams struggle to piece together these cross-environment attacks, making it crucial to connect the dots between disparate signals.
Cisco Discloses Second Actively Exploited Zero-Day Vulnerability
Cisco has disclosed a second actively exploited zero-day vulnerability, CVE-2026-76460, a maximum-severity flaw in its Identity Services Engine (ISE) that lets attackers bypass authentication and take full control of affected devices. This vulnerability is particularly alarming because it allows hackers to modify network access policies, extract sensitive credentials, and move undetected across the network.
Check Point Flaw Lets Unauthenticated Users Execute Code as Root
A critical flaw in Check Point's Security Management and Log Servers, rated 9.8 out of 10, allows unauthenticated users to execute code as root via a simple login request with a very long username. Fortunately, there's no evidence that this vulnerability has been exploited in the wild - yet.
Cisco Discloses Active Exploitation of ISE Flaw
Cisco warns that a critical API vulnerability, CVE-2026-76460, is under active exploitation, allowing attackers to bypass security and gain unauthorized access to devices with a simple crafted request. This maximum-severity flaw scores a perfect 10.0 on the CVSS scale, making it a high-risk threat that demands immediate attention.
Cisco Discloses Actively Exploited Zero-Day in Identity Services Engine
Cisco has sounded the alarm on a critical zero-day flaw in its Identity Services Engine that's being actively exploited by attackers, allowing them to bypass authentication and gain unauthorized access. To stay safe, customers are urged to upgrade to a patched version ASAP.
Space Development Agency Delays Orbital Mesh Network Rollout
The Space Development Agency's highly anticipated Orbital Mesh Network rollout has hit a significant snag, with delays now stretching to at least a year, according to SDA director G.P. Sandhoo. The agency's timeline has slipped from a mere three months behind to a substantial 12-month delay.
Cisco Discloses Actively Exploited Zero-Day in Email Gateways
A critical zero-day vulnerability, CVE-2026-76461, is under active exploitation, allowing hackers to remotely execute commands as root on Cisco Secure Email Gateway appliances with just a simple email. This gaping security hole gives attackers total control of the gateway, putting your email security at risk.
Fraudulent Hires Evade Detection, Gain Network Access Before Exposure
Imagine getting hired, passing background checks, and receiving your official login credentials - all without being who you claim to be. Once inside, malicious hires can wreak havoc for days, with the average fraudulent employee enjoying 5.73 days of unrestricted access to sensitive corporate networks.
Defense Cyber Spending Poised to Double by 2031
Get ready for a surge in defense cyber spending - it's expected to nearly double from $14.99 billion in 2026 to a whopping $28.75 billion by 2031. This dramatic growth is driven by increasing threats, a reliance on connected tech, and a new focus on cyber warfare capabilities.

Cisco FMC Exploits Fuel Ransomware, Credential Theft
Cisco is urging customers to apply hotfixes immediately to protect against ransomware and credential theft attacks exploiting vulnerabilities in its Secure Firewall Management Center (FMC) software. The company has already released patches for the affected versions and plans to roll out additional security updates soon.
Check Point Discloses High-Severity VPN Certificate Flaws Enabling Unauthenticated RCE
Check Point has uncovered two critical vulnerabilities in VPN certificates that could let hackers run code remotely without authentication, posing a huge threat to security. The flaws, with a near-perfect CVSS score of 9.8, affect various Check Point products, including Security Gateways, Security Management Server, and Spark Firewall.
Ransomware gangs exploit WatchGuard firewall flaw
Ransomware gangs are exploiting a critical vulnerability in WatchGuard Firebox firewalls, allowing them to execute malicious code remotely with ease. This flaw, known as CVE-2025-14733, affects various Fireware OS versions and could leave your network exposed to low-complexity attacks.
Cisco Secure FMC Flaw Exploited in Active Attacks
Hackers are actively exploiting a critical vulnerability in Cisco Secure Firewall Management Center (FMC) software, allowing them to bypass authentication and gain root access to vulnerable devices. This severe flaw, rated 10.0 on the CVSS scale, lets attackers execute scripts and commands remotely without logging in.
Cisco Discloses IOS XR Flaws, Urges Immediate Software Updates
Cisco is urging immediate action to protect against two critical vulnerabilities in its IOS XR operating system, with CVSS scores of 9.8 that could allow hackers to wreak havoc on your network. Update your software now to prevent potential security breaches!
Attackers Exploit Zero-Days in SonicWall SMA 1000 Appliances
SonicWall's SMA 1000 appliances are under attack, thanks to two newly disclosed zero-day vulnerabilities - CVE-2026-83548 and CVE-2026-83549 - that can be chained together for a complete network compromise. Attackers are already exploiting these flaws in the wild, prompting urgent patching advice from the vendor and cybersecurity authorities.
HPE Fixes Remote Code Execution Flaw in ArubaOS-CX
HPE has patched a critical flaw in ArubaOS-CX that could let hackers run malicious code with elevated privileges - and all they need to do is send specially crafted packets to an affected device. This remote code execution vulnerability, tracked as CVE-2026-73749, is a serious threat that demands immediate attention.
Cisco Discloses Critical Flaw in Nexus 9000 Switches
Cisco has uncovered a critical flaw in its Nexus 9000 switches, known as CVE-2026-20212, which could allow an unauthenticated attacker to remotely execute code as root. This vulnerability affects 10 specific models and has already been patched by the company.
SonicWall Zero-Days Exploited in Wild, Firm Urges Immediate Patching
SonicWall is urging immediate patching for two zero-day vulnerabilities in its SMA1000 appliances, which are being actively exploited in the wild by hackers. The more critical flaw, CVE-2026-83548, has a severity rating of 10.0 and can be triggered without authentication, putting sensitive data at risk.
BGP Hijack Targets Softaculous Traffic, Delivers Malware
In a shocking 33-hour heist, a BGP hijack diverted traffic meant for Softaculous, delivering malware to unsuspecting users via a valid TLS certificate issued to the attacker. The clever hack exploited a weakness in internet routing, allowing the attacker to intercept and compromise Virtualizor installations.
Ubiquiti Patches Three Maximum-Severity Flaws in UniFi Line
Ubiquiti has patched three critical vulnerabilities in its UniFi line, with a severity score of 10 out of 10, that could allow hackers to gain control of affected devices. These flaws, along with 19 others, were disclosed in a security bulletin, highlighting the need for immediate updates.
Army Seeks Digital Twin to Bolster Network Security, AI Training
The Army is on a mission to supercharge its network security and AI training by building a comprehensive digital twin of its networks - a virtual replica that will allow humans and AI to team up and defend against a staggering 1.2 million daily cyber attacks. This ambitious project will create a realistic, constantly updated training environment where operators can test and harden their defenses.
Cisco Bug Severity Scores Spark Urgent Patching Calls
Cisco's bug severity scores are sounding alarm bells, with warnings rated as high as 10 out of 10 - a perfect score that's more commonly associated with Olympic gymnastics! It's time to take urgent action and patch those bugs ASAP.
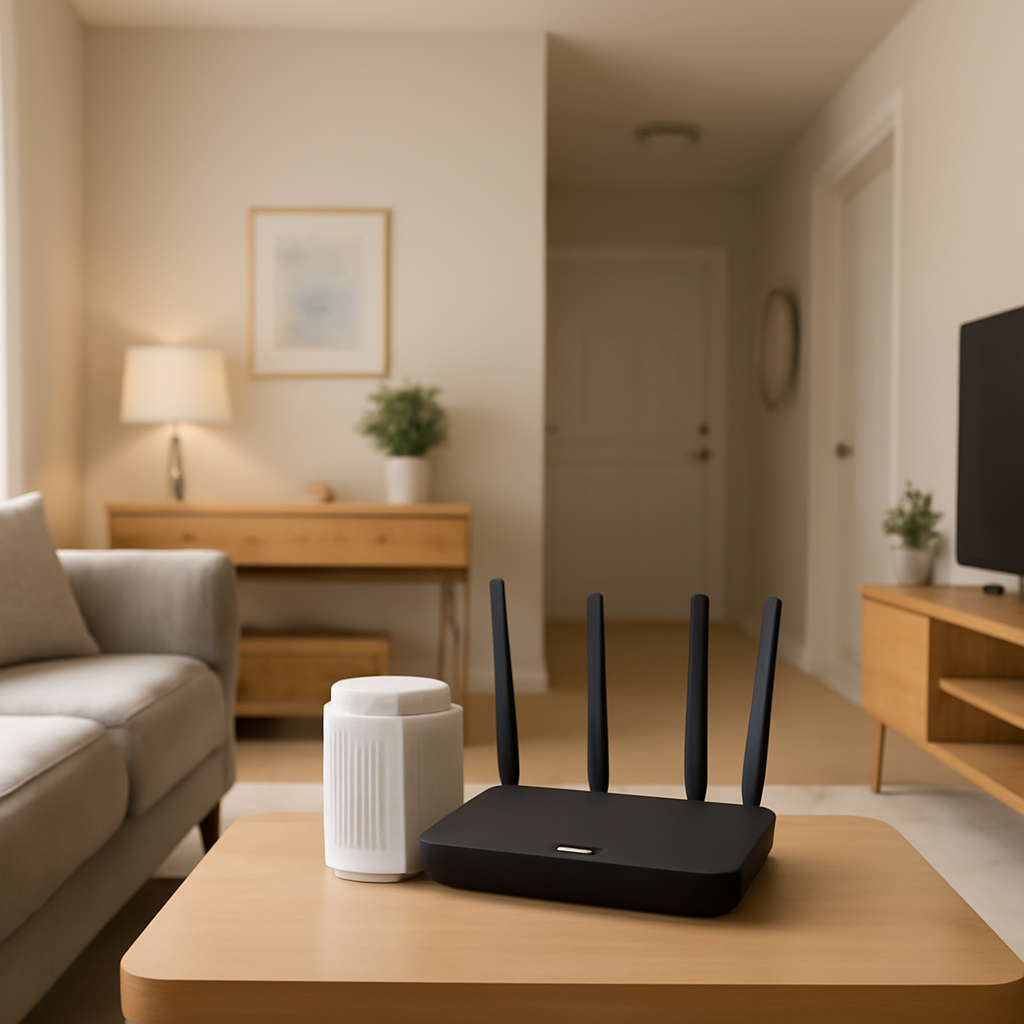
Comcast Bolsters Wi-Fi Motion Detector with Enhanced Security Features
Meet Xfinity Shield, a powerful security bundle that combines WiFi Motion, a cutting-edge motion detection feature, with robust cybersecurity protections from your Xfinity Gateway router, giving you an added layer of home security awareness. This innovative tool detects movement without recording video or capturing images, providing a discreet and effective way to keep your home and family safe.