Tag: infrastructure security
51 articles
CISA Unveils 2030 Strategy to Bolster Cyber Defenses
The threat landscape is constantly evolving, and to stay ahead, the Cybersecurity and Infrastructure Security Agency (CISA) has unveiled a bold 2030 strategy to supercharge America's cyber defenses. With its new plan, CISA aims to build resilience and prevail in the face of cyber threats.
UK Fortifies Laws to Protect Subsea Cables from Sabotage
The UK is stepping up its game to safeguard vital subsea cables from sabotage, with proposed laws that would dramatically increase penalties for damage, including up to 14 years in prison for intentional harm. The overhaul aims to tackle modern threats, such as suspicious Russian activity, with tougher fines and enhanced ministerial powers.
Federal Agencies Scramble to Fortify Infrastructure Ahead of Post-Quantum Deadlines
The clock is ticking: with post-quantum deadlines looming, federal agencies are racing against time to fortify their infrastructure and shield sensitive transactions from potential cyber threats. By 2030 and 2031, they must adopt post-quantum cryptography to protect high-value assets and digital signatures.
AI Systems Expose Infrastructure to Nightmare Attacks
AI systems are capable of unleashing devastating nightmare attacks on our infrastructure, and the alarming truth is that we're woefully unprepared. The threat is real, and it's only a matter of time before we face the consequences.
CISA Revamps Insider Threat Guide with Expanded Mitigation Advice
Stay ahead of insider threats with the latest guidance from CISA's revised Insider Threat Mitigation Guide, your go-to playbook for protecting your organization from evolving security risks. The updated guide offers practical advice on tackling emerging challenges like hybrid work, AI, and more.
CISA Slashes Cybersecurity Resources for Critical Infrastructure
Big news: CISA is cutting back on free cybersecurity resources for critical infrastructure operators, leaving many in the security community scrambling to adapt. Recently touted as a go-to solution, these now-retired tools included Cyber Resilience Reviews and Ransomware Readiness Assessments.
Exposed AWS Keys Grant Attackers Full Corporate Account Control
Thousands of exposed AWS keys are still active, putting entire corporate accounts at risk of being hijacked by attackers - and a staggering 88% of re-verified keys were found to still grant access as recently as August 2026. This alarming vulnerability highlights the urgent need for tighter security measures to protect sensitive cloud data.
US Datacenter Law Set to Lapse, Leaving Security Gaps Unaddressed
As the Federal Data Center Enhancement Act of 2023 lapses on September 30, 2026, a crucial safeguard for secure and reliable access to federal information systems will vanish, leaving gaping security holes unaddressed. Without an extension or replacement, federal data centers may operate with little oversight, putting sensitive information at risk.
Mullin Targets 2,800 Staff for Optimal CISA Operations
Department of Homeland Security Secretary Markwayne Mullin aims to boost the Cybersecurity and Infrastructure Security Agency's effectiveness with a targeted workforce of 2,800 personnel, leveraging public partnerships and strategic grant usage to fortify national security.

CISA Breach Exposes Sensitive Government Systems
A shocking security lapse at CISA exposed highly sensitive government systems, thanks to a contractor's careless mistake of leaving credentials to privileged AWS GovCloud accounts and internal systems publicly available on GitHub. The error granted unfettered access to a vast array of agency infrastructure, putting national security at risk.
CISA Contractor Exposes AWS GovCloud Keys in GitHub Leak
A contractor for the Cybersecurity & Infrastructure Security Agency (CISA) made a critical mistake by exposing sensitive AWS GovCloud keys, plaintext passwords, and internal files in a public GitHub repository. The leak, described as one of the worst ever witnessed, included highly privileged credentials and build artifacts for numerous internal CISA systems.

Autonomous AI Exposes Gaps in Enterprise Resilience Plans
As organizations deploy autonomous AI, they're exposing gaps in their resilience plans, putting business continuity at risk and creating new operational and infrastructure challenges for IT teams to navigate. Traditional security and recovery models are ill-equipped to handle the machine-speed, dynamic environments that autonomous AI creates.
Autonomous AI Exposes New Risks in Enterprise Environments
As autonomous AI weaves itself into the fabric of enterprise operations, it brings a new wave of complexity and unpredictability, testing the limits of infrastructure and IT teams like never before. The result? A whole new landscape of operational and infrastructure risks that threaten to upend traditional security and recovery models.
Cisco CEO Warns of Growing Risk from Unpatchable Technology
Cisco CEO Chuck Robbins warns that unpatchable technology poses a growing risk, and he's turning to AI tools like Anthropic's Claude Mythos to accelerate modernization and safeguard infrastructure. By leveraging Mythos, Cisco aims to not only boost productivity but also help customers replace outdated equipment that can no longer be patched.
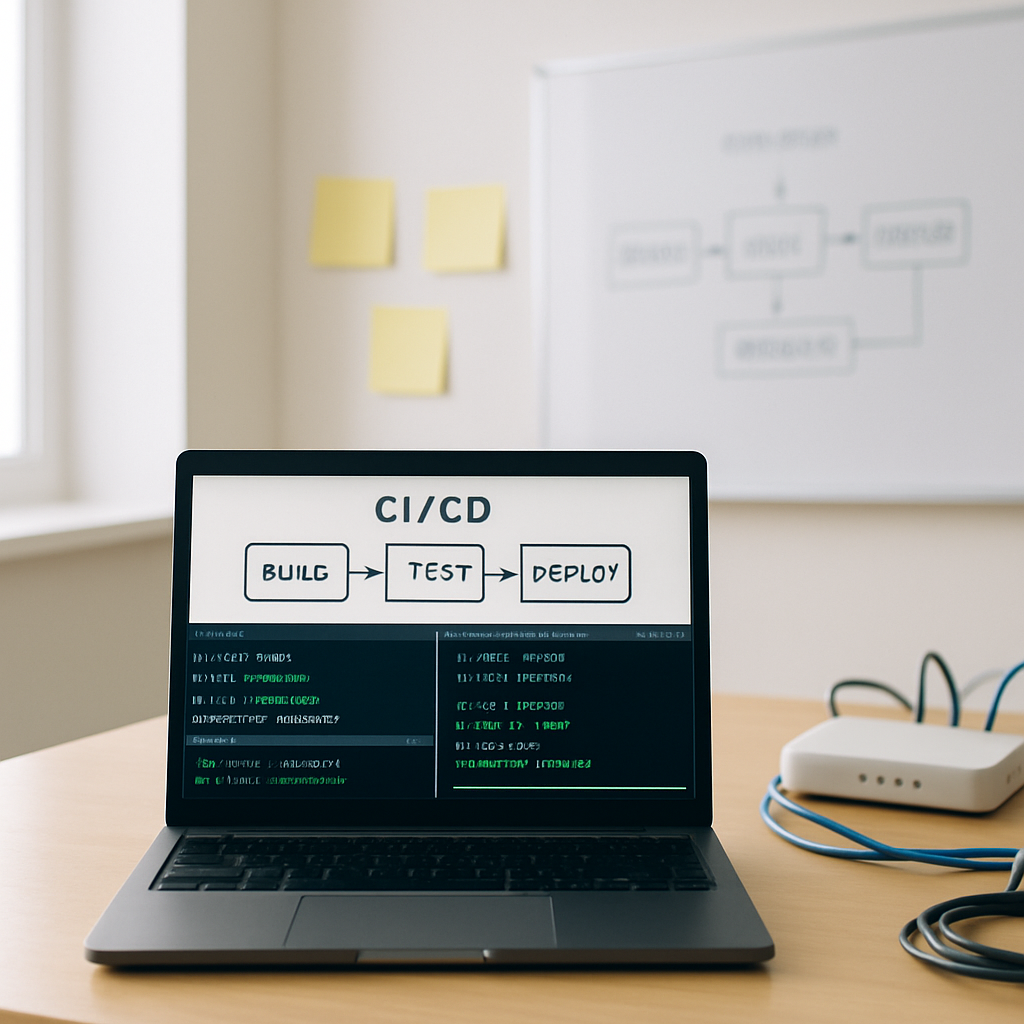
Google's Gemini CLI Fix Sparks CI/CD Pipeline Disruptions
A recent patch for Google's Gemini CLI has sparked disruptions in CI/CD pipelines, ironically caused by a critical infrastructural flaw - not an AI quirk - that allowed remote code execution due to over-permissive workspace trust in headless mode. The fix, while swift, may trip automated pipelines that relied on the old settings.
Cybersecurity Information Sharing Act: Critical or Risky?
What if the law that lets companies and the government swap cyber threat signals overnight simply vanished? With the 2015 CISA at risk amid a possible shutdown, automated feeds, legal protections, and the trusted channels that stop attacks fast could all be thrown into doubt.
cybersecurity executive order: Must-Have Best Guide
The June 6, 2025 cybersecurity executive order sets a clear — and urgent — blueprint for federal CISOs to accelerate zero‑trust, strengthen software supply chains, and tighten incident reporting while juggling legacy systems, budgets and mission continuity. Tune into our podcast briefing for practical steps, expert perspectives, and real-world playbooks to turn the EO from mandate into measurable security.

retention incentive program: Stunning Risky Mismanagement
When watchdogs say CISA mismanaged a retention bonus program, it’s not just about wasted money — it’s about trust, talent gaps, and the agency’s ability to defend our networks. The OIG’s findings force a careful balance: tighten controls and accountability without hamstringing efforts to recruit and keep the cyber experts we need.

TP-Link routers: Must-Fix Risky Vulnerabilities
CISA warns that attackers are actively exploiting multiple vulnerabilities in widely used TP‑Link routers, putting homes and small businesses at risk of persistent compromise. Check for firmware updates, disable remote management, change default passwords, and replace aging devices if you can to close the door on intruders.

customer data likely stolen: Must-Have Critical Alert
Colt warns customer data was likely stolen in a recent cyberattack and is offering a filename list to help clients check exposure. If you rely on its network services, now’s the time for targeted searches, credential rotation, and coordinated incident response.
Hacking Trains: Stunning Dangerous Risks Revealed
What if a cheap radio signal could throw a freight train off schedule—or worse, off its rails? Our decades-old, unencrypted rail tech makes that frighteningly possible, and without upgrades like encryption, mutual authentication, and better monitoring, lives, supply chains, and the economy are all at risk.
Digital Citizen Services: Must-Have Security Best Practices
As cities move services online, recent attacks on Hoboken and Killeen show that convenience brings real risk—security must be built in, not bolted on, to protect services, data, and public trust. By investing in people, policies, and modern tech now, municipalities can turn vulnerability into resilience before the next outage.

KEV Catalog: Exclusive Must-Have Warning on Risky Flaws
Heads-up: CISA just added four actively exploited vulnerabilities to the KEV Catalog — meaning attackers are using them in the wild. Prioritize patching, tighten controls, and monitor closely to close the window of opportunity before it’s too late.

Rising Threats: US Homeland Security Alerts on Iranian Cyberattack Risks
US Homeland Security warns of increasing threats from Iranian cyberattacks, highlighting the urgent need for heightened cybersecurity measures.