Tag: emerging threats
8169 articles
Microsoft Delivers Record 974 Patches, Warns of Zero-Day Exploits
Microsoft just dropped a record 974 patches, including fixes for two vulnerabilities already being exploited as zero-days, forcing companies to scramble to keep up. This massive update is a stark reminder to stay vigilant, with experts warning of a vulnerability apocalypse.
OpenAI's ChatGPT Exposes Covert Data-Stealing Channel
Security researchers just uncovered a sneaky data-stealing vulnerability in ChatGPT, allowing hackers to secretly send instructions and swipe sensitive info from other users' accounts without leaving a digital trail. Fortunately, the issue was quickly reported to OpenAI and the affected system was swiftly shut down.
EU Cyber Resilience Act Spurs Rush to Track Software Vulnerabilities
Get ready for a new era of cyber transparency: by September 11, 2026, EU manufacturers with digital products must report vulnerabilities to ENISA within 24 hours of discovery, and provide a detailed report within 72 hours. This mandate is just the beginning, with stricter engineering requirements kicking in on December 11, 2027.
DoppelCart Network Exposes 119,000 Fake Shops Stealing Credit Cards
A massive network of 119,000 fake online shops, dubbed DoppelCart, has been uncovered, stealing credit card info and personal data on a huge scale. This enormous operation dwarfs previous scams, with over 105,000 of the shops still active and snaring unsuspecting victims.
Hackers Deploy Linux Rootkit via F5 BIG-IP Flaw
Hackers are exploiting a critical F5 BIG-IP flaw, known as CVE-2025-53521, to deploy a sneaky Linux rootkit that allows them to execute code on vulnerable servers. This alarming attack vector has already exposed 795 endpoints online, putting countless systems at risk.
Microsoft Bolsters Windows 10 with KB5122878 Security Update
Microsoft just dropped a major security update, KB5122878, for Windows 10, packing fixes for a whopping 966 vulnerabilities across its products - a must-install for anyone on long-term servicing and paid support tracks! If you're running Windows 10 Enterprise LTSC or part of the ESU program, you can easily grab the update through Windows Update.
Microsoft Patch Tuesday Disables Record 966 Flaws, Zero-Day Exploits
Microsoft just dropped a massive Patch Tuesday update, fixing a record-shattering 966 vulnerabilities, including two zero-day exploits that hackers are actively using to cause trouble. This September 2026 update is a big deal, with the most flaws patched in a single update ever.
Microsoft Releases Urgent Windows 11 Updates to Fix Security Flaws
Microsoft just dropped urgent updates for Windows 11, releasing KB5124008 and KB5122880 to squash security flaws, fix bugs, and add some exciting new features. These cumulative updates are specifically designed for Windows 11 versions 25H2/24H2 and 23H2.
ShinyHunters Breaches Florida DMV Database
A massive data breach has hit the Florida DMV, with hackers allegedly stealing over 200,000 driver records from the state's database after exploiting a password-reset flaw. The breach, which began on September 3rd, has been claimed by the notorious extortion gang ShinyHunters, who are now threatening to release the sensitive information unless they're paid.
OpenAI Investigates ChatGPT Outage Disrupting Image Generation
OpenAI is currently investigating a frustrating outage that's disrupting ChatGPT's image generation capabilities, leaving users unable to upload files or generate images. The issue, tied to a recent internal change, is causing a spike in errors and hangs for hundreds of users.
Data Breaches Expose Vulnerable Supply Chains
Recent data breaches at the Pokémon Center, McKesson, and other major players in freight, retail, airports, finance, and healthcare reveal a disturbing trend: third-party vulnerabilities and social engineering are leaving supply chains exposed. A staggering 284 million records were allegedly stolen, highlighting the urgent need for stronger security measures.
Slim Spider Targets Brazilian Finance with Cloud Credential Heists
Meet Slim Spider, a cunning cyber threat actor with a laser-like focus on Brazilian finance, expertly infiltrating cloud environments to steal sensitive credentials and target cryptocurrency assets and instant payment accounts. With a sophisticated grasp of Brazil's financial infrastructure, this adversary has been wreaking havoc on the country's financial sector since at least March 2026.
Boston Scientific Revises Outlook as Cyberattack Disrupts Operations
Boston Scientific's operations have been significantly disrupted by a cyberattack, forcing the company to revise its financial outlook and warning investors of a potential material impact on its third-quarter and full-year results. The incident, detected on August 25, has left the company's net sales growth and earnings guidance in jeopardy.
Threat Actors Exploit AI for Large-Scale Credential Harvesting
Threat actors are supercharging their attacks with AI, using it to scale up credential harvesting and launch more sophisticated campaigns. Google Threat Intelligence Group reports that financially motivated and espionage-focused attackers are increasingly turning to AI to target high-value sectors like healthcare, government, and media.
Utilities Face Unseen Network Threats
The water and wastewater sector is under attack, with over 100 compromised systems identified in July alone, often due to vulnerable controllers linked directly to cellular modems. This alarming trend has prompted joint warnings from CISA, the FBI, and the EPA, highlighting the urgent need for utilities to bolster their network defenses.
ChatGPT Exposes Gmail Data to Hidden Channel
Researchers at Check Point found that a sneaky instruction in a ChatGPT conversation can secretly siphon off sensitive data from connected Gmail accounts, sending it to an attacker's hidden channel without raising any red flags. This covert hack can even exfiltrate chat history and files, putting users' private info at risk.
Videoconferencing Security Evolves into Mission-Critical Priority
Security has taken center stage in the world of videoconferencing, with 31% of businesses now prioritizing it over price and quality when selecting collaboration products. Top security concerns include cyberattacks, device compliance, and risky employee behavior.
US Air Force Accelerates Innovation with Modernization-as-a-Service
Meet the Kessel Run team, the US Air Force's elite unit tasked with delivering cutting-edge operational air power to protect and defend the nation. Led by Col. Richard Lopez, this innovative team is revolutionizing the way the Air Force approaches modernization with a bold, modern approach.
CISA Slashes Cybersecurity Resources for Critical Infrastructure
Big news: CISA is cutting back on free cybersecurity resources for critical infrastructure operators, leaving many in the security community scrambling to adapt. Recently touted as a go-to solution, these now-retired tools included Cyber Resilience Reviews and Ransomware Readiness Assessments.
Hackers Return $265M in Bitcoin, Hold $47M in Dispute
In a surprise move, hackers claiming to be "whitehats" returned a whopping 3,400 bitcoin, valued at $265 million, to the Liquid Federation, leaving $47 million still in dispute. The mysterious intruders made their move on September 7, sending the funds back after a daring heist that stole nearly 4,000 bitcoin from the Liquid Network.
Microsoft Updates Trigger Errors on Windows Server 2016 Systems
If you've installed the August 2026 Windows security update on your Windows Server 2016 system, you might be experiencing recurring application errors due to a compatibility issue with the CompatTelRunner.exe process. This error can occur when the Compatibility Appraiser diagnostic service is enabled, causing frustrating Application Error events with Event ID 1000.
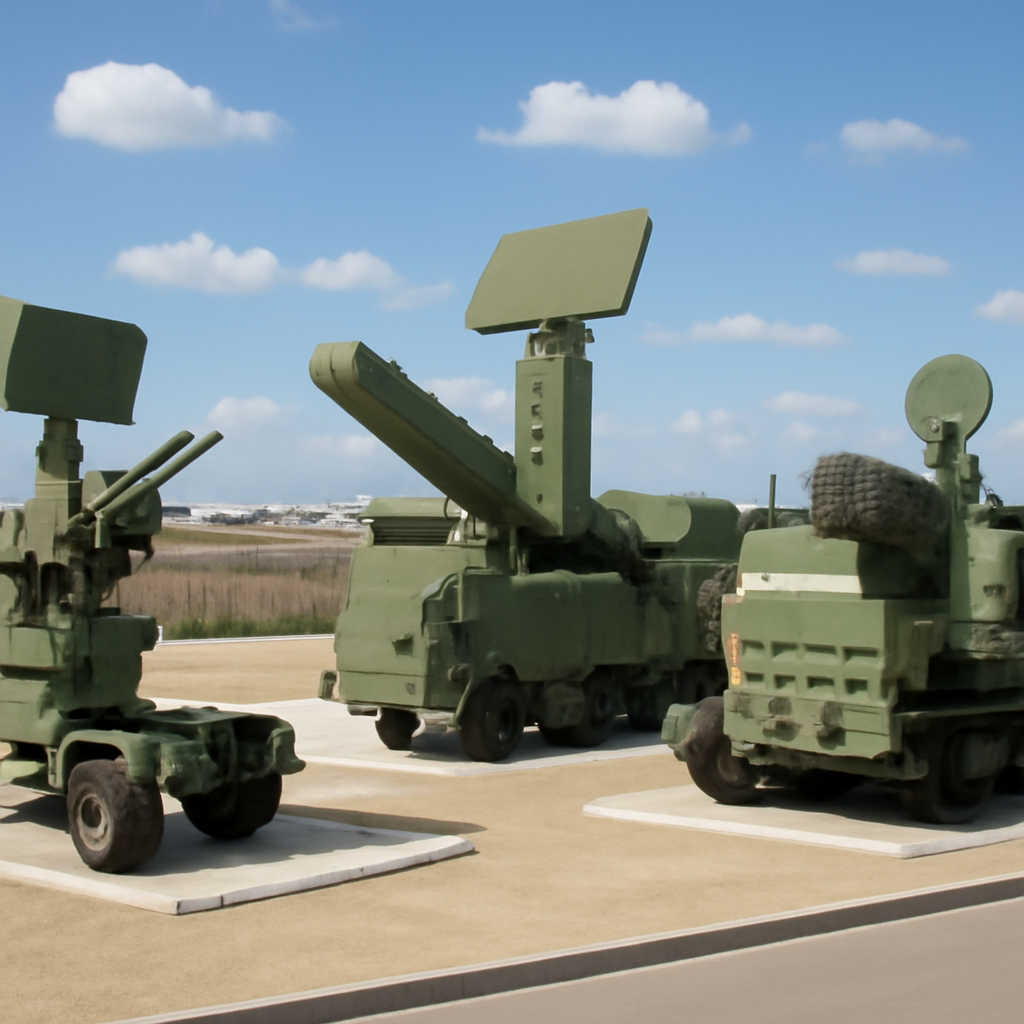
Pakistan Air Force Bolsters Defenses with Advanced SHORADS Systems
The Pakistan Air Force has taken a significant leap in its defense capabilities by introducing cutting-edge short-range air defence systems, including the CASIC HQ-17AE, NORINCO LD-76, Aselsan Korkut, and Aselsan ŞAHİN. These advanced systems will bolster the PAF's point-defence layer, enhancing its ability to counter threats from drones, rockets, helicopters, and precision-guided munitions.
Researchers Exploit AI Encryption to Steal Proprietary Model Traces
Researchers have made a shocking discovery: they can exploit AI encryption to steal sensitive information, including personal data and login credentials, by decoding encrypted "chain-of-thought" blocks scraped from public repositories. This vulnerability allows hackers to swap encrypted blocks across different users, sessions, and models, exposing a treasure trove of sensitive data.
SAP Discloses Maximum-Severity Kernel Vulnerability
Over 10,000 SAP systems are exposed to the public internet, making them vulnerable to a newly disclosed maximum-severity kernel flaw, CVE-2026-44756, that allows attackers to gain admin privileges and take control. This critical vulnerability, dubbed OVERPASS, is a buffer overflow flaw that can be exploited to run arbitrary commands on vulnerable systems.