Tag: emerging threats
8459 articles
Legacy Security Tools Hinder Data Protection Efforts
With data constantly moving across cloud and AI environments, traditional security tools are holding you back from truly protecting your data - it's time for a modern approach. A staggering 72% of security professionals agree that data security is more critical than ever, making an evolution in strategy urgent.

DLP Falters as Data Leakage Shifts to Browser-Based Activities
Traditional data loss prevention methods are struggling to keep up as 46% of sensitive file uploads to web apps are sent to unsanctioned accounts, revealing a significant blind spot in modern DLP systems. This gap is largely due to the rise of browser-based activities, where conventional DLP methods fall short.
Malicious Site Exploits AI Interest to Deploy Beagle Backdoor
Beware of a fake website masquerading as Anthropic's Claude interface, tricking users into downloading a 505 MB ZIP archive that unleashes a new, previously undocumented Windows backdoor called Beagle. This malicious campaign uses a convincing imitation of the legitimate site to spread the infection.
US Crackdown Targets 'Laptop Farms' Aiding North Korea's Illicit IT Schemes
The US has cracked down on "laptop farms" helping North Korea's illicit IT schemes, sentencing two US nationals to 18 months in prison for enabling North Korean IT workers to remotely work at nearly 70 American companies. This move is part of a federal initiative to shut down North Korea's revenue generation schemes.
Palo Alto Networks Discloses Active Exploitation of PAN-OS Flaw Enabling Espionage
Palo Alto Networks has uncovered active exploitation of a high-severity flaw in PAN-OS software, allowing attackers to execute arbitrary code with root privileges and inject shellcode into vulnerable systems. This critical vulnerability, tracked as CVE-2026-0300, enables unauthenticated remote code execution, putting affected appliances at risk of espionage.
Dragos Warns of AI-Powered Cyber-Attack on Mexican Water Utility
A recent cyber attack on a Mexican water utility highlights the growing threat of AI-powered attacks, with commercial AI tools used to identify and breach operational technology infrastructure. The attack, detected by Dragos, shows how easily an adversary can target critical infrastructure with the help of advanced AI tools.
Vulnerabilities Surge as Exploit Kits Expand in Q1 2026
The Q1 2026 report reveals a concerning surge in vulnerabilities and exploit kits, with attackers increasingly targeting Microsoft Office and Windows with new logic-flaw exploits. This quarter saw a notable rise in security-feature bypasses, including CVE-2026-21509 and CVE-2026-21514, which allow specially crafted files to execute commands with user privileges.

Congress Probes Trump Administration's Commercial Spyware Ties
Rep. Summer Lee is raising red flags about the Trump Administration's cozy ties to commercial spyware, specifically its willingness to let US investment flow into sanctioned companies like NSO Group and use their tools to infiltrate cell phones. She's demanding answers from the Commerce Department about its role in these dealings.

AI Exploits Emerge as New Security Threat
As AI use grows, a hidden risk is emerging: malicious inputs can alter model behavior, bypassing safeguards and putting enterprises at risk. This "prompt injection" tactic is like phishing, targeting the link between user and system to wreak havoc.

Crypto Heist Ringleader Gets 6.5 Years for $230 Million Loot
Marlon Ferro, the mastermind behind a brazen crypto heist, has been sentenced to 6.5 years for stealing $230 million in cryptocurrency using a cunning mix of online scams and targeted home invasions. He served as the group's instrument of last resort, carrying out daring residential burglaries to get his hands on valuable digital assets.
Incident Response Readiness Exposes Operational Gaps
Being incident response ready means more than just having a plan - it requires immediate visibility into identity and authentication access, including investigator-level read access to crucial systems. Without this visibility, teams are left making blind containment decisions and piecing together timelines with guesswork.
MicroStealer Targets Education, Telecom with Credential Theft FTC Cracks Down on Kochava's Location Data Practices Proton Mail Adds Quantum-Safe Encryption Supply Chain Hardened with pnpm 11 Release Meta Deploys AI for Underage Enforcement North Korea-Linked Cybercrime Case Upheld ICS Security Flaws Disclosed in Eclipse BaSyx MOVEit Automation Exposes Critical Vulnerability VECT Ransomware Encryption Flaws Discovered Oracle Accelerates Patching with
MicroStealer malware is on the loose, targeting education and telecom sectors with a sneaky credential theft attack that's harvesting sensitive data, including browser credentials, cryptocurrency wallets, and system info. This stealthy threat uses a multi-stage delivery chain to quickly swipe valuable info and send it to hackers.

State-sponsored hackers exploit Palo Alto Networks firewall zero-day
Palo Alto Networks has issued a warning about a critical zero-day vulnerability, CVE-2026-0300, that allows state-sponsored hackers to exploit its firewalls and execute arbitrary code with root privileges. The company is tracking limited exploitation attempts, linked to a cluster of likely state-sponsored threat activity.
Fake Claude AI site delivers Beagle Windows backdoor malware
Beware of a fake Claude AI site that's really a malware trap: a 505MB archive disguised as a legitimate installer delivers a sneaky Windows backdoor called Beagle. Clicking the download button on the site leads to trouble, not the AI tool you might be expecting.
Weak Passwords Expose Networks to Unintended Access
Even a seasoned expert like Roger Grimes, CISO advisor at KnowBe4, has fallen victim to the pitfalls of weak passwords - in a surprising turn of events, he recalling a time when he accidentally gained access to a client's network using the password "rosebud", famously lifted from a film plot.

Daemon Tools Software Trojanized in Supply Chain Attack
Malware was discovered hidden in certain Daemon Tools Lite installers, prompting developer Disc Soft to issue a clean build and confirm a supply chain attack had compromised their system. A malware-free version was released within 12 hours of notification.
PyPI Packages Deliver ZiChatBot Malware via Zulip APIs
Malicious Python packages on PyPI were found to be secretly delivering a new malware called ZiChatBot, which uses Zulip APIs to receive instructions. These seemingly harmless packages covertly dropped malicious components, highlighting the importance of vigilance when downloading code from public repositories.

Phishing Campaigns Exploit Vercel's AI Tools
Scammers are using Vercel's AI tools to create super-realistic phishing sites that mimic popular brands, making it easier for them to trick victims into handing over sensitive info. This clever tactic allows attackers to quickly recreate malicious pages, even if they're taken down.
vm2 Library Vulnerabilities Enable Sandbox Escape and Code Execution
A dozen critical vulnerabilities in the vm2 Node.js library can be exploited by hackers to break free from sandbox restrictions and run malicious code on vulnerable systems. This serious security flaw has been assigned high CVSS scores, emphasizing the urgent need for users to patch their systems.
US Unveils Cyberattacks as Counterterrorism Tool
The US has officially added cyberattacks to its counterterrorism arsenal, vowing to use offensive cyber operations against those who plan to harm Americans or support terrorist plots. This bold move is part of a new strategy that combines diplomatic, financial, and covert actions to disrupt and deter threats to US interests.
Agentic AI Empowers Cyber Criminals with Nation-State Capabilities
The Department of Defense is leveraging agentic AI tools to revolutionize its operations, with Emil Michael reporting that tasks that once took two weeks can now be completed in just three hours, freeing up teams to focus on high-priority work. This game-changing tech has already shown tremendous success since its rollout on the GenAI.mil platform in December.
Palo Alto Networks Discloses Zero-Day Flaw in PAN-OS Software
Palo Alto Networks has issued a warning about a zero-day flaw in its PAN-OS software, tracked as CVE-2026-0300, which allows unauthenticated remote code execution with root privileges. This buffer overflow vulnerability in the User-ID Authentication Portal poses a high risk to PA-Series and VM-Series firewalls.
Australia's Security Architecture Needs Diversity to Counter Complex Threats
Australia's national security ecosystem is drowning in data, but struggling to cut through complexity - and simply adding more information can make things worse, not better. To stay ahead of evolving threats, its security architecture needs a fresh approach that prioritises what matters most.
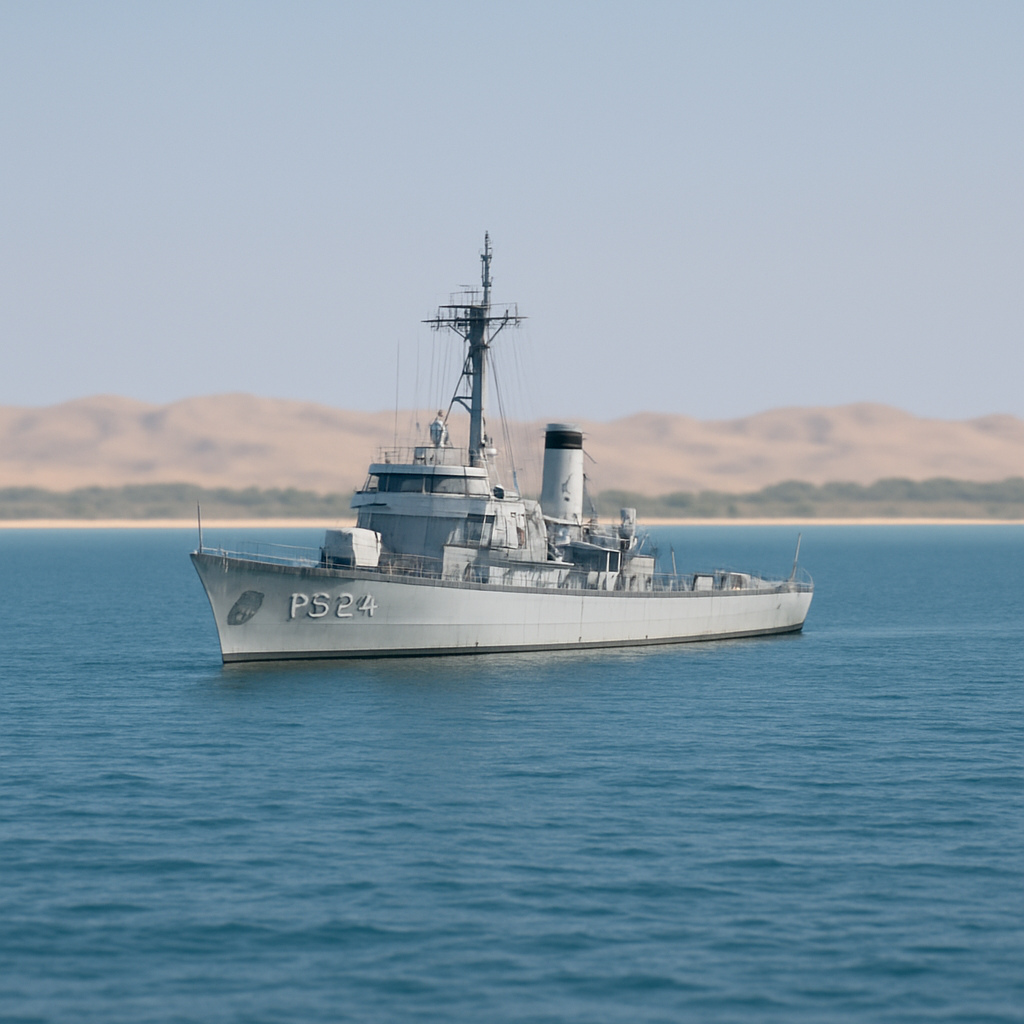
US-Led Drills Target Ship in Strategic Luzon Strait
In a display of military precision, a US-led live-fire exercise sank a decommissioned Philippine Navy patrol corvette, BRP Quezon, in the strategic Luzon Strait, roughly 50 miles offshore. The vessel, a former World War II-era minesweeper, met its target fate near the Paoay Sand Dunes on Luzon's coast.