Tag: emerging threats
8401 articles

OPM Proposes Sweeping NDA Rule for Federal Employees
The Office of Personnel Management wants to shake up the way federal employees handle confidential information, proposing a new nondisclosure agreement rule that would require all employees to sign a pledge protecting internal agency details. If implemented, the rule could have far-reaching implications for whistleblowing and employee accountability.

FortiGuard Labs Exposes Sophisticated Phishing Campaign Targeting Windows Users
Beware of a sneaky phishing campaign that's targeting Windows users with a multi-stage attack chain, starting with a seemingly harmless email attachment that unleashes a powerful malware. This stealthy threat uses clever tactics like process hollowing to inject malicious code into trusted Windows processes.

FBI Warns Law Firms of In-Person Extortion Tactics by Silent Ransom Group
The FBI is sounding the alarm for US law firms, warning them of a growing threat from the Silent Ransom Group, which targets the legal industry for its highly sensitive data and uses in-person extortion tactics. This group has been linked to a string of incidents, and the FBI is urging law firms to be vigilant.

Cybersecurity Burnout Spurs Call for Risk-Based Response
Half of all cyber professionals are burning out weekly or daily - it's time for organizations to shift their approach and view burnout as a critical operational risk, rather than just a wellness issue. By reframing burnout in this way, businesses can prioritize effective solutions and safeguard their cyber resilience.
SOCs Shut Down Incident Risks with Proactive Threat Detection
Stay ahead of incident risks with proactive threat detection from ANY.RUN's Threat Intelligence Feeds, which deliver a continuous stream of high-confidence threat data from a vast network of organizations and SOC professionals. By shrinking the time between detection and understanding, modern Security Operations Centers (SOCs) can effectively shut down threats before they cause harm.

CrowdStrike and Google Disrupt Glassworm Botnet Infrastructure
In a major win for cybersecurity, a powerful collaboration between CrowdStrike, Google, and the Shadowserver Foundation successfully dismantled the Glassworm botnet by simultaneously taking down all four of its command-and-control channels. This bold move cut off the botnet's operators from infected devices, preventing further malicious activity.
India's CERT-In Urges 12-Hour Patch Deadline for Exploited Vulnerabilities
CERT-In is urging organizations to act fast - patch, mitigate, or remove exposure to exploited vulnerabilities within 12 hours for internet-facing and high-priority systems. This strict deadline aims to minimize risk and protect critical assets from potential attacks.
Glassworm botnet disrupted by takedown of resilient C2 infrastructure
In a major win for cybersecurity, researchers from CrowdStrike, Google, and The Shadowserver Foundation have successfully disrupted the Glassworm botnet by dismantling its complex command-and-control infrastructure. This takedown cuts off the lifelines of the threat actors, halting their campaigns that had been ongoing since October 2025.
CrowdStrike Disrupts GlassWorm Malware's Global Supply Chain Attack Infrastructure
In a major win for cybersecurity, CrowdStrike teamed up with Google and the Shadowserver Foundation to dismantle the global infrastructure behind the GlassWorm malware attack, crippling its ability to issue commands or deliver new payloads to infected machines. This coordinated operation targeted and neutralized the malware's command-and-control channels, protecting software developers from further exploitation.

Researchers Warn of LLM Guardrail Vulnerability to Multi-Turn Manipulation
Beware: even the toughest-sounding safety guardrails on large language models can be easily bypassed by clever attackers who use multi-turn conversations to manipulate them. Cisco researchers found that none of the models they tested were completely safe from this type of exploitation.
Fraudsters Target World Cup Fans with 4300 Fake FIFA Domains
Scammers are gearing up to target FIFA World Cup fans with a massive network of over 4,300 fake domains, a recent analysis revealed. These fraudulent sites, linked to six distinct scams and four threat actors, are currently dormant but ready to be activated as the 2026 tournament approaches.

Security Researcher Exploits Flaw in Pretalx Conference Tool
A security researcher recently uncovered a vulnerability in pretalx, a popular conference tool, that could let hackers inject malicious code into an organizer's interface, putting sensitive data at risk. This flaw, known as a stored cross-site scripting vulnerability, could be triggered through simple search queries.

FBI Warns of In-Person Data Theft Attacks by Extortion Gang
The FBI has issued a warning about a sneaky new tactic used by the notorious Silent Ransom Group: showing up in person to steal sensitive data, after gaining trust through clever phishing and phone scams. This brazen approach combines remote access tricks with physical presence at victim sites, marking a chilling evolution in their extortion methods.

Gitea Flaw Exposes Private Container Images to Unauthenticated Attacks
A newly disclosed vulnerability in Gitea, tracked as CVE-2026-27771, allows unauthenticated attackers to access private container images, potentially exposing tens of thousands of deployments worldwide. This flaw lets anyone on the internet pull private images without needing an account, password, or credentials.
CISA Mandates Emergency Patch for Exploited cPanel Plugin Flaw
A critical vulnerability in the LiteSpeed cPanel plugin, known as CVE-2026-48172, is being actively exploited by remote attackers, allowing them to execute arbitrary scripts with root privileges. CISA has issued an emergency patch, giving affected users just four days to update and protect themselves.

UK Firms Bolster Cyber Defenses as AI Risks Mount
As uncertainty becomes the new normal, UK businesses are bolstering their cyber defenses, with 68% of leaders planning to boost cybersecurity investment over the next year. Despite this, many remain vulnerable, with fewer than three in 10 confident in their ability to respond to a major cyber incident.

Dutch Police Apprehends Suspect in Ajax Football Club Hack
Dutch police have arrested a 35-year-old man from Buren for repeatedly hacking into Ajax football club's computer systems, granting himself unauthorized access. The suspect's identity and motives are still under investigation.

Microsoft Warns of AI-Driven Cryptojacking Campaign Targeting High-Performance GPUs
Beware of a sneaky new cryptojacking scam that's using AI chatbots to trick you into downloading malicious software - hackers are now hiding in plain sight, serving up poisoned links in chatbot responses that seem like harmless software recommendations. This cunning tactic is a game-changer for cyber threats, making it even harder to spot danger online.

PureLogs Infostealer Exploits Purchase Order Phishing Lures
Beware of purchase order phishing scams that can deliver a powerful infostealer, capable of stealing sensitive credentials and cryptocurrency keys, via a simple yet cleverly disguised email with a malicious RAR attachment. Even security software can be fooled, as one campaign was only flagged as a threat after it was already sent.

South Korea Advances Nuclear-Powered Submarine Program
South Korea is taking a giant leap in its naval capabilities with the Jang Bogo N Project, a new class of nuclear-powered submarines that will boast functionally unlimited range, higher mobility, and lightning-fast transit times. These game-changing vessels will play a crucial role in defending against threats from North Korea's submarines and more.

Navy Disbands Information Warfare Directorate Amid Organizational Overhaul
The Navy has taken a bold step in modernizing its operations by disbanding its Information Warfare Directorate and reallocating its vital duties across three new directorates, reflecting a fundamental shift in mindset towards recognizing information warfare as a critical domain. This move promises to enhance the Navy's capabilities in intelligence, policy, IT, space, cyber, and programmatic requirements.
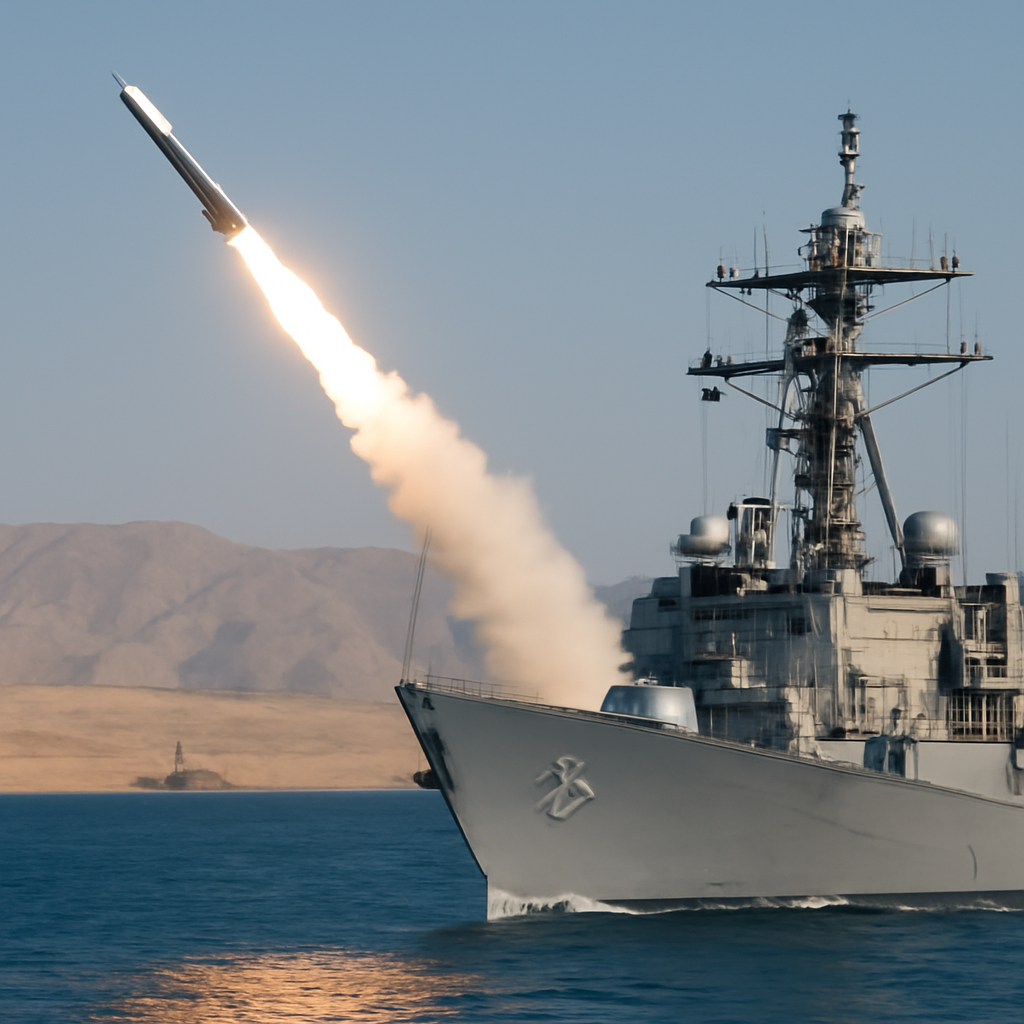
US Strikes Iranian Targets Amid Escalating Strait of Hormuz Tensions
The US has launched a defensive strike on Iranian targets, including missile launch sites and boats attempting to lay mines, in response to escalating tensions in the Strait of Hormuz. Iran's Foreign Ministry has vowed to retaliate, warning that it won't hesitate to defend its territory.

Turkey Bolsters Naval Capabilities with 100 Kamikaze USVs
Turkey is taking its naval capabilities to the next level with a bold move to acquire 100 kamikaze unmanned surface vessels (USVs), a game-changing technology that will significantly boost its military prowess. The ambitious project has been divided among three top Turkish defence teams, ensuring a competitive edge and redundancy in production.
US Carriers Reposition Amid Surge in Global Hotspots
As the global landscape shifts, US carriers are strategically repositioning to stay ahead of the curve, with a notable presence in key hotspots. The US Navy is making its move, with CENTCOM forces having already redirected over 100 commercial vessels and allowed vital aid to pass through.