Tag: emerging threats
8358 articles
Accenture Bolsters Industrial Cybersecurity with $4.18B Acquisition Spree
As Robert M. Lee aptly puts it, our critical infrastructure, from energy and water systems to manufacturing plants, is crying out for robust cybersecurity that can stay one step ahead of evolving threats - and failing to deliver it could have disastrous societal consequences. Accenture is answering the call with a whopping $4.18 billion investment to bolster industrial cybersecurity.
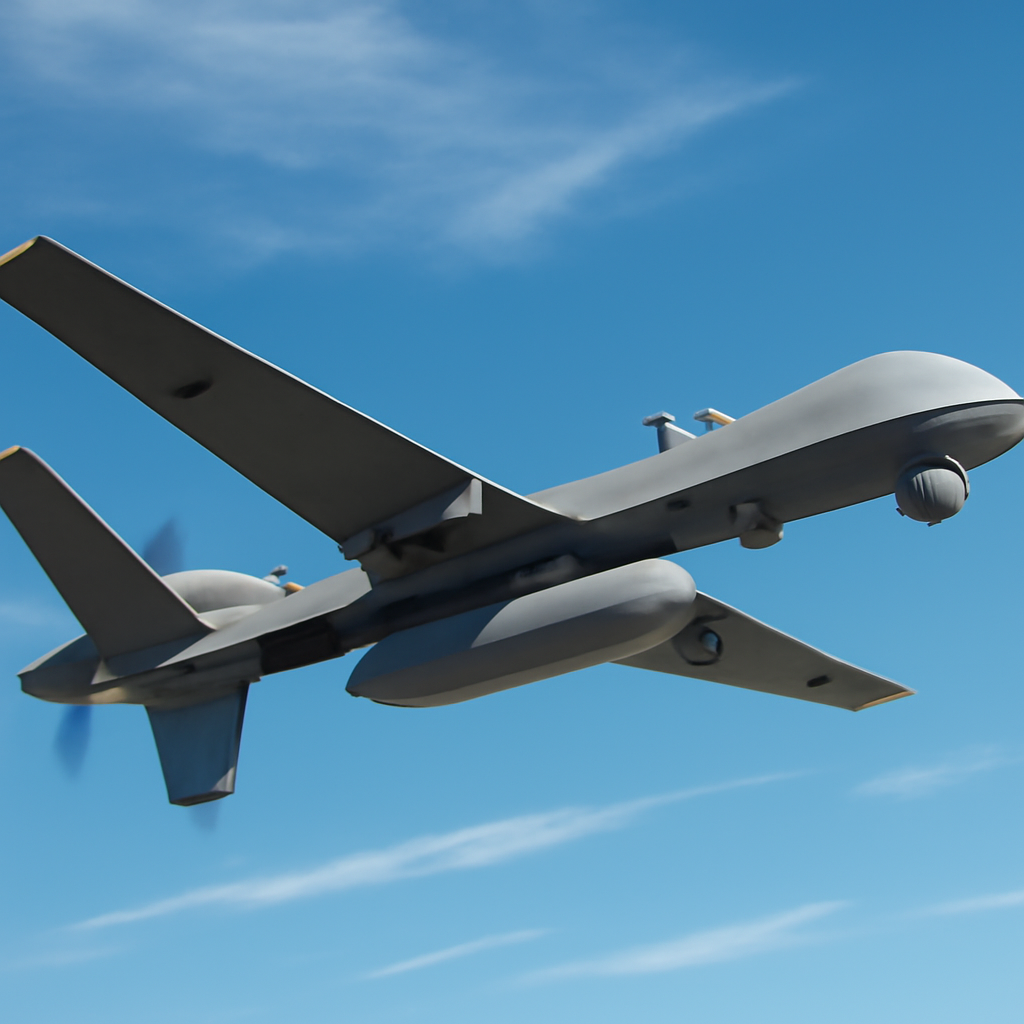
MQ-9 Reaper Gains Airborne Early Warning Radar Capability
The MQ-9 Reaper just took its defensive capabilities to new heights with the successful flight test of an airborne early warning radar pod, giving it critical aloft sensing to detect and defend against a range of threats. This game-changing upgrade was made possible through a partnership with Saab, which supplied the innovative LoyalEye radar system.
NetNut Exposed in Massive Popa Botnet Operation
Meet Popa, a sneaky Android-based plugin that's been secretly infiltrating over 1.4 million internet addresses via unofficial streaming apps and set-top devices, researchers have uncovered. This stealthy operation is linked to the notorious Vo1d botnet family, which has been targeting vulnerable Android TV boxes.
Nintendo Data Breach Exposes Employee Survey Information
Nintendo of America recently experienced a data breach through a third-party survey service, exposing limited employee survey information, but fortunately, no customer or financial data was compromised. The company is working to resolve the issue and has confirmed that its own systems remain secure.
TeamPCP Exploits Open-Source Trust Model in Mass Software Compromise
In a shocking display of cunning, TeamPCP has compromised over 1,000 software packages in under four months, injecting malicious code and redefining the notion of trust in open-source supply chains. This brazen attack has left a trail of destruction, with roughly 500 million weekly downloads affected across major registries like npm, PyPI, and GitHub.
Pentagon Faces New Limits on Equity Stakes in Private Companies
The Senate Armed Services Committee is pushing to give the Office of Strategic Capital explicit authority to take equity stakes in private companies crucial to national security, a move that could reshape the Pentagon's investment landscape. This development could have significant implications for the future of defense innovation and investment.
India Weighs Russian Fighter Jet Offer Amid 5G Aerospace Dilemma
Russia's Vladimir Putin has offered India a game-changing deal: joint production of the cutting-edge SU-57 fifth-generation fighter aircraft, with no strings attached. The proposal comes at a critical time for India's air power ambitions.
Malware Developers Embed Deceptive Code to Evade AI Analysis
Malware developers are getting sneaky, hiding deceptive code in their spyware to throw off AI analysis - and it's working, with one developer adding text about nuclear and biological weapons to their malicious software. This clever trickery tricks AI systems into ignoring the real threat.
Pentagon Bolsters Rare Earth Supply with $1.2 Billion in Loans
The Pentagon is investing $1.2 billion to boost the US rare earth supply, with $725 million going to Energy Fuels and $500 million to Phoenix Tailings to enhance domestic processing and magnet production. This significant move aims to strengthen America's foothold in the critical rare earths sector.
Cyber Trust Erodes as AI, Tools Enable New Attacks
Trust is crumbling in the digital world as hackers exploit AI and tools to launch devastating attacks, turning trusted platforms into malware delivery mechanisms. The latest threat: hijacked Google Ads and AI developer tools used to funnel over 2,000 victims to malicious download pages.
Chinese Hackers Infiltrate Defense Research with Custom Malware
Chinese hackers have launched a stealthy attack on defense research using custom malware, embedding it into upgrade workflows so it survives even when vulnerabilities are patched. This allows the malware to re-infect new versions, making it a persistent and concerning threat.
Malware Spreads via USB, Targets Crypto Wallets with Clipboard Theft
Beware of a sneaky malware that's spreading through USB drives and targeting crypto wallets by stealing sensitive info from your clipboard every half a second. This cunning threat replaces wallet addresses, harvests seed phrases and private keys, and even takes rapid screenshots to get its hands on your digital assets.
UK Watchdog Cautions Healthcare Worker Over Royal's Medical Records Breach
When trust in healthcare settings is broken and personal info is mishandled, swift action is taken - as seen in the ICO's recent decision to issue a formal caution to a former healthcare professional for misusing sensitive patient data. The watchdog is clear: people's personal info must be safe from exploitation.
INC Ransomware Targets 830+ Victims, Expands as Major RaaS Threat
The INC ransomware group has rapidly grown into a major threat, claiming over 830 victims since August 2023, with US organizations making up more than 65% of those affected. Sectors such as legal services, manufacturing, and healthcare are among the most targeted, as INC expands its reach as a prominent Ransomware as a Service (RaaS) operation.
Malware Campaign Exploits AI, Fake GitHub Stars to Spread Crypto Clipper
This sneaky malware uses AI and fake GitHub stars to spread a crypto clipper that can steal your cryptocurrency by swapping your wallet address with the attacker's - and it's been designed to harvest small, repeated thefts from over 15,500 cryptocurrency wallet addresses. The malware operates stealthily, watching your clipboard for crypto wallet addresses and replacing them with an attacker-controlled address.
Google Exposes Flaw in Kubernetes Operator, Denies Bug Bounty
Google's security team initially praised researcher Justin O'Leary for uncovering a high-severity flaw, dubbed ConfigConfusion, in the Config Connector add-on for Kubernetes - only to later claim it wasn't a vulnerability at all and deny a bug bounty. The issue still lingers, leaving users of the open-source tool potentially exposed.
Microsoft Exposes Windows Clipper Malware Campaign Using USB Worm.
Microsoft's security team has uncovered a sneaky malware campaign that's been secretly stealing cryptocurrency from Windows users since February 2026, using a clever combination of a USB worm and a stealthy Tor-based command center. The malware, known as a Windows Clipper, uses Windows Script Host and ActiveX to launch a Tor proxy and communicate with its command center.
Klue OAuth Breach Enables Icarus Extortion Attacks on Salesforce Data
A recent OAuth breach at market intelligence platform Klue has enabled a new extortion group called Icarus to steal sensitive Salesforce CRM data from multiple organizations, sparking a wave of ransom demands. Salesforce has swiftly responded by disabling the connection between Klue's Battlecards app and its platform to protect customers.
DragonForce Hackers Exploit Microsoft Teams to Conceal Backdoor Traffic
Meet Backdoor.Turn, a sneaky malware that uses Microsoft Teams to hide its secret communication with hackers, leveraging the platform's relay infrastructure to stay under the radar. By masquerading as a legitimate connection, it allows attackers to remotely control infected systems undetected.
Microsoft 365 Exposes Data Protection Gaps for Businesses
Microsoft 365 is a powerhouse for productivity, but it leaves data protection gaps that put businesses at risk. The harsh reality is that while Microsoft safeguards its infrastructure, the responsibility of protecting your business data - including backups and recovery - falls squarely on your shoulders.
Law Enforcement Disrupts SocGholish Botnet Linked to Evil Corp
In a major win for cybersecurity, an international coalition of law enforcement agencies has dismantled the notorious SocGholish botnet, liberating nearly 15,000 compromised WordPress sites and taking down 106 servers and domains used by cybercriminals. This bold operation has effectively cut off the cybercrime gang's access to thousands of infected computer systems.
India Warns Telegram Over Exam Leak Channels Before Nationwide Block
India's government took swift action against Telegram, warning the platform about exam leak channels just two weeks before blocking it nationwide, as a crucial medical school entrance exam approached. The move came after complaints of leaked NEET-UG 2026 material being shared on the platform.
Hidden AI Agents Expose Access Risks in Corporate Networks
Can your security team instantly identify who authorized an autonomous AI agent to access your company's core intellectual property? The uncomfortable truth is that most enterprises have no clear answer, leaving them vulnerable to hidden AI access risks.
Apple patches Beats Studio Buds flaw that allowed eavesdropping via Bluetooth
Apple just patched a major flaw in its Beats Studio Buds that allowed hackers within Bluetooth range to eavesdrop on conversations through the earbuds' microphone, even if they weren't paired with the device. The company has released a security update, Beats Firmware Update 1B211, to fix the issue.