Tag: emerging threats
8354 articles
Progress Resumes ShareFile Storage Zones After Patching Vulnerability Exploit
Progress Software swiftly responded to a credible security threat, suspending ShareFile Storage Zones Controller for four days to safeguard customer data, before resuming service on July 14. The brief outage ensured the protection of its flagship enterprise file-sharing service and private data storage.
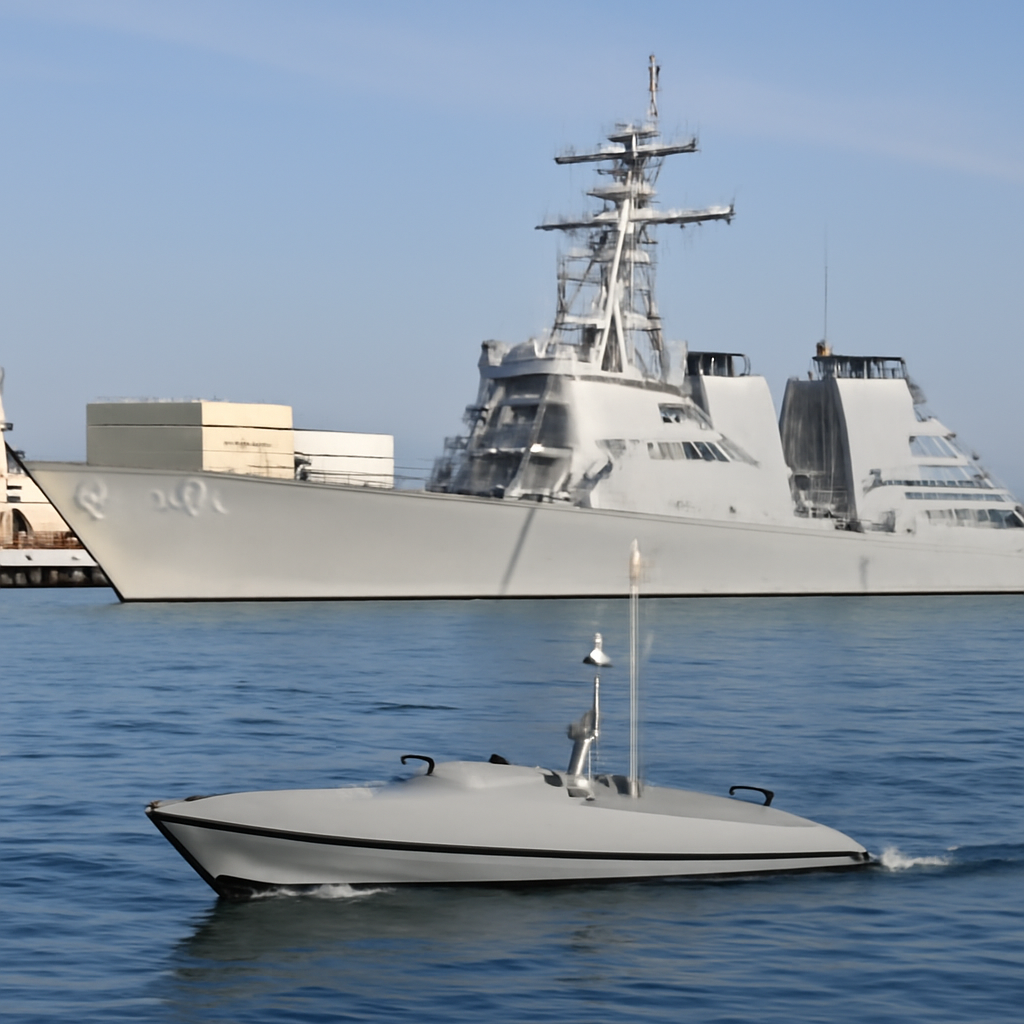
US Deploys Sea Drones in First Combat Strike Against Iran
The US has made history with its first combat strike using sea drones, targeting Iran's Bandar Abbas Naval Base in a bold move to protect commercial shipping in the Strait of Hormuz. The daring operation, carried out by CENTCOM, hit a submarine facility and dozens of other targets across southern Iran.
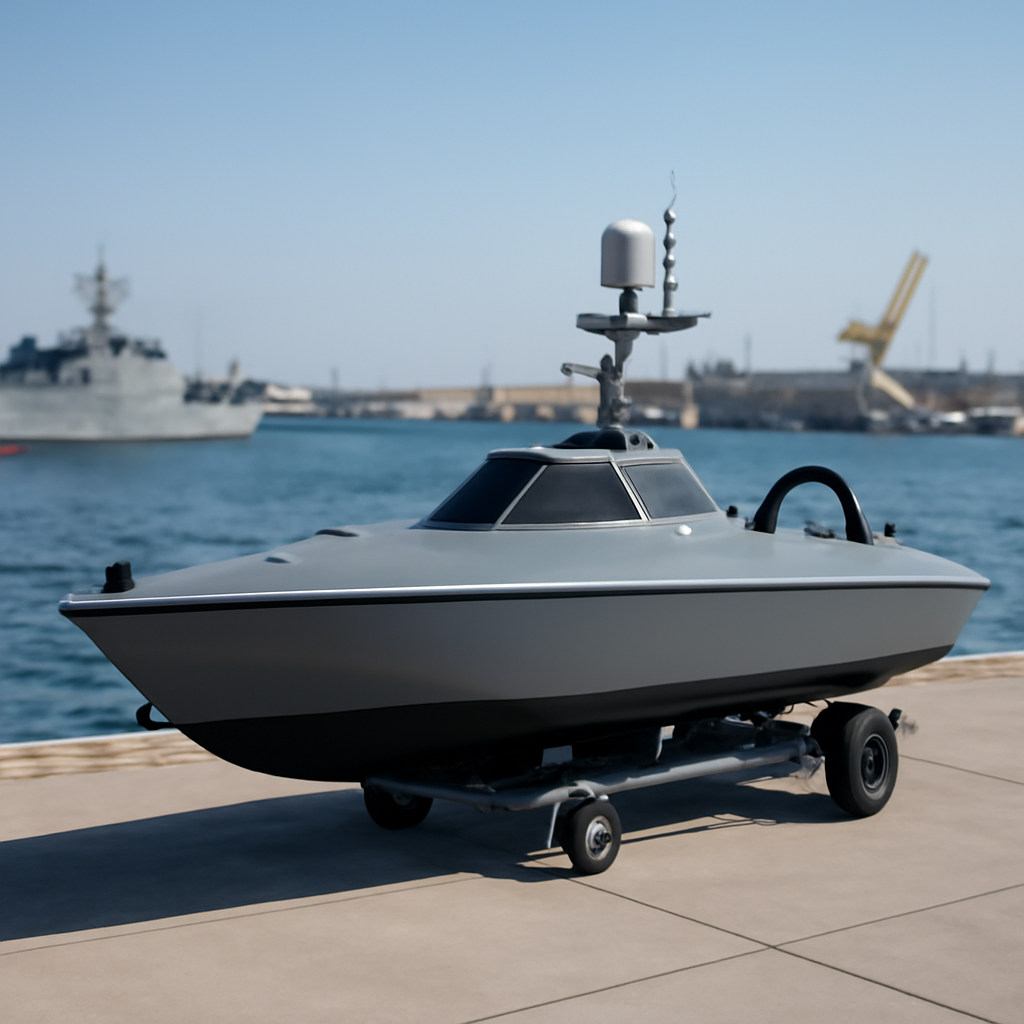
Pakistan's Navy Confronts the Dark Side of Unmanned Surface Warfare
The US Navy has just made history with its first-ever combat use of a one-way attack sea drone, striking Iran's Bandar Abbas Naval Base with three Saronic Corsair unmanned surface vessels. This game-changing tech has a 1,000 lb payload capacity, over 1,000 nautical miles of range, and can zip through the water at 35 knots.
Australia Confronts Space Security Risks with Resilience Push
Space is a double-edged sword - it offers a decisive military advantage, but also creates a vulnerability that can be exploited. To stay ahead, Australia is focusing on building resilience in its space capabilities to absorb losses and disruptions.
FIFA Exposes Vulnerability in Application Backends
A shocking vulnerability was discovered in the backends of two FIFA applications, Football Data Platform and Commentator Information System, where authorization checks were surprisingly handled by client-side code, leaving them open to potential exploitation. This flaw highlights a critical error in application design, where security checks were outsourced to the user interface, rather than being rigorously enforced on the server-side.
Cursor Flaw Enables Malicious Repositories to Execute Windows Code
A newly discovered flaw in Cursor allows malicious repositories to run Windows code simply by opening a project, exploiting a vulnerability that lets it execute any git.exe file found in the repository root without warning. This alarming exploit requires no prior access to the victim's machine, making it a serious security risk.
USAF Tanker Operations at Ben Gurion Airport Face New Limits
Israel's Transportation Minister Miri Regev has set a new limit of 20 U.S. Air Force refueling tankers at Ben Gurion Airport, ensuring that commercial flights won't be disrupted and thousands of travelers' plans remain on track. This move allows remaining tankers to land at nearby Air Force bases instead.
Microsoft Disrupts 570 Security Flaws in Record Patch Tuesday Release
Microsoft just dropped a record-breaking Patch Tuesday update, fixing a whopping 570 security flaws - nearly triple the number from last month - with nearly 60 of them rated critical, allowing attackers to take remote control of your Windows device with ease. This massive update, powered by AI-driven vulnerability discoveries, also patched three zero-day vulnerabilities already being exploited in the wild.
Bayraktar Kızılelma Conducts Supersonic Air-to-Ground Missile Test
The Bayraktar Kızılelma has aced its first supersonic air-to-ground missile test, striking a target with pinpoint accuracy from over 120 km away using Roketsan's JET-230 missile. This major milestone marks a significant advancement in the drone's combat capabilities.
OkoBot Malware Targets Crypto Users Worldwide
Meet OkoBot, a sneaky malware framework that's got crypto users worldwide in its crosshairs, with over 20 malicious payloads and implants that can be assembled in different ways to wreak havoc. It spreads through clever tactics like ClickFix attacks and fake GitHub packages masquerading as legitimate software.
TuxBot Exposes IoT Botnet Framework With LLM-Assisted Development
Meet TuxBot, a cutting-edge IoT botnet framework that's equipped with a powerful arsenal of tools, including 1,496 username/password pairs for Telnet brute-forcing and a highly adaptable bot that can target a wide range of devices. This sophisticated framework is capable of automating attacks and can be easily customized to wreak havoc on a massive scale.
Compromised AsyncAPI Packages Deliver Multi-Stage Botnet Malware
Malicious actors have compromised several AsyncAPI packages, delivering a sophisticated multi-stage botnet malware that uses a command framework with six independent communication channels. The affected packages include @asyncapi/generator-helpers, @asyncapi/generator-components, @asyncapi/generator, and @asyncapi/specs in specific versions.
Vulnerabilities Remain Unaddressed Despite Swift Remediation Efforts
Malicious npm packages have skyrocketed 451% year-over-year, highlighting a disturbing trend where old vulnerabilities continue to resurface and supply-chain abuse is scaling rapidly, putting organizations at risk. Despite swift remediation efforts, many critical vulnerabilities remain unaddressed.
CISA Warns of Actively Exploited SharePoint Flaws
Don't let your SharePoint servers become an easy target: over 800 Internet-exposed servers remain unpatched against actively exploited vulnerabilities, including CVE-2026-32201 and CVE-2026-45659. Act now to protect your systems from potential attacks.
Microsoft Patch Deluge Exposes New Normal in Cybersecurity Updates
Microsoft just dropped a record 570 security updates on Patch Tuesday, revealing a new normal in cybersecurity: AI has drastically reduced the cost of finding vulnerabilities, leading to a surge in fixes that shows no signs of slowing down. This massive update batch included critical patches for elevation of privilege, remote code execution, and information disclosure flaws.
UK Bolsters National Risk Register with New Cyber Threat Scenarios
The UK is stepping up its defenses against cyber threats, updating its National Risk Register with new scenarios that highlight the potentially deadly consequences of online attacks. This move comes as the government acknowledges that cyber threats, alongside pandemics and natural disasters, pose a significant risk to the nation's safety.
Microsoft Blocks Windows Updates on Dell PCs Due to Shutdowns
Microsoft has temporarily blocked a crucial Windows 11 security update for certain Dell PCs due to reports of unexpected shutdowns and performance issues. The move comes after a previous preview update caused problems with the Intel Innovation Platform Framework Processor Participant driver.
US Charges Russian Nationals for Bulletproof Hosting Services
US authorities have charged three Russian nationals with operating illicit bulletproof hosting services that enabled cybercrime, affecting victims across 21 states, including banks, schools, hospitals, and media companies. The accused, Aleksandr Volosovik, Yulia Pankova, and Kirill Zatolokin, allegedly facilitated a range of malicious activities through their services.
SonicWall Zero-Days Exploited, Enable Admin Command Execution
SonicWall is urging immediate action to fix two zero-day vulnerabilities in its Secure Mobile Access (SMA) 1000 series appliances, which are being actively exploited by attackers to execute admin-level commands. These critical flaws, tracked as CVE-2026-15409 and CVE-2026-15410, could compromise your system's security if not patched right away.
DHS Breach Exposes Flaws in Cyber Detection Process
A recent cyber incident at the Department of Homeland Security went undetected for weeks, despite raising red flags in not one, but two separate assessments that were initially dismissed as harmless. The breach, which occurred on the Homeland Security Information Network (HSIN), highlights alarming flaws in the cyber detection process.
Pentagon Scraps Cybersecurity Certification Phase, Launches Reform Review
The Department of Defense is shaking things up in the world of cybersecurity certification, suspending Phase 2 of its Cybersecurity Maturity Model Certification (CMMC) program and launching a 60-day review to explore a more streamlined approach. This move aims to ease compliance burdens, especially for small and medium-sized businesses.
US Army Munitions Plant Falters, Fails to Produce 155mm Parts
The US Army's goal of producing 100,000 155mm artillery rounds per month is at risk due to a production shortfall at a key munitions plant in Texas. A critical facility has failed to deliver 30,000 essential projectile metal parts, crippling the Army's artillery production capabilities.
Treasury Disrupts Ransomware Networks with Sanctions on VPN Service
The US Treasury Department has cracked down on a notorious VPN service, 1VPNS, and its alleged administrators, sanctioning them for enabling ransomware groups to launch devastating attacks on US companies and institutions. This move disrupts the cybercriminal ecosystem, cutting off a key tool used to hide attack origins, deploy malware, and manage stolen data.
South Korea Bolsters Electronic Warfare with Global 6500 Jammer Jets
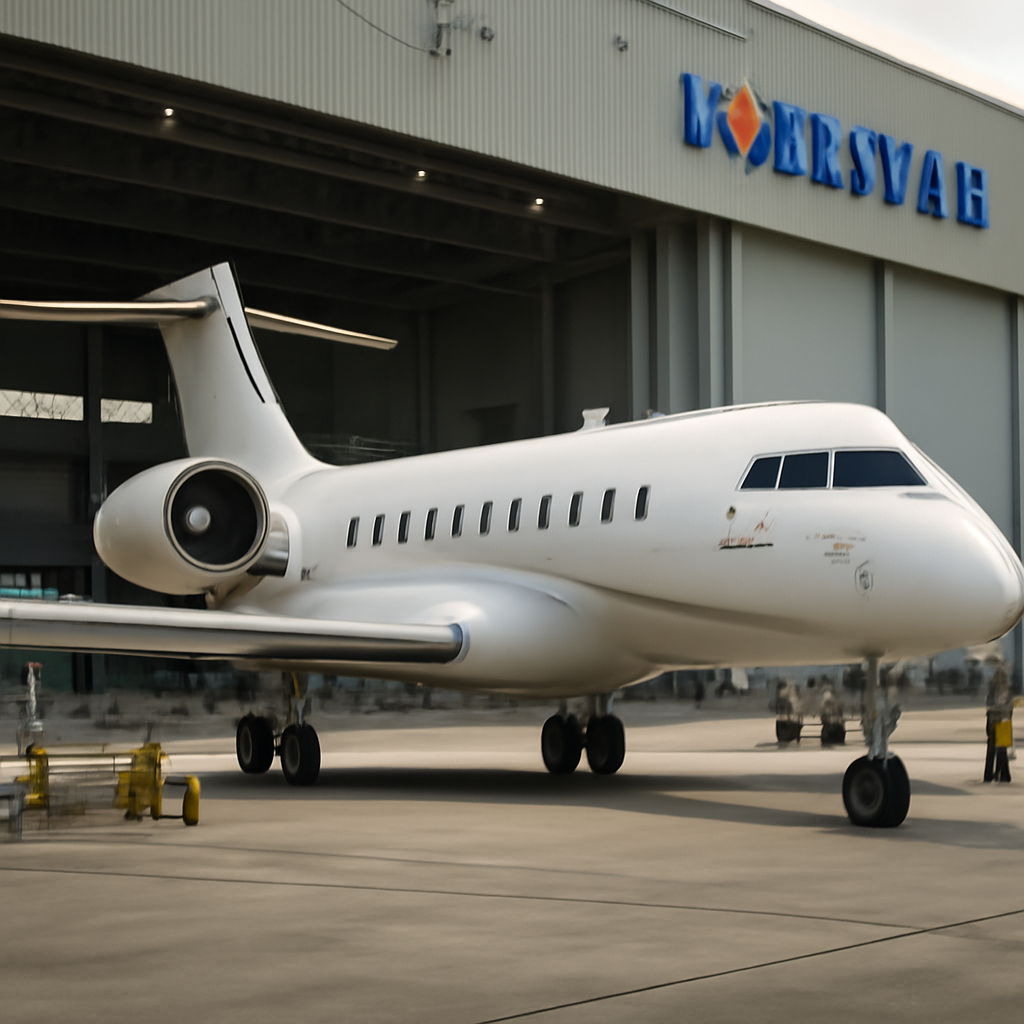
South Korea is taking its electronic warfare capabilities to the next level with the acquisition of two Global 6500 jets, which will be converted into cutting-edge standoff jammer aircraft. The move underscores the country's commitment to bolstering its defense systems, leveraging the high-performance and versatility of the Global 6500 aircraft.