Tag: containerization
7 articles
Docker Fixes Flaw That Let Users Push Images as Others on Hub
Docker patched a critical security flaw that allowed users to push images as others on Docker Hub, exposing a vulnerability that went undetected for over two years. The bug, logged as CVE-2026-105445, had a near-perfect CVSS 4.0 score of 9.4, highlighting the severity of the issue.
Microsoft Expands WSL with Native Linux Container Support
Microsoft just made it a whole lot easier to work with Linux containers on Windows, introducing a new command-line tool, wslc.exe, that lets you build, run, and deploy containers with ease. You can get started by running wsl --update and using familiar container commands.
Docker Flaw Lets Guest Code Read, Modify macOS Host Files
A newly discovered Docker flaw on macOS could allow malicious code in a virtual machine to break free from its sandbox and read or modify sensitive host files, potentially leading to code execution on the host. This vulnerability, tracked as CVE-2026-77179, leverages a weakness in the virtio-fs host server to gain unauthorized access.
Chainguard Reaches 1 Billion Build Manifests with AI-Powered Factory Overhaul
Chainguard has achieved a major milestone, processing over 1 billion container build manifests in just six months - a doubling of its output - thanks to a revolutionary AI-powered factory overhaul that enables daily, verifiable rebuilds. This impressive feat reflects a fundamental shift in the company's system, ensuring a constantly updated catalog of fresh, reliable artifacts.
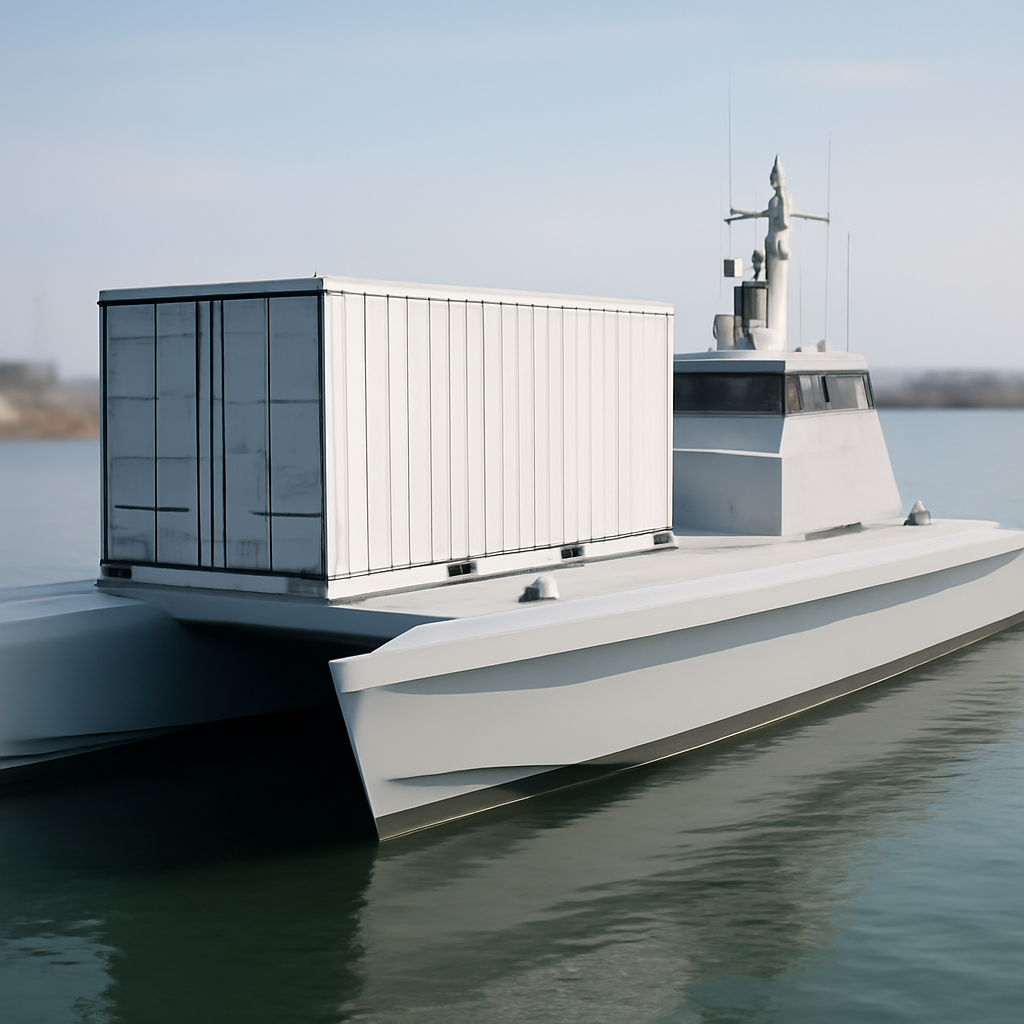
ARES Shipyard Unveils Large Container-Rated Catamaran USV Design
Meet the game-changing catamaran USV design from ARES Shipyard, a 22.5-metre vessel capable of carrying a single 40 ft shipping container, revolutionizing unmanned surface vessel capabilities. This innovative design boasts a spacious flatbed section, offering a significant upgrade from ARES's existing ULAQ family.

Container Escapes Fuel Supply Chain Attacks on Cloud Infrastructures
Containers can quickly become a gateway to your entire cloud infrastructure if vulnerable to attacks, with hackers exploiting flaws like CVE-2019-5736, CVE-2022-0492, and CVE-2024-21626 to break free from isolated environments and wreak havoc on your host system. There are five key entry points for container attacks, including vulnerabilities, misconfigurations, and supply chain threats.

Docker Images Expose Hidden Vulnerabilities
Docker containers are a top target for attackers, with a recent analysis of 100 popular Docker Hub images revealing that 64 contained critical flaws due to outdated software versions. Only one in ten images was fully up to date, leaving a vast majority vulnerable to predictable and dangerous exposures.